

libpeconv
 hasherezade/libpeconv
Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
binary-analysismalware-analysismemory-forensics+4
1.4k
hasherezade/libpeconvCustom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
 vxunderground/vxug-papers
Research code & papers from members of vx-underground.
 redcode-labs/coldfire
Golang malware development library
 aaaddress1/pr0cess
some gadgets about windows process and ready to use :)
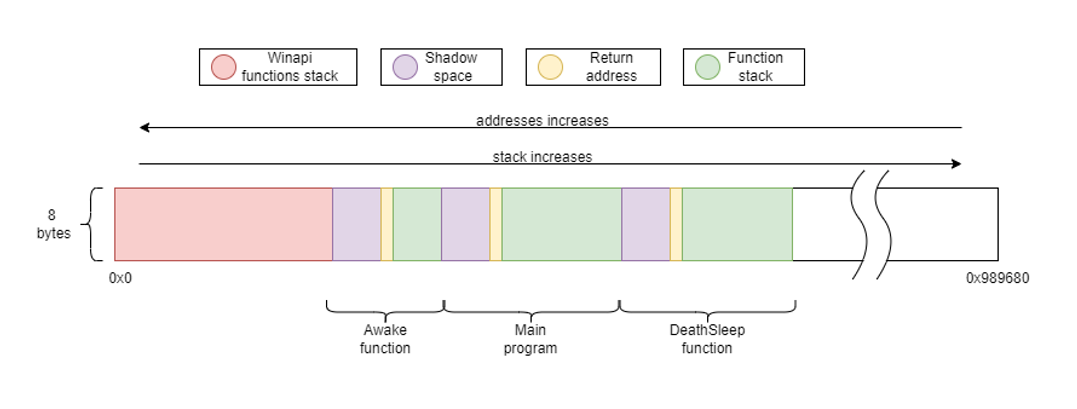 janoglezcampos/deathsleep
A PoC implementation for an evasion technique to terminate the current thread and restore it before resuming execution, while implementing page…
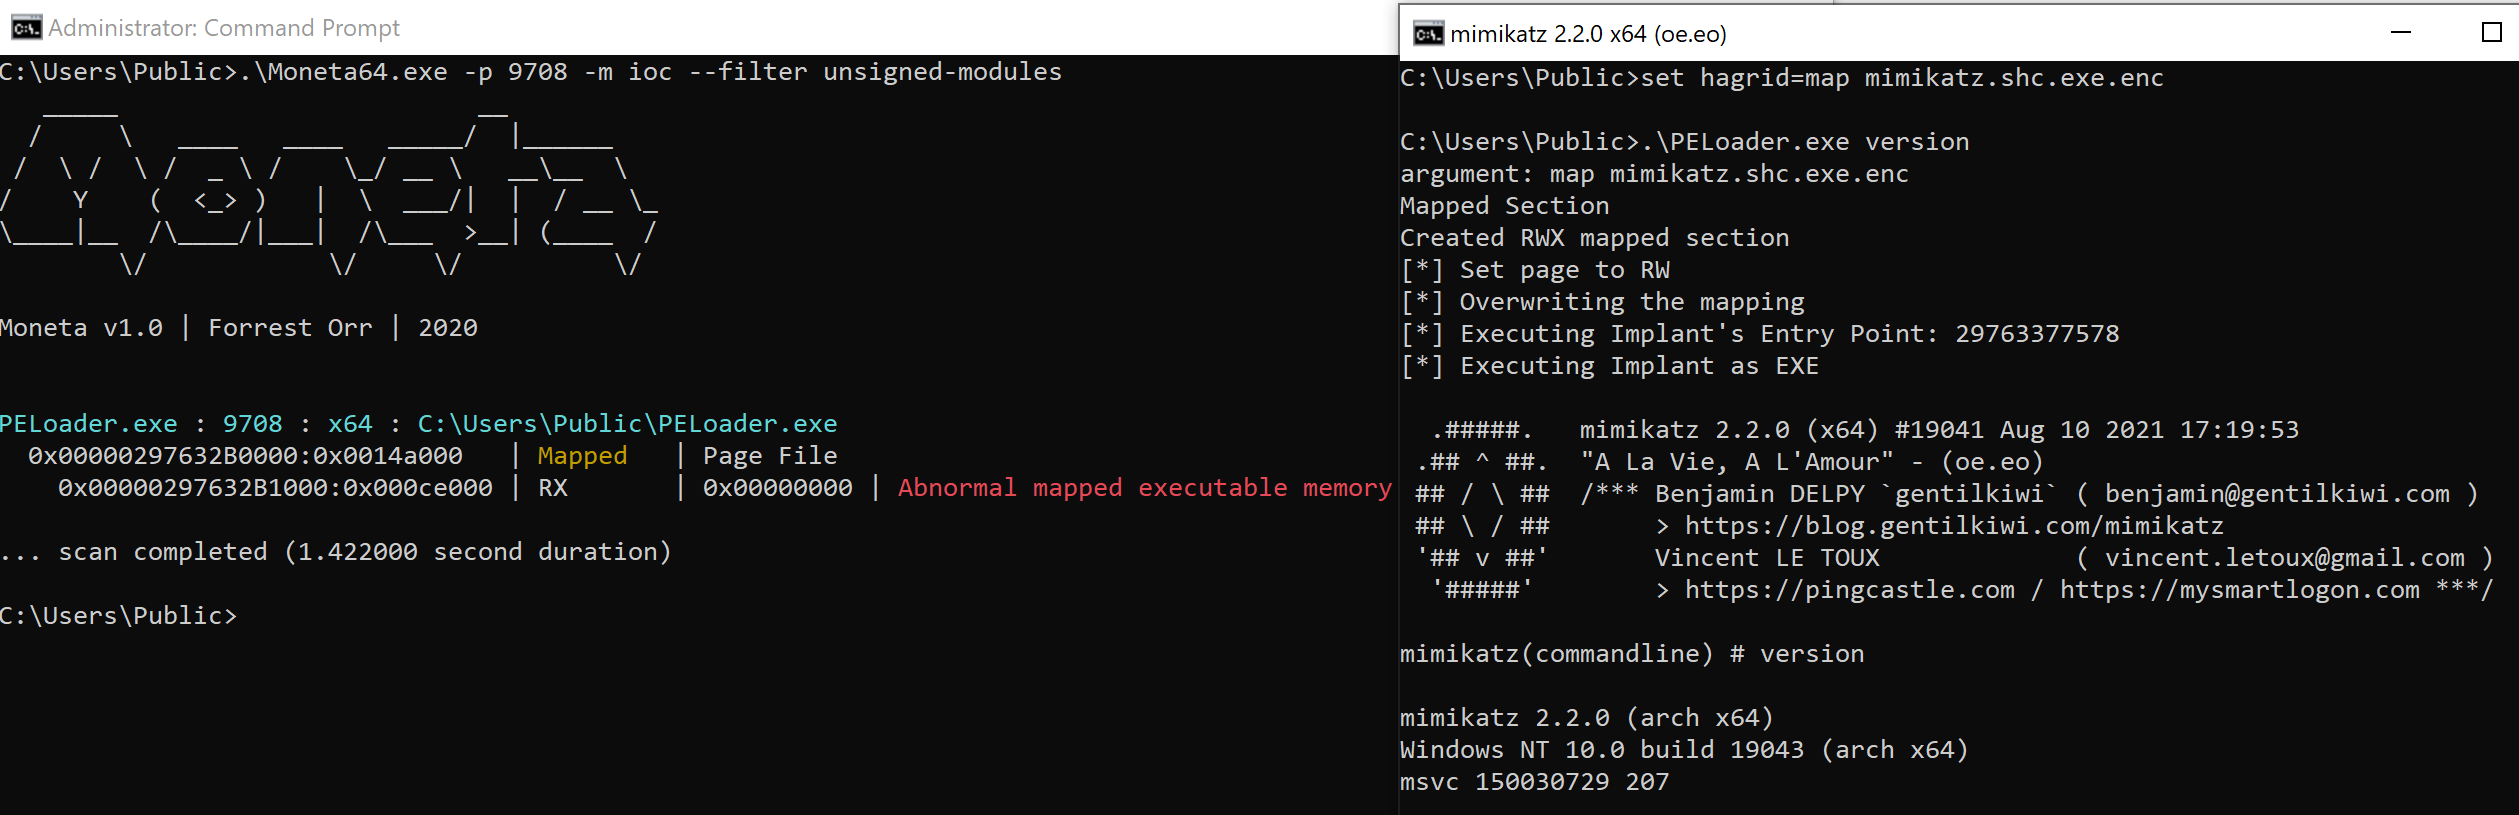 hagrid29/peloader
PE loader with various shellcode injection techniques
 matheuzsecurity/furtex
Post-exploitation and evasion research toolkit for Linux.
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 strivexjun/memorymodulepp
C++ library to load DLLs directly from memory without touching disk, with exception handling support, enabling stealthy code execution and evasion of…
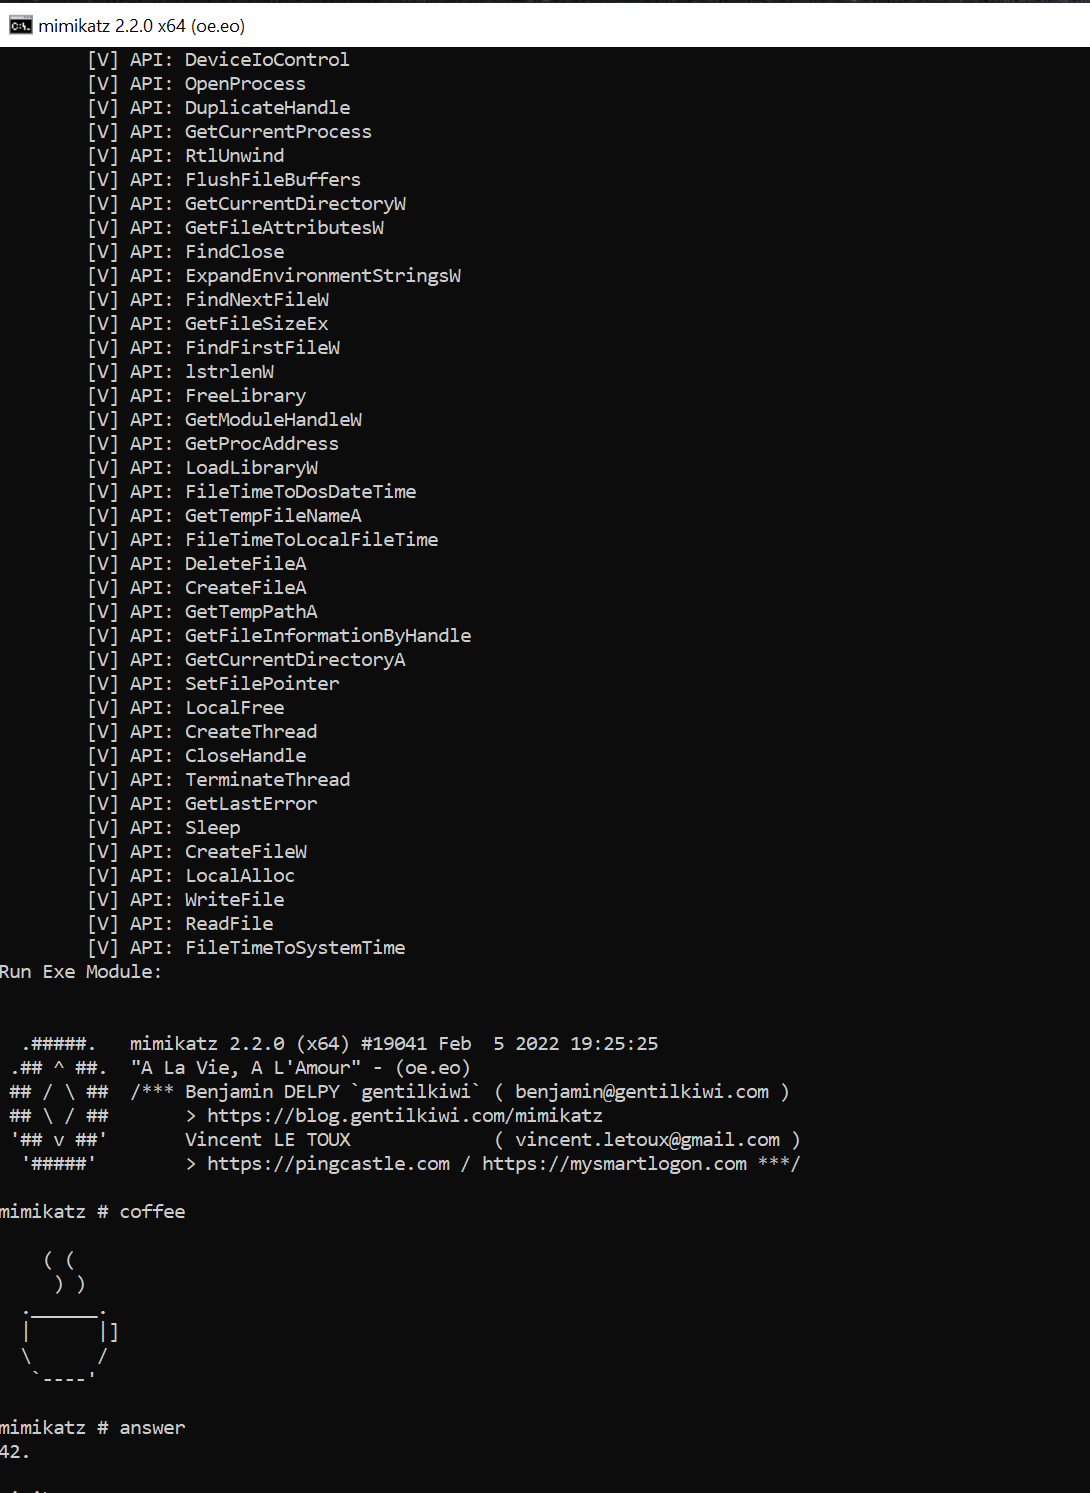 s3cur3th1ssh1t/nim-runpe
A Nim implementation of reflective PE-Loading from memory
 kleiton0x00/shelltropy
A technique of hiding malicious shellcode via Shannon encoding.
 nccgroup/cve-2017-8759
NCC Group's analysis and exploitation of CVE-2017-8759 along with further refinements
 malwaretech/tinyxpb
Windows XP 32-Bit Bootkit
 dr4k0nia/niximports
A .NET malware loader, using API-Hashing to evade static analysis
 sh0ckfr/lockbit3.0-mpclient-defender-poc
Lockbit3.0 Microsoft Defender MpClient.dll DLL Hijacking PoC
 withsecurelabs/doublepulsar-usermode-injector
A utility to use the usermode shellcode from the DOUBLEPULSAR payload to reflectively load an arbitrary DLL into another process, for use in testing…
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development