
ps-ppl-bypass
 r41n3rzuf477/ps-ppl-bypass
Process Explorer vulnerable driver PPL Bypass
binary-exploitationdefensive-toolsexploitation+5
2722 days ago
r41n3rzuf477/ps-ppl-bypassProcess Explorer vulnerable driver PPL Bypass
 gmh5225/memory-relocalloc
C proof-of-concept that locates code caves in the .reloc section of mapped DLLs to allocate and execute small shellcode, replacing typical memory…
 aaaddress1/pr0cess
some gadgets about windows process and ready to use :)
 aydinnyunus/cve-2024-24576-exploit
CVE-2024-24576 Proof of Concept
 sh4hin/gopurple
Yet another shellcode runner consists of different techniques for evaluating detection capabilities of endpoint security solutions
 jm00nj/icmp-ghost-a-fileless-x64-assembly-c2-agent
Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…
 solomonsklash/sleepycrypt
A shellcode function to encrypt a running process image when sleeping.
 po6ix/poc-for-cve-2023-41993
Proof-of-concept exploit for CVE-2023-41993, a WebKit JIT type confusion in Safari. Provides addrof/fakeobj primitives via heap manipulation and…
 sp0pielar/cve-2019-9791
Exploit chain for CVE-2019-9791 & CVE-2019-11708 against firefox 65.0 on windows 64bit
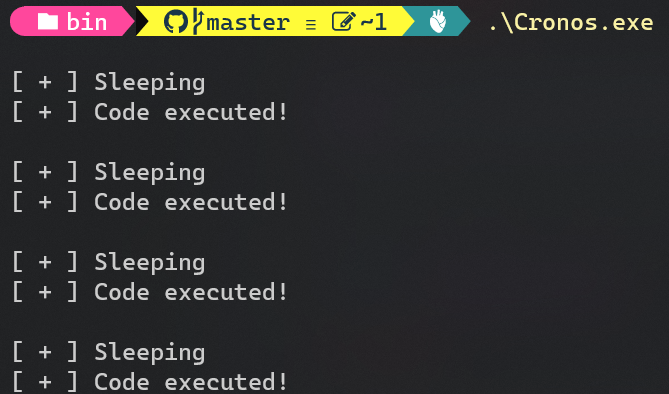 idov31/cronos
PoC for a sleep obfuscation technique leveraging waitable timers to evade memory scanners.
 rasta-mouse/process-inject-kit
Port of Cobalt Strike's Process Inject Kit
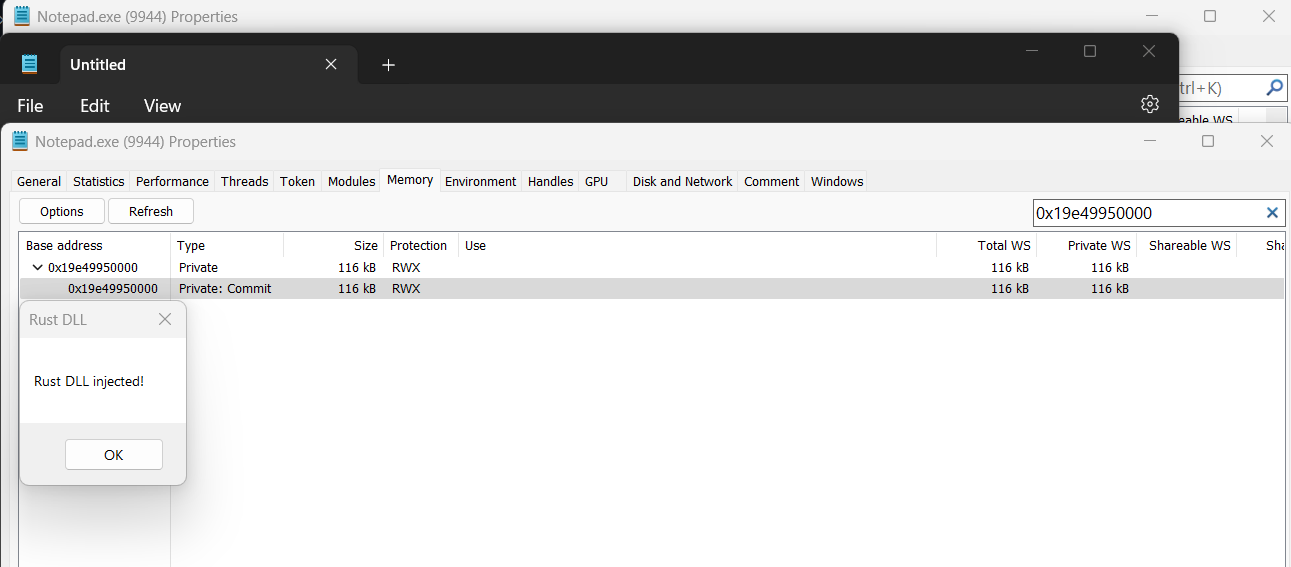 memn0ps/venom-rs
Rusty Injection - Shellcode Reflective DLL Injection (sRDI) in Rust (Codename: Venom)
 gmh5225/iat-hook
C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
 secrary/injectproc
InjectProc - Process Injection Techniques [This project is not maintained anymore]
 cobalt-strike/unhook-bof
Remove API hooks from a Beacon process.
 winterknife/pinkpanther
Windows x64 handcrafted token stealing kernel-mode shellcode
 withsecurelabs/doublepulsar-usermode-injector
A utility to use the usermode shellcode from the DOUBLEPULSAR payload to reflectively load an arbitrary DLL into another process, for use in testing…
 calligraf0/cve-2024-0311
Proof-of-concept exploit for CVE-2024-0311 bypassing Skyhigh Client Proxy policy via process injection and named pipe manipulation, with custom…