
cua-kit
 preludeorg/cua-kit
Tools for attacking Computer Use Agents
ai-securitycommand-and-controlexploitation+7
preludeorg/cua-kitTools for attacking Computer Use Agents
 xsscx/cve-2017-5638
Example PoC Code for CVE-2017-5638 | Apache Struts Exploit
 shinthink/cve-2026-57827
CVE-2026-57827 — RSFiles! Joomla Component Unauthenticated File Upload RCE. Split-controller upload bypass. CVSS 9.8 | CWE-434 | com_rsfiles < 1.17.12
 jas502n/cve-2015-5254
ActiveMQ Deserialization RCE
 zyphorixofficialmain-lab/cve-2026-87902
Python exploit for CVE-2026-87902, a WordPress Core LFI-to-RCE chain. Fingerprints versions, writes a PHP shell via pearcmd, and provides command…
 jenderal92/cve-2026-41940
Bulk scanner and mass exploitation tool for CVE-2026-41940 on cPanel/WHM, built for automated target validation and high-speed multi-threaded…
 shinthink/solrradar
☄️ Mass reconnaissance & exploitation framework for Apache Solr CVE-2026-44825 — Velocity template injection to RCE
 null200ok/cve-2026-41940-tool
A comprehensive Python utility to **detect**, **scan in bulk**, and **exploit** the critical authentication bypass vulnerability (CVE-2026-41940) in…
 g0d150ne/xss2shell
Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…
 shivshantp/cve-2025-2825-crushftp-authbypass
Authentication Bypass PoC for CVE-2025-2825 – Exploiting CrushFTP 10.x
 ghostlyrootb2h/cve-2026-82222
Exploit framework for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports mass scanning, auto-detection, multi-threading,…
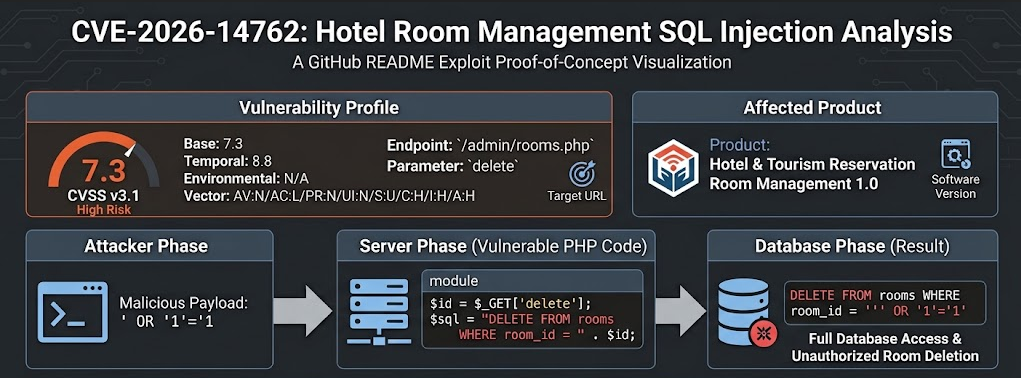 tc4dy/cve-2026-14762-poc-exploit
Multi-threaded time-based blind SQL injection exploit for CVE-2026-14762 targeting Hotel & Tourism Reservation 1.0. Enumerates databases, tables,…
 cerberusmrxi/wp-bricks-exploit-cve-2024-25600
CVE-2024-25600 - Unauthenticated RCE exploit for WordPress Bricks Builder Theme. Advanced exploitation framework with interactive shell, reverse…
 hann1bl3l3ct3r/fuxapwn
POC exploit for CVE-2026-25895 FUXA Unauthenticated Path Traversal -> Arbitrary File Write -> RCE
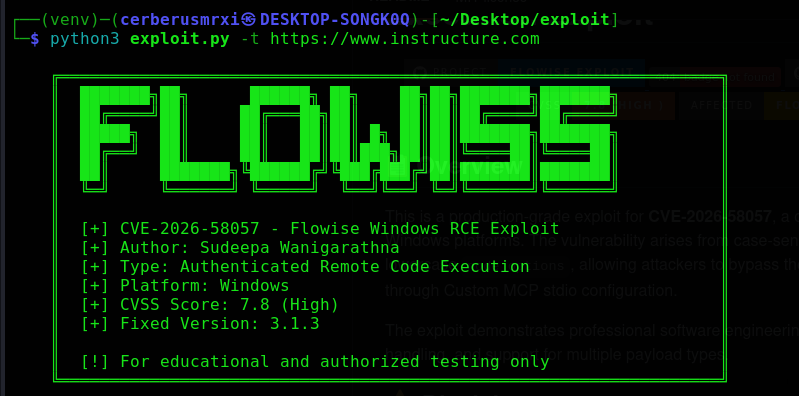 cerberusmrxi/flowise-cve-2026-58057-exploit
Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…
 nxploited/cve-2026-91097-cve-2026-91106
HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)
 bambooqj/cve-2025-32432
AI修复生成的CVE-2025-32432的poc