
Christmas
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
adversarial-attackids-ips-evasionpayload-development+3
maldev-academy/christmasPoC demonstrating a multi process injection chain aimed at remotely executing shellcode
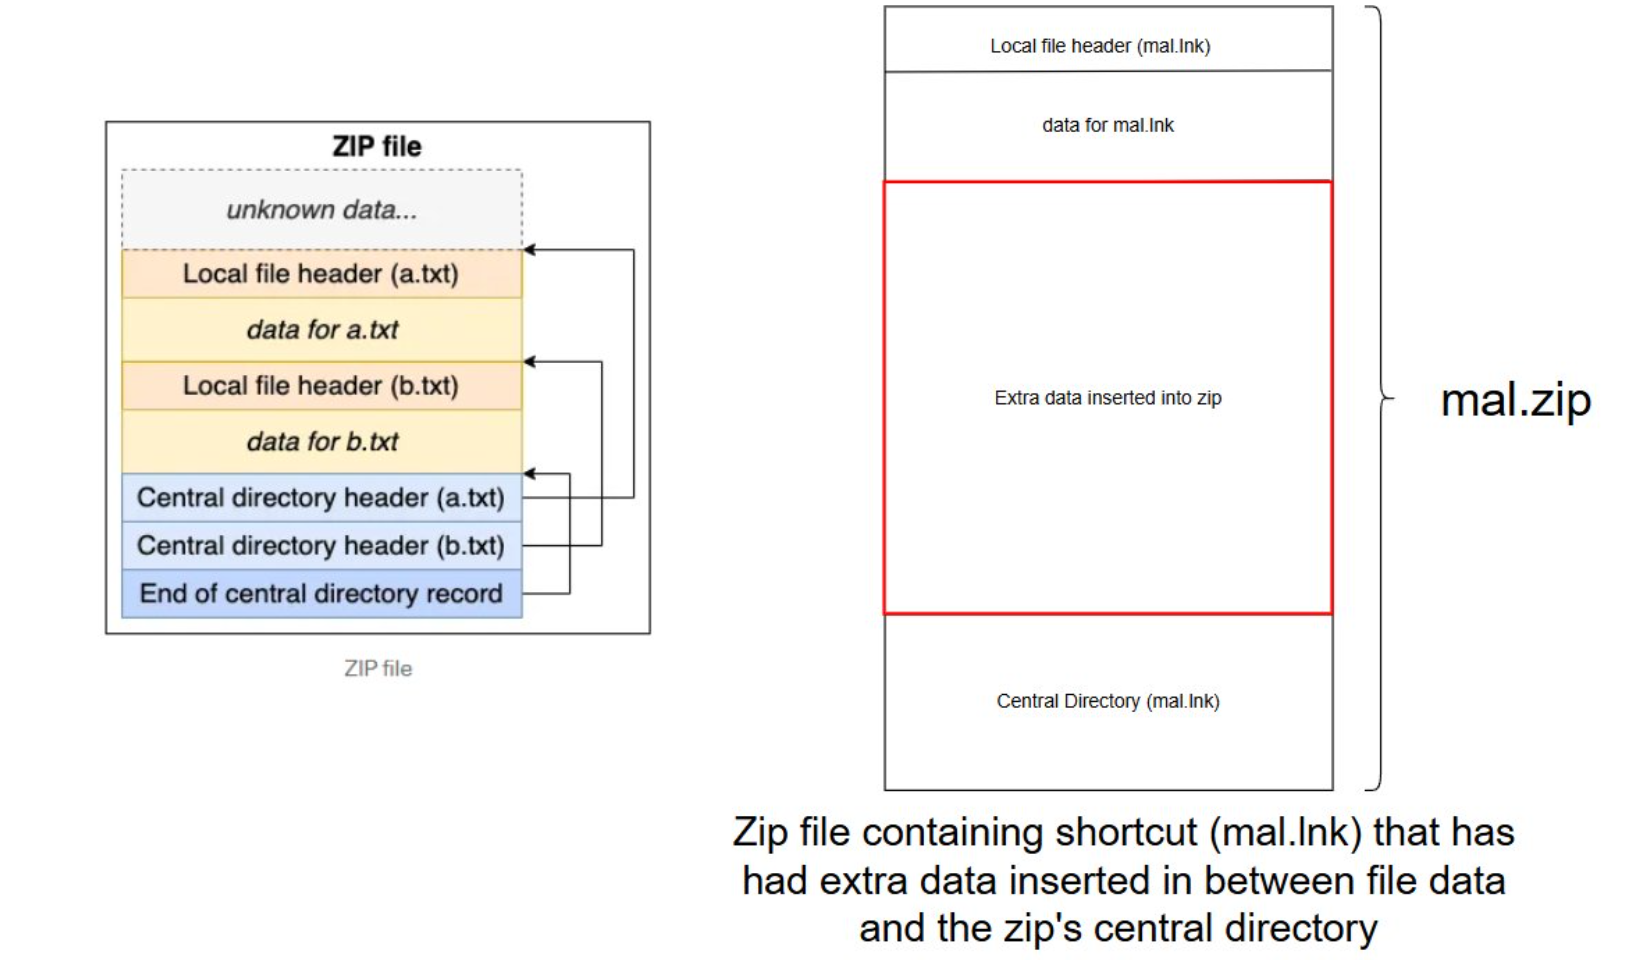 octoberfest7/zip_smuggling
Python3 utility for creating zip files that smuggle additional data for later extraction
 namazso/linux_injector
A simple ptrace-less shared library injector for x64 Linux
 kudaes/split
Apply a divide and conquer approach to bypass EDRs
 saadahla/pe-obfuscator
PE obfuscator with Evasion in mind

 rasta-mouse/process-inject-kit
Port of Cobalt Strike's Process Inject Kit
 sh0ckfr/lockbit3.0-mpclient-defender-poc
Lockbit3.0 Microsoft Defender MpClient.dll DLL Hijacking PoC
 lloydlabs/ntqueueapcthreadex-ntdll-gadget-injection
This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
 adepts-of-0xcc/vba-macro-experiments
Collection of VBA macro published in our twitter / blog
 idov31/jormungandr
Jormungandr is a kernel implementation of a COFF loader, allowing kernel developers to load and execute their COFFs in the kernel.


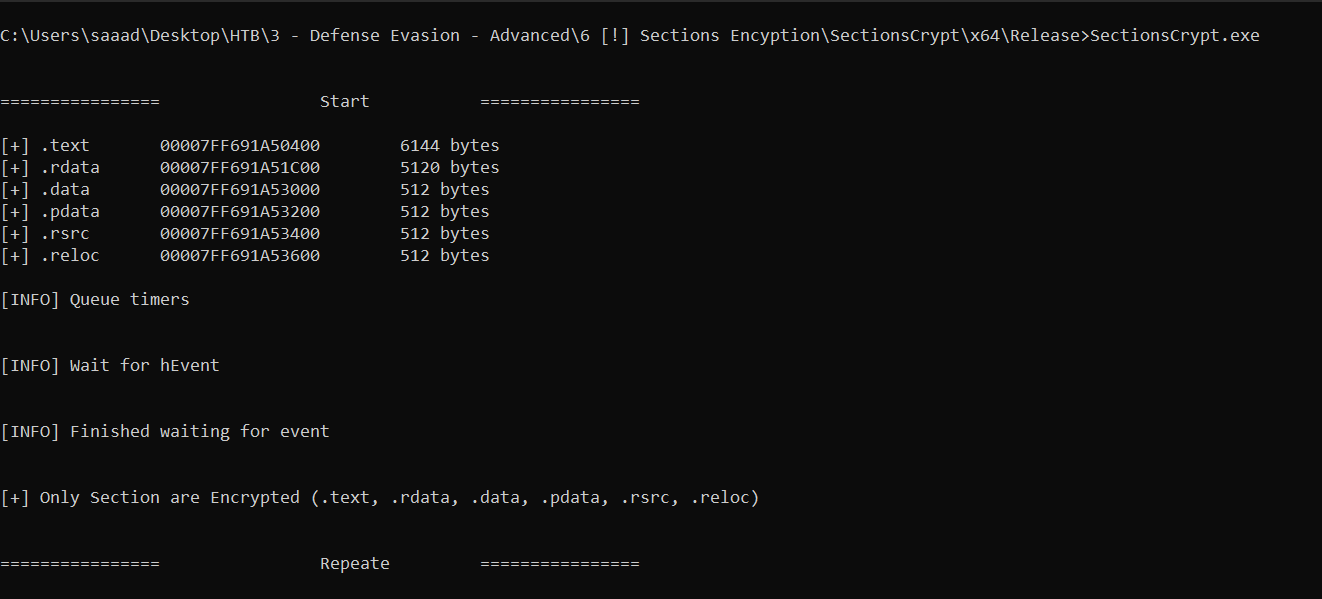 saadahla/d1rksleep
Improved version of EKKO by @5pider that Encrypts only Image Sections
 rad9800/vehapiresolve
Resolves Windows APIs at runtime using vectored exception handlers and hashed lookups to hide imports and slow reverse engineering of offensive…
 kozmer/aad-bofs
Cobalt Strike BOF collection for attacking Azure AD during red team operations, covering authentication, enumeration, and post-exploitation vectors.
 thiagopeixoto/winsos-poc
A PoC demonstrating code execution via DLL Side-Loading in WinSxS binaries.