
P4wnP1_aloa
 rogandawes/p4wnp1_aloa
P4wnP1 A.L.O.A. by MaMe82 is a framework which turns a Rapsberry Pi Zero W into a flexible, low-cost platform for pentesting, red teaming and…
bluetooth-securityexploit-frameworkshardware-hacking+5
4.4k
rogandawes/p4wnp1_aloaP4wnP1 A.L.O.A. by MaMe82 is a framework which turns a Rapsberry Pi Zero W into a flexible, low-cost platform for pentesting, red teaming and…
 cr4sh/smmbackdoor
First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…
 bin4ry/unipwn
BLE exploit framework for Unitree robots: command injection via hardcoded AES keys enables remote takeover, payload injection, and wormable…
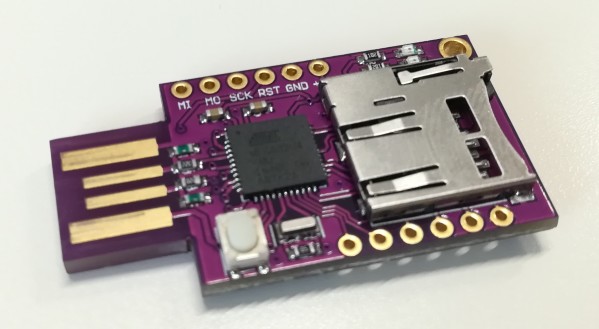 mharjac/bad_ducky
Rubber Ducky compatible clone based on CJMCU BadUSB HW.
 jgoyd/ios-attack-chain-cve-2025-31200-cve-2025-31201
CVE-2025-31200 is a zero-day, zero-click RCE in iOS CoreAudio’s AudioConverterService, triggered by a malicious audio file via iMessage/SMS.…
 itsmehacker/ducky-exploit
Arduino Rubber Ducky Framework
 90n45-d3v/bluebunny
BLE-based C2 server for Hak5 Bash Bunny enabling wireless command injection, payload delivery, and remote control over Bluetooth Low Energy.
 eason-zz/bluetoothducky
Exploit implementation for CVE-2023-45866 enabling unauthenticated Bluetooth keyboard injection using DuckyScript payloads on Raspberry Pi.
 drapl0n/pwnkit
USB Rubber Ducky payload that exploits CVE-2021-4034 to escalate privileges and spawn a root shell on Unix-like systems in under 10 seconds.
 davidkowalk/arduino-netcat-backdoor
*Proof of concept* Attacks a Windows machine running Windows 7 or later, creating a persistent Backdoor.
 rxerium/bash-bunny-payloads
Personally crafted Bash Bunny Payloads