
EvilVM
 jephthai/evilvm
Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
command-and-controlexploit-frameworkspayload-development+7
209
jephthai/evilvmForth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
 byt3bl33d3r/gcat
A PoC backdoor that uses Gmail as a C&C server
 octoberfest7/xll_phishing
XLL Phishing Tradecraft
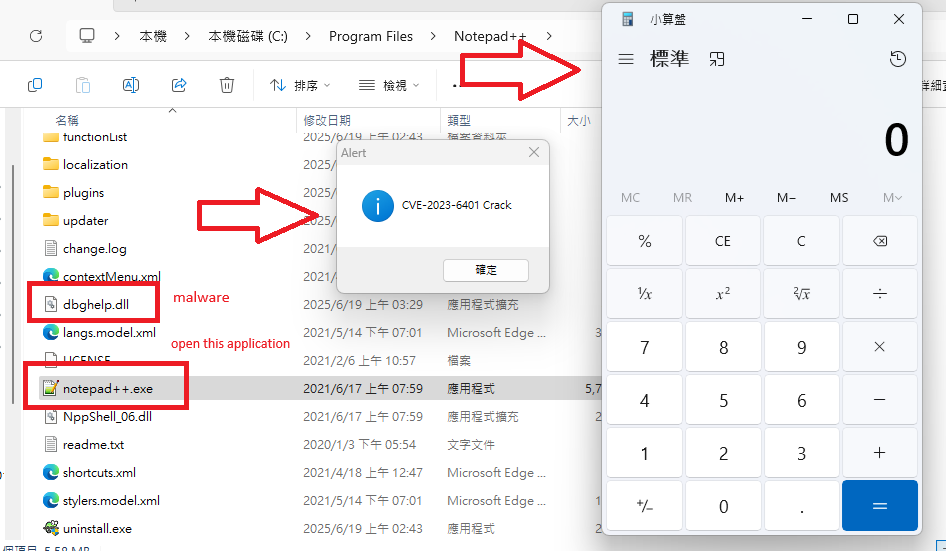 mekitoci/cve-2023-6401
CVE-2023-6401 is a DLL hijacking vulnerability that allows attackers to execute arbitrary code by placing a malicious `dbghelp.dll` file in the…
 samugit83/redamon
Autonomous AI red team framework that chains reconnaissance, exploitation, and post-exploitation into a single pipeline, then triages findings,…
 paulsec/twittor
A fully featured backdoor that uses Twitter as a C&C server
 r3nhat/grat2
We developed GRAT2 Command & Control (C2) project for learning purpose.
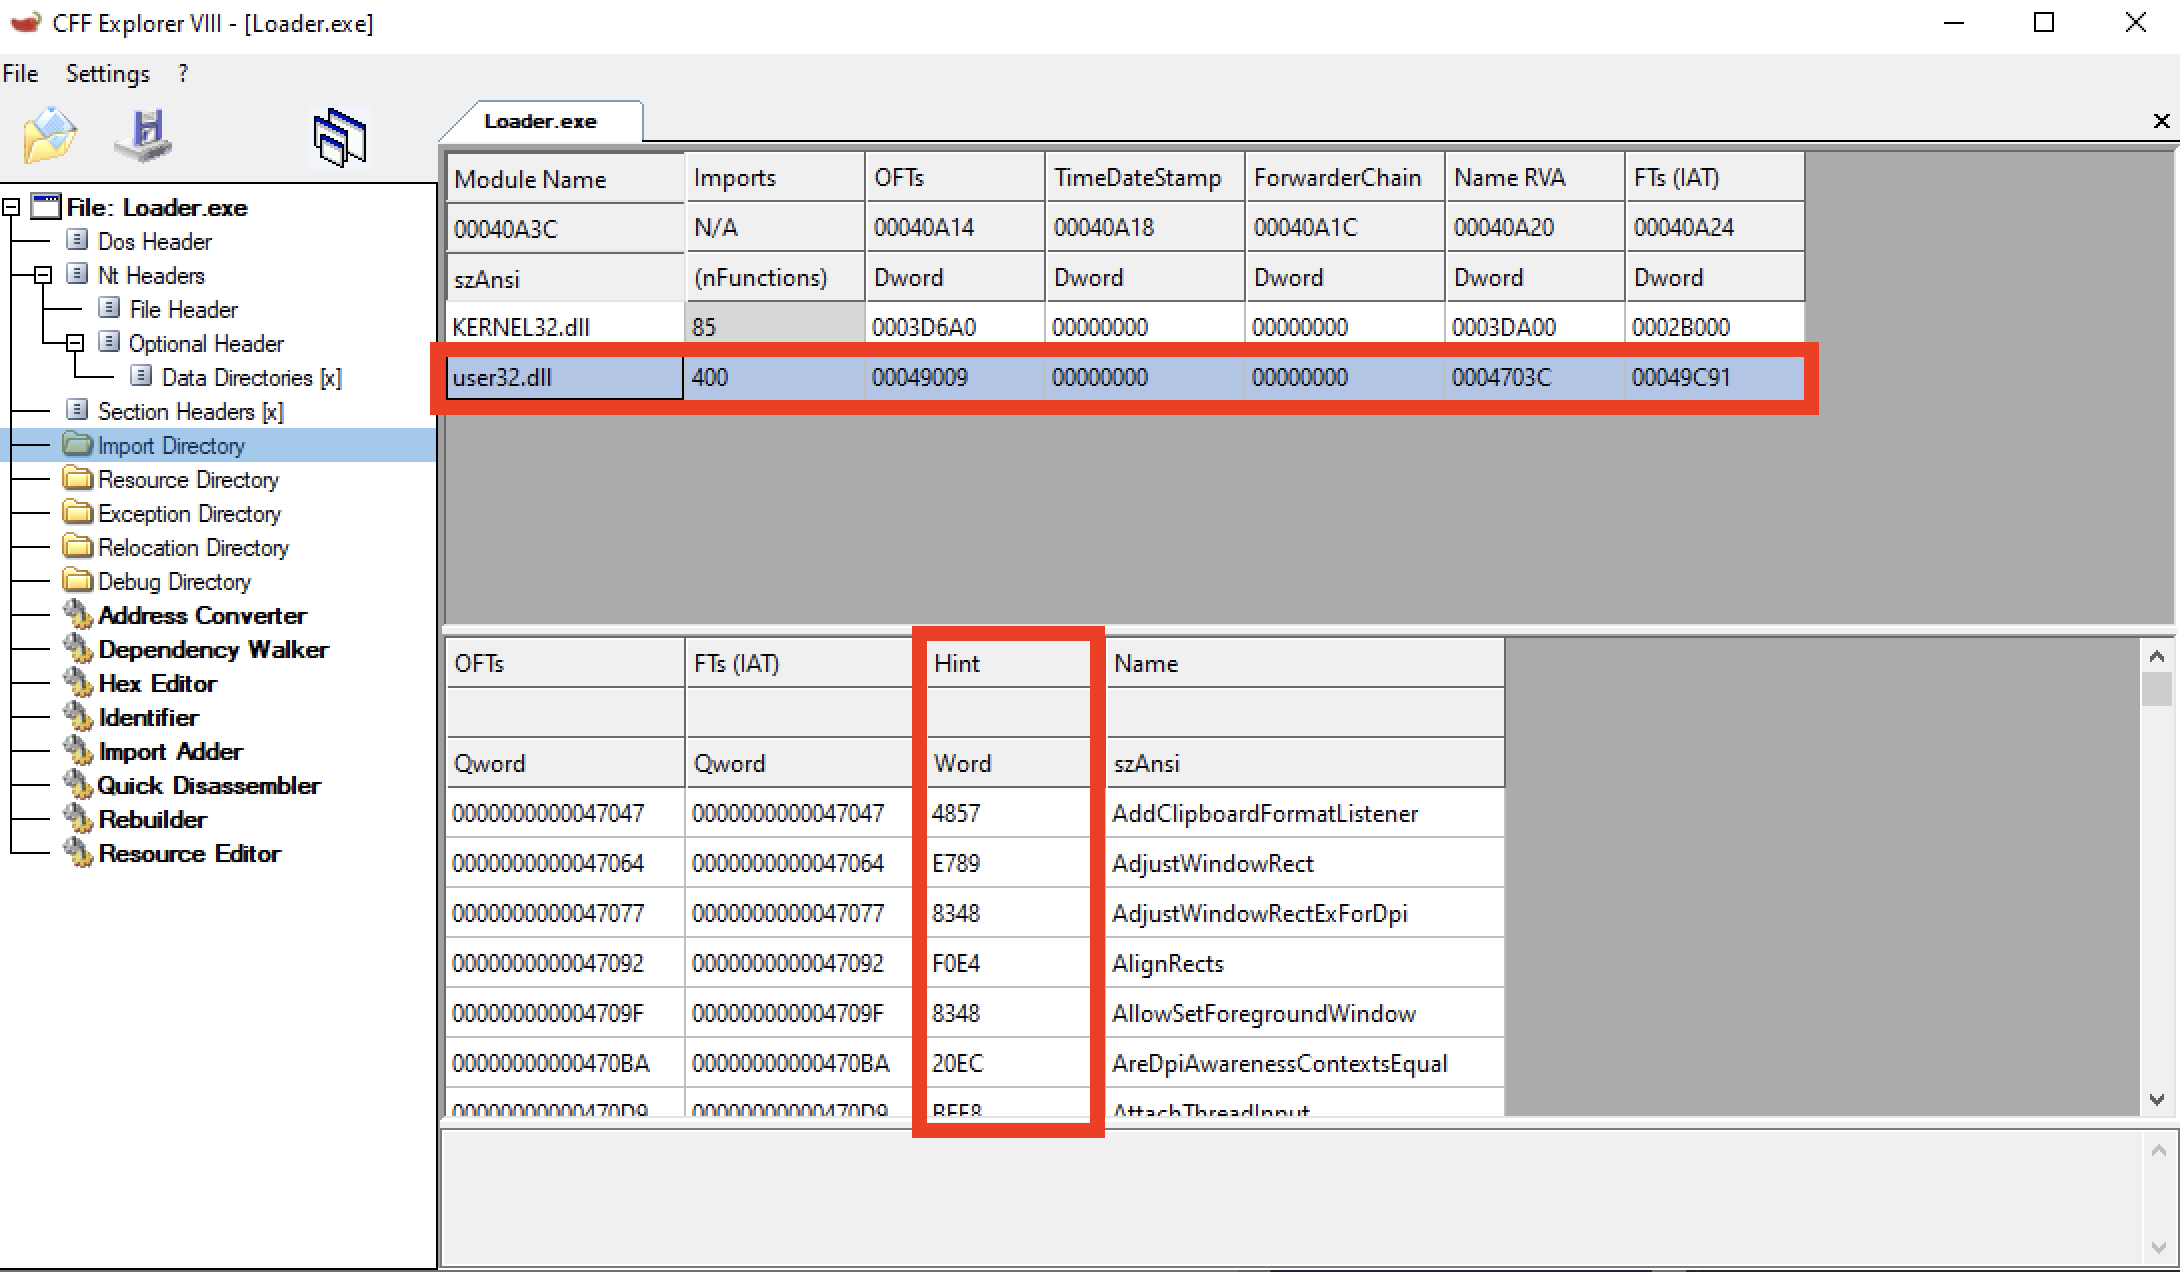 frkngksl/hintinject
A PoC project for embedding shellcode to Hint/Name Table
 0xc4r/cve-2026-21508_poc
Proof-of-concept for CVE-2026-21508, demonstrating a DLL hijacking attack on Windows 11 that escalates privileges by loading a crafted DLL into…
 radoi-teodor/cve-2023-21768-dse-bypass
Windows kernel exploit for CVE-2023-21768 that bypasses Driver Signature Enforcement (DSE) to load unsigned drivers, enabling local privilege…
 thecryinggame/cve-2022-39197-rce
CVE-2022-39197 RCE POC
 hackernese/sneakyexe
Automatic UAC-Bypassing for custom payloads during privilege escalation testing
 cerbersec/ares
Project Ares is a Proof of Concept (PoC) loader written in C/C++ based on the Transacted Hollowing technique
 artemcyberlab/project-exploiting-cve-2024-27198-rce-vulnerability
In this project, I exploited the CVE-2024-27198-RCE vulnerability to perform a remote code execution (RCE) attack on a vulnerable TeamCity server.
 deepinstinct/dcomuploadexec
DCOM Lateral movement POC abusing the IMsiServer interface - uploads and executes a payload remotely
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 showy-headteacher114/cve-2025-66398
Demonstrate exploitation of Signal K Server CVE-2025-66398 allowing unauthenticated attackers to inject backdoor and enable remote code execution.
 softdeadlock/voron-crypto
Voron messenger crypto/protocol library (X3DH-lite + Double Ratchet, group sender-keys, onion transport) — external review requested