
pedit-cow
 theendofabbys/pedit-cow
Linux kernel privilege escalation exploit for CVE-2026-46331, abusing the traffic control pedit subsystem to corrupt the page cache and execute SUID…
binary-exploitationexploitationpayload-development+2
theendofabbys/pedit-cowLinux kernel privilege escalation exploit for CVE-2026-46331, abusing the traffic control pedit subsystem to corrupt the page cache and execute SUID…
 boos4721/copyfail-rs
Rust exploit for CVE-2026-31431, a Linux kernel page-cache write primitive via AF_ALG splice, enabling privilege escalation to root through…
 morton-li/copy-fail-cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel privilege escalation, with x86_64, AArch64, and C payloads to obtain root on affected…
 danimrtzp/cve-2026-31431-revshell
Weaponized Python exploit for CVE-2026-31431, chaining Linux kernel privilege escalation to a daemonized root reverse shell with full PTY, patching…
 void0red/cve-2023-32233
Linux kernel privilege escalation exploit for CVE-2023-32233 using nft_quota UAF, ROP chain, and modprobe_path overwrite to gain root on kernels…
 sunrain/cve-2014-0196
Proof-of-concept exploit for CVE-2014-0196, a Linux kernel vulnerability, demonstrating exploitation techniques.
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 openpixelsystems/c-copy-fail
C-based exploit for CVE-2026-31431 in the Linux Kernel Crypto API, targeting aarch64 and amd64 architectures with shellcode generation and ancillary…
 1n53c/cve-2021-3156-poc
Heap-based buffer overflow exploit for CVE-2021-3156 in sudo, offering local privilege escalation to root on vulnerable Linux systems.
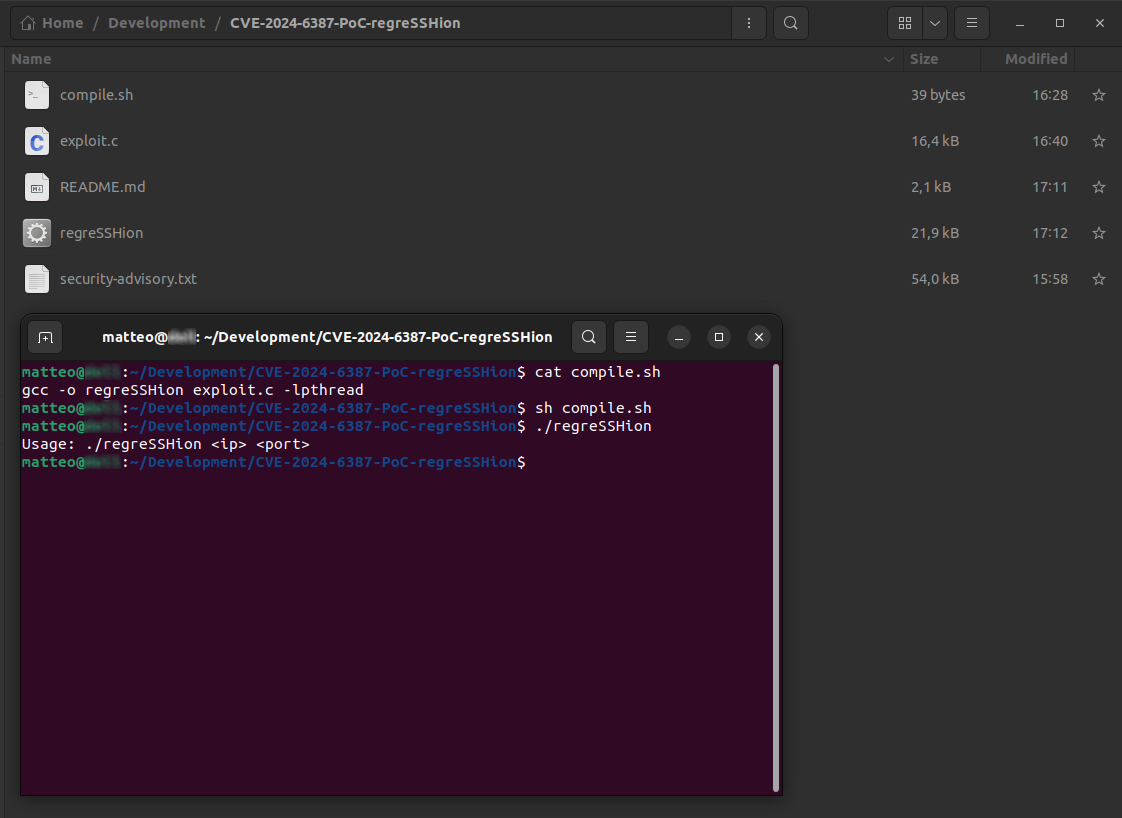 xonoxitron/regresshion
CVE-2024-6387 (regreSSHion) Exploit (PoC), a vulnerability in OpenSSH's server (sshd) on glibc-based Linux systems.
 deoxykev/cve-2021-4034-rust
Rust implementation of the CVE-2021-4034 polkit pkexec local privilege escalation exploit, with build instructions and detection considerations.
 h1sok444/cve-2026-23744-poc
Proof-of-concept exploit for CVE-2026-23744, targeting /api/mcp/connect to achieve remote command execution on Linux systems via reverse shell.
 febinrev/deepin-linux_reader_rce-exploit
CVE-2023-50254: PoC Exploit for Deepin-reader RCE that affects unpatched Deepin Linux Desktops. Deepin Linux's default document reader…
 lala-amber/cve-2024-6387
Python-based proof-of-concept exploit for CVE-2024-6387 (OpenSSH regreSSHion) targeting glibc-based 32-bit Linux systems via heap manipulation and…

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 symbolexe/cve-2024-6387
SSH Exploit for CVE-2024-6387 : RCE in OpenSSH's server, on glibc-based Linux systems
 istanescu/cve-2017-1000251_exploit
Proof-of-concept exploit for CVE-2017-1000251, demonstrating a specific vulnerability in a Linux kernel component for security testing and research.
 bytereaper77/dirty-pipe
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe) enabling local privilege escalation on Linux kernels 5.8–5.16 via pipe buffer manipulation…