mythic_telegram_profile

Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…

Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…

Gitea diffpatch RCE (CVE-2026-60004) PoC - repo-write to RCE as Gitea service account

Exploitation des vulnérabilités sur la version vsftpd 2.3.4 du service ftp (CVE-2011-2523)

This repository contains some python scripts implementation for the MS08-067 Windows Server Service vulnerability (CVE-2008-4250). This is a classic…

Exploit chain for unauthenticated RCE on Microsoft SharePoint, combining a JWT authentication bypass with unsafe .NET type instantiation to achieve…

An elevation of privilege vulnerability exists when the Windows Print Spooler service improperly allows arbitrary writing to the file system, aka…

Automated proof-of-concept exploit for CVE-2026-60004, a Gitea diffpatch Git hook RCE that plants a post-index-change hook to gain a reverse shell as…

Android 3.0 through 4.1.x on Disney Mobile, eAccess, KDDI, NTT DOCOMO, SoftBank, and other devices does not properly implement the WebView class,…

This repository contains a Metasploit module implementation for the MS08-067 Windows Server Service vulnerability (CVE-2008-4250). This is a classic…

Bash-based exploit for CVE-2026-24061 targeting telnet service, providing payload execution for penetration testing and vulnerability verification.

A Rust implementation of the POC for CVE-2017-7269, targeting the WebDAV service in Microsoft Internet Information Services (IIS) 6.0.

Proof-of-concept exploit for CVE-2023-38408, demonstrating exploitation of a remote code execution vulnerability in a targeted application or service.

Proof-of-concept exploit for CVE-2024-31771 demonstrating arbitrary file write in TotalAV via symbolic link attack, enabling DLL planting and SYSTEM…

ArcGIS Enterprise geoprocessing service that publishes a Python toolbox for command execution.

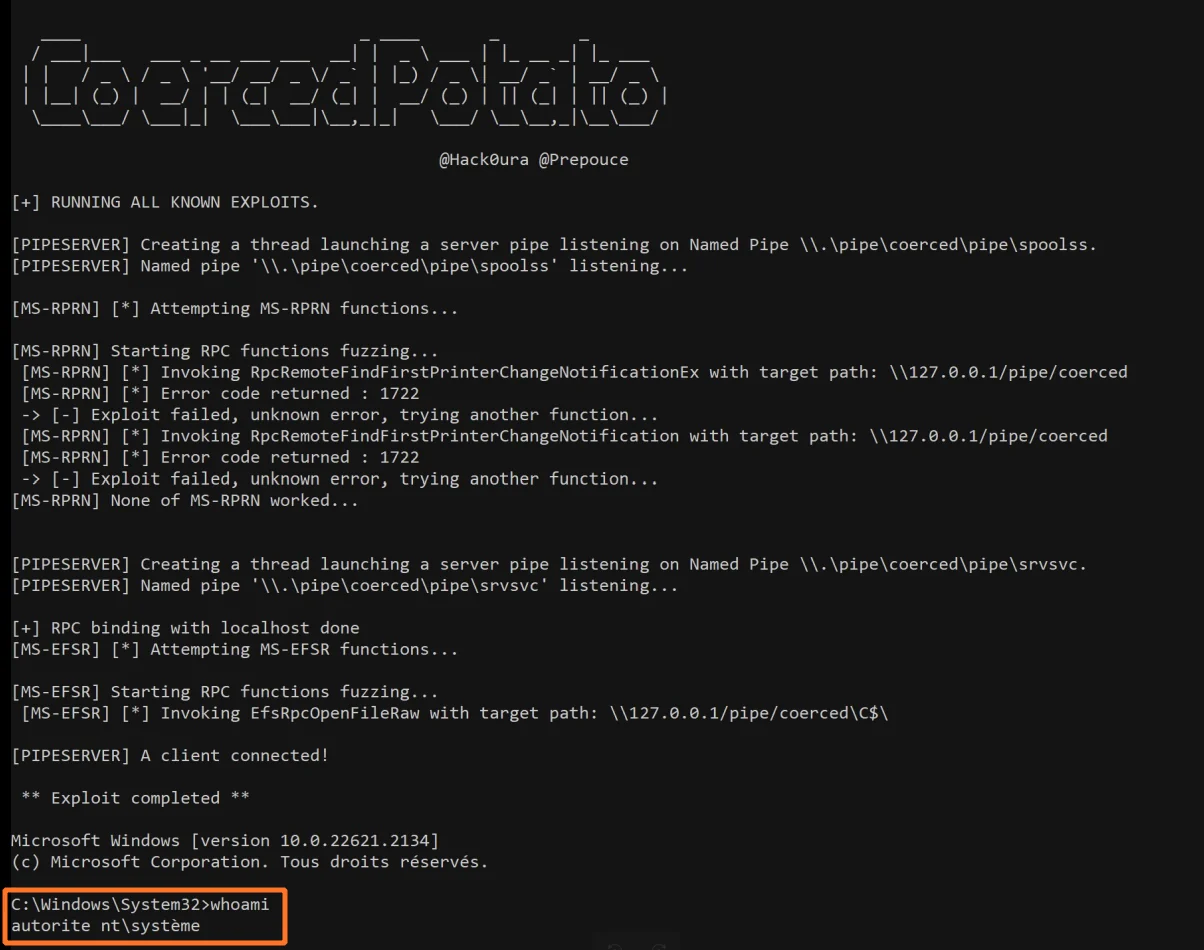
Windows local privilege escalation tool that abuses SeImpersonatePrivilege via MS-RPRN and MS-EFSR RPC coercion to execute commands as SYSTEM.

Linux bash script automation for metasploit

poc for CVE-2025-24252 & CVE-2025-24132

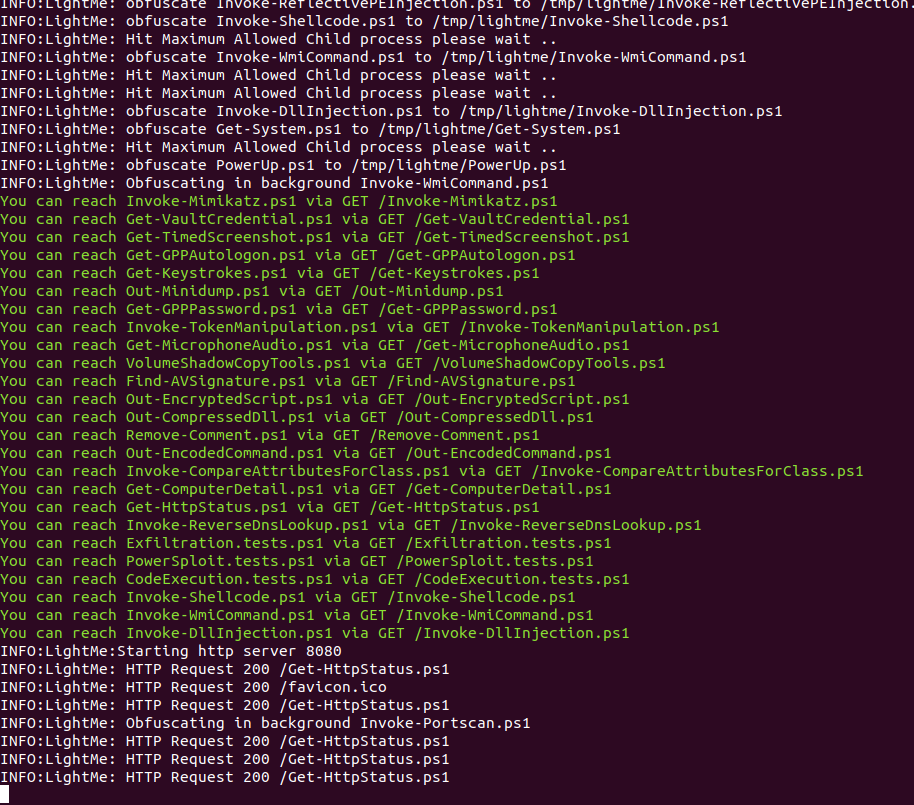
HTTP Server serving obfuscated Powershell Scripts/Payloads