

cve-2018-12386
 0xlyte/cve-2018-12386
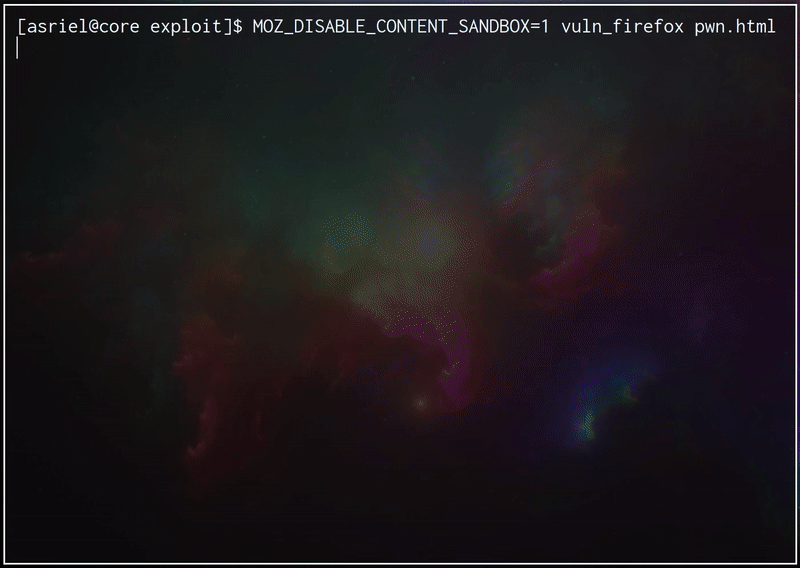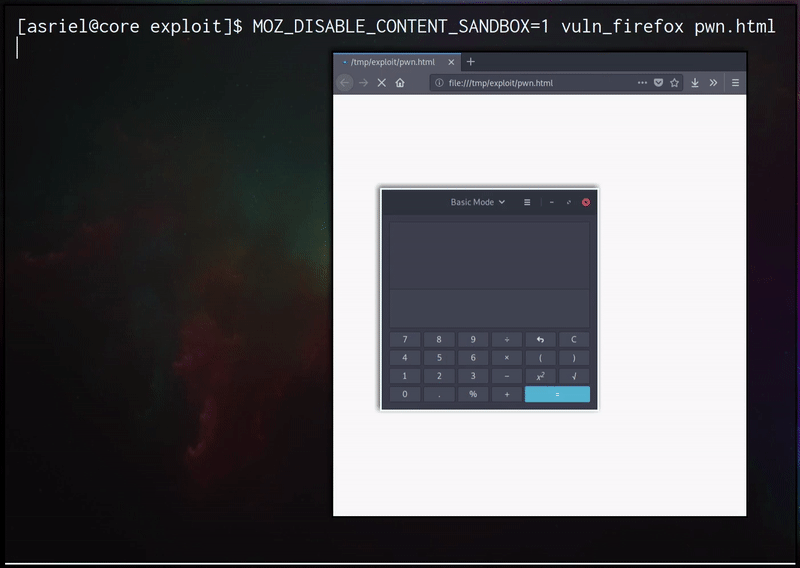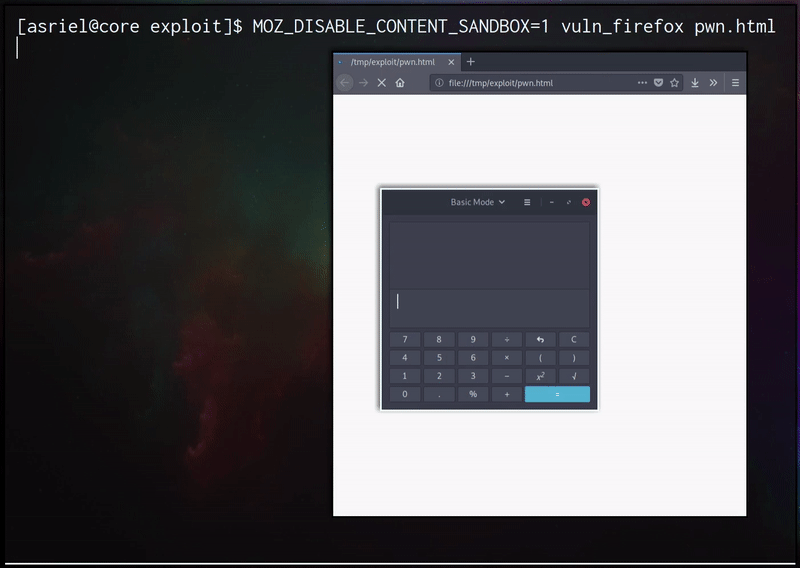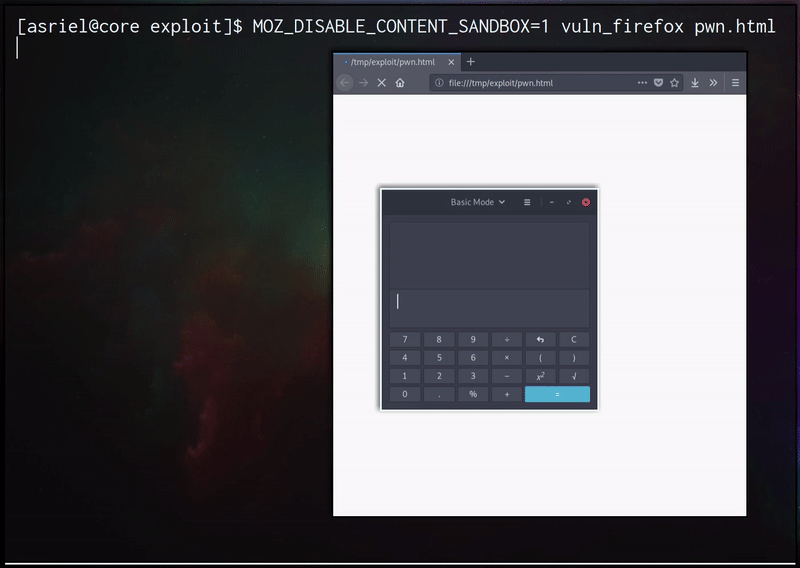
CVE-2018-12386 - Firefox Sandboxed RCE Exploit for Linux (Firefox <v62.0.3)
binary-exploitationeducationexploitation+2
26 years ago
0xlyte/cve-2018-12386CVE-2018-12386 - Firefox Sandboxed RCE Exploit for Linux (Firefox <v62.0.3)
 hydra3evil/cve-2018-12386
CVE-2018-12386 - Firefox Sandboxed RCE Exploit for Linux (Firefox <v62.0.3)
 kkirsche/slae
SecurityTube Linux Assembly Expert x86 Exam
 imkk000/play-go-copy-fail-cve-2026-31431
Educational Go implementation of a Linux syscall-based exploit for CVE-2026-31431, demonstrating payload crafting and PTY upgrade techniques for…
 jscamposx/hack
Repositorio de investigación de seguridad que contiene una Prueba de Concepto (PoC) para la vulnerabilidad CVE-2021-4034 (PwnKit) y utilidades de…
 vig9610/exploiting-samba-on-metasploitable-2
Utilize metasploit from a Kali Linux machine to exploit a well-known samba vulnerability (CVE-2007-2447). This is done in order to infiltrate a…
 gallopsled/pwntools
CTF framework and exploit development library
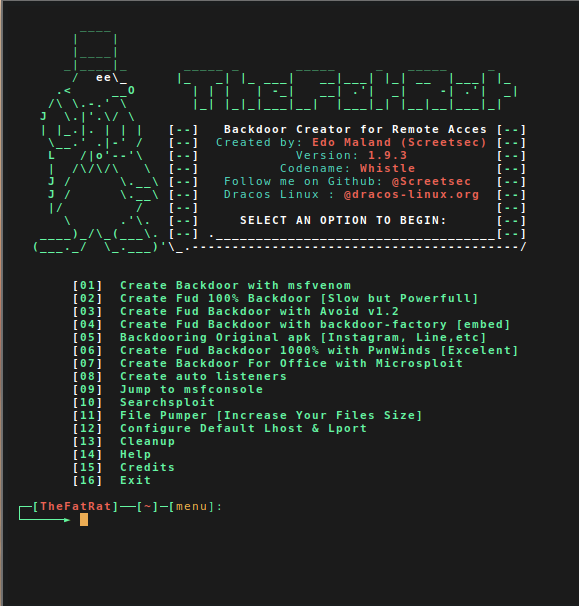 screetsec/thefatrat
Thefatrat a massive exploiting tool : Easy tool to generate backdoor and easy tool to post exploitation attack like browser attack and etc . This…
 bashfuscator/bashfuscator
A fully configurable and extendable Bash obfuscation framework. This tool is intended to help both red team and blue team.
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 arosenmund/defcon33_silence_kill_edr
Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.
 0xdea/shellcode
A collection of my shellcode samples.
 yo-yo-yo-jbo/macos_app_structure
Educational deep dive into macOS app bundles, plist files, and launchd process behavior, with offensive security notes on packaging payloads as .app…
 artbitrage/stealth-kid-rat
Stealth Kid RAT (SKR) is an open-source multi-platform Remote Access Trojan (RAT) written in C#. Released under MIT license. The SKR project is fully…
 cybertechajju/r2c-cve-2025-55182-66478
🔥 React2Shell Toolkit - CVE-2025-55182 & CVE-2025-66478
 geniuszly/cve-2024-5522
PoC exploit scanner for CVE-2024-5522 in WordPress. Scans target URLs with custom payloads to identify vulnerable sites, outputting color-coded…
 jarpex/cve-2023-4911-exploit-optimized
Pure C exploit for CVE-2023-4911 (Looney Tunables) — x86_64 & aarch64 implementations. Multi-processing brute-forcing, dynamic calibration,…
 rushikesh-a-bhujbal/cve-2011-2523
From-scratch exploit development in Python. No Metasploit. No frameworks. Raw socket-level implementation of real CVEs against authorized lab targets.