
Archived
ScareCrow
 optiv/scarecrow
ScareCrow - Payload creation framework designed around EDR bypass.
exploit-frameworkspayload-developmentpayload-generation+3
 knownsec/pocsuite
This project has stopped to maintenance, please to https://github.com/knownsec/pocsuite3 project.
 maxprog-svg/cve-2026-68820_mass_exploit
Automated local privilege escalation exploit for Windows 10/11 targeting AFD.sys use-after-free to gain SYSTEM, with PPL bypass and EDR evasion for…
 rburrito/payloadgenerator
A wrapper for MSFvenom that allows for easy generation of payloads
 s0md3v/cloak
Cloak can backdoor any python script with some tricks.
 zhzyker/exphub
Exphub[漏洞利用脚本库] 包括Webloigc、Struts2、Tomcat、Nexus、Solr、Jboss、Drupal的漏洞利用脚本,最新添加CVE-2020-14882、CVE-2020-11444、CVE-2020-10204、CVE-2020-10199、CVE-2020-1938…

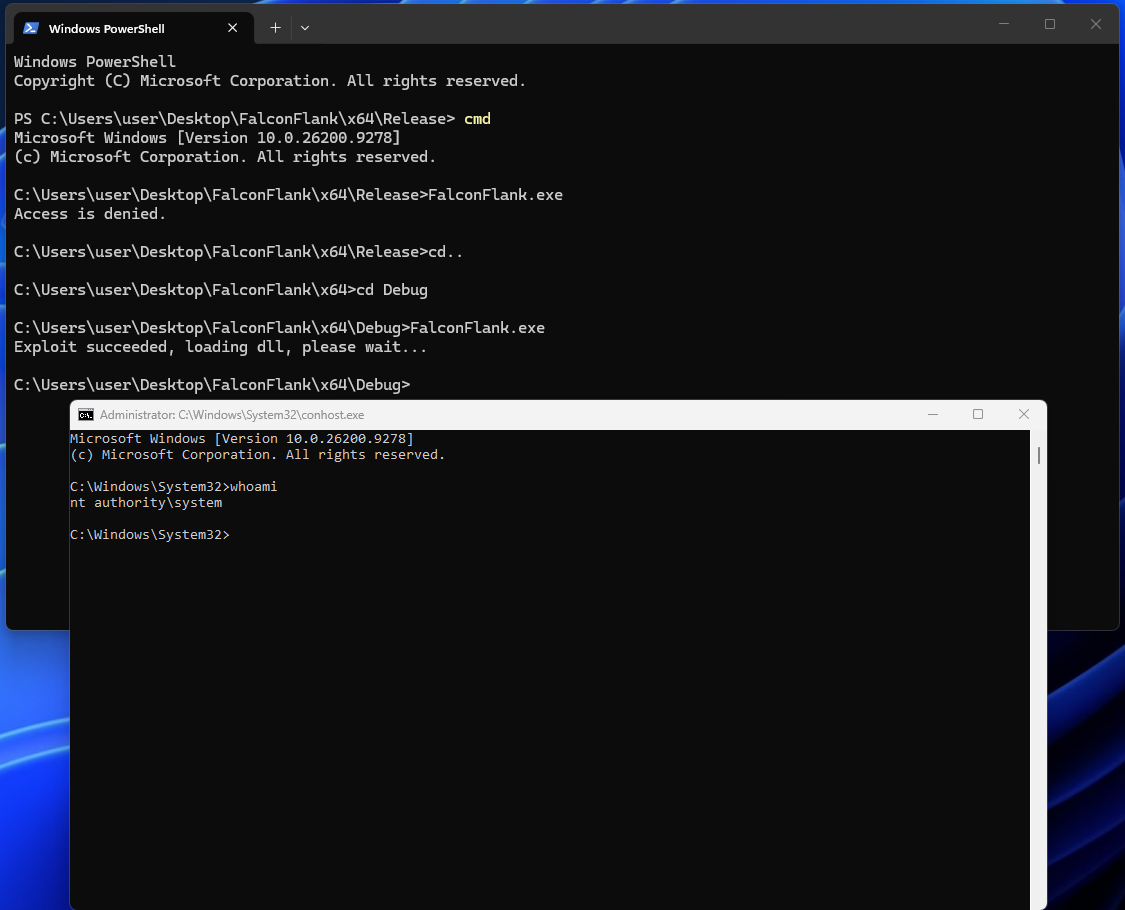 msnightmare/falconflank
Crowdstrike Falcon 0day Privilege Escalation Vulnerability
 x86byte/obfusk8
Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries
 mgeeky/threadstackspoofer
Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…
 reverseclabs/wepwnise
WePWNise generates architecture independent VBA code to be used in Office documents or templates and automates bypassing application control and…
 kyleavery/aceldr
Cobalt Strike UDRL for memory scanner evasion.
 boku7/injectamsibypass
Cobalt Strike BOF - Bypass AMSI in a remote process with code injection.
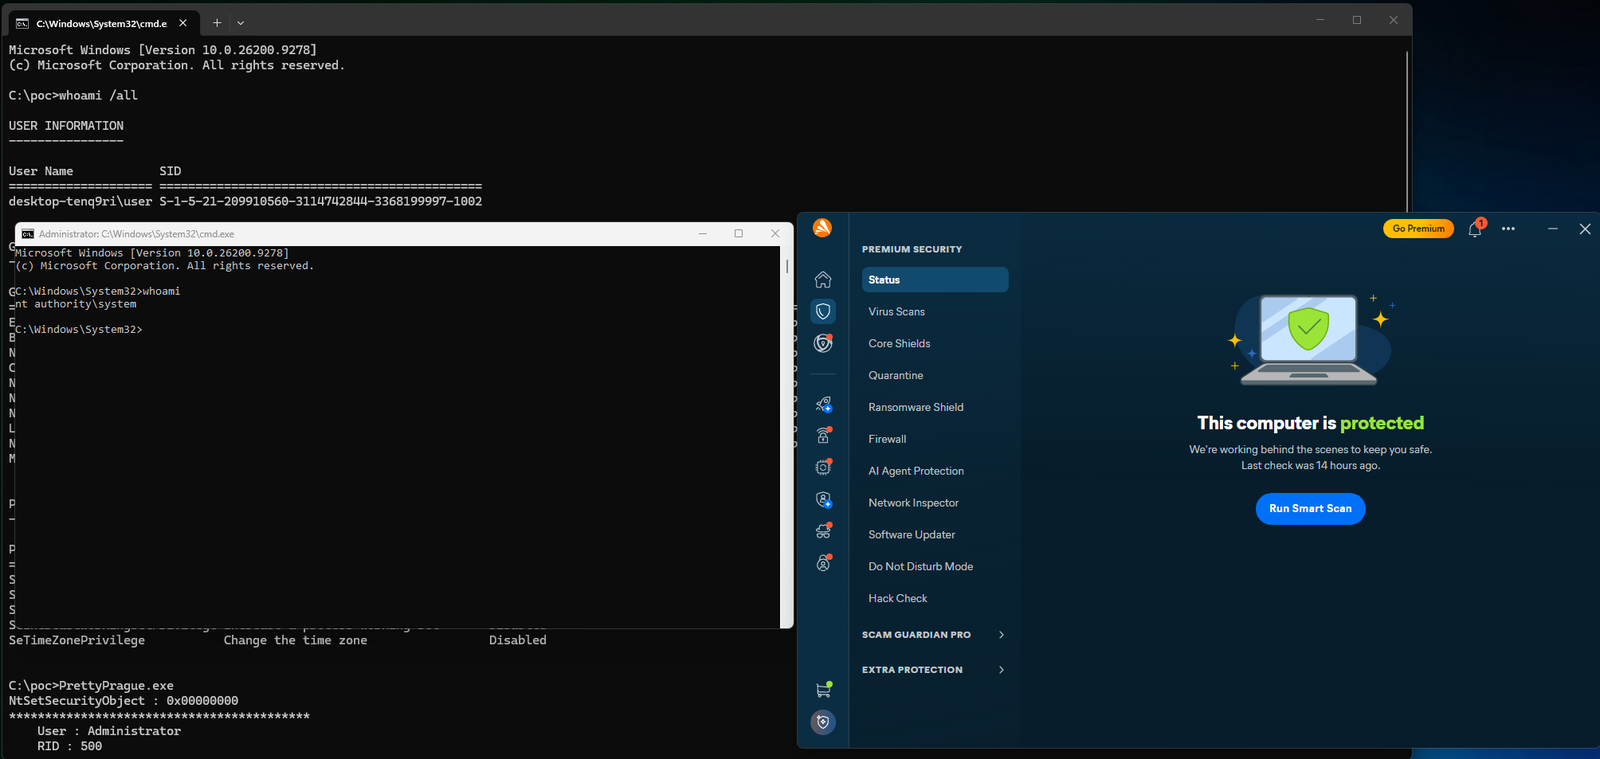 msnightmare/prettyprague
GenDigital Avast Antivirus ZeroDay Elevation of Privileges Vulnerability
 getrektboy724/betterxencrypt
A better version of Xencrypt.Xencrypt it self is a Powershell runtime crypter designed to evade AVs.
 hosch3n/proxyvulns
[ProxyLogon] CVE-2021-26855 & CVE-2021-27065 Fixed RawIdentity Bug Exploit. [ProxyOracle] CVE-2021-31195 & CVE-2021-31196 Exploit Chains.…
 hktalent/cve_2020_2546
CVE-2020-2546,CVE-2020-2915 CVE-2020-2801 CVE-2020-2798 CVE-2020-2883 CVE-2020-2884 CVE-2020-2950 WebLogic T3 payload exploit poc python3,
 n1ckdunn/exploitivator
Automate Metasploit scanning and exploitation