

0xM0nCrush
 deathshotxd/0xm0ncrush
Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.
defensive-toolsexploitationpayload-development+4
77
deathshotxd/0xm0ncrushKernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.
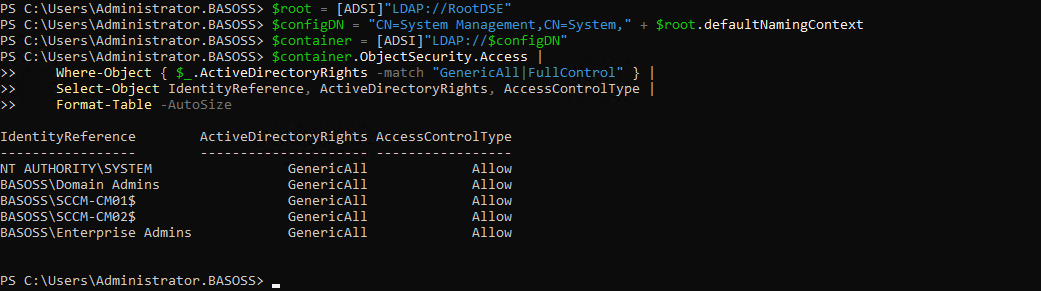 omribaso/sccm-cve-2026-47301-remote-code-execution-exploit
Proof-of-concept exploit chain (CVE-2026-47301) for Microsoft Configuration Manager (SCCM), combining a broken access, CAB arbitrary-write path…
 fsecurelabs/cve-2018-4121
macOS 10.13.3 (17D47) Safari Wasm Exploit
 mellow-hype/cve-2024-20017
exploits for CVE-2024-20017
 schierlm/javapayload
JavaPayload is a collection of pure Java payloads to be used for post-exploitation from pure Java exploits or from common misconfigurations (like not…
 l0n3m4n/cve-2024-6387
PoC - Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (Scanner and Exploit)
 jiansiting/cve-2020-0796
Proof-of-concept exploit for CVE-2020-0796 (SMBGhost) remote overflow vulnerability. Python script to check and trigger the SMBv3 compression bug on…
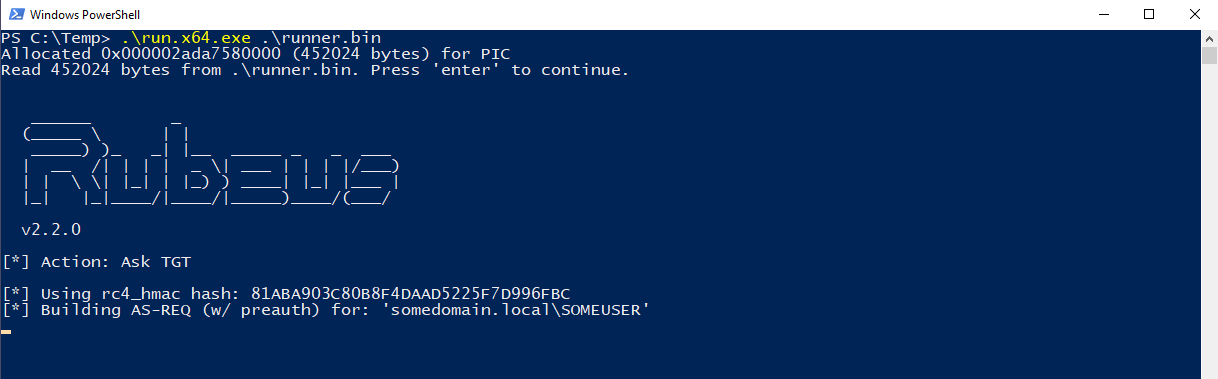 ofasgard/execute-assembly-pico
A PICO for Crystal Palace that implements CLR hosting to execute a .NET assembly in memory.
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
 csenox/semanagevolumeexploit
Windows local privilege escalation exploit abusing SeManageVolumePrivilege to grant full C:\ drive access and gain a SYSTEM shell via PrintConfig.dll…
 coolboy4me/cve-2019-0708_bluekeep_rce
it works on xp (all version sp2 sp3)
 uf0o/cve-2020-17382
PoC exploits for CVE-2020-17382
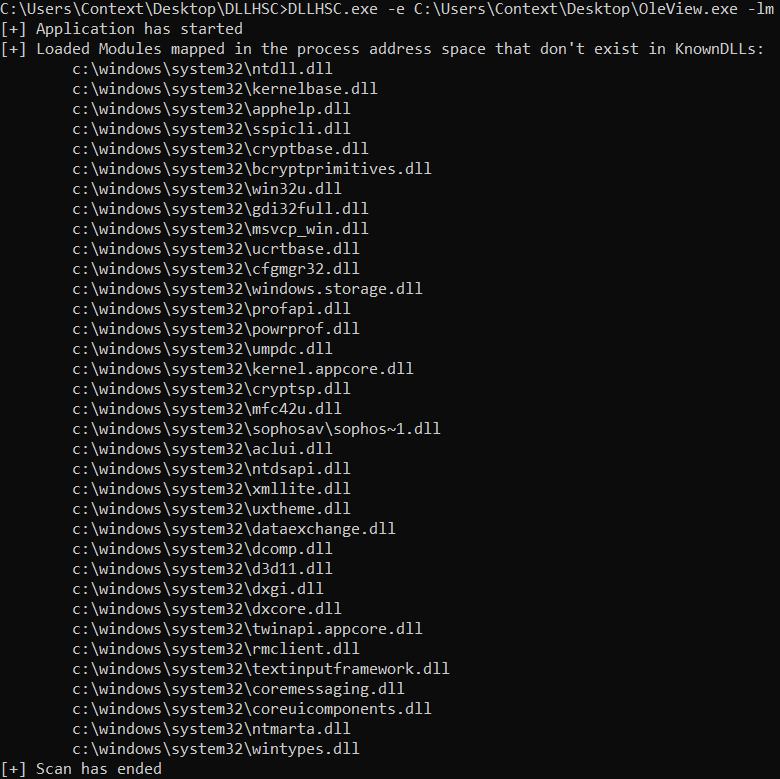 ctxis/dllhsc
Automated scanner for discovering DLL search order hijacking candidates in Windows executables, featuring import table parsing, runtime module…
 assetnote/cpanel2shell-scanner
High fidelity scanner for CVE-2026-41940 (cPanel & WHM authentication bypass)
 y4er/openam-cve-2021-35464
openam-CVE-2021-35464 tomcat 执行命令回显
 codewhitesec/httpremotingobjrefleak
Additional resources for leaking and exploiting ObjRefs via HTTP .NET Remoting (CVE-2024-29059)
 cyberstruggle/chalumeau
Chalumeau is automated,extendable and customizable credential dumping tool based on powershell and python.
 kpcyrd/sh4d0wup
Signing-key abuse and update exploitation framework