CVE-2026-65643-PoC-Toolkit

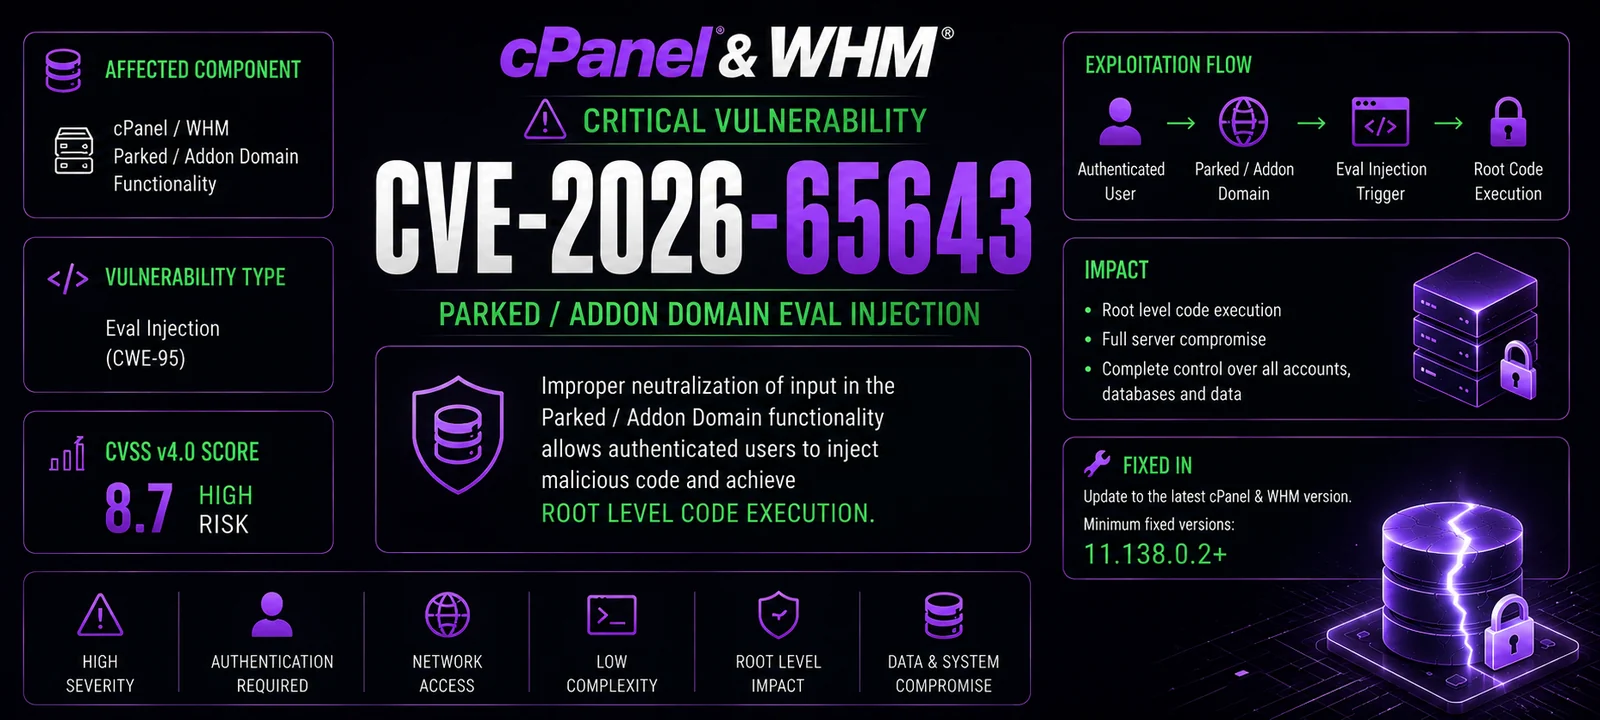
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…

Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…

self cleaning CVE-2025-27591 Poc that grants a root reverse shell instead of modifying passwd files

CVE 2025 27237 Zabbix LPE proof of concept.

Use after free in Windows Common Log File System Driver allows an authorized attacker to elevate privileges locally.

Data-only exploit for CVE-2024-0582

64-bit Windows kernel privilege escalation exploit for CVE-2016-0040 (WMI Receive Notification vulnerability) using GDI bitmap manipulation for token…

Standalone Python 3 exploit for CVE-2017-17562 targeting GoAhead web server 2.5–3.6.5 with automated CGI endpoint discovery and reverse shell payload…

Proof-of-concept backdoor for SCCM Management Point using rogue COM service for persistent remote command execution as SYSTEM.

Proof-of-concept exploit for CVE-2024-3400, demonstrating command injection in Palo Alto PAN-OS with a Python-based backdoor, persistence via…

CVE-2024-53691

Shellcodes for Windows >= 11 x64

POC exploit code for CVE-2020-1048(PrintDemon)

Proof-of-concept exploit for CVE-2020-8289 demonstrating remote code execution as SYSTEM/root via Backblaze backup client's SSL verification bypass…

bin2shell is very small utils for extract shell code from the binary file

CVE-2024-37032 (Probllama) PoC for Ollama ≤0.1.33: path traversal and arbitrary file write via model digest handling, leading to automated privilege…

Python-based exploit and reverse shell payload generator for CVE-2023-42115, featuring scan and exploit modes with cross-platform payload creation.

My exploit for CVE-2024-48990. Full details of how I made this are on my blog.

USB Rubber Ducky payload that exploits CVE-2021-4034 to escalate privileges and spawn a root shell on Unix-like systems in under 10 seconds.