Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
1103 results
metasploit-framework preview

metasploit-framework

GitHubrapid7/metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

command-and-controldatabase-securitydata-exfiltration+20
39.3k
12h 15m ago
Exploits preview

Exploits

GitHubkmkz/exploits

Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…

command-and-controlcontainer-escapeeducation+6
2281 day ago
CVE-2026-33017-Langflow-RCE preview

CVE-2026-33017-Langflow-RCE

GitHubindustri4l-h3ll-xpl0it3rs/cve-2026-33017-langflow-rce

CVE-2026-33017 Exploit | by infrar3d

educationexploitationpayload-development+3
14 days ago
CVE-2026-90847 preview

CVE-2026-90847

GitHubshlln/cve-2026-90847

Proof-of-concept for CVE-2026-90847, an authenticated RCE in iux_set.cgi via malicious .cfg tar upload that writes commands into crontab for…

embedded-systems-securityexploitationiot-security+5
15 days ago
cve-2025-66398 preview

cve-2025-66398

GitHubshowy-headteacher114/cve-2025-66398

Demonstrate exploitation of Signal K Server CVE-2025-66398 allowing unauthenticated attackers to inject backdoor and enable remote code execution.

exploitationpayload-developmentpenetration-testing+3
117 days ago
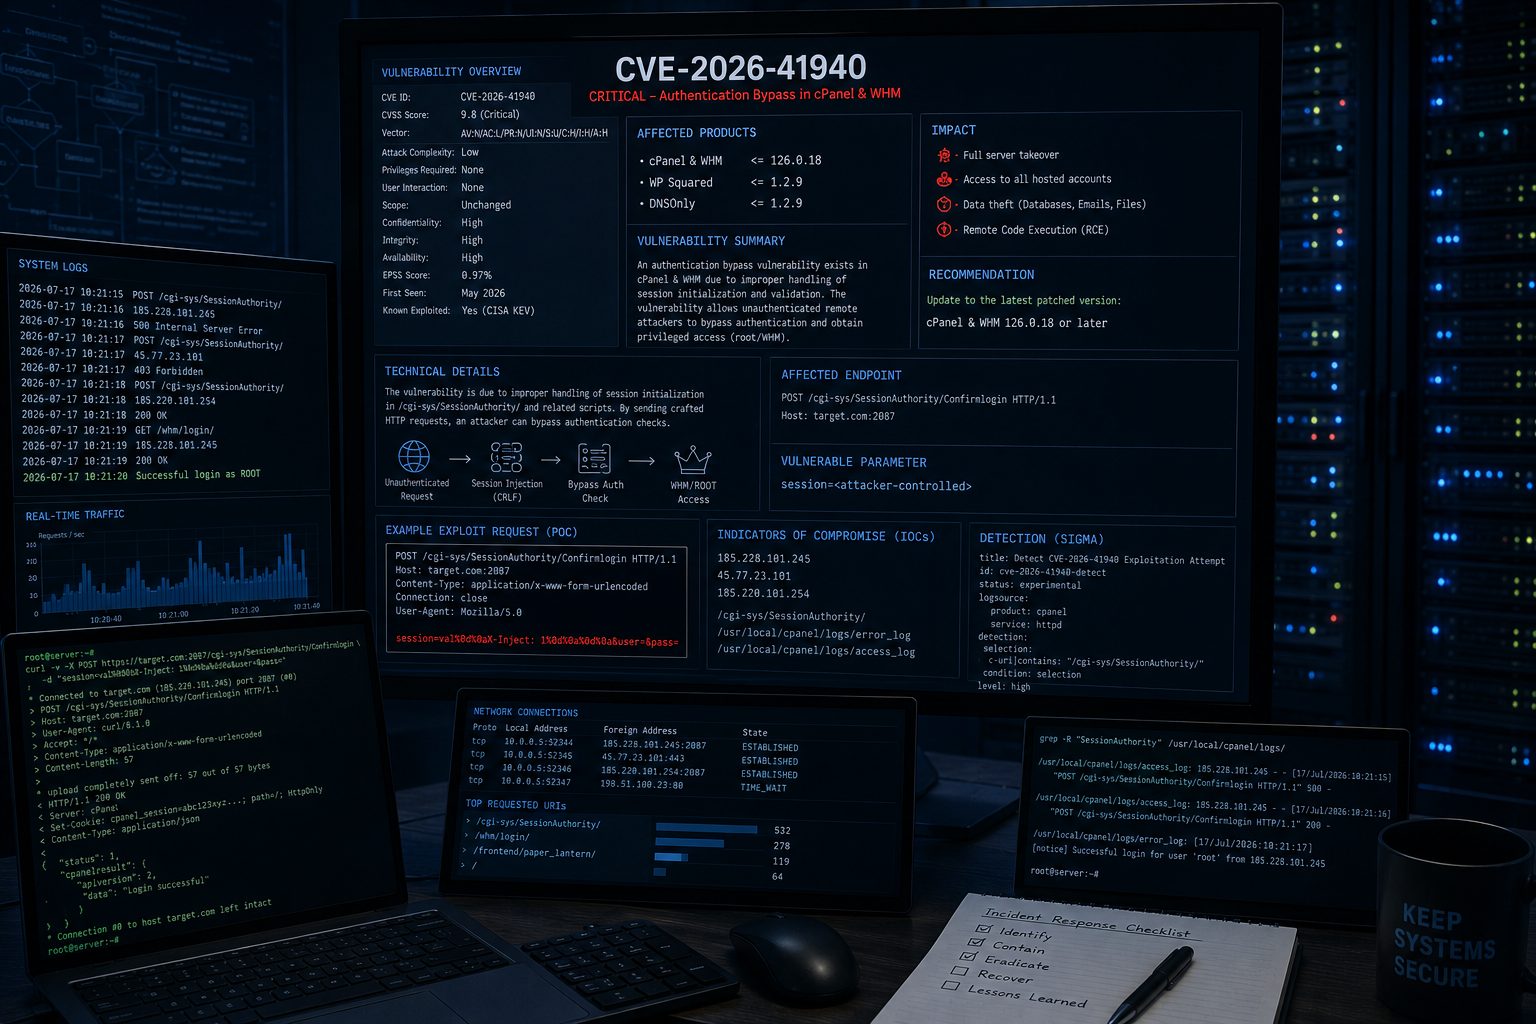
CVE-2026-41940-PoC-Exploit preview

CVE-2026-41940-PoC-Exploit

GitHubtc4dy/cve-2026-41940-poc-exploit

PoC exploit for CVE-2026-41940 targeting cPanel/WHM authentication bypass via CRLF injection. Supports session hijacking, RCE, reverse shell, mass…

authentication-authorizationcommand-and-controlexploitation+8
1118 days ago
CVE-2025-8110 preview

CVE-2025-8110

GitHubghxstsec/cve-2025-8110

Proof-of-concept exploit for CVE-2025-8110, a Gogs RCE vulnerability exploiting path traversal via symbolic links and sshCommand injection to deliver…

exploitationpayload-developmentpenetration-testing+3
518 days ago
CVE-2025-55182 preview

CVE-2025-55182

GitHub0xblackash/cve-2025-55182

Proof-of-concept exploit for CVE-2025-55182: unauthenticated RCE in React Server Components via unsafe deserialization, enabling arbitrary command…

exploitationpayload-developmentpenetration-testing+3
22 days ago
CVE-2026-65643-PoC-Toolkit preview

CVE-2026-65643-PoC-Toolkit

GitHubtc4dy/cve-2026-65643-poc-toolkit

Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…

command-and-controlexploitationpayload-development+7
1422 days ago
CVE-2026-102489 preview

CVE-2026-102489

GitHubhorizon3ai/cve-2026-102489

Proof-of-concept exploit for CVE-2026-102489 in Zammad: chains a WebSocket session leak into authenticated session hijacking and unauthenticated…

exploitationpayload-developmentpost-exploitation+4
624 days ago
CVE-2024-56426 preview

CVE-2024-56426

GitHubcreeeeger/cve-2024-56426

A PoC of the CVE-2024-56426 vulnerability.

binary-exploitationembedded-systems-securityexploitation+6
1728 days ago
CVE-2026-31857 preview

CVE-2026-31857

GitHub0xtatsuki/cve-2026-31857

Craft CMS RCE via relational conditionals in the control panel

exploitationpayload-developmentpenetration-testing+6
29 days ago
CVE-2026-103441 preview

CVE-2026-103441

GitHubbombobombone/cve-2026-103441

Local proof-of-concept and sanitized report for CVE-2026-103441, a PHP object-injection flaw in the MediaWiki action=parse API that can reach RCE via…

exploitationpapers-researchpayload-development+3
1 month ago
CVE-2026-6951 preview

CVE-2026-6951

GitHubeqstlab/cve-2026-6951

Proof-of-concept exploit for CVE-2026-6951, a simple-git --config filter bypass enabling RCE via the Git ext protocol, with a Docker lab and reverse…

exploitationpayload-developmentpenetration-testing+4
21 month ago
CVE-2020-14882 preview

CVE-2020-14882

GitHubmilo2012/cve-2020-14882

CVE-2020-14882

command-and-controlexploitationpayload-development+3
81 month ago
SC3010-Computer-Security preview
Archived

SC3010-Computer-Security

GitHubaipeacs/sc3010-computer-security

Using Struts2 and PowerShell to recreate CVE-2017-5638 OGNL Injection vulnerability.

code-analysiseducationexploitation+6
1 month ago
CVE-2026-86218 preview

CVE-2026-86218

GitHubsuper-meuw/cve-2026-86218

Python 3 proof-of-concept exploit for CVE-2026-86218, a pre-auth RCE in N-able N-central via a Struts multipart race condition, with command…

exploitationpayload-developmentpenetration-testing+5
1 month ago
CVE-2026-91097-CVE-2026-91106 preview

CVE-2026-91097-CVE-2026-91106

GitHubnxploited/cve-2026-91097-cve-2026-91106

HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)

defensive-toolsexploitationinformation-gathering+7
11 month ago
Previous12…62Next