
Comment2Shell
 deathshotxd/comment2shell
Zero-click pre-auth WordPress CVE-2026-93485 exploit chain: stored XSS in wpautop() escalates to admin-session plugin upload and a self-deleting…
exploitationlabs-practicepayload-development+7
64
deathshotxd/comment2shellZero-click pre-auth WordPress CVE-2026-93485 exploit chain: stored XSS in wpautop() escalates to admin-session plugin upload and a self-deleting…
 joaovicdev/exploit-cve-2026-87902
Lab vulnerável (Docker) + PoC Python para a CVE-2026-87902 — path traversal não autenticado no WordPress Core (page-template -> LFI -> RCE…
 hassham1/cve-2026-87902
WordPress Core <= 7.1.1 unauthenticated LFI to RCE - validation lab, PoC, nuclei template (GHSA-7hp8-65ch-5whp)
 dinosn/cve-2026-87902-wordpress-lfi-lab
Reproduction lab + URL-list scanner + PoC for CVE-2026-87902 / GHSA-7hp8-65ch-5whp — WordPress get_page_template() unauthenticated LFI to conditional…
 0xcyp1337/cve-2026-82222-massexploit
Exploit tool for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports single-target and batch exploitation with…
 boreas37/cve-2026-64638-poc-xss2shell-
XSS2Shell (CVE-2026-64638) WordPress pre-auth XSS to RCE chain — PoC exploit + defensive audit tool + nuclei template
 anggatechi/cve-2026-3844
CVE-2026-3844 — Unauthenticated Arbitrary File Upload to RCE in Breeze Cache (WordPress). CVSS 9.8 CRITICAL. Mass scanner + auto shell injector with…
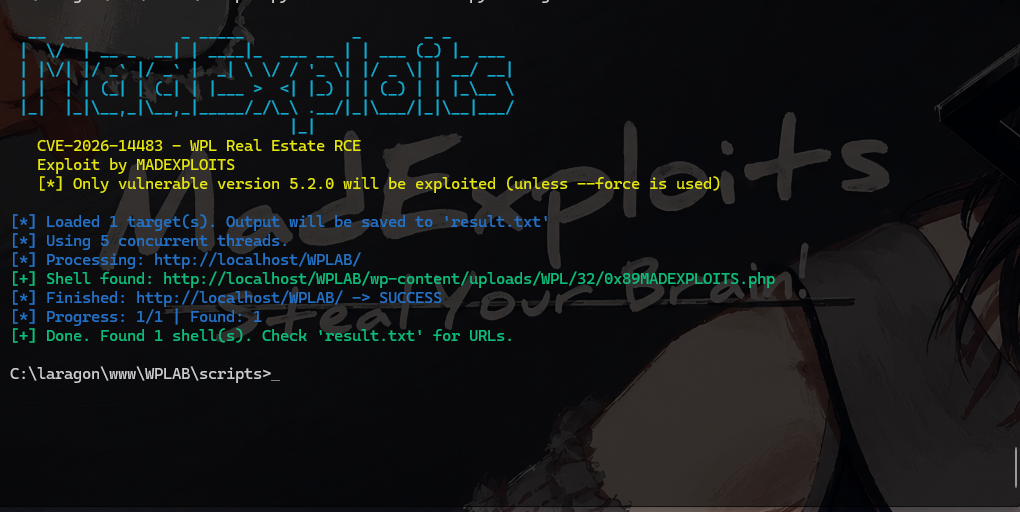 madexploits/cve-2026-14483
CVE-2026-14483 POC EXPLOIT BY MADEXPLOITS
 ghostpels/cve-2026-13001
Exploit for CVE-2026-13001: Unauthenticated RCE in Podlove Podcast Publisher via extension confusion. Includes mass scanning, interactive shell, and…
 bahartanir/wp2shell-scanner
CVE-2026-63030 / CVE-2026-60137 - WordPress pre-auth RCE scanner
 cerberusmrxi/wp-bricks-exploit-cve-2024-25600
CVE-2024-25600 - Unauthenticated RCE exploit for WordPress Bricks Builder Theme. Advanced exploitation framework with interactive shell, reverse…
 cerberusmrxi/wp-contest-gallery-28.1.4-exploit
Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…
 murrez/cve-2026-6433
PoC for CVE-2026-6433: WordPress FlipperCode Custom CSS, JS & PHP (≤2.0.7) — unauthenticated SQLi to RCE. Python 3 stdlib; single target or bulk…
 willygailo/wg-cve-2026-1555-linux
Automated exploit toolkit for CVE-2026-1555, a critical unauthenticated file upload RCE in the WebStack WordPress theme. Features PyQt5 GUI,…
 jenderal92/cve-2026-4885
Piotnet Addons for Elementor Pro <= 7.1.70 - Unauthenticated Arbitrary File Upload via Form File Upload
 xshadow-here/cve-2026-4885
Piotnet Addons for Elementor Pro <= 7.1.70 - Unauthenticated Arbitrary File Upload → RCE
 murrez/cve-2026-0911
Authenticated PoC for CVE-2026-0911: tests weak file upload and orphan file behavior in WordPress Hustle plugin's module import endpoint, with…
 nxploited/cve-2025-2563
The User Registration & Membership WordPress plugin before 4.1.2 does not prevent users to set their account role when the Membership Addon is…