
COFFLoader
 trustedsec/coffloader
Run Beacon Object Files (BOFs) outside Cobalt Strike by parsing 64-bit COFF object files, with Beacon-compatible argument generation and helper…
binary-analysispayload-developmentpenetration-testing+2
659
trustedsec/coffloaderRun Beacon Object Files (BOFs) outside Cobalt Strike by parsing 64-bit COFF object files, with Beacon-compatible argument generation and helper…
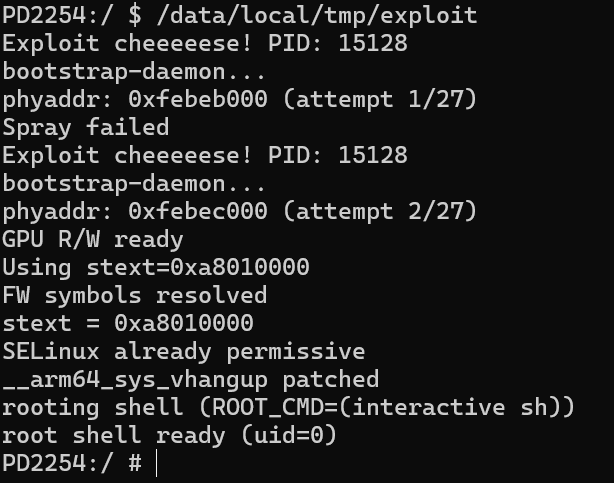 xianwan1314/cve-2025-21479-iqoo11pro
CVE-2025-21479 (Qualcomm Adreno GPU) reproduction notes for vivo iQOO 11 Pro (PD2254) - authorized research
 flangvik/obfuscatedsharpcollection
Attempt at Obfuscated version of SharpCollection
 bytereaper77/dirty-pipe
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe) enabling local privilege escalation on Linux kernels 5.8–5.16 via pipe buffer manipulation…
 kuzeyardabulut/cve-2024-0582
Data-only exploit for CVE-2024-0582
 louiselalanne/cve-2024-23745
In Notion Web Clipper 1.0.3(7), a .nib file is susceptible to the Dirty NIB attack.
 joeymeech/cve-2022-0847-exploit-implementation
Using CVE-2022-0847, "Dirty Pipe Exploit", to pop a reverse bash shell for arbitrary code execution on a foreign machine.
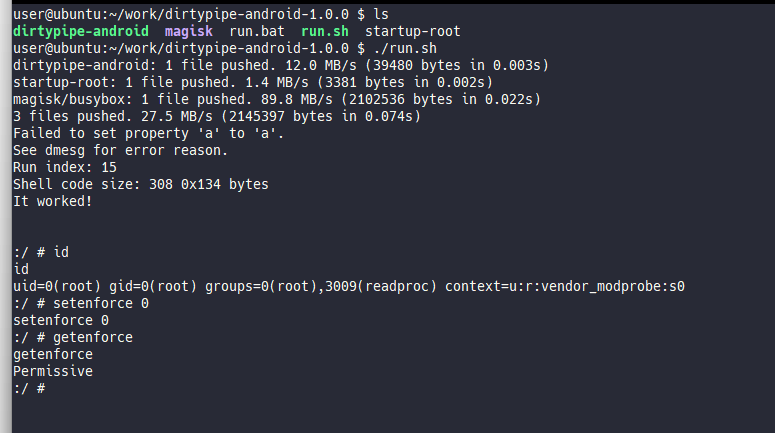 polygraphene/dirtypipe-android
Dirty Pipe root exploit for Android (Pixel 6)
 ludovicpatho/cve-2022-0847_dirty-pipe
Hacked up Dirty Pipe (CVE-2022-0847) PoC that hijacks a SUID binary to spawn a root shell. (and attempts to restore the damaged binary as well)
 syfi/cve-2018-4878
Flash Exploit Poc