

ultrasploiter
 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
command-and-controlexploitationexploit-frameworks+9
vqkro/ultrasploiterA single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…

 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 r41n3rzuf477/ps-ppl-bypass
Process Explorer vulnerable driver PPL Bypass
 tc4dy/cve-2026-54121-poc-exploit
👻 CVE-2026-54121 - Best CertiGhost AD CS Multi-Exploit Framework | Advanced toolkit with rogue DC/LDAP servers, certificate abuse, PKINIT hash…
 dagowda/notrdp
Havoc C2 plugin that creates a hidden Windows desktop, streams it to a browser viewer, and injects mouse/keyboard input for covert remote control.
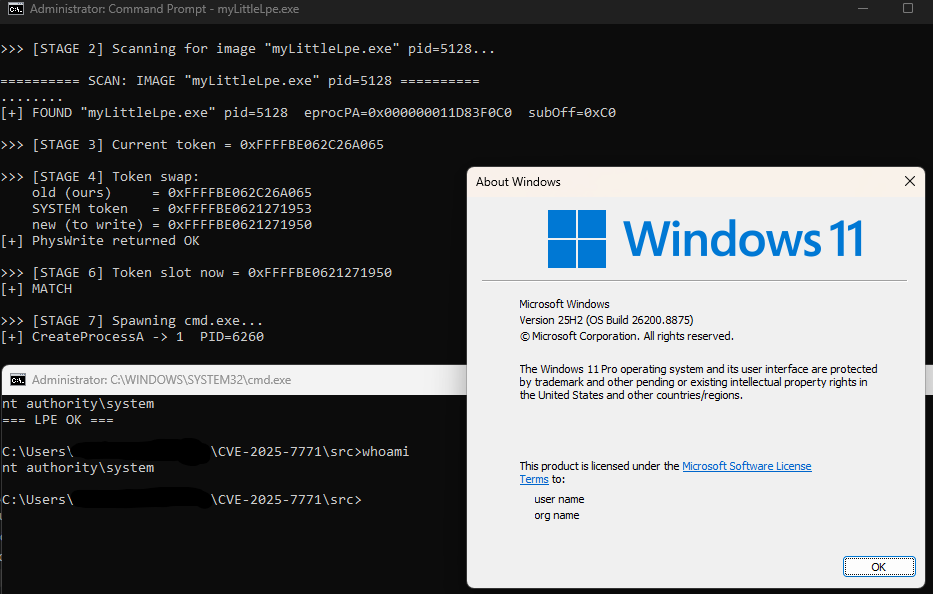 yulisec/cve-2025-7771
Full exploit chain for CVE-2025-7771 in ThrottleStop.sys, abusing unvalidated physical memory R/W IOCTLs to escalate from administrator to SYSTEM on…
 nxploited/cve-2026-91097-cve-2026-91106
HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)
 28zaaky/khaos-c2
KHAOS is a modern C2 framework that routes agent traffic through cloud services already trusted by enterprise networks.
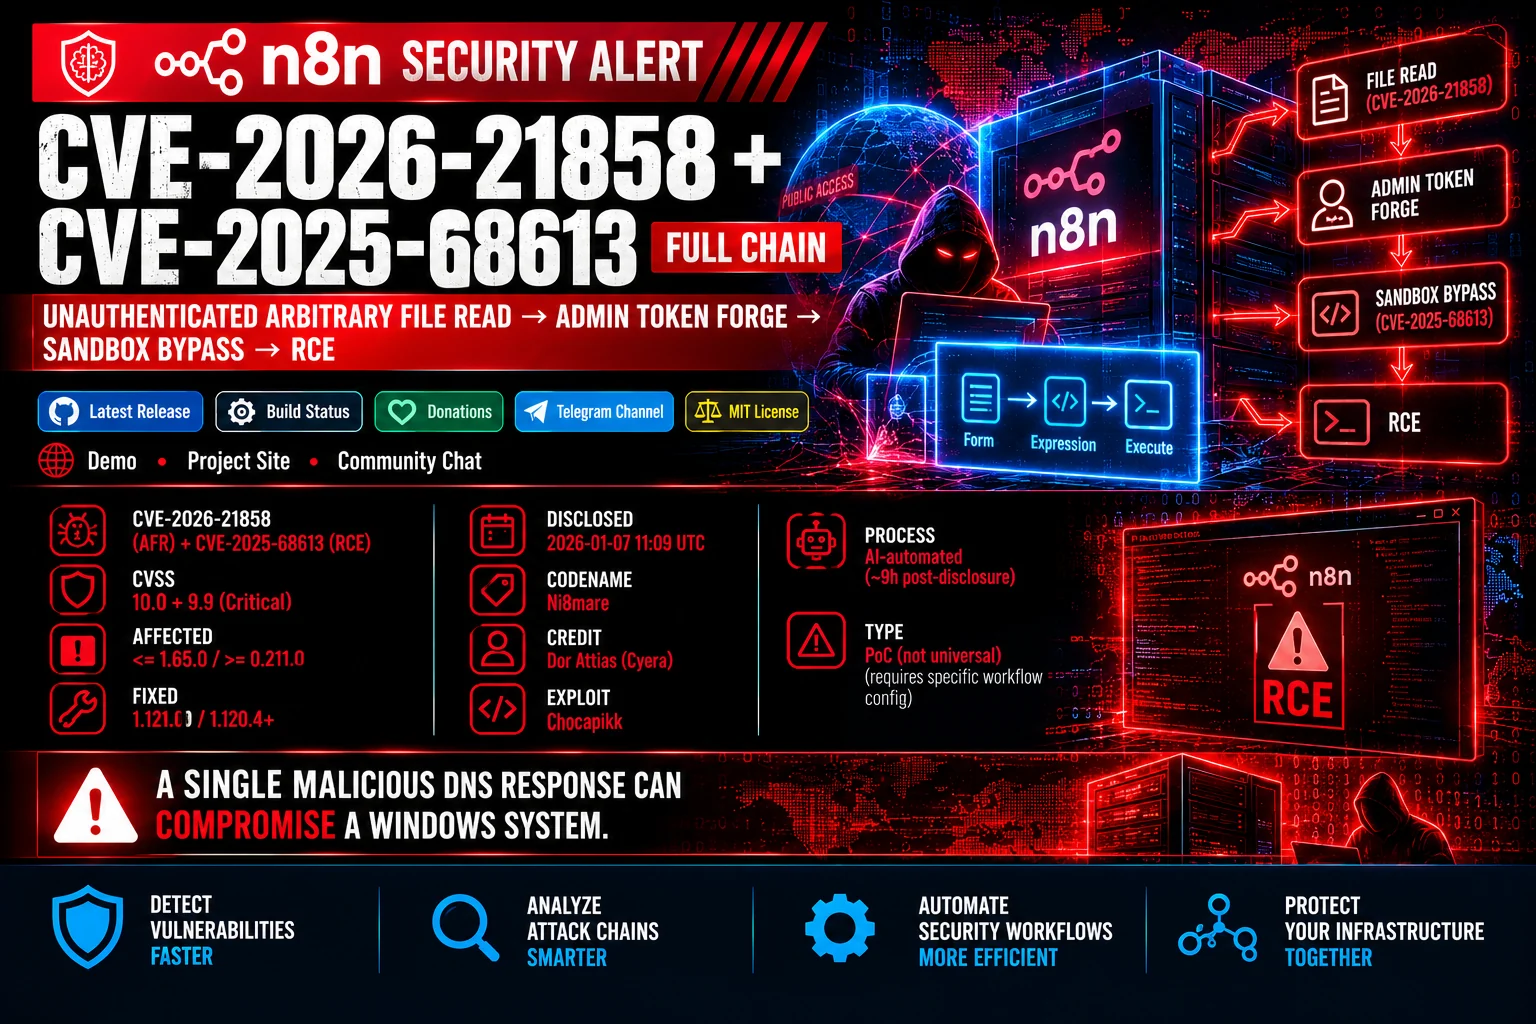 zerodayevil/cve-2026-21858-n8n-fullchain
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…
 vsvalinx/cve-2025-5548
Educational repository documenting the full exploitation lifecycle of a stack buffer overflow in FreeFloat FTP Server 1.0, including fuzzing, EIP…
 abraxas/veneficus
Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.
 abraxas/veneficus-implant-public
Spicy malware 0day. Full kill-chain malware: exploit, pivot, c2, persistence. Rust converted to pseudo-code - if you're smart you can build it…
 hackspeak/cve-2026-62735
Local privilege escalation exploit for Windows HTTP.sys integer overflow (CVE-2026-62735), demonstrating crash and full SYSTEM shell via nonpaged…
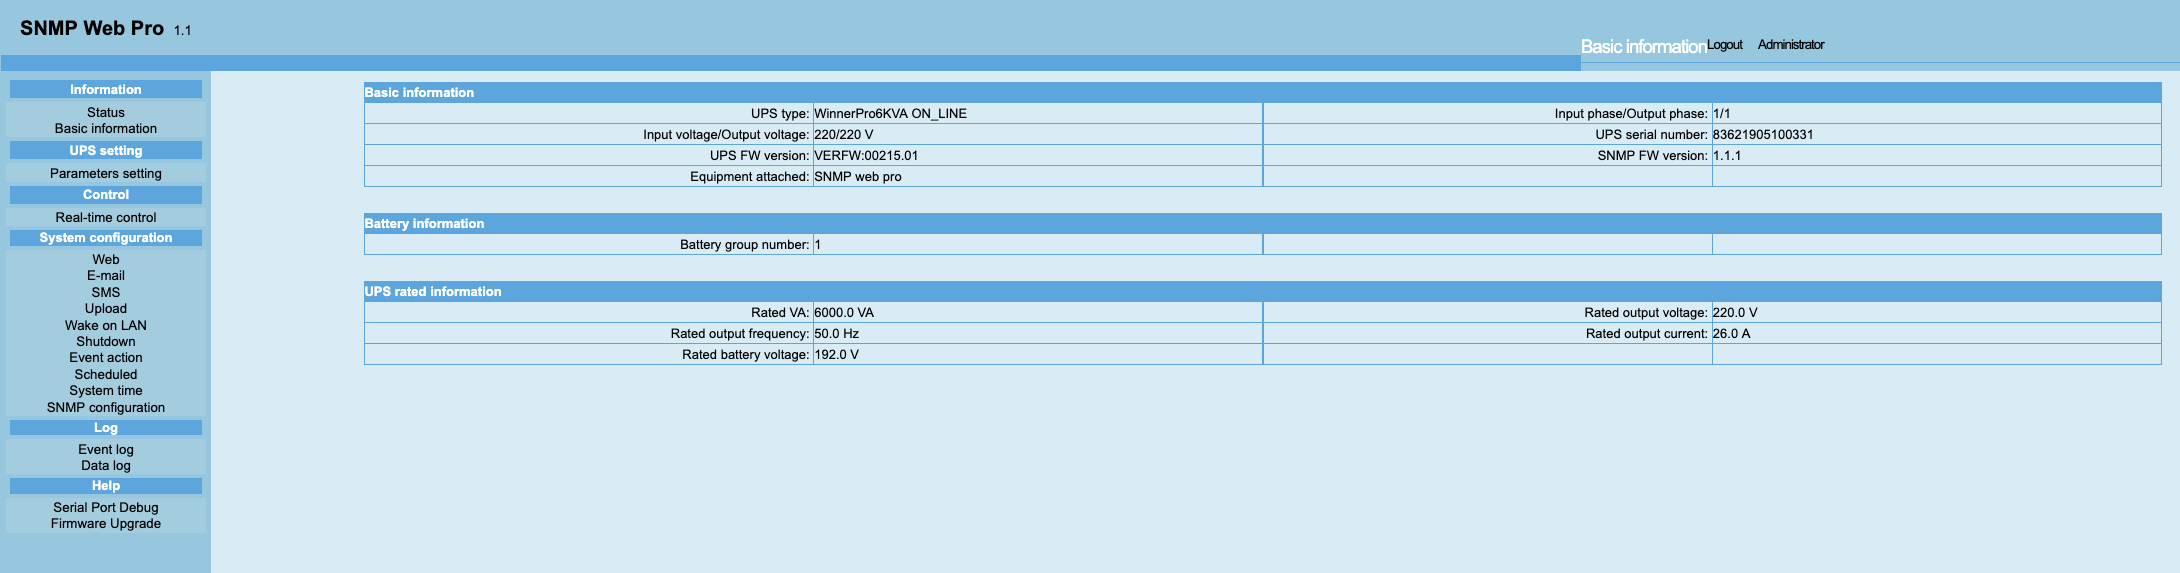 virgula0/cve-2026-44402
Pre-Authenticated Full Root Remote Command Execution in Voltronic Power SNMP Web Pro 1.1
 icex0/wp2shell-poc
wp2shell (CVE-2026-63030 & CVE-2026-60137) - full RCE chain
 g0d150ne/wp2shell
Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…
 jendmaoul/xss2shell-cve-2026-64638
CVE-2026-64638 — WordPress Pre-Auth Reflected XSS → RCE via DOM Clobbering + Application Password Theft + REST API Plugin Activation. Dual-mode PoC…
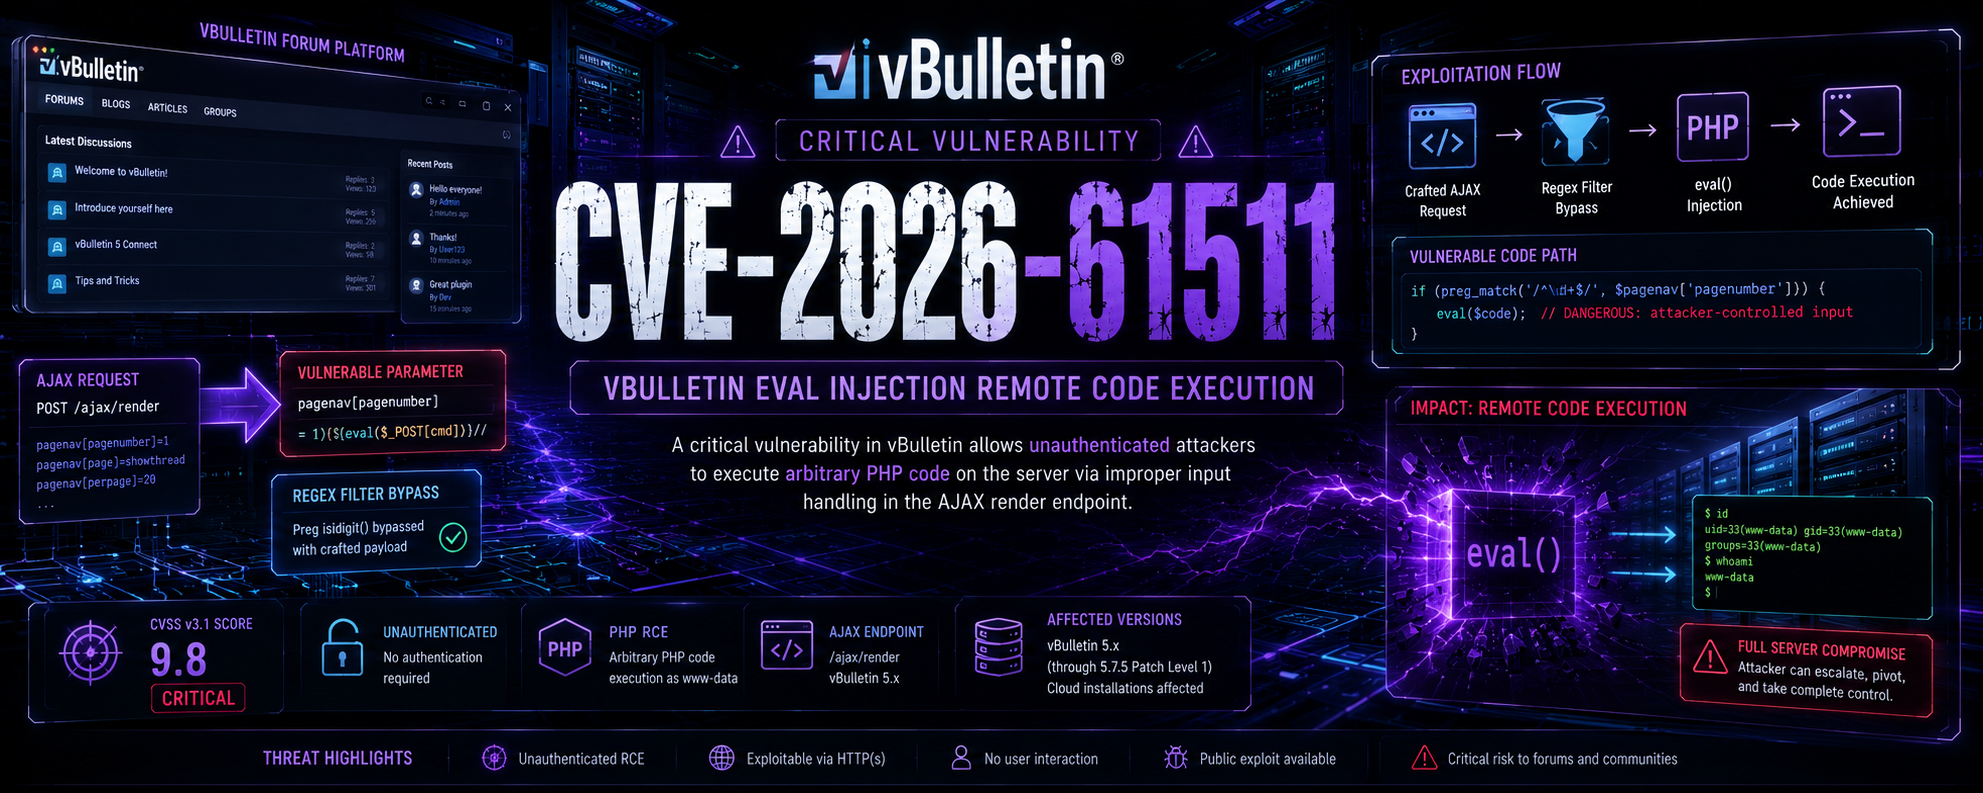 tc4dy/cve-2026-61511-poc-exploit
CVE-2026-61511 – vBulletin Pre-Auth RCE (CVSS 9.8). Vuln 5.x/6.x (unpatched). Multi-exploit via Endpoint Pool, AJAX, PHPFuck WAF bypass. Full…