
PPPoEject
 manizada/pppoeject
Linux kernel local privilege escalation PoC for CVE-2026-68121, chaining PPPoE, FUSE, and IP6GRE to corrupt kernel memory and gain root.
binary-exploitationexploitationmemory-forensics+4
manizada/pppoejectLinux kernel local privilege escalation PoC for CVE-2026-68121, chaining PPPoE, FUSE, and IP6GRE to corrupt kernel memory and gain root.
 theendofabbys/pedit-cow
Linux kernel privilege escalation exploit for CVE-2026-46331, abusing the traffic control pedit subsystem to corrupt the page cache and execute SUID…
 huaguiqi/asus_i005-cve-2026-43499
Android local privilege escalation exploit for CVE-2026-43499 that patches kernel creds and launches embedded KernelSU in late-load mode via…
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 0b0111100/2008
Linux kernel exploit implementations targeting CVE-2008-0600, CVE-2008-0900, and CVE-2008-4210, providing proof-of-concept code for privilege…
 dorlow/hazel-cve-2026-43499
Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…
 oopnv70-lab/ghostlock-aak-apk
GhostLock AAK Launcher - CVE-2026-43499 Linux kernel rtmutex stack UAF local privilege escalation trigger (GPLv3)
 bmax121/kernelpatch
Patching and hooking the Linux kernel with only a stripped Linux kernel image.
 lyravoid/kernelpatch
Patches and hooks the Linux kernel using only a stripped kernel image, extracting symbols and injecting code for inline and syscall hooking on arm64.
 teutekeune/ibssloader
Research tooling to boot Linux on iPad mini 1 via checkm8, patched iBSS/iBEC, and custom bare-metal payloads, including device tree port, kernel…
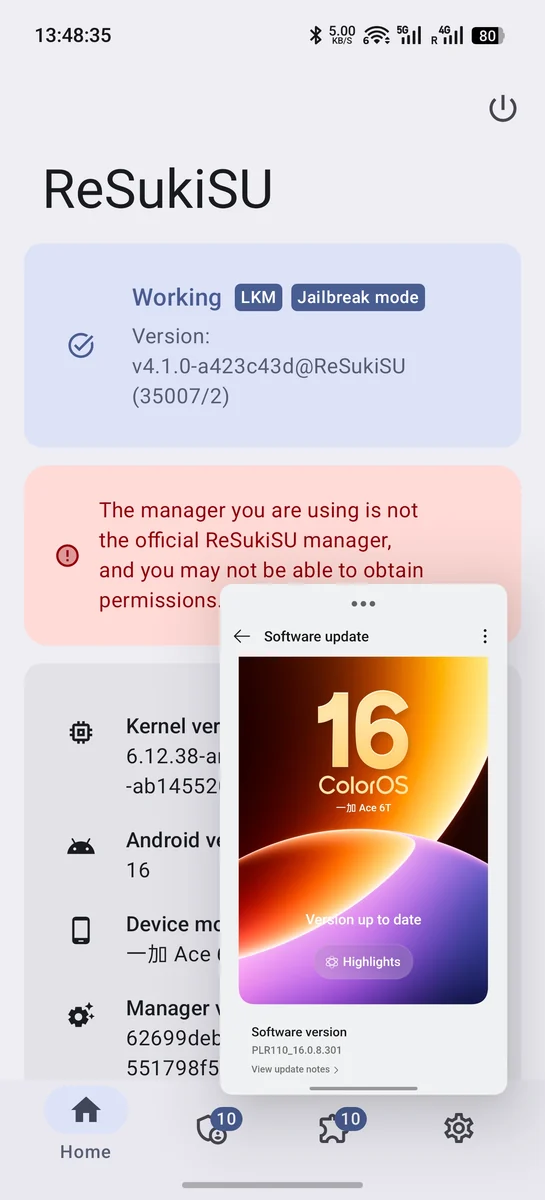 xiaobailovesstirring/ghostlock-k419-adapter
GhostLock (CVE-2026-43499) adapter for 4.19.152-perf+ Android kernel
 gitchw/ghostlock-cve-2026-43499
CVE-2026-43499 (GhostLock) — Linux kernel futex PI rt_mutex UAF ARM32 privilege escalation research targeting Huawei Watch 4 Pro (kernel 5.4.210)
 cenobyte-vincit/slot2
UEFI GRUB2 bootkit that installs a pre-boot networked implant via NVRAM boot option, chainloads a UKI, executes a dracut payload, and kexecs the…
 valentineus/hp-slate7-root-kit
HP Slate 7 2800 Android 4.1.1 rooting kit using CVE-2015-1805.
 yijiacloud/ghostlock-oppo-pckm00
CVE-2026-43499 GhostLock futex UAF LPE PoC for OPPO PCKM00 (SM6150) / Linux 4.14.180
 buter-chkalova/rvbbit-arsenal
Offensive & defensive Linux kernel security research focused on rootkit behavior, observable artifacts and detection.
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 2932796375github/cve-2026-43499_oppo-mt6835
Proof-of-concept exploit chain for CVE-2026-43499 targeting OPPO MT6835 Android devices, with preload payload, build system, and analysis notes for…