

LazyOwn
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
ai-securitycommand-and-controlexploit-frameworks+8
301
grisuno/lazyownRed team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 samugit83/redamon
Autonomous AI red team framework that chains reconnaissance, exploitation, and post-exploitation into a single pipeline, then triages findings,…
 gallopsled/pwntools
CTF framework and exploit development library
 kamalx06/tornadoc2
Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 jm33-m0/emp3r0r
Self‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.
 dimamend/cve-2022-42889-text4shell
Docker-based lab environment to reproduce and test CVE-2022-42889 (Text4Shell) remote code execution vulnerability in Apache Commons Text.
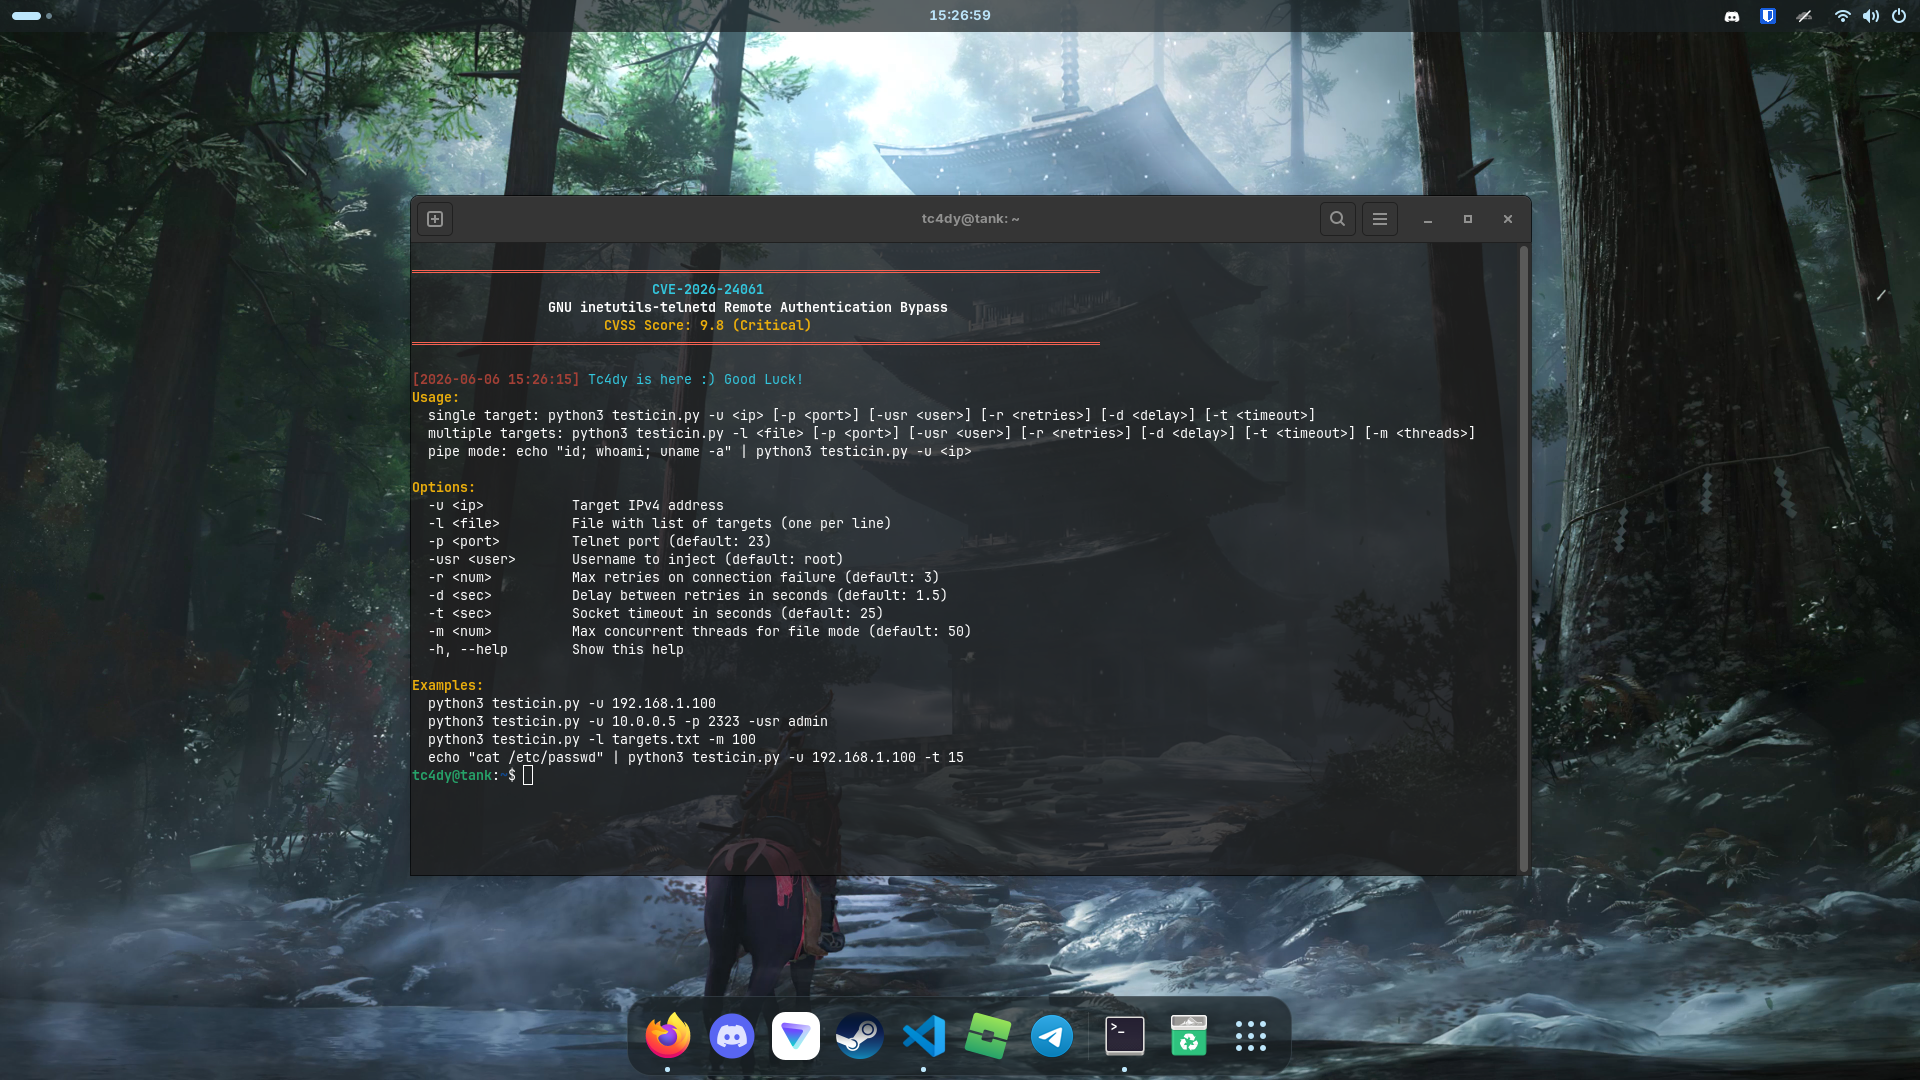 tc4dy/cve-2026-24061-poc-exploit
Remote authentication bypass exploit for GNU inetutils-telnetd (CVE-2026-24061) using CRLF injection to gain instant root shell. Supports single/mass…
 bishopfox/sliver
Adversary Emulation Framework
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
 bmax121/kernelpatch
Patching and hooking the Linux kernel with only a stripped Linux kernel image.
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 lyravoid/kernelpatch
Patches and hooks the Linux kernel using only a stripped kernel image, extracting symbols and injecting code for inline and syscall hooking on arm64.
 dullpurple-sloop726/cve-2026-31431-linux-copy-fail
Exploit CVE-2026-31431 on Linux using a Rust implementation to achieve local privilege escalation via an arbitrary page cache write primitive.
 mythicagents/thanatos
Mythic C2 agent targeting Linux and Windows hosts written in Rust
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…