
ghostlock-s26
 1ndevelopment/ghostlock-s26
GhostLock (CVE-2026-43499) app for the Galaxy S26 series
android-securityexploitationmobile-app-pentesting+5
10
1ndevelopment/ghostlock-s26GhostLock (CVE-2026-43499) app for the Galaxy S26 series
 s-p4rk/cve-2018-6574
Go-based exploit for CVE-2018-6574 using a shared library (attack.so) to demonstrate remote code execution vulnerability.
 schich/lucky-spark
A stealthy stager designed for shellcode payloads staged with http/https like Sliver, or on github raw.
 cybertechajju/cve-2026-59734-poc
OS Command Injection in Health Check → Remote Code Execution
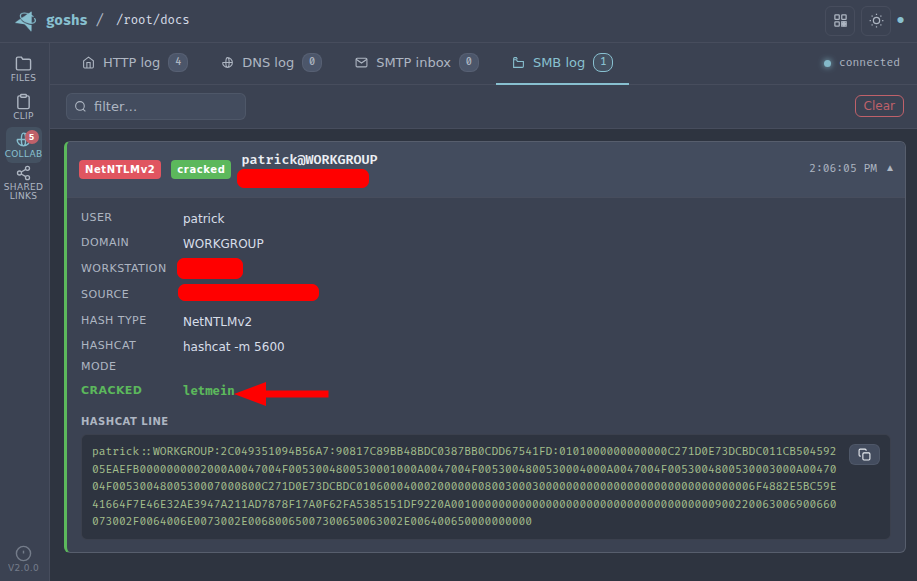 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 kayl22/cve-2025-8110-gogs-rce
GOGS RCE cve-2025-8110 python script that automates the whole attack chain of creating a repository with a symlink file pointing to .git/config and…
 thewhiteh4t/cve-2026-27483
MindsDB Path Traversal to RCE PoC
 sadisticnight/poc-cve-2025-62222
Proof-of-concept demonstrating remote code execution via prompt injection in GitHub Copilot Chat, using a crafted Python file to trigger a…
 vaishnavucv/cve-2011-2523
Python exploit for vsftpd 2.3.4 - Backdoor Command Execution
 whoami-chmod777/zerologon-attack-cve-2020-1472-poc
Python exploit for CVE-2020-1472 (Zerologon) that changes a domain controller's machine account password, enabling DCSync and full domain compromise.…
 susmdt/effective-waffle
yet another sleep encryption thing. also used the default github repo name for this one.
 kimorea/cve-2020-27955-lfs
Windows RCE exploit for CVE-2020-27955 targeting git-lfs, affecting GitHub Desktop, VS Code, and other Git clients via crafted .bat/powershell…
 motikan2010/cve-2023-23924
CVE-2023-23924 (Dompdf - RCE) PoC
 csenox/cve-2022-2992
Authenticated Remote Command Execution in Gitlab via GitHub import
 thejoyofhacking/dirkjanm-cve-2020-1472
Exploit for CVE-2020-1472 (Zerologon) that resets the domain controller account password, enabling DCSync, with restoration steps to revert changes.
 whitetea2424/cve-2020-27955-lfs-main
Batch and PowerShell exploit for CVE-2020-27955, a Git-LFS remote code execution vulnerability affecting Git, GitHub Desktop, VS Code, and other…
 marsable/cve-2020-27955-lfs
RCE exploit for CVE-2020-27955 targeting Git LFS on Windows, with .bat and PowerShell payloads for testing Git, GitHub CLI, VS Code, and other tools.
 arnoldqqq/cve-2020-27955
Exploit for CVE-2020-27955, a Git LFS remote code execution vulnerability, with a .bat/powershell payload targeting Windows Git clients.