
KindaRails2Shell
 0xsha/kindarails2shell
Single-file PoC for Rails CVE-2026-66066: arbitrary file read, secret recovery, threaded scanning, and conditional RCE via signed image variations.
exploitationlabs-practicepayload-development+4
4
0xsha/kindarails2shellSingle-file PoC for Rails CVE-2026-66066: arbitrary file read, secret recovery, threaded scanning, and conditional RCE via signed image variations.
 h4mr3r/cve-2024-5082
Proof-of-concept exploit for CVE-2024-5082, a remote code execution vulnerability in Sonatype Nexus Repository Manager 2 via crafted Maven artifacts…
 k3ystr0k3r/php-8.1.0-dev-backdoor
PHP 8.1.0-dev User-Agentt Backdoor Remote Code Execution (RCE)
 gouldnicholas/cve-2026-7669-poc
PoC for CVE-2026-7669: SGLang silent trust_remote_code override -> RCE
 octetsplicer/lazypariah
A tool for generating reverse shell payloads on the fly.
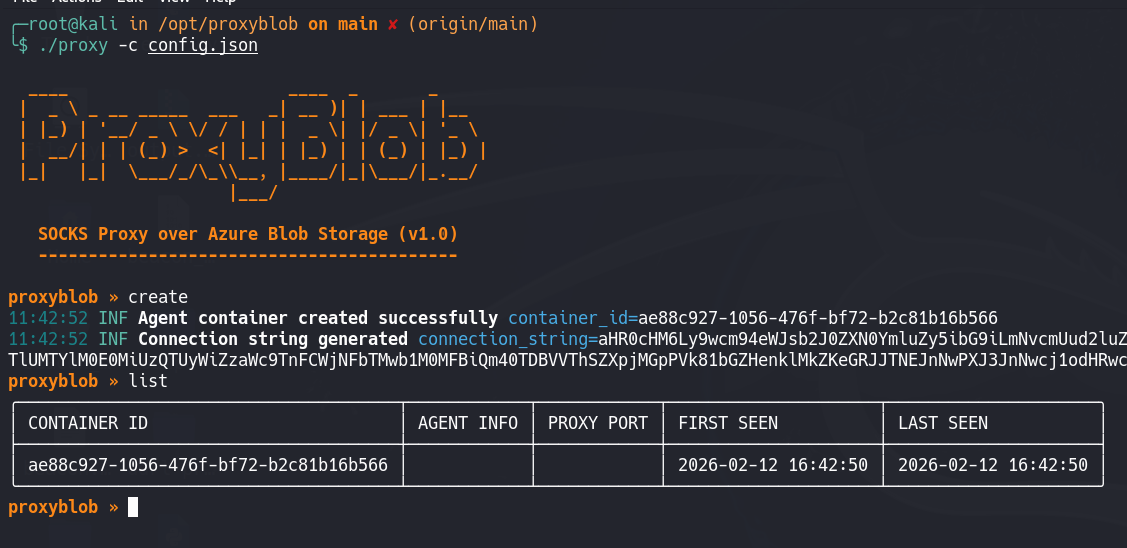 dazzyddos/clickonceblobber
Weaponize signed .NET ClickOnce applications for initial access by hijacking a dependency DLL via AppDomainManager injection and loading a C# port of…
 dvkunion/cve-2025-53547-poc
CVE-2025-53547 one of poc code
 darkcodersc/sharpftpc2
A Streamlined FTP-Driven Command and Control Conduit for Interconnecting Remote Systems.
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
 ianyong/cve-2022-32223
Demonstration exploit for CVE-2022-32223: DLL hijacking in Node.js on Windows via malicious providers.dll, targeting OpenSSL installations.
 nikip72/cve-2021-4034
Statically linked implementation of the CVE-2021-4034 privilege escalation exploit, with encoded payload written to disk and no gcc dependency.
 barbarisch/cve-2019-3980
CVE-2019-3980 exploit written in win32/c++ (openssl dependency). Port of https://github.com/tenable/poc/blob/master/Solarwinds/Dameware/dwrcs_dwDrvIns…
 devang-solanki/cve-2018-6574
Exploit for remote command execution in Golang go get command.