
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
105 results
Harald preview

Harald

GitHubgmh5225/harald

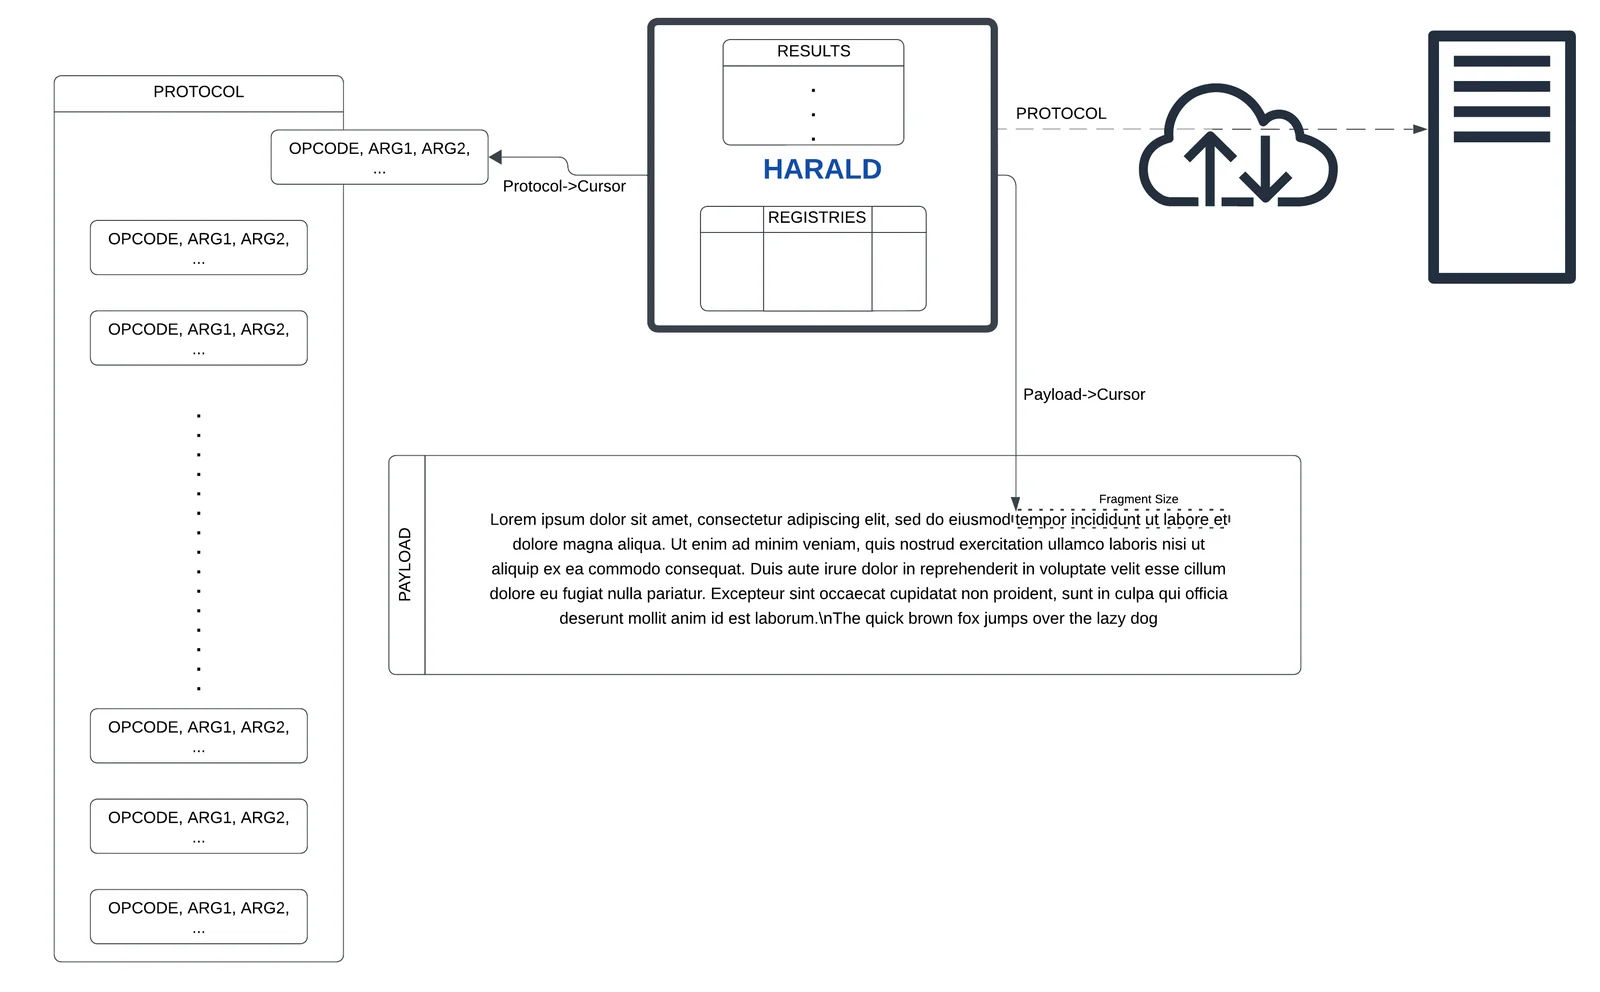
An in-memory minimal CPU for agnostic on-the-fly protocols creation
command-and-controlexploitationids-ips-evasion+6
1 year ago
malvinci preview

malvinci

GitHubgsoffmarket/malvinci

This simple but powerful script will introduce a new type of malware that will turn off the firewall, start an HTTP server, forward its port through…
command-and-controldata-exfiltrationpayload-development+3
592 years ago
CS_SleepMask preview

CS_SleepMask

GitHubjas502n/cs_sleepmask

CS_SleepMask

ids-ips-evasionpayload-developmentpenetration-testing-frameworks+2
45 years ago
dyen preview

dyen

GitHubcenobyte-vincit/dyen

In-memory Mach-O dylib loader for stock macOS Python; decrypts, maps, and runs payloads without dlopen or writing to disk, with optional encrypted…
binary-analysiscryptographyids-ips-evasion+4
1 month ago
PSSW100AVB preview

PSSW100AVB

GitHubtihanyin/pssw100avb

A list of useful Powershell scripts with 100% AV bypass (At the time of publication).

ai-securitycommand-and-controlids-ips-evasion+5
1.4k3 months ago
SleepyCrypt preview

SleepyCrypt

GitHubsolomonsklash/sleepycrypt

A shellcode function to encrypt a running process image when sleeping.
ids-ips-evasionpayload-developmentred-teaming+1
3375 years ago
BokuLoader preview

BokuLoader

GitHubxforcered/bokuloader

A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!

adversarial-attackcommand-and-controlids-ips-evasion+4
3332 years ago
Lastenzug preview

Lastenzug

GitHubcodewhitesec/lastenzug

Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
command-and-controlids-ips-evasionpayload-development+3
2353 years ago
MalwareApiLibrary preview

MalwareApiLibrary

GitHubmalwareapilib/malwareapilibrary

collection of apis used in malware development
ids-ips-evasionpayload-developmentred-teaming
2324 years ago
TamperingSyscalls preview

TamperingSyscalls

GitHubrad9800/tamperingsyscalls

C++ library that retrieves and spoofs Windows syscall arguments using hardware breakpoints and exception handlers to subvert EDR telemetry.

ids-ips-evasionpayload-developmentpost-exploitation+1
5074 years ago
Burp2Malleable preview

Burp2Malleable

GitHubcodextf2/burp2malleable

Quick python utility I wrote to turn HTTP requests from burp suite into Cobalt Strike Malleable C2 profiles

command-and-controlids-ips-evasionpayload-development+2
4193 years ago
rust_syscalls preview

rust_syscalls

GitHubjanoglezcampos/rust_syscalls

Single stub direct and indirect syscalling with runtime SSN resolving for windows.

ids-ips-evasionpayload-developmentpost-exploitation+1
2383 years ago
SharpWhispers preview

SharpWhispers

GitHubsecforce/sharpwhispers

C# porting of SysWhispers2. It uses SharpASM to find the code caves for executing the system call stub.
ids-ips-evasionpayload-developmentpost-exploitation+2
1123 years ago
Cronos preview

Cronos

GitHubidov31/cronos

PoC for a sleep obfuscation technique leveraging waitable timers to evade memory scanners.
cryptographyids-ips-evasionpayload-development+2
6283 years ago
Bitmancer preview

Bitmancer

GitHubzimawhit3/bitmancer

Nim Library for Offensive Security Development
binary-analysisids-ips-evasionpayload-development+4
2003 years ago
Unwinder preview

Unwinder

GitHubkudaes/unwinder

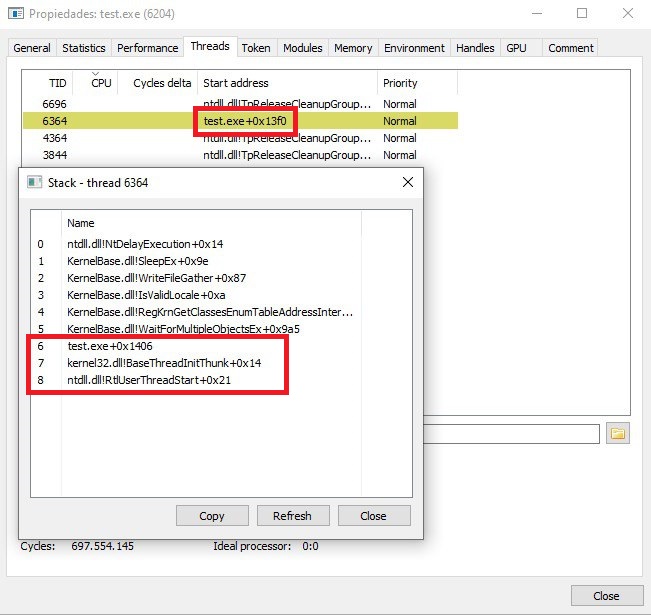
Call stack spoofing for Rust
adversarial-attackids-ips-evasionpayload-development+2
3851 year ago
WTSRM2 preview

WTSRM2

GitHubrad9800/wtsrm2

Header-only C++17 library for evasive Windows development: compile-time API hashing, DLL unhooking, hardware breakpoint clearing, VEH removal, and…
ids-ips-evasionpayload-developmentred-teaming
1633 years ago
CobaltWhispers preview

CobaltWhispers

GitHubnvisosecurity/cobaltwhispers

CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…

adversarial-attackcommand-and-controlids-ips-evasion+4
2433 years ago
Previous123456Next