external-c2-experiments

Go external C2 module for go-exploit that catches reverse SSH shells, providing a server listener and payload client for integrating custom C2…

Go external C2 module for go-exploit that catches reverse SSH shells, providing a server listener and payload client for integrating custom C2…

Python PoC for CVE-2026-100721: detects and exploits vm2 <3.12.2 NodeVM external allowlist bypass, achieving sandbox escape and host RCE via local…

Python exploit chaining CVE-2023-27163 SSRF in Requests Baskets with Mailtrail v0.53 to forward internal services and execute a reverse shell.

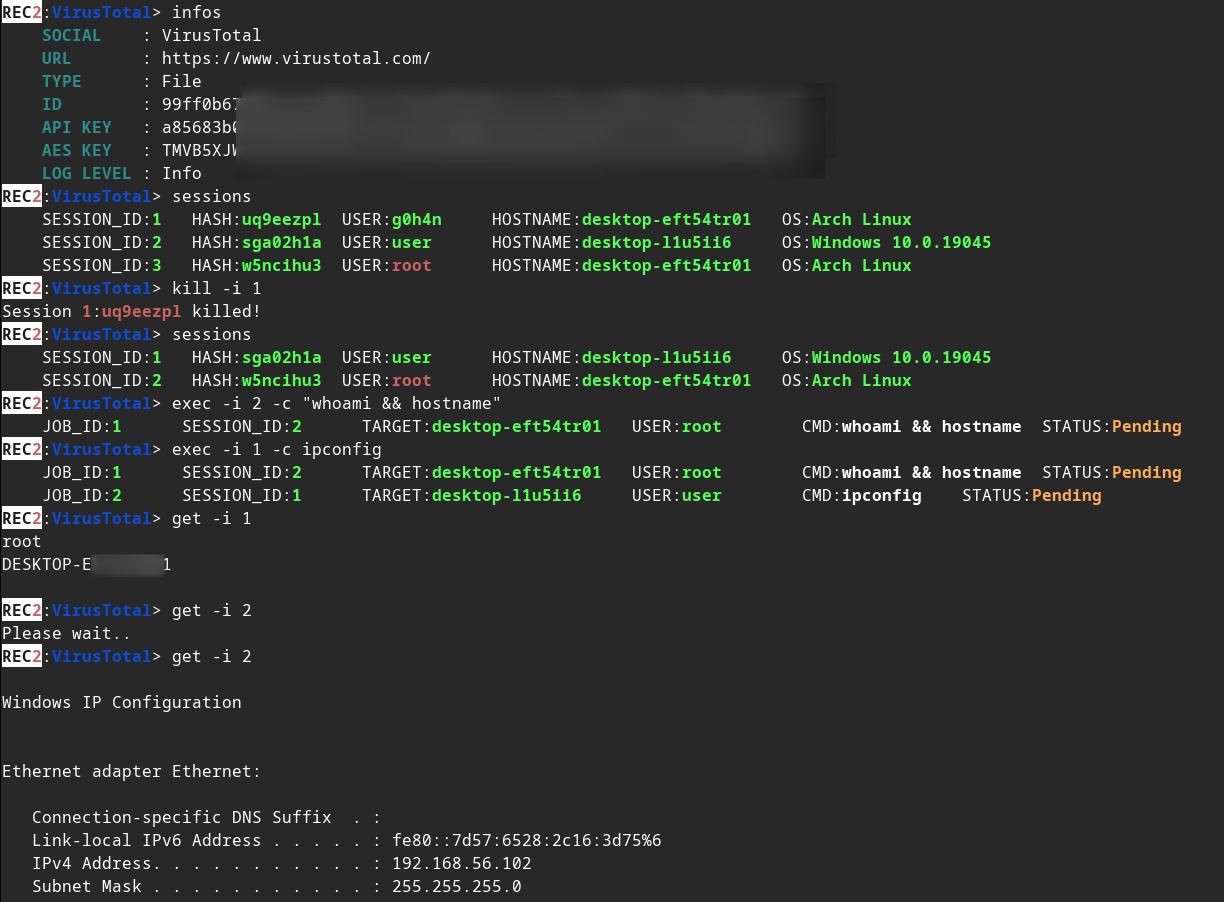
REC2 (Rusty External Command and Control) is client and server tool allowing auditor to execute command from VirusTotal and Mastodon APIs written in…

Jasmin Ransomware is an advanced red team tool (WannaCry Clone) used for simulating real ransomware attacks. Jasmin helps security researchers to…

Voron messenger crypto/protocol library (X3DH-lite + Double Ratchet, group sender-keys, onion transport) — external review requested

POC for Cobalt Strike external C2

Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on

A library for integrating communication channels with the Cobalt Strike External C2 server

Python api for usage with cobalt strike's External C2 specification

Python api for usage with cobalt strike's External C2 specification

CobaltStrike External C2 for Websockets

CVE-2025-55182 - React Server Components RCE Exploit & Scanner Supports external servers and CLI interface

CVE-2025-11953 - The React Native Metro server's default external binding exposes a vulnerable endpoint, allowing unauthenticated attackers to…

ActiveMQ Deserialization RCE

This is a Python 3 version of this exploit. Hope it works!!!

Fawkes is a golang Mythic C2 Agent exclusively written by AI.

Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…