
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
360 results
CVE-2026-33017 preview

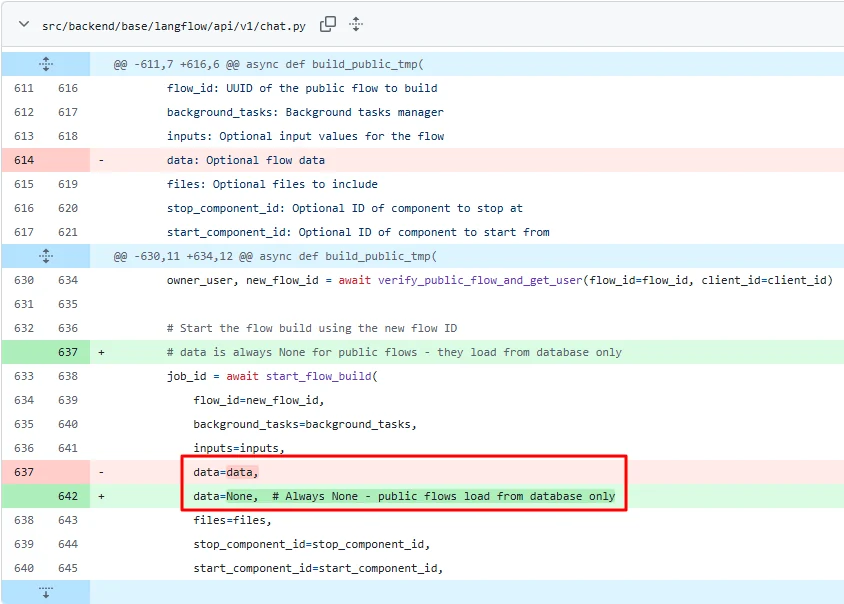
CVE-2026-33017

GitHubyym8538/cve-2026-33017

Proof-of-concept exploit for CVE-2026-33017, an unauthenticated RCE in Langflow's build_public_tmp endpoint, injecting a malicious custom component…
ai-securityexploitationpayload-development+6
1
1 month ago
libheif-grid-nextjs-rce preview

libheif-grid-nextjs-rce

GitHubfortbridge-uk/libheif-grid-nextjs-rce

Private Fortbridge PoC for the CVE-2026-32740 Next.js/sharp leak-to-memcpy-GOT RCE chain

binary-exploitationexploitationlabs-practice+6
14 days ago
FUD-C2-Framework preview

FUD-C2-Framework

GitHubx3r0day/fud-c2-framework

A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
command-and-controlencryption-decryption-toolsids-ips-evasion+9
74 months ago
DirtyFrag-Galaxy preview

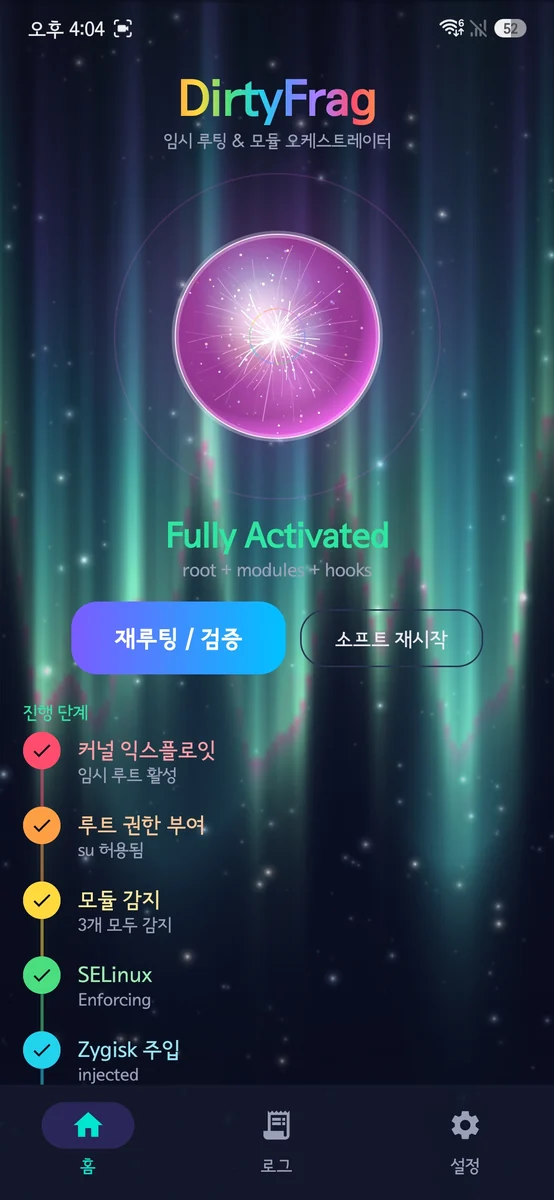
DirtyFrag-Galaxy

GitHubcoey0814/dirtyfrag-galaxy

One-click temporary KernelSU root (late-load) for Samsung Galaxy via DirtyFrag (CVE-2026-43284). No Shizuku/PC/ADB.
android-securityexploitationmobile-app-pentesting+5
53 days ago
IAT-Hook preview

IAT-Hook

GitHubgmh5225/iat-hook

C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…

binary-exploitationcode-analysismalware-analysis+4
4 years ago
ICALL-GADGET preview

ICALL-GADGET

GitHubgmh5225/icall-gadget

Exploit for redirecting control flow of a legit kernel module to your own illegitimate kernel module to evade anti-cheats stack walking
binary-exploitationexploitationids-ips-evasion+5
12 years ago
Relapse-Exploit preview

Relapse-Exploit

GitHubntfargo/relapse-exploit

PS5 exploit chain for firmware 7.00-13.60 combining a WebKit JSC info leak and typedarray corruption with an aio_multi_wait UAF race for kernel…
binary-exploitationeducationexploitation+5
8322 days ago
CVE-2026-94545 preview

CVE-2026-94545

GitHubeqstlab/cve-2026-94545

Proof-of-concept exploit for CVE-2026-94545, an unauthenticated RCE in Next.js next/og via SVG injection and a ROP chain against the native sharp…

exploitationpayload-developmentremote-access-tool+3
92 days ago
op13-cve-2026-64560 preview

op13-cve-2026-64560

GitHuba23bc/op13-cve-2026-64560

Device-specific Android kernel exploit for CVE-2026-64560 on OnePlus 13 builds, providing temporary root via ADB shell with verified payloads and…

android-securitybinary-exploitationexploitation+8
44 days ago
cve-2026-64560-a16 preview

cve-2026-64560-a16

GitHubbecome-illusory/cve-2026-64560-a16

CVE-2026-64560 toolkit: Go single-binary toolchain + realme RMX5010 (A16, SM8750) target port

android-securitybinary-exploitationexploitation+8
5 days ago
opace6-cve-2026-64560 preview

opace6-cve-2026-64560

GitHubwangs-official/opace6-cve-2026-64560

Temporary root tool for OnePlus Ace 6 that exploits the CVE-2026-64560 Linux kernel POSIX CPU timer use-after-free to gain root until reboot, without…

android-securitybinary-exploitationexploitation+6
6 days ago
opace6-cve-2026-64560 preview

opace6-cve-2026-64560

GitHubqingle009/opace6-cve-2026-64560

OnePlus Ace 6 temporary root tool (CVE-2026-64560) - device-verified port with corrected bootidParent address

android-securitybinary-exploitationexploitation+7
5 days ago
house_of_apple_2 preview

house_of_apple_2

GitHubjazho76/house_of_apple_2

Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…

binary-exploitationdebuggerseducation+7
31 month ago
RC4Decryption preview

RC4Decryption

GitHubweedhashpeddler/rc4decryption

Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…
binary-analysiscryptographydefensive-tools+6
359 days ago
CVE-2026-87575-CVE-2026-87606-CVE-2026-87491-and-CVE-2026-85046.-Escape-the-v8-carcass. preview

CVE-2026-87575-CVE-2026-87606-CVE-2026-87491-and-CVE-2026-85046.-Escape-the-v8-carcass.

GitHubsneakynachos/cve-2026-87575-cve-2026-87606-cve-2026-87491-and-cve-2026-85046.-escape-the-v8-carcass.

Chained Chrome V8 renderer escape proof-of-concept exploiting four CVEs: Float64Array corruption, Wasm overwrite, popup navigation retargeting, and…
binary-exploitationexploitationpapers-research+5
516 days ago
ReflectivePluginLoader preview

ReflectivePluginLoader

GitHubracoten/reflectivepluginloader

A minimal PE mapper that loads DLLs straight from memory and calls into a clean plugin interface, no LoadLibrary needed.

binary-exploitationdefensive-toolseducation+7
4317 days ago
CVE-2025-21479-FX5P preview

CVE-2025-21479-FX5P

GitHubdiyiqiuye/cve-2025-21479-fx5p

Temporary root for OPPO Find X5 Pro (PFEM00) via CVE-2025-21479 + KernelSU LKM late-load (cloud-buildable)
android-securitybinary-exploitationexploitation+6
7 days ago
CVE-2019-11707-from-an-IonMonkey-type-confusion-to-SYSTEM- preview

CVE-2019-11707-from-an-IonMonkey-type-confusion-to-SYSTEM-

GitHubg4sp4rcs/cve-2019-11707-from-an-ionmonkey-type-confusion-to-system-

Windows proof-of-concept exploit chain for CVE-2019-11707, a Firefox IonMonkey type confusion, combining browser RCE with sandbox escape to achieve…

binary-exploitationeducationexploitation+6
2 days ago
Previous12…20Next