
CVE-2026-22777
 si13nttt/cve-2026-22777
Proof-of-concept exploit chaining CRLF injection in ComfyUI-Manager's config endpoint with an arbitrary git install to achieve unauthenticated remote…
command-and-controlexploitationpayload-development+5
si13nttt/cve-2026-22777Proof-of-concept exploit chaining CRLF injection in ComfyUI-Manager's config endpoint with an arbitrary git install to achieve unauthenticated remote…
 khush-613/cve-2026-44011-poc
Python proof-of-concept exploit for CVE-2026-44011, an authenticated RCE in Craft CMS via Yii behavior injection, with two-stage command output…
 langz337/cve-2026-63030
Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
 akash0x00/zoneminder-1.29-1.30-rce-exploit
Unauthenticated SQL injection to RCE exploit for ZoneMinder 1.29/1.30 (CVE-2016-10204, EDB-41239). Single-command SQLi to webshell to reverse shell…
 n0qword/mythic_ornn
LLM-driven generator for Mythic Agents, Payload-Type and C2 Profiles.
 tc4dy/cve-2026-65643-poc-toolkit
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…
 mbanyamer/cve-2026-25130-cybersecurity-ai-cai-framework-0.5.10
Proof-of-concept demonstrating argument injection leading to OS command injection in the CAI framework's find_file utility, enabling arbitrary…
 febinrev/atril_cbt-inject-exploit
CVE-2023-44452, CVE-2023-51698: CBT File Parsing Argument Injection that affected Popular Linux Distros
 dxleryt/cve-2026-26331
Proof-of-concept demonstrating arbitrary command injection via yt-dlp's --netrc-cmd option, exploiting shell metacharacters in URLs to execute…
 dapthehuman/cve-2026-40176-cve-2026-40261
Proof-of-concept demonstrating command injection in Composer's Perforce driver (CVE-2026-40176), enabling remote code execution via crafted…
 simoesctt/ctt-mailpit-rce-v1.0---temporal-resonance-mail-server-takeover
Exploit tool that transforms SMTP header injection into remote code execution with self-propagating worm capabilities, featuring persistence…
 pasindu-sd/cve-2025-69212-exploit
Automated exploit for CVE-2025-69212 command injection in OpenSTAManager, featuring admin authentication, malicious ZIP upload, and reverse shell or…
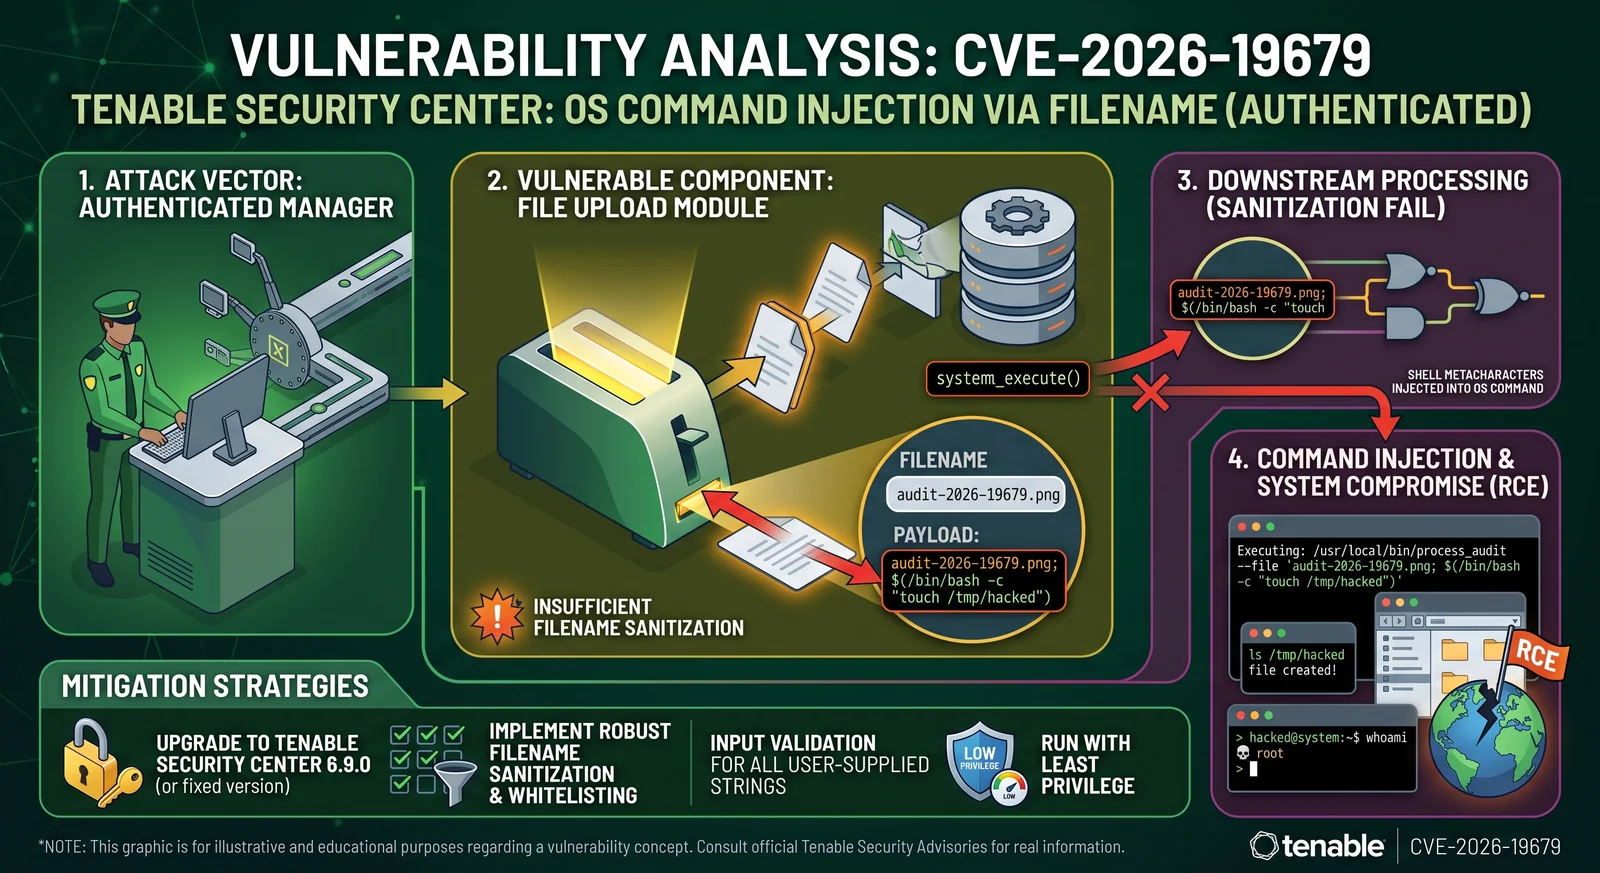 h00die/poc-cve-2026-19679
Proof-of-concept exploit for CVE-2026-19679, an insufficient filename sanitization vulnerability in audit-file upload leading to command injection.…
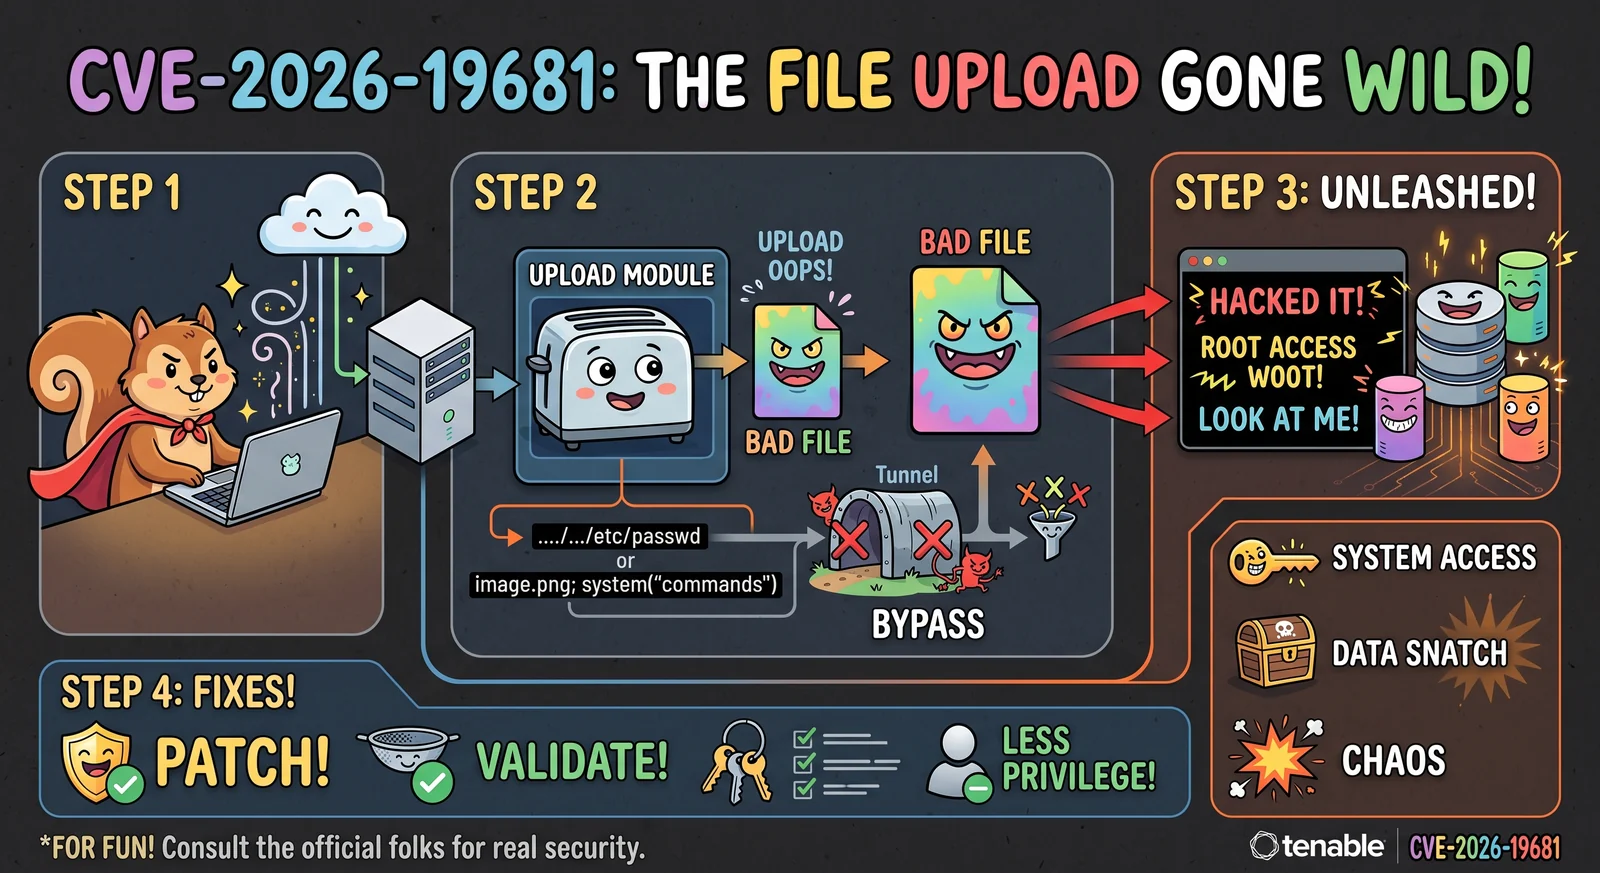 h00die/poc-cve-2026-19681
Proof-of-concept exploit for authenticated command injection in file upload processing, demonstrating two-step chain via REST API with blind timing…
 s3c/globalprotect-ca-cert-ipc
Proof-of-concept exploit for CVE-2025-0117 in GlobalProtect, achieving privilege escalation to SYSTEM via a backdoored installer and DLL injection.
 jasonbernier/cve-2025-5781
Proof-of-concept exploit for CVE-2025-57819 in FreePBX: SQL injection in the AJAX API to execute arbitrary PHP, create a persistent webshell, and…
 faisal-p27/wareed-dns-c2
DNS-only command-and-control framework with Windows agent, payload generation, remote shell execution, shellcode injection, and SOCKS5 proxy support…
 bin4ry/unipwn
BLE exploit framework for Unitree robots: command injection via hardcoded AES keys enables remote takeover, payload injection, and wormable…