
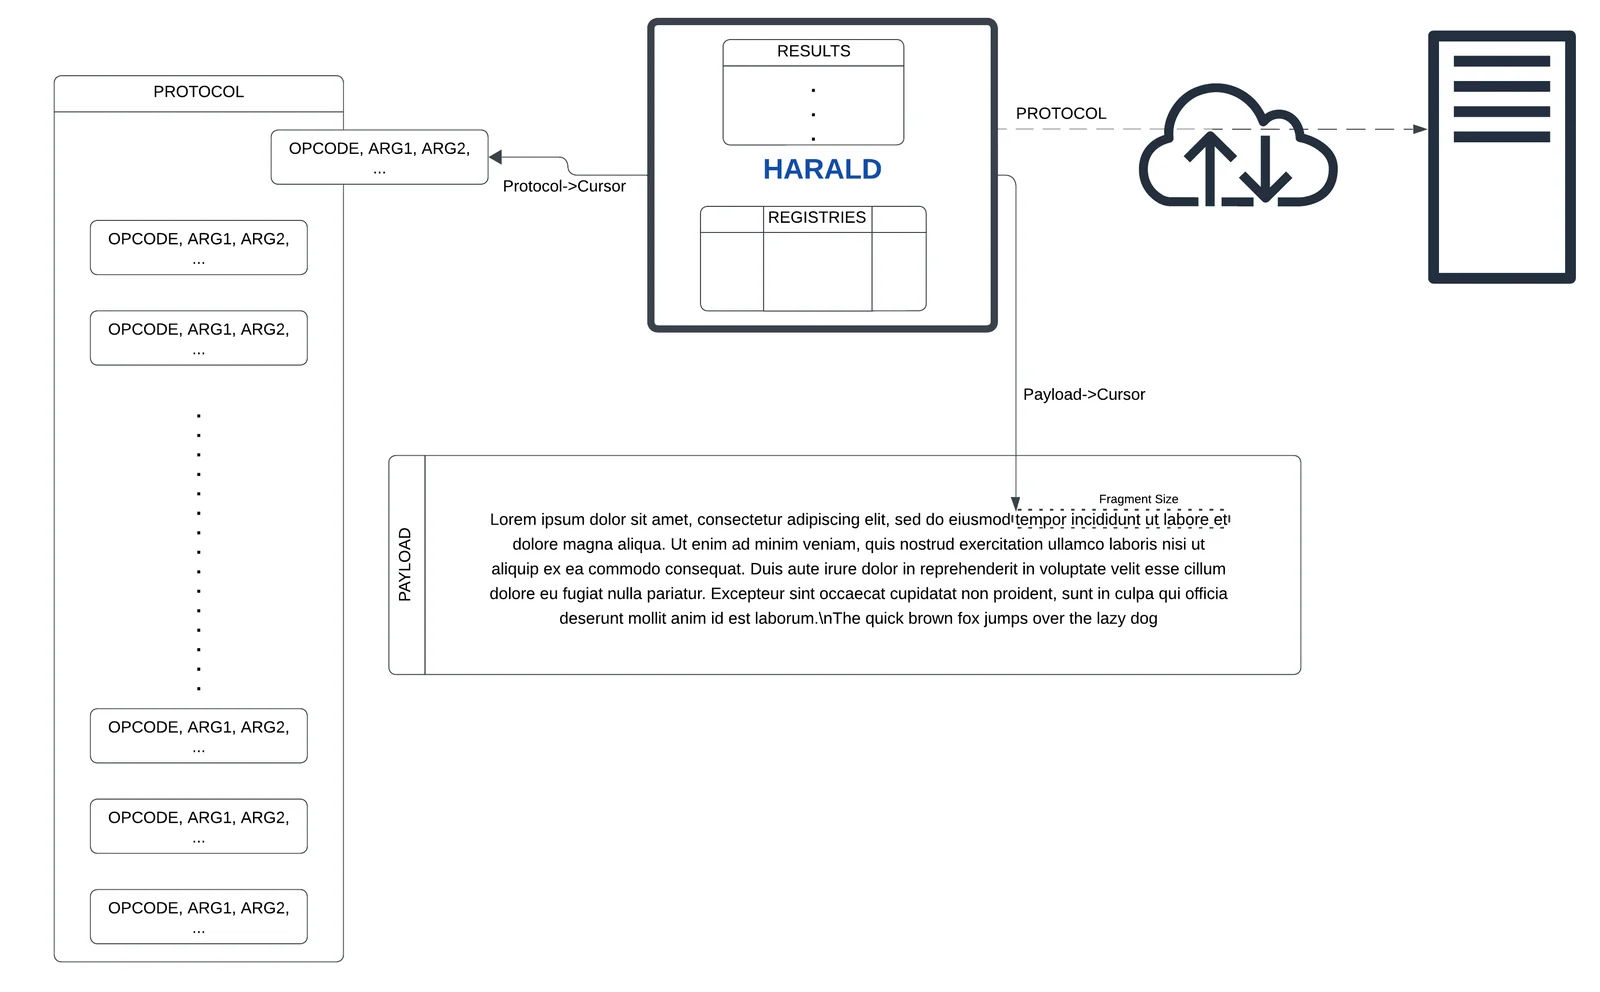
Harald
 gmh5225/harald
An in-memory minimal CPU for agnostic on-the-fly protocols creation
command-and-controlexploitationids-ips-evasion+6
gmh5225/haraldAn in-memory minimal CPU for agnostic on-the-fly protocols creation
 paradoxis/dnsrpc-bof
Beacon Object File (BOF) implementation of the dnscmd.exe functionality used to obtain remote code execution on an ADIDNS server by exploiting the…
 0xc4r/cve-2026-21508_poc
Proof-of-concept for CVE-2026-21508, demonstrating a DLL hijacking attack on Windows 11 that escalates privileges by loading a crafted DLL into…
 hypnguyen1209/cve-2026-62911
Proof-of-concept exploit for CVE-2026-62911: pre-auth RCE on Microsoft Exchange via NTLM relay to MRSProxy, writing an ASPX webshell for SYSTEM…
 judgedbykira/cve-2026-25938-fuxa-unauthenticated-rce
An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA
 loaxert/cve-2025-59528-poc
PoC for CVE-2025-59528 used to achieve remote code execution on the Silentium machine at HTB
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 malwareapilib/malwareapilibrary
collection of apis used in malware development
 mainframed/dc30_workshop
DEFCON 30 Mainframe buffer overlow workshop container
 pwntester/serialkillerbypassgadgetcollection
Collection of bypass gadgets to extend and wrap ysoserial payloads
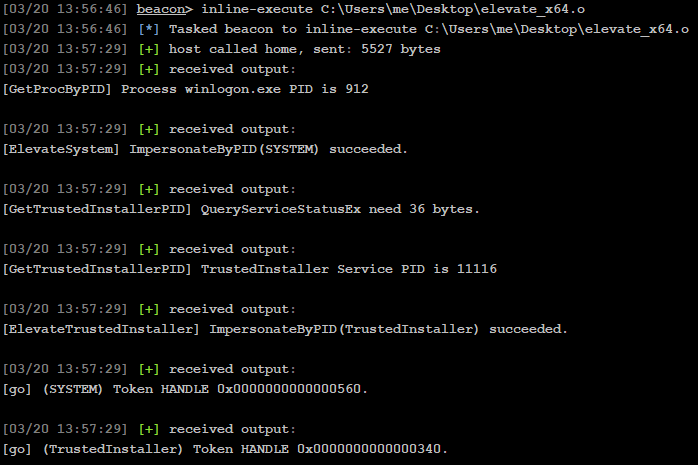 mr-un1k0d3r/elevate-system-trusted-bof
Cobalt Strike Beacon Object File that elevates an active beacon to SYSTEM and grants TrustedInstaller privileges through SetThreadToken token…
 d00mfist/mystikal
macOS Initial Access Payload Generator
 vxcrypt0r/voidgate
A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…
 arosenmund/defcon33_silence_kill_edr
Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.
 maldev-academy/ghostlyhollowingviatamperedsyscalls2
Implementing Ghostly-Hollowing using tampered syscalls for remote PE injection
 schierlm/javapayload
JavaPayload is a collection of pure Java payloads to be used for post-exploitation from pure Java exploits or from common misconfigurations (like not…
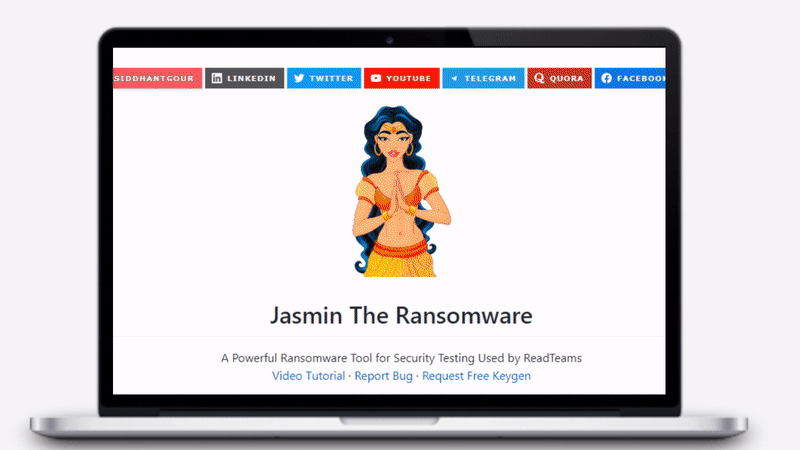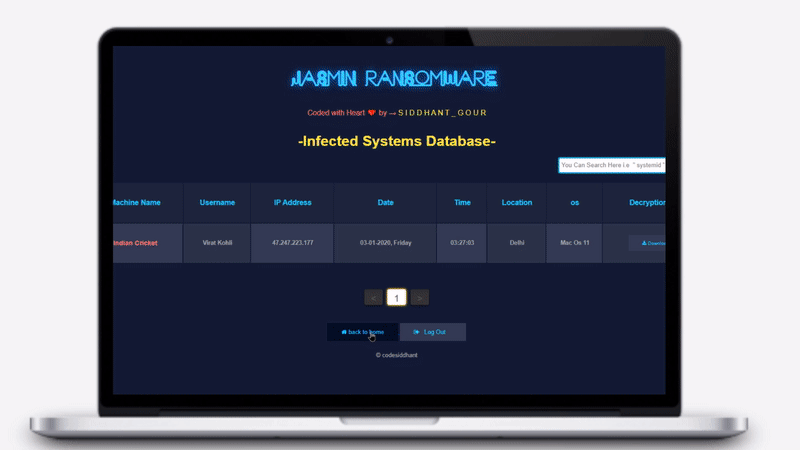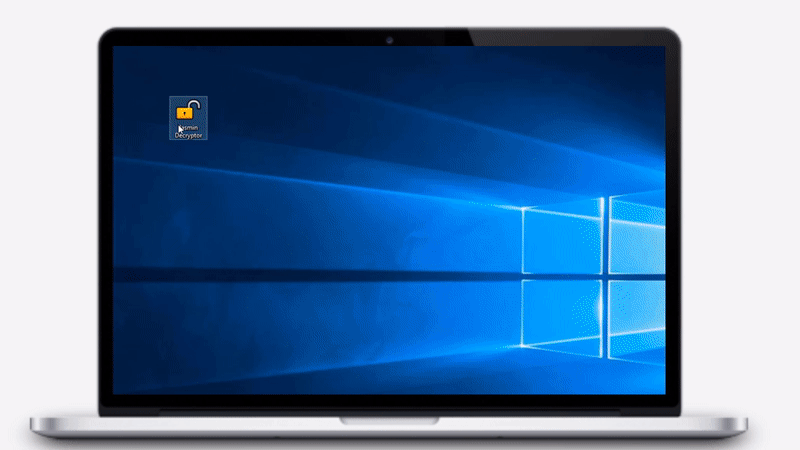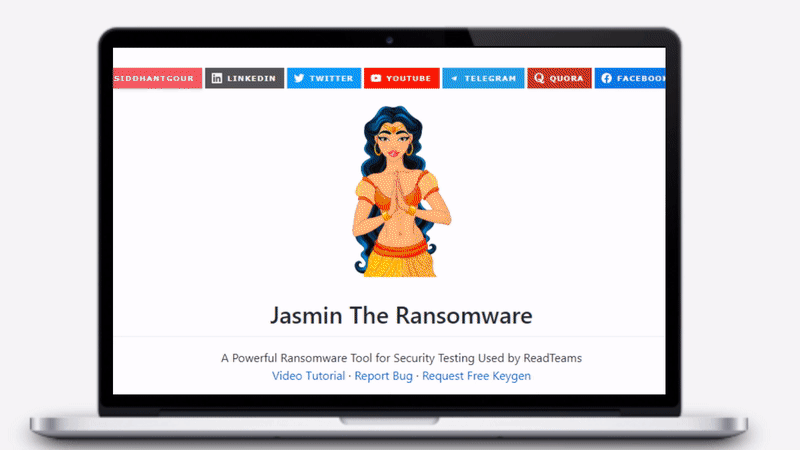 codesiddhant/jasmin-ransomware
Jasmin Ransomware is an advanced red team tool (WannaCry Clone) used for simulating real ransomware attacks. Jasmin helps security researchers to…
 al1ex/fastjsonautotypebypass
FastJsonAutoTypeBypass