

voidsyscall
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
command-and-controlencryption-decryption-toolsids-ips-evasion+9
55
voidsecsoftwares/voidsyscallCross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
 gu-007/struts2-tool
Struts2 S2-045/S2-046 CVE-2017-5638 detection & exploitation tool
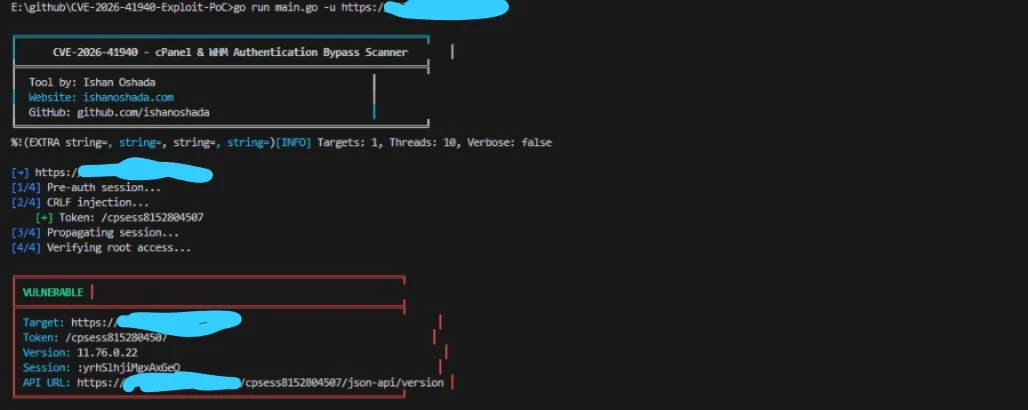 ishanoshada/cve-2026-41940-exploit-poc
Exploit PoC for CVE-2026-41940, a cPanel & WHM authentication bypass via CRLF injection. Includes mass scanning, post-exploitation actions, and an…
 h1sok444/cve-2026-23744-poc
Proof-of-concept exploit for CVE-2026-23744, targeting /api/mcp/connect to achieve remote command execution on Linux systems via reverse shell.
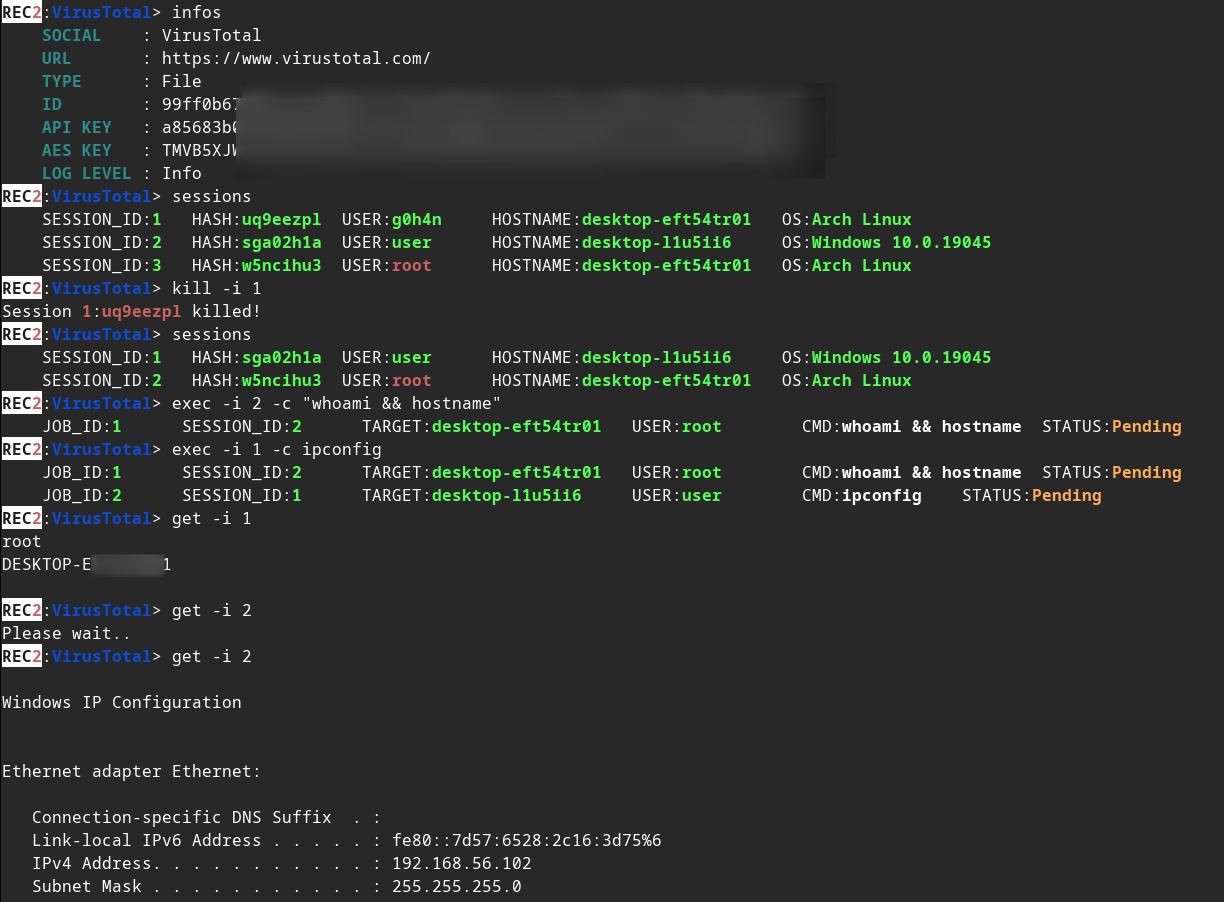 g0h4n/rec2
REC2 (Rusty External Command and Control) is client and server tool allowing auditor to execute command from VirusTotal and Mastodon APIs written in…
 m1ddl3w4r3/wsl_payload_builder
A powerful shell script for creating custom WSL (Windows Subsystem for Linux) distributions with embedded payloads.
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
 1xpwn/cve-2025-32463
This CVE addresses a vulnerability in sudo versions 1.9.14 to 1.9.17, enabling unauthorized local privilege escalation to root access.
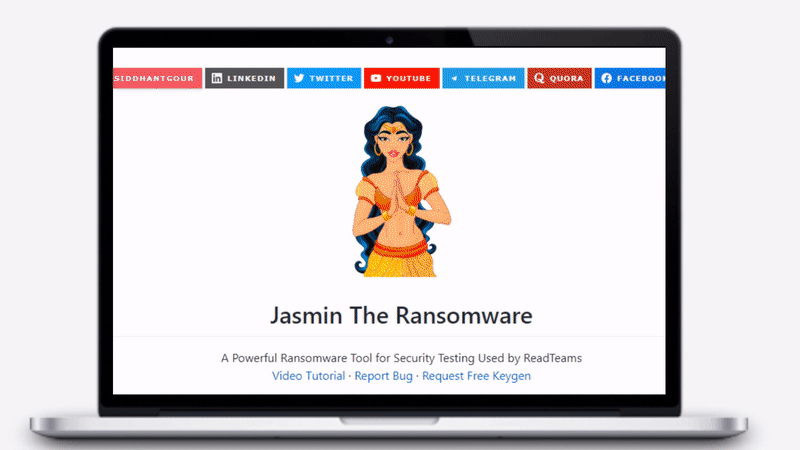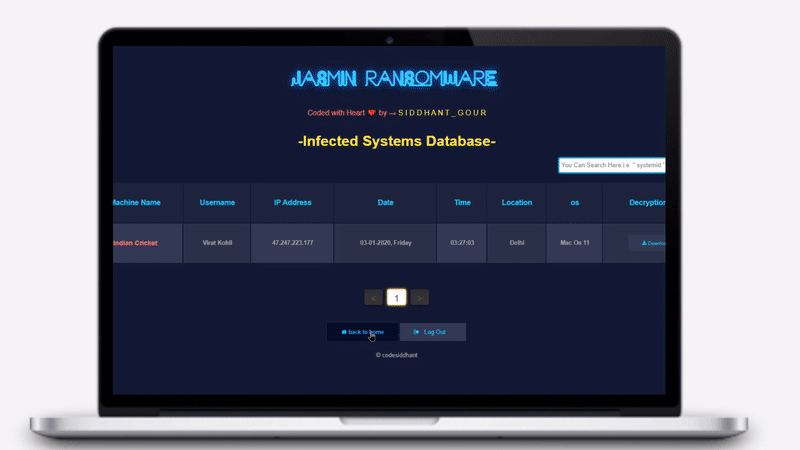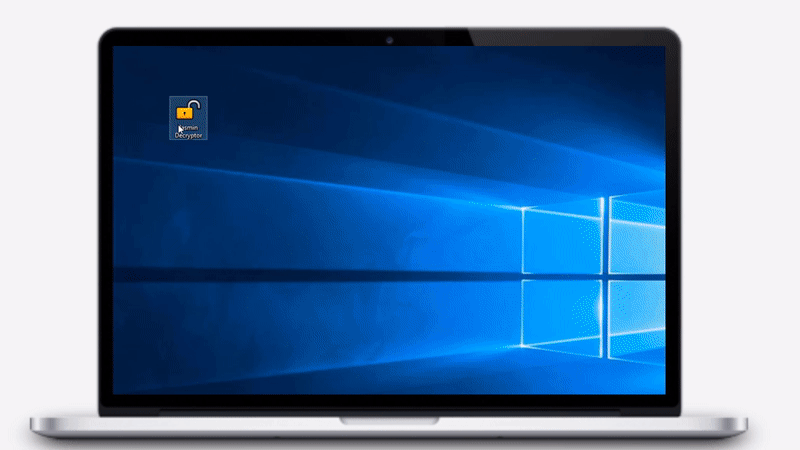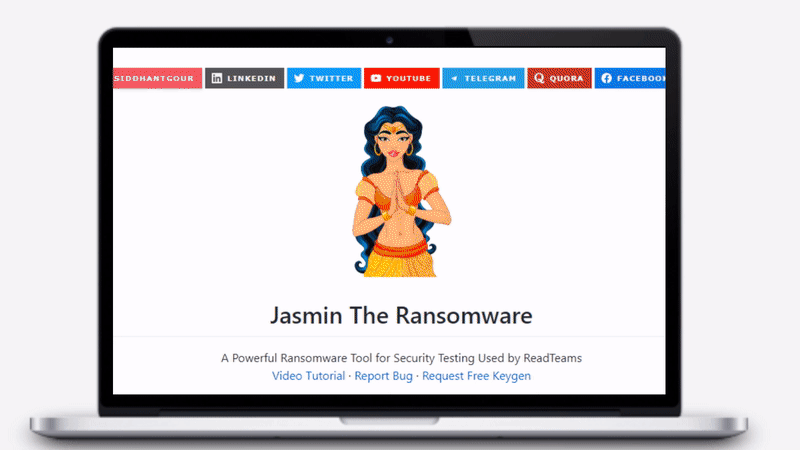 codesiddhant/jasmin-ransomware
Jasmin Ransomware is an advanced red team tool (WannaCry Clone) used for simulating real ransomware attacks. Jasmin helps security researchers to…
 cenobyte-vincit/encrypted-linux-kernel-modules
encrypted-linux-kernel-modules
 adaptix-framework/adaptixc2
AdaptixC2 is a highly modular advanced redteam toolkit
 nu11secur1ty/metasploit-framework-nu11secur1ty
Extending of metasploit-framework
 user696/mrrat
:mouse: This is a cross-platform Python 2.x Remote Access Trojan (RAT)
 tarlogicsecurity/chankro
Herramienta para evadir disable_functions y open_basedir
 popyue/cve-2025-47812
RCE for WingFTP v4.7.3
 luoqichen/cve-2025-55182-poc
Go-based scanner and exploitation tool for CVE-2025-55182 (Next.js RCE). Supports batch scanning, command execution, Godzilla memory shell injection,…
 freax13/cve-2024-21980-poc
Exploit for CVE-2024-21980 targeting AMD SEV firmware to decrypt arbitrary memory of decommissioned SEV-SNP guests via a command buffer enforcement…
 vuducmanhno100-cloud/cve-2024-6387
CVE-2024-6387 POC (Currently being edited)