

TornadoRevC2
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
command-and-controlinformation-gatheringlateral-movement+8
38
kamalx06/tornadorevc2Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 jvbotelho/skewrun
Active Directory time discovery protocols for red teams. Stealthy extraction via Kerberos, SMB, NTLM, and CLDAP.
 shinthink/solrradar
☄️ Mass reconnaissance & exploitation framework for Apache Solr CVE-2026-44825 — Velocity template injection to RCE
 xaitax/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Microsoft-Outlook-Remote-Code-Execution-Vulnerability
 xsscx/cve-2017-5638
Example PoC Code for CVE-2017-5638 | Apache Struts Exploit
 zyphorixofficialmain-lab/cve-2026-87902
Python exploit for CVE-2026-87902, a WordPress Core LFI-to-RCE chain. Fingerprints versions, writes a PHP shell via pearcmd, and provides command…
 marshall-hallenbeck/cve_2025_68413-4
Disclosure and PoCs for CVE-2025-68413 and CVE-2025-68414
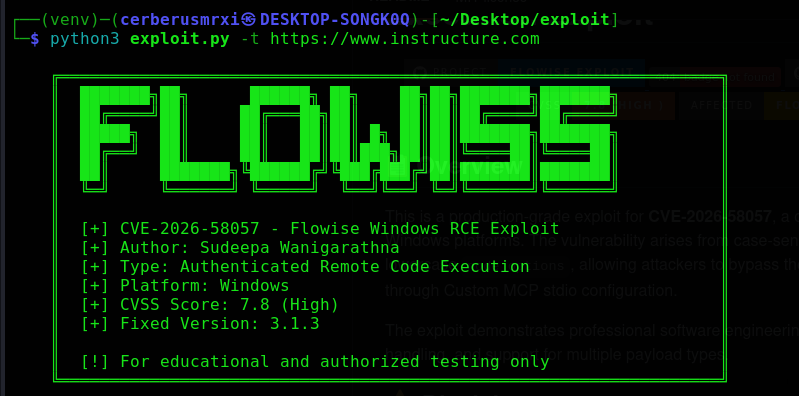 cerberusmrxi/flowise-cve-2026-58057-exploit
Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…
 ghostlyrootb2h/cve-2026-82222
Exploit framework for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports mass scanning, auto-detection, multi-threading,…
 liaoziqi-gzfls/cve-2026-42945
CVE-2026-42945 Nginx Rift
 zephrfish/wp2shell-scanner
CVE-2026-63030, CVE-2026-60137, wp2shell scanner
 jenderal92/cve-2026-41940
Bulk scanner and mass exploitation tool for CVE-2026-41940 on cPanel/WHM, built for automated target validation and high-speed multi-threaded…
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
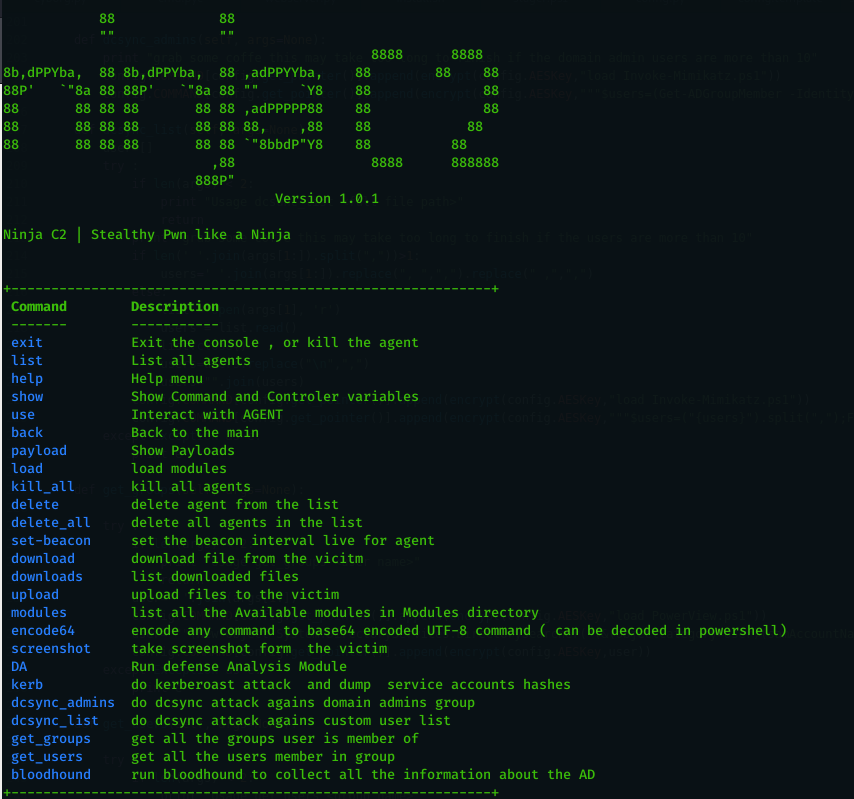 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations
 egebalci/egesploit
EGESPLOIT is a golang library for malware development
 shinthink/cve-2026-57827
CVE-2026-57827 — RSFiles! Joomla Component Unauthenticated File Upload RCE. Split-controller upload bypass. CVSS 9.8 | CWE-434 | com_rsfiles < 1.17.12
 gquere/pwn_jenkins
Notes about attacking Jenkins servers
 truekas/ls-poc
Proof-of-concept exploit for CVE-2026-30368, demonstrating authentication bypass in Lightspeed Classroom to control student devices via Ably channel.