

TornadoRevC2
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
command-and-controlinformation-gatheringlateral-movement+8
38
kamalx06/tornadorevc2Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 jvbotelho/skewrun
Active Directory time discovery protocols for red teams. Stealthy extraction via Kerberos, SMB, NTLM, and CLDAP.
 shinthink/solrradar
☄️ Mass reconnaissance & exploitation framework for Apache Solr CVE-2026-44825 — Velocity template injection to RCE
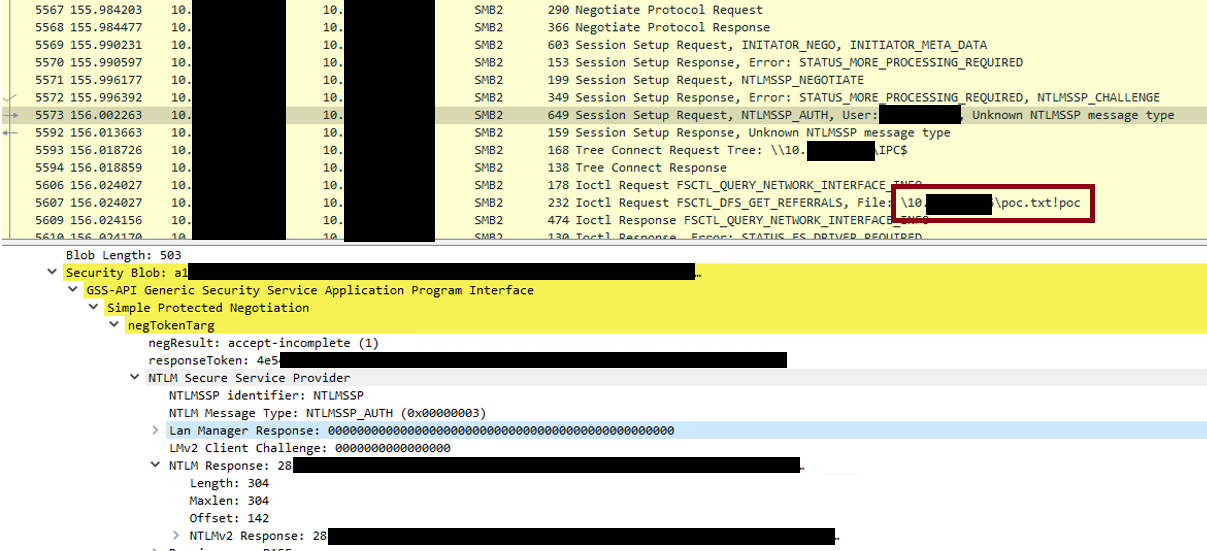 xaitax/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Microsoft-Outlook-Remote-Code-Execution-Vulnerability
 zyphorixofficialmain-lab/cve-2026-87902
Python exploit for CVE-2026-87902, a WordPress Core LFI-to-RCE chain. Fingerprints versions, writes a PHP shell via pearcmd, and provides command…
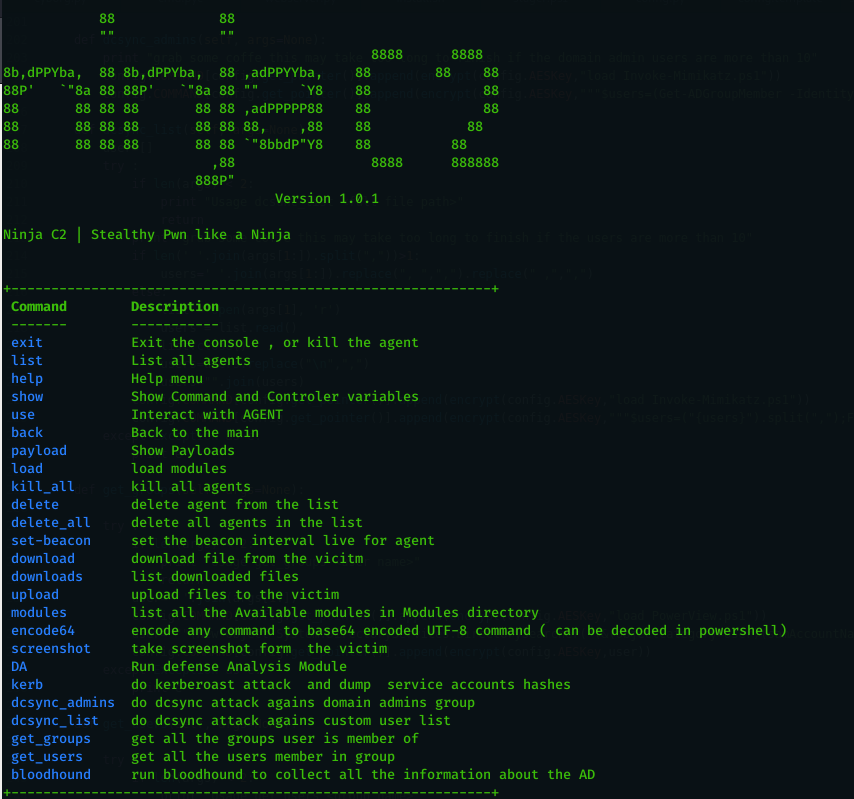 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations
 cerberusmrxi/flowise-cve-2026-58057-exploit
Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
 ghostlyrootb2h/cve-2026-82222
Exploit framework for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports mass scanning, auto-detection, multi-threading,…
 egebalci/egesploit
EGESPLOIT is a golang library for malware development
 imbas007/cve-2026-42533
Exploit for nginx heap buffer overflow (CVE-2026-42533) providing pre-auth RCE via two-pass capture clobbering. Includes info leak, heap spray, and…
 gquere/pwn_jenkins
Notes about attacking Jenkins servers
 zephrfish/wp2shell-scanner
CVE-2026-63030, CVE-2026-60137, wp2shell scanner
 0xdea/tactical-exploitation
Modern tactical exploitation toolkit.
 nxploited/cve-2026-91097-cve-2026-91106
HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)
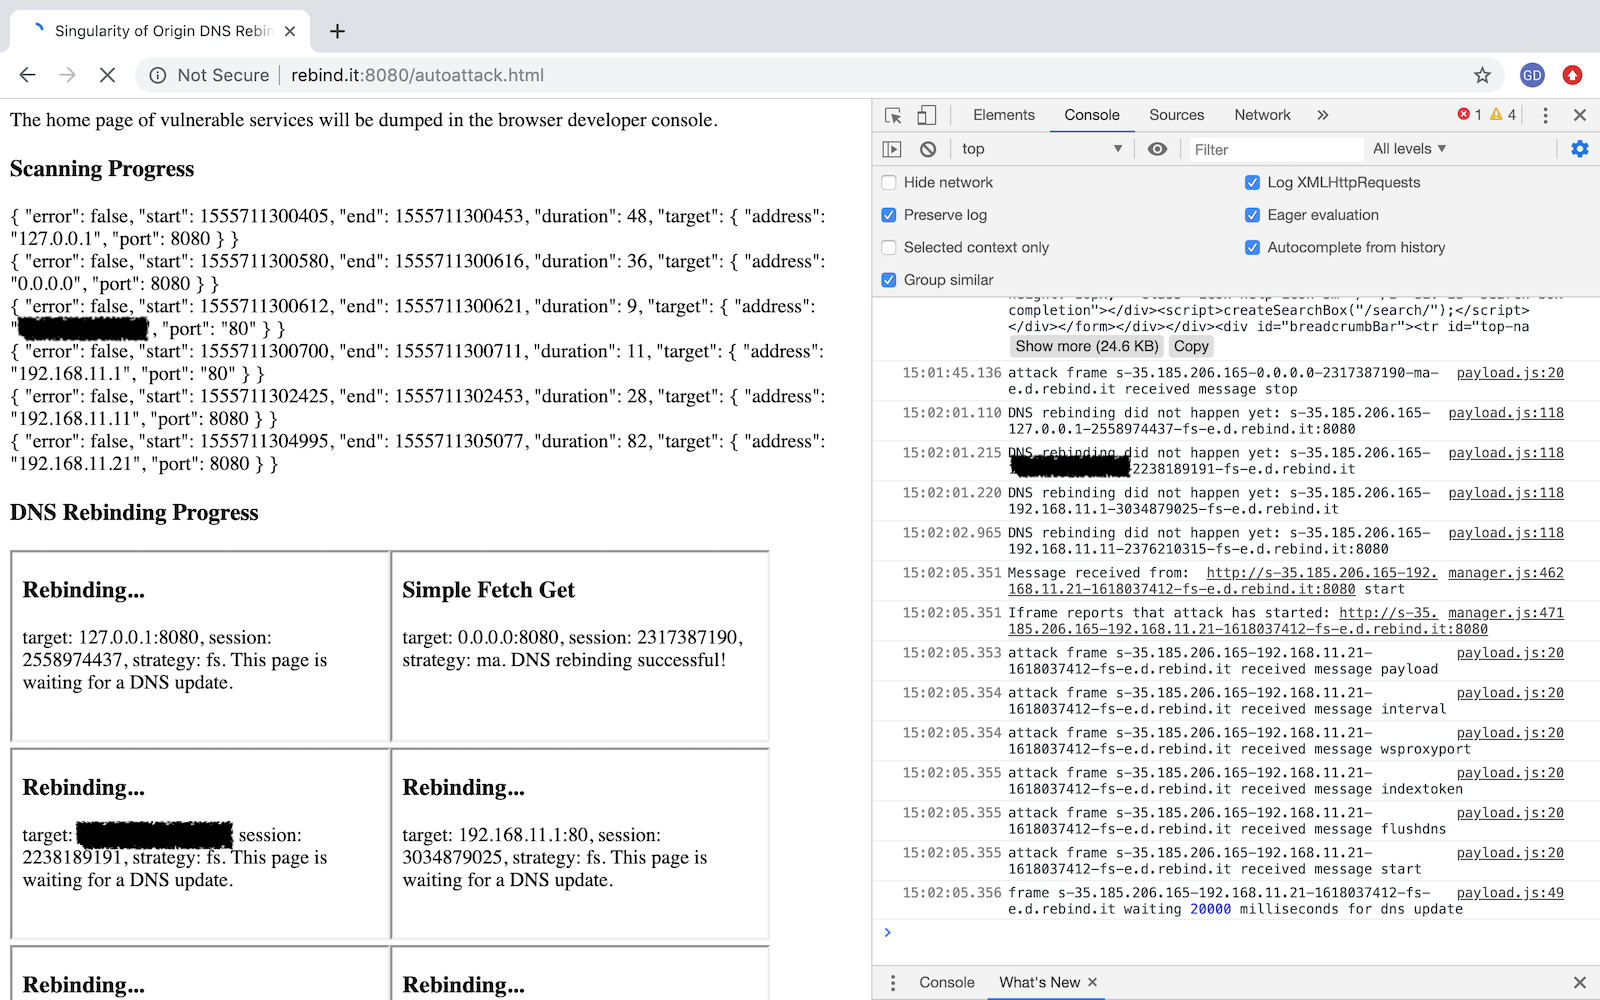 nccgroup/singularity
A DNS rebinding attack framework.
 marshall-hallenbeck/cve_2025_68413-4
Disclosure and PoCs for CVE-2025-68413 and CVE-2025-68414
 g0d150ne/xss2shell
Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…