
 therealdreg/nasm_linux_x86_64_pure_sharedlib
NASM Linux x86_64 pure (no deps) shared library (.so), POC for Reflective ELF SO injection
 schierlm/javapayload
JavaPayload is a collection of pure Java payloads to be used for post-exploitation from pure Java exploits or from common misconfigurations (like not…
 phoenixc2/phoenixc2
Command & Control-Framework created for collaboration in python3
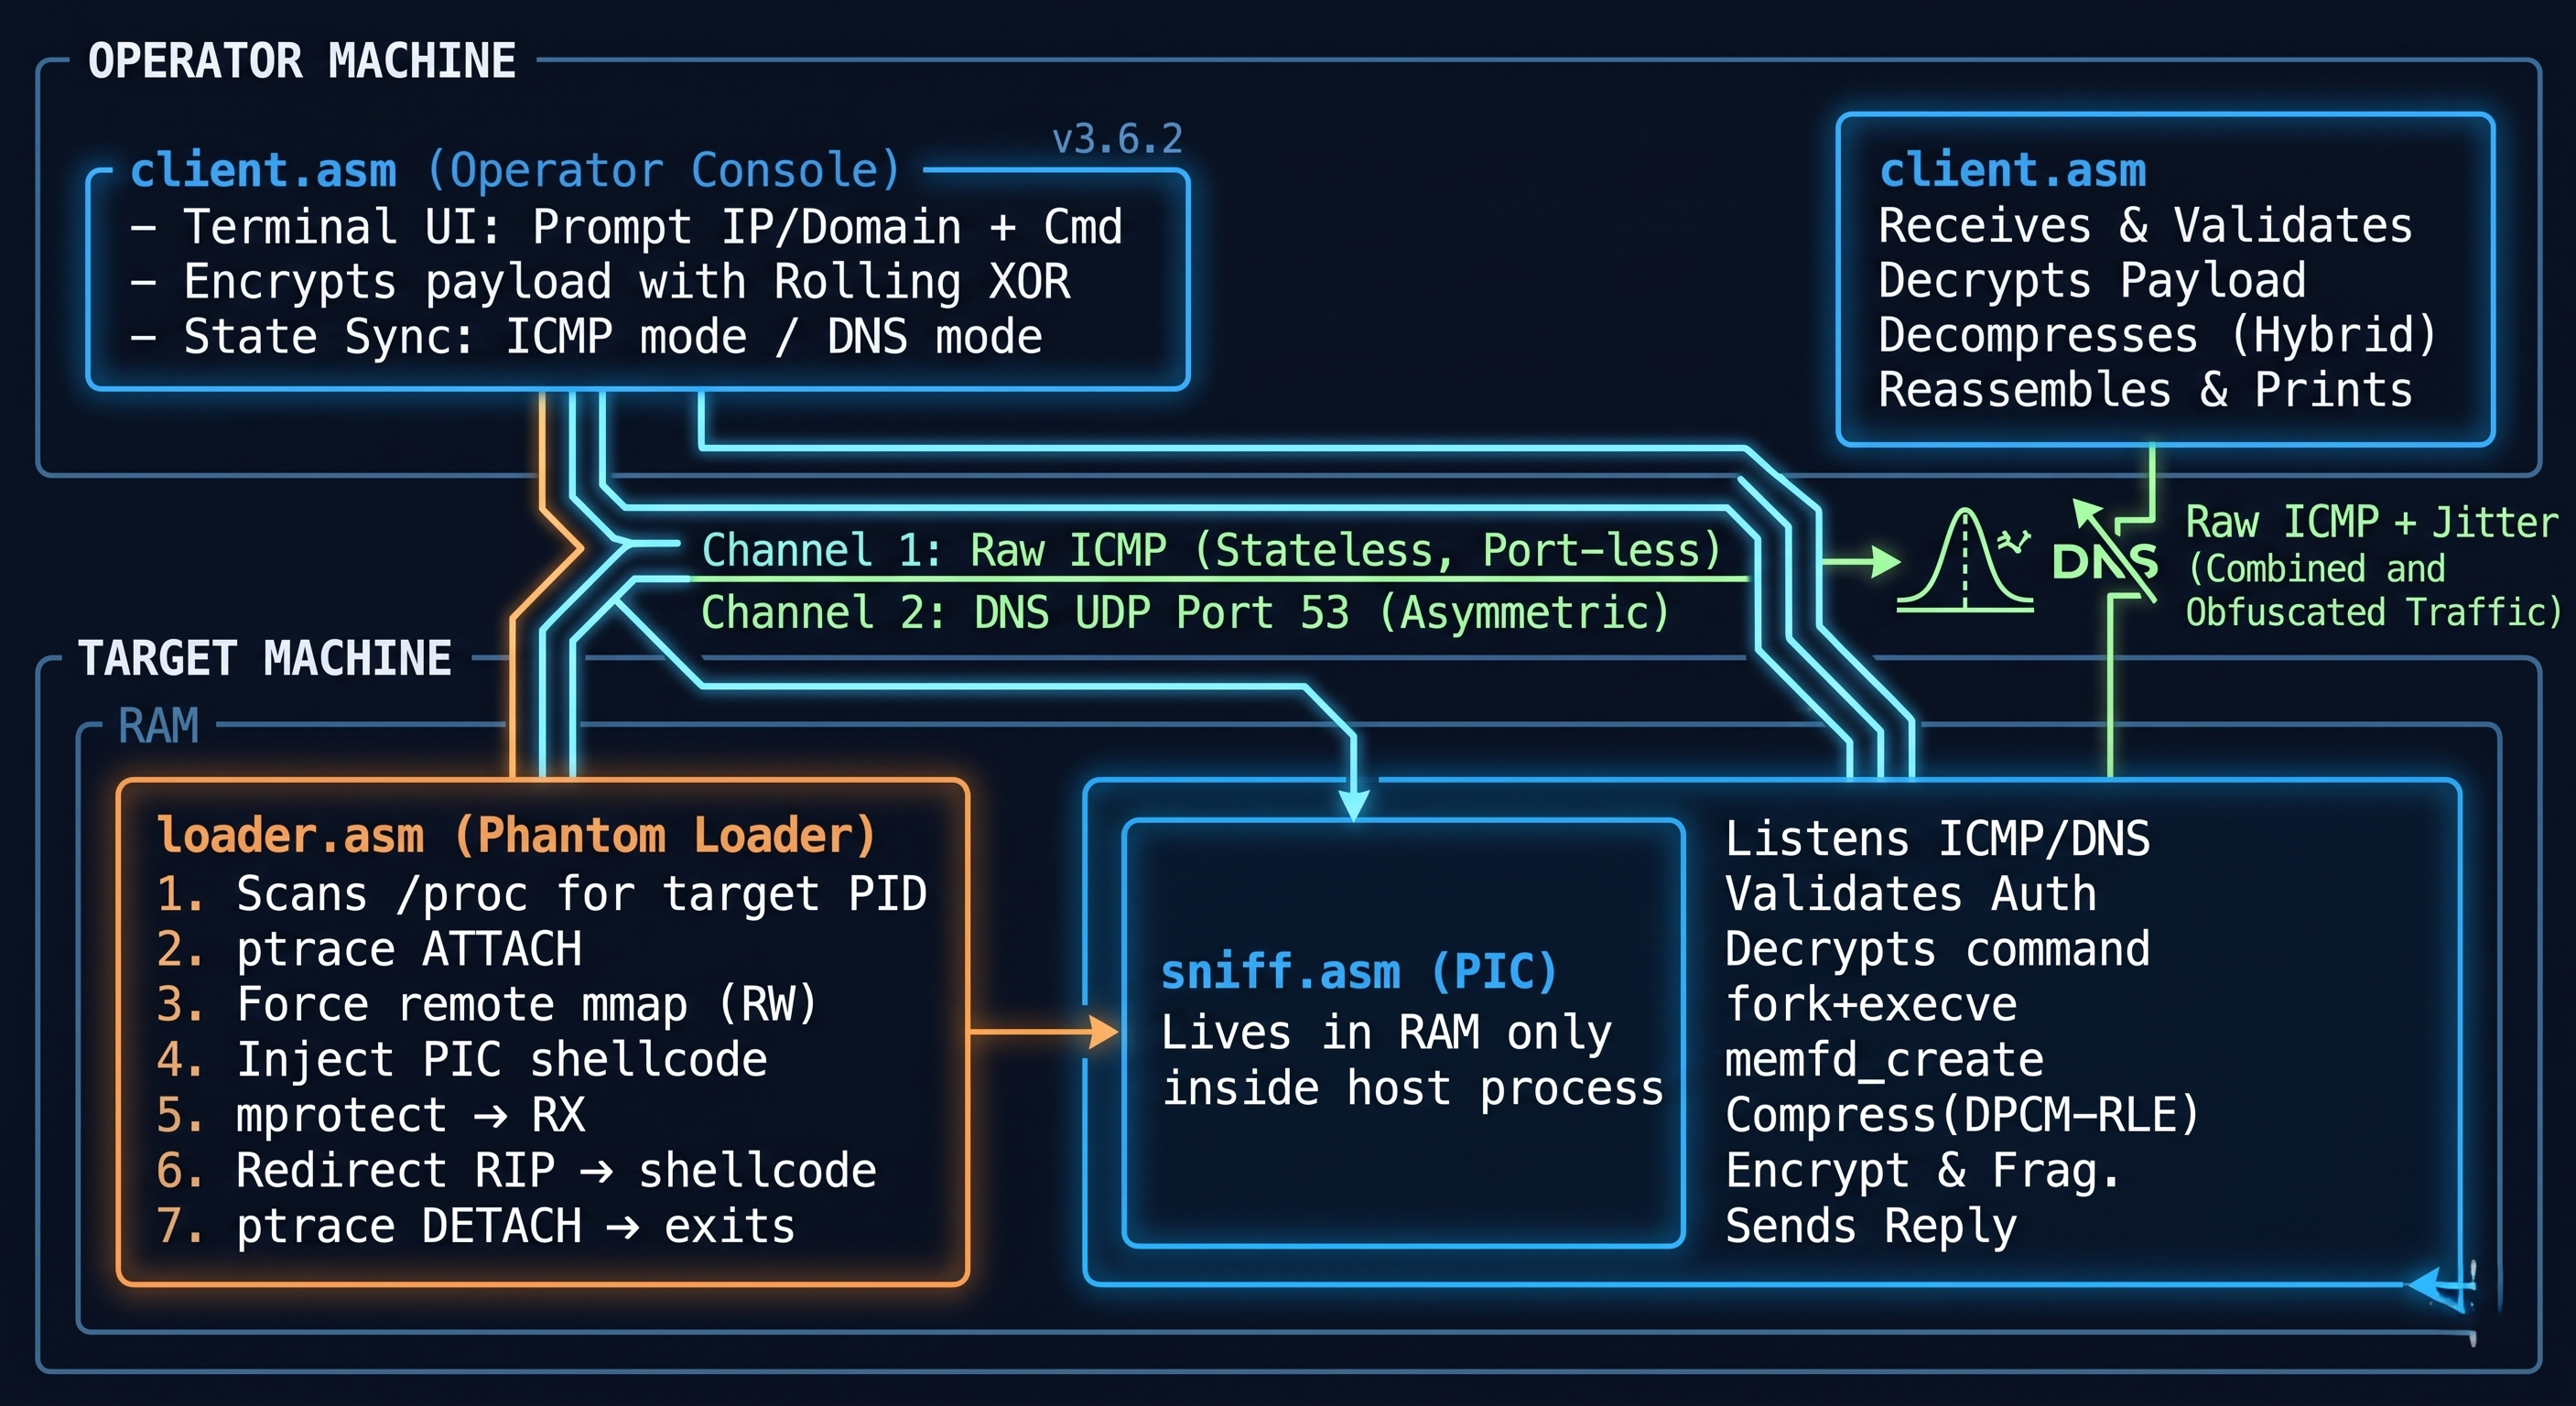 jm00nj/icmp-ghost-a-fileless-x64-assembly-c2-agent
Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…
 jarpex/cve-2023-4911-exploit-optimized
Pure C exploit for CVE-2023-4911 (Looney Tunables) — x86_64 & aarch64 implementations. Multi-processing brute-forcing, dynamic calibration,…
 homjxi0e/cve-2017-9779
Automatic execution Payload From Windows By Path Users All Exploit Via File bashrc
 oxdbxkxo/ez-pwnkit
Go implementation of the PwnKit Linux Local Privilege Escalation exploit (CVE-2021-4034)