Graffiti
 ekultek/graffiti
A tool to generate obfuscated one liners to aid in penetration testing
payload-developmentpayload-generationpenetration-testing+1
1807 years ago
ekultek/graffitiA tool to generate obfuscated one liners to aid in penetration testing
 xlinshan/coldroot
Mac OS Trojan (RAT) made with love <3
 dinosn/cve-2024-20931
Java-based exploit for CVE-2024-20931 bypassing CVE-2023-21839 patch in Oracle WebLogic. Uses JNDI injection via ForeignOpaqueReference to achieve…
 j4ck3lsyn-gen2/cve-2026-6307-longinus
CVE-2026-6307 PoC: Longinus - 2 Boundaries in One Bug https://nebusec.ai/research/v8-cve-2026-6307-writeup/)
 adityabhatt3010/react2shell-cve-2025-55182
React2Shell CVE-2025-55182: unauthenticated unsafe deserialization in React Server Components leading to reliable remote code execution via the…
 oscerd/cve-2026-49042
PoC reproducer for CVE-2026-49042 (Apache Camel camel-langchain4j-tools): a prompt-injected LLM's tool-call arguments become unfiltered Exchange…
 k3ystr0k3r/php-8.1.0-dev-backdoor
PHP 8.1.0-dev User-Agentt Backdoor Remote Code Execution (RCE)
 uwugreed/cve-2025-55182-poc
I know you are probably here from Hack the Box, if so, yes this one actually works.
 ebadfd/cve-2019-19609
Strapi Framework Vulnerable to Remote Code Execution
 phvilasboas/cve-2021-4034
Exploit for CVE-2021-4034, a local privilege escalation in polkit's pkexec, providing a root shell via a shared library and GCONV_PATH manipulation.
 dvkunion/cve-2025-53547-poc
CVE-2025-53547 one of poc code
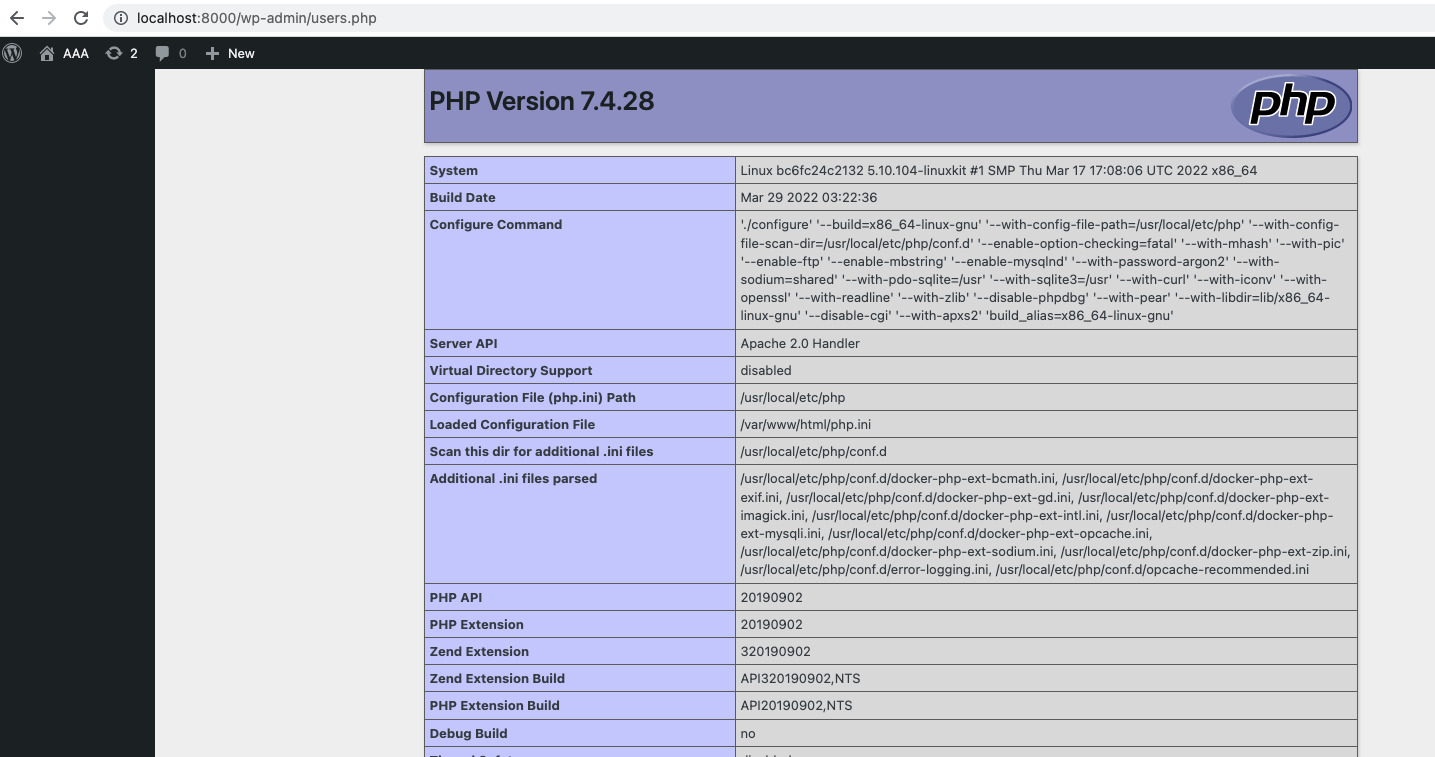 grazee/cve-2022-1329-wordpress-elementor-rce
Proof-of-concept exploit for CVE-2022-1329, a remote code execution vulnerability in WordPress Elementor 3.6.0-3.6.2. Includes Docker-based…
 vilasboasph/cve-2021-4034
Exploit for CVE-2021-4034, a local privilege escalation in polkit's pkexec, providing a root shell via a shared library and GCONV path manipulation.
 kozmic/laravel-poc-cve-2018-15133
PoC for CVE-2018-15133 (Laravel unserialize vulnerability)
 shreyas-malhotra/cve-2025-27410
Updated PoC for CVE-2025-27410, since the one publicly available in the security advisory is prone to failing.